
SecureForce
 hackops-academy/secureforce
A simplified but capable penetration testing framework with exploit library, payload creation, and interactive console for authorized security testing
command-and-controlexploitationexploit-frameworks+6
hackops-academy/secureforceA simplified but capable penetration testing framework with exploit library, payload creation, and interactive console for authorized security testing
 ivansmc/cve-2025-10353-poc
Exploit for CVE-2025-10353. Unauthenticated File Upload on Melis Platform Framework that leads to RCE
 g01d3nw01f/cve-2021-4034
Automates the compilation and serving of the PwnKit exploit for CVE-2021-4034, enabling local privilege escalation on vulnerable Linux systems.
 mrbrutti/cartero
Modular phishing framework with CLI for cloning sites, sending templated emails, and launching phishing campaigns via email, SMS, iMessage, and…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 sam00/cve-2026-56158-.net-framework-rce-poc-exploit
Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…
 mogwaisec/mjet
Mogwai Java Management Extensions (JMX) Exploitation Toolkit
 jenderal92/cve-2026-49049
Mass vulnerability scanner for CVE-2026-49049 – Unauthenticated Remote Code Execution in Joomla Helix3 plugin. Multi‑threaded, detects both executed…
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 ambionics/phpggc
PHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
 redtimmy/richsploit
Exploitation toolkit for RichFaces
 federicodotta/java-deserialization-scanner
All-in-one plugin for Burp Suite for the detection and the exploitation of Java deserialization vulnerabilities
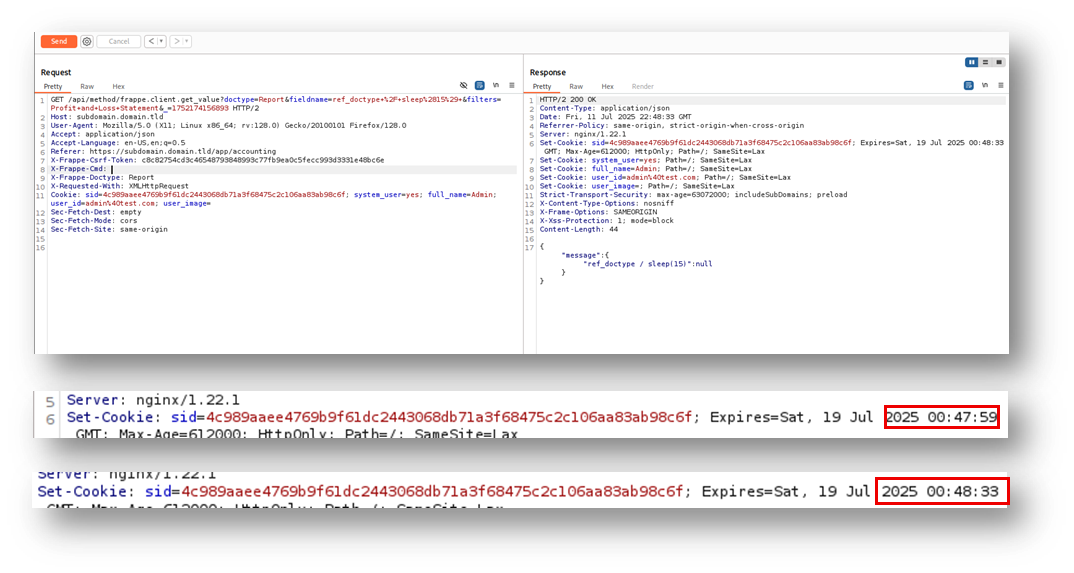 moalali/cve-2025-56380
Frappe Framework v15.72.4 was discovered to contain a SQL injection vulnerability via the fieldname parameter in the frappe.client.get_value API…
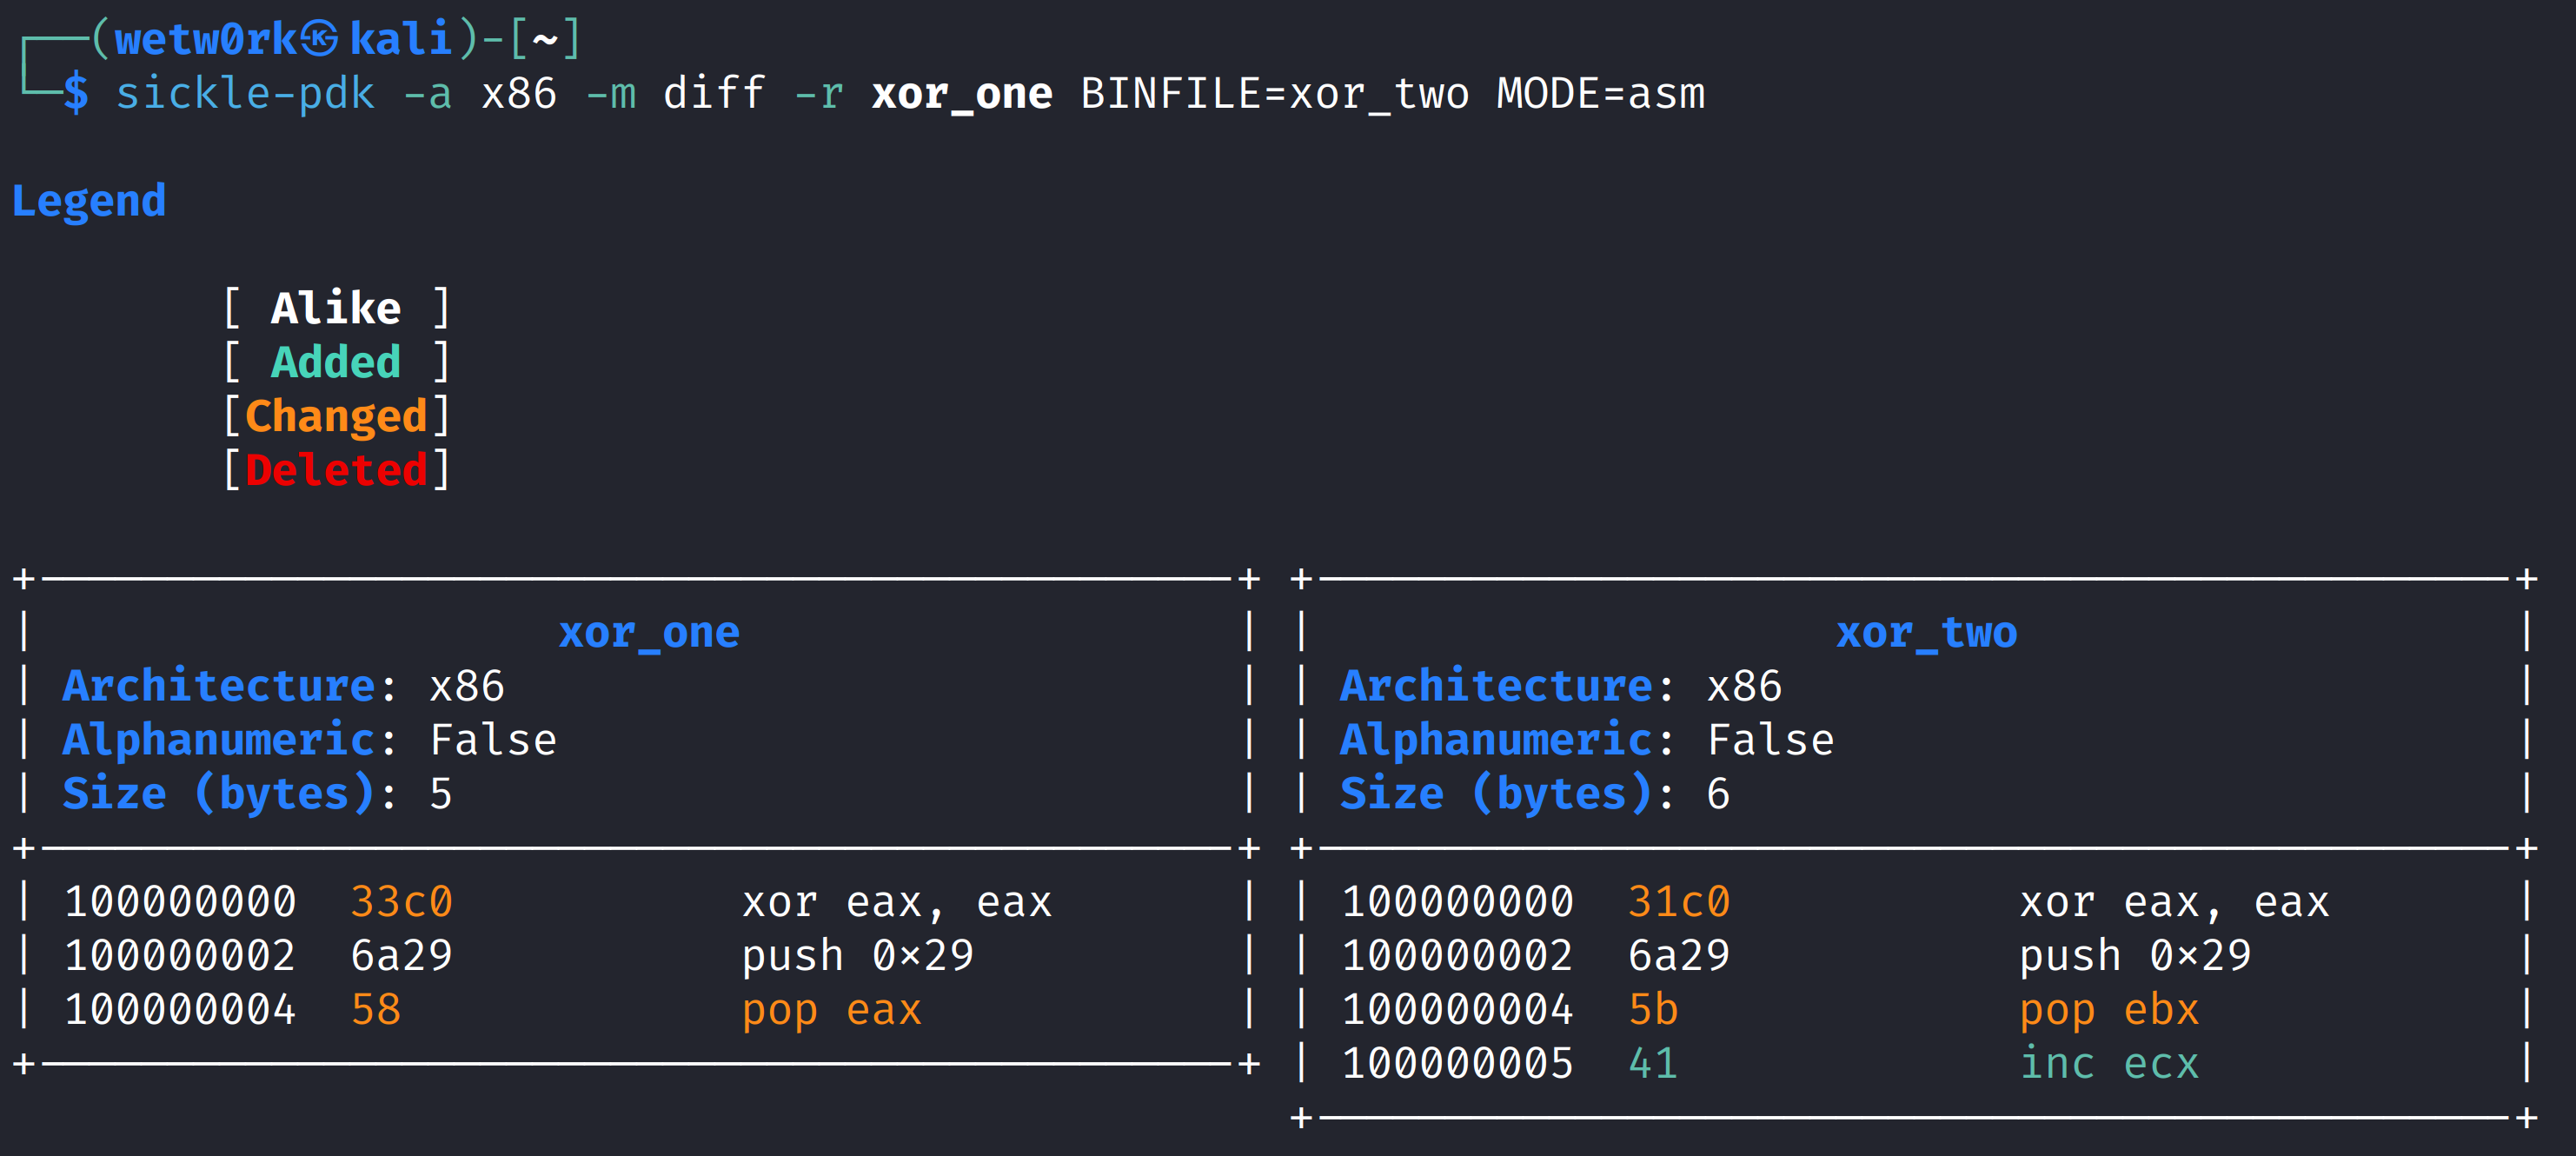 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 tc4dy/cve-2026-60206-poc-exploit
👾 CVE-2026-60206 - Oracle WebLogic SAML Auth Bypass Exploit Framework ⚡Bash & Python versions. Features: --detect safe check, --exploit…
 gh05tcrew/metasploitmcp
MCP Server for Metasploit