

Archived
pickl3
 hlldz/pickl3
Windows active user credential phishing tool
payload-generationpenetration-testingphishing+2
285
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
 z3r0sw0rd/cve-2023-38831-poc
Proof-of-Concept for CVE-2023-38831 Zero-Day vulnerability in WinRAR

 alt3kx/cve-2021-26084_poc
Proof-of-concept exploit for CVE-2021-26084, an OGNL injection vulnerability in Confluence Server and Data Center, demonstrating unauthenticated…
 lp008/cve-2021-25646
Exploit for CVE-2021-25646 Apache Druid RCE via crafted HTTP POST request to the sampler endpoint, with embedded payload delivery and Snort detection…
 aeroot/wp-gdpr-compliance-plugin-exploit
Exploit of the privilege escalation vulnerability of the WordPress plugin "WP GDPR Compliance" by "Van Ons"…
 xaitax/winrar-cve-2023-38831
This module exploits a vulnerability in WinRAR (CVE-2023-38831). When a user opens a crafted RAR file and its embedded document, a script is…
 thestingr/cve-2025-25257
Public PoC for CVE-2025-25257: FortiWeb pre-auth SQLi to RCE
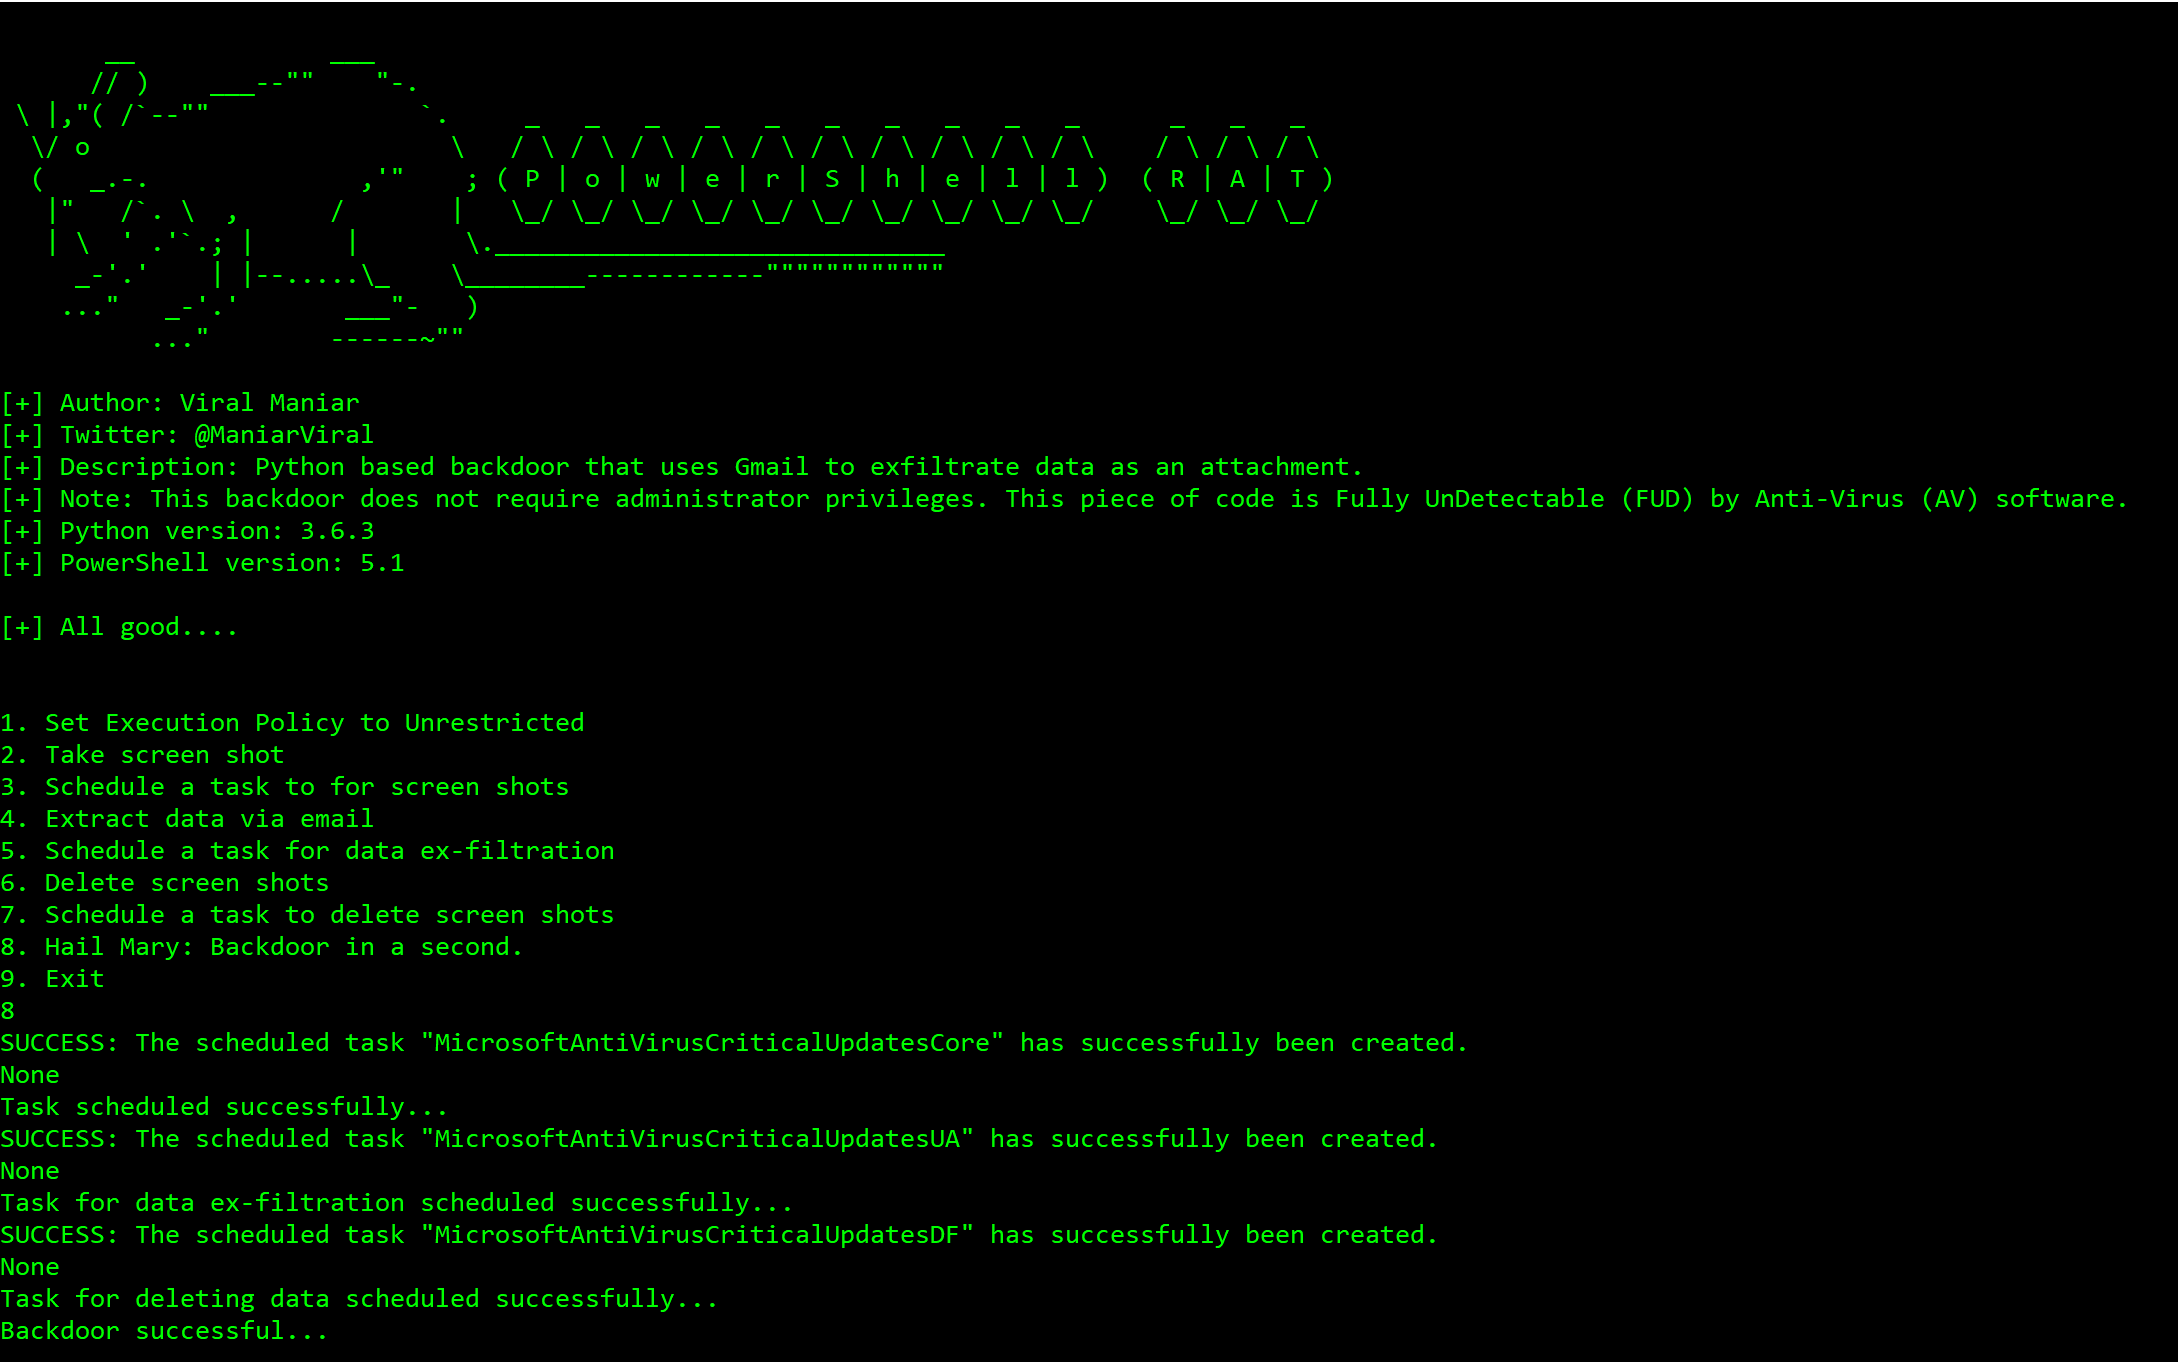 viralmaniar/powershell-rat
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 namazso/dll-proxy-generator
Generate a proxy dll for arbitrary dll
 nytrorst/xssfuzzer
XSS Fuzzer is a tool which generates XSS payloads based on user-defined vectors and fuzzing lists.
 dragoqcc/cruciblec2
A C# Command & Control framework
 sergeb250/blueducky
BlueDucky exploits a Bluetooth vulnerability, specifically CVE-2023-45866, which allows an attacker to inject keystrokes into a target device. The…
 ungabunga-ctf/cve-2023-26039
CVE-2023-26039 - ZoneMinder. Any authenticated user can construct an api command to execute any shell command as the web user.
 scs-labrat/android_autorooter
Exfiltrate sensitive user data from apps on Android 12 and 13 using CVE-2024-0044 vulnerability remotely