metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

A Web Vulnerability Scanner and Patcher

Python proof-of-concept for detecting CVE-2023-27372 in SPIP CMS. Scans single or multiple URLs for the vulnerability and outputs results to terminal…

Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…

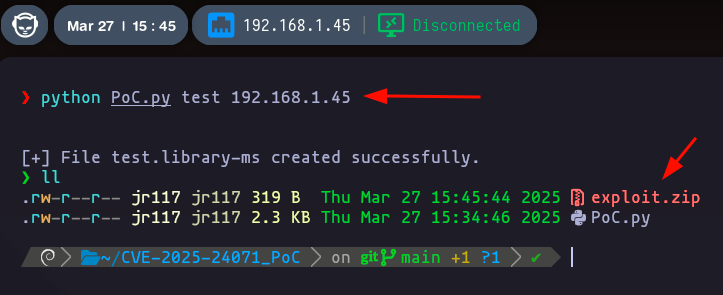
A PoC of CVE-2025-24071 / CVE-2025-24054, A windows vulnerability that allow get NTMLv2 hashes

Aimy Captcha-Less Form Guard Joomla Component PHP Object Injection RCE. clfgd XOR keystream recovery + unserialize(). CVSS 10.0 | CWE-502 |…

SMBGhost (CVE-2020-0796) Automate Exploitation and Detection

Nuclei template providing a proof-of-concept for CVE-2024-4577, a PHP CGI argument injection vulnerability, enabling automated detection and testing.

CVE-2026-58480 / CVE-2026-15158 — Unauthenticated RCE in Blocksy Companion Pro < 2.1.47 (300K+ installs). Pre-auth arbitrary file upload via…

Laravel RCE Exploit PoC - CVE-2021-3129 (user-friendly with automatic log path detection)

All about bug bounty (bypasses, payloads, and etc)

Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)

CVE-2026-63030 (RCE) + CVE-2026-60137 (SQLi)

WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…

Windows Remote Desktop Services Vulnerability Allows Remote Code Execution

Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…

WordPress wp2shell vulnerability-chain scanner for CVE-2026-63030 and CVE-2026-60137, with active detection, optional PoC, JSON export.

Apache Tomcat AJP Ghostcat (CVE-2020-1938) exploit tool for file disclosure with multi-target scanning, custom wordlists, and upload point detection…