
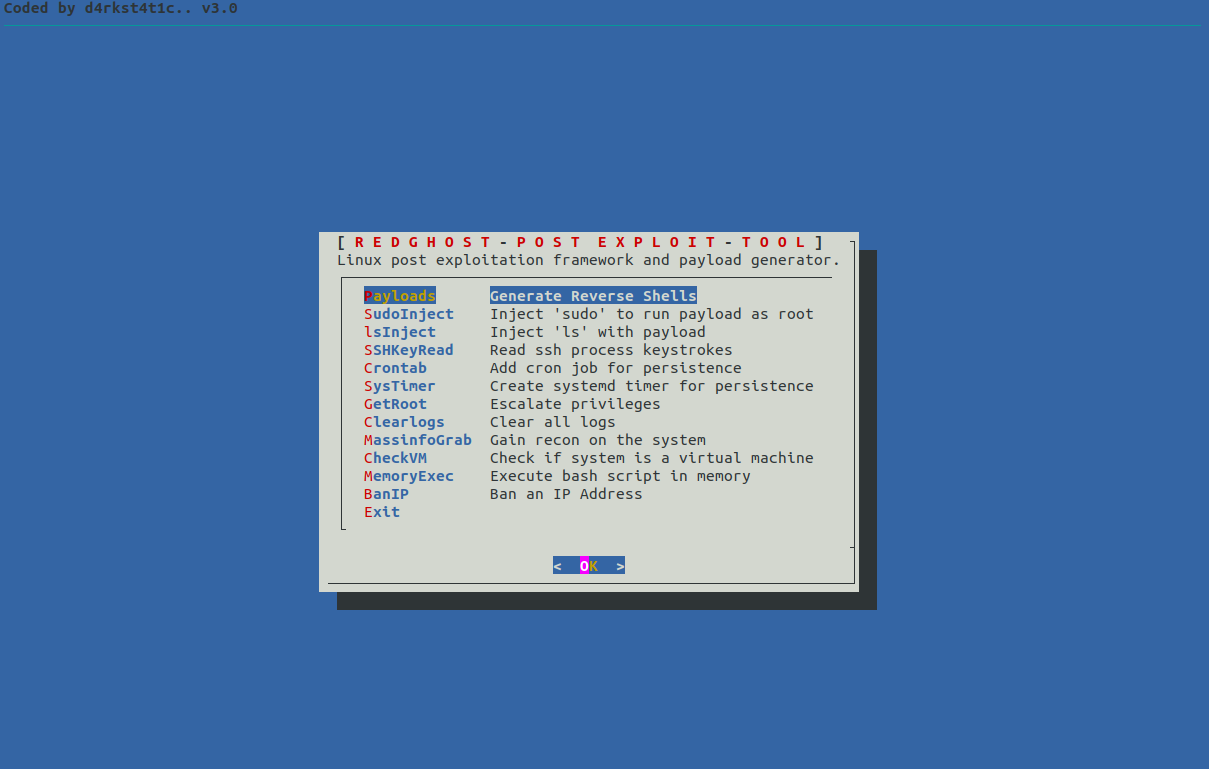
RedGhost
 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
command-and-controllateral-movementpayload-generation+5
541
d4rk007/redghostLinux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 hadi999/nxcrypt
NXcrypt - 'python backdoor' framework
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 cn33liz/p0wnedshell
PowerShell Runspace Post Exploitation Toolkit
 bashfuscator/bashfuscator
A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…
 degenerat3/meteor
A cross-platform C2/teamserver supporting multiple transport protocols, written in Go.
 lightningspeed221/winrar-exploit-cve-2023-38831
C# utility demonstrating CVE-2023-38831 archive-structure exploitation technique for WinRAR versions below 6.23. Builds proof-of-concept binaries for…
 andreiverse/grc2
Lightweight C2 framework written in Nim for generating implants, managing listeners, and executing tasks via TCP/HTTP with a loot system for…
 jonasuliana/cve-2017-8759
Simple C# implementation of CVE-2017-8759