

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 threat9/routersploit
Exploitation Framework for Embedded Devices
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 owasp/owasp-hunting
Curated collection of payloads for ethical security testing and bug bounty hunting, covering common web vulnerabilities and attack vectors.
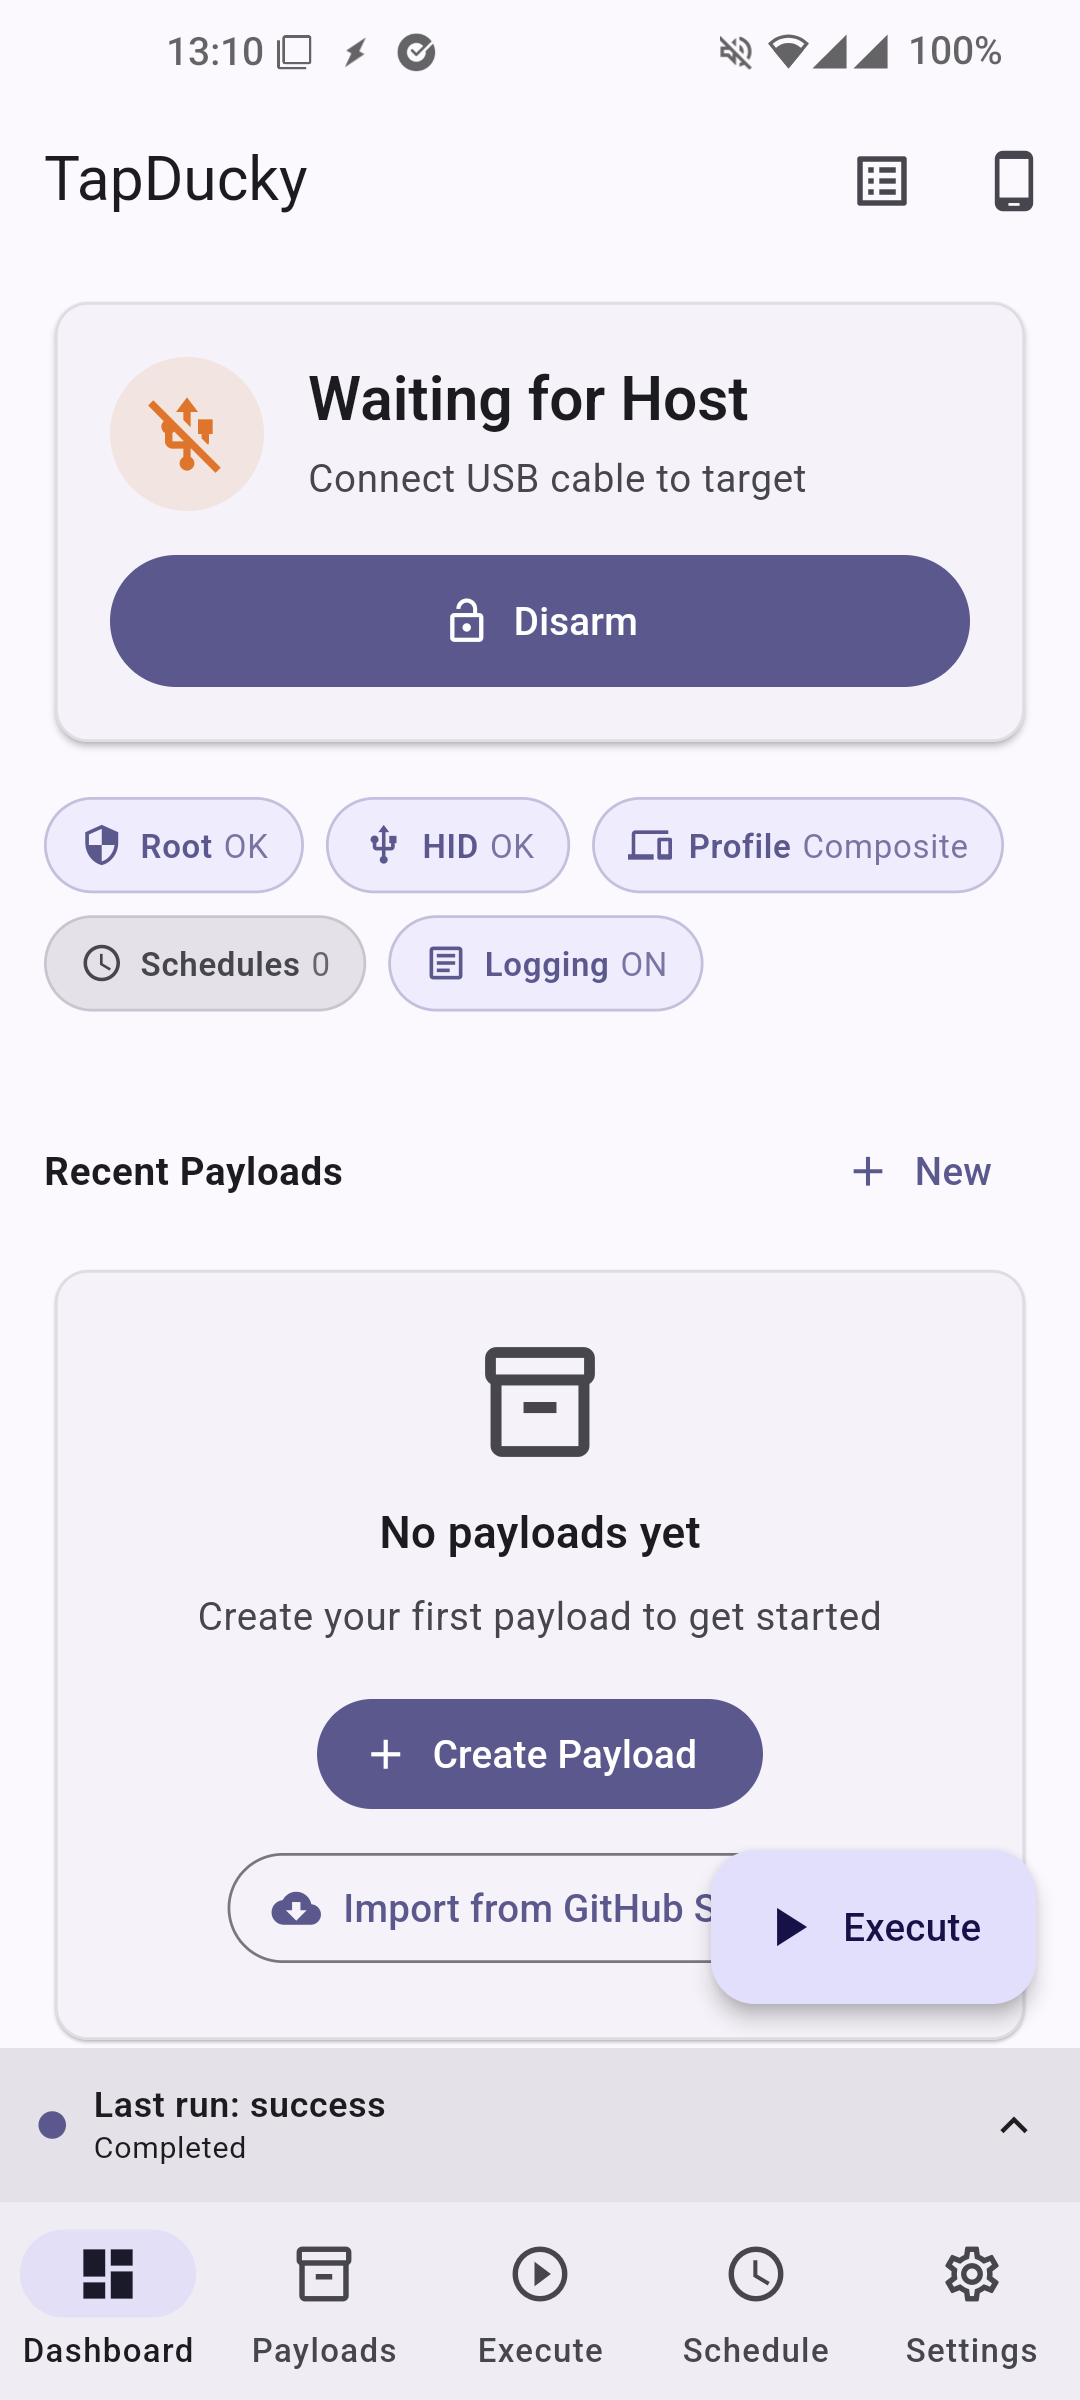 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector
 mhaskar/octopus
Open source pre-operation C2 server based on python and powershell
 nccgroup/ransomware-simulator
NCC Group Ransomware Simulator
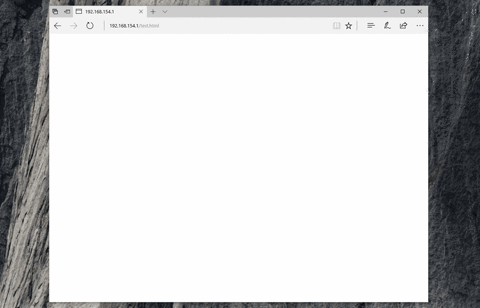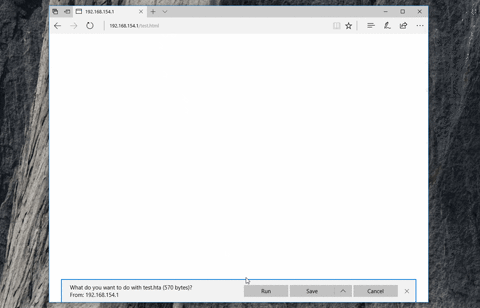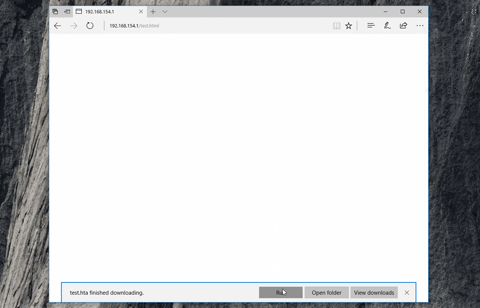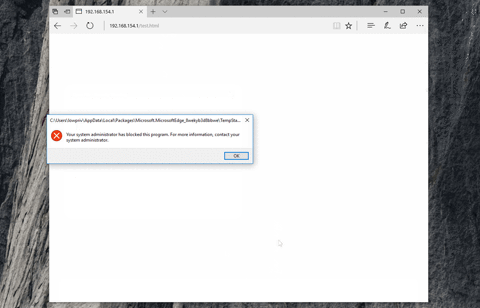 nccgroup/demiguise
HTA encryption tool for RedTeams
 abraxas/cve-2026-48356
Proof-of-concept and lab pack for CVE-2026-48356, an unauthenticated unrestricted file upload in Magento Open Source guest-cart REST custom options.
 wietze/invoke-argfuscator
Invoke-ArgFuscator is an open-source, cross-platform PowerShell module that helps generate obfuscated command-lines for common system-native…
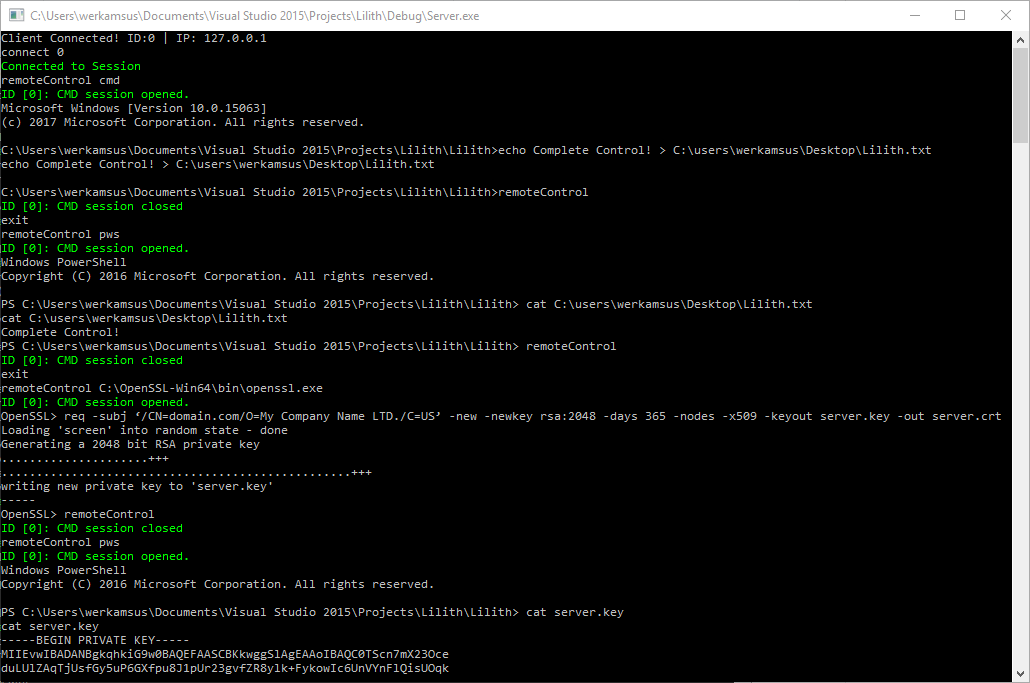 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
 nmmorette/cve-2024-34102
CVE-2024-34102 exploit for python3
 inok009/foxcms-cve-2025-29306-poc
Python PoC for CVE-2025-29306, a parameter injection RCE in FOXCMS v1.2. Injects PHP code via the id parameter on /images/index.html for authorized…
 pushkarup/cve-2023-5360
The Royal Elementor Addons and Templates WordPress plugin before 1.3.79 does not properly validate uploaded files, which could allow unauthenticated…
 mrsqar-ye/door404
Web application backdoor builder