

SSTImap
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
code-analysiscommand-and-controldynamic-code-analysis+6
vladko312/sstimapAutomatic SSTI detection tool with interactive interface

 m4cs/digiduck-framework
Framework for Digiduck Development Boards running ATTiny85 processors and micronucleus bootloader!
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 kosmicowl045/ict287-cve-2022-42889
Setup and exploit recreation for CVE-2022-42889 Text4Shell.
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
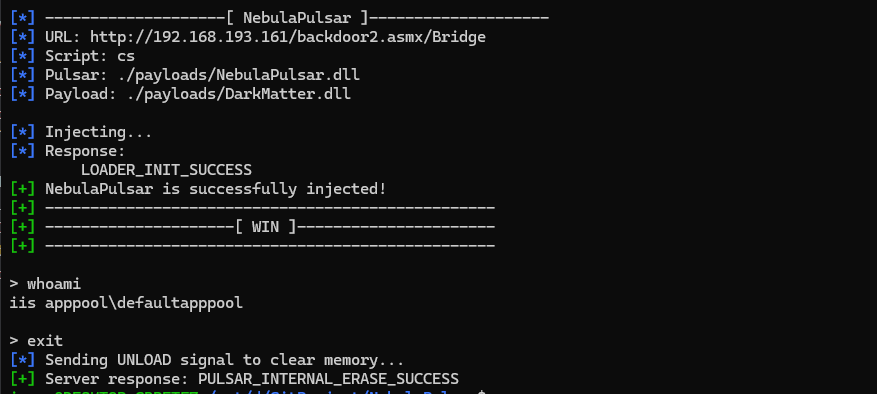 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
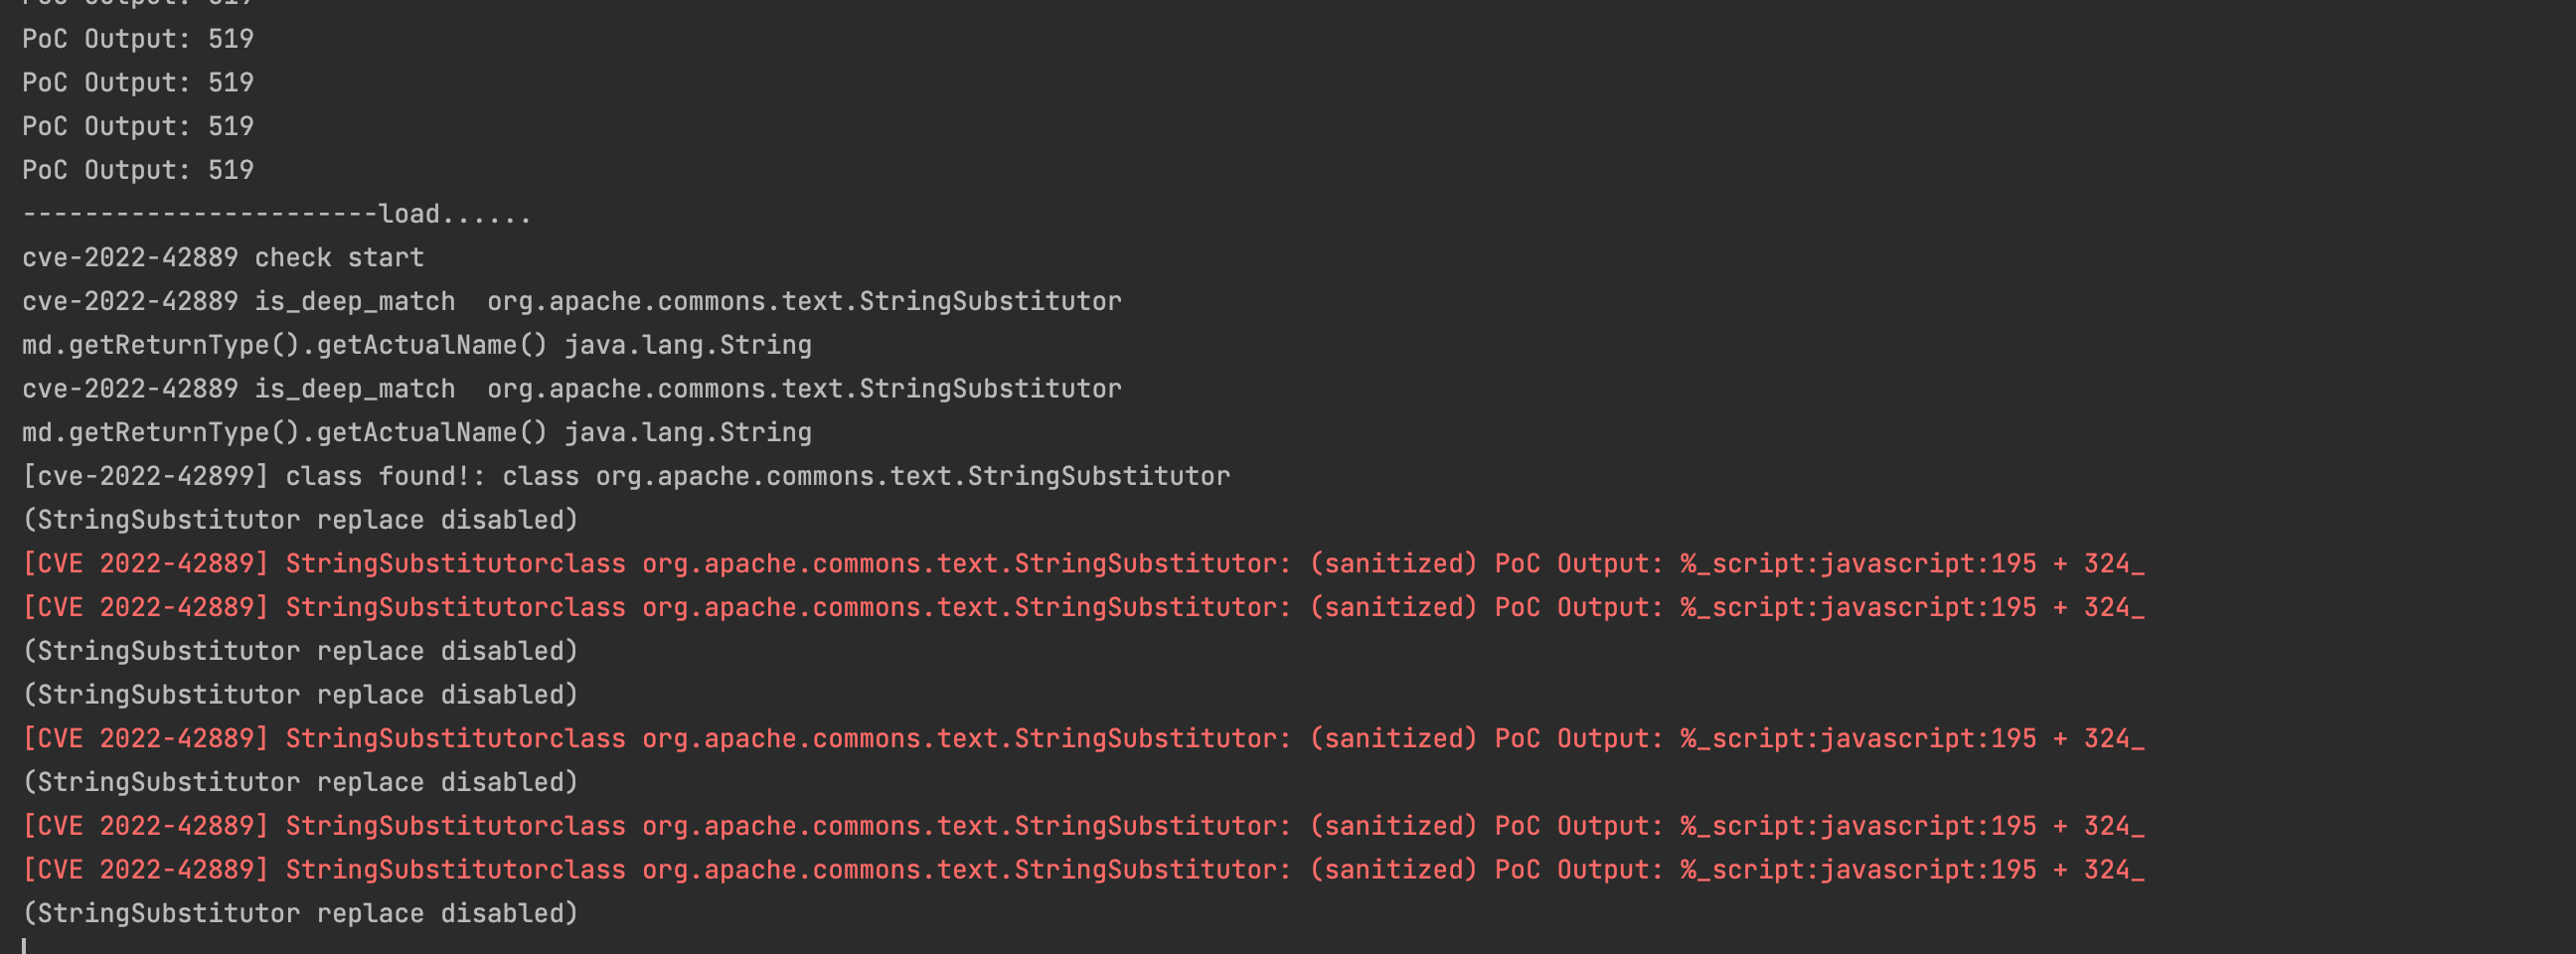 uk0/cve-2022-42889-intercept
通过 jvm 启动参数 以及 jps pid进行拦截非法参数
 nettitude/poshc2
A proxy aware C2 framework used to aid red teamers with post-exploitation and lateral movement.
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 0xcan1337/cve-2025-47812-poc
Simple exploit for Wing FTP Server RCE (CVE-2025-47812) to run commands and get a reverse shell. For educational use only.
 higorgabrieldcf/gocd_poc_supply_chain_attack
CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
 kali-dass/cve-2021-44228-log4shell
Java-based proof-of-concept exploit for CVE-2021-44228 (Log4Shell) enabling remote command execution, OS information gathering, and arbitrary…
 cyber-niz/cve-2020-9496
Manual exploit for CVE-2020-9496, an unauthenticated Java deserialization RCE in Apache OFBiz XML-RPC, with step-by-step instructions for payload…