
hackingtool
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
cloud-securityexploitationforensics+9
79.5k
z4nzu/hackingtoolAll-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
 izzz0/cve-2023-27372-poc
Python proof-of-concept for detecting CVE-2023-27372 in SPIP CMS. Scans single or multiple URLs for the vulnerability and outputs results to terminal…
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
 urbanesec/zackattack
Unveiled at DEF CON 20, NTLM Relaying to ALL THE THINGS!
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 julian911015/log4j-scanner-exploit
Script en bash que permite identificar la vulnerabilidad Log4j CVE-2021-44228 de forma remota.
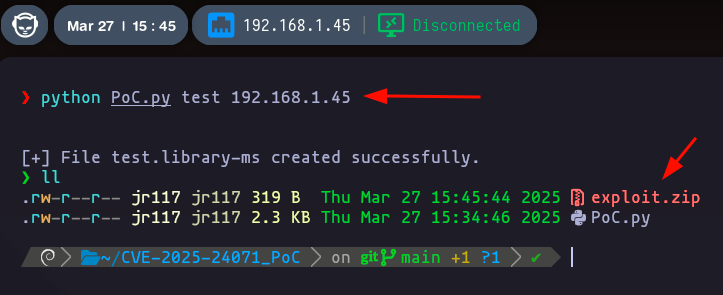 marcejr117/cve-2025-24071_poc
A PoC of CVE-2025-24071 / CVE-2025-24054, A windows vulnerability that allow get NTMLv2 hashes
 aydinnyunus/keylogger
Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.
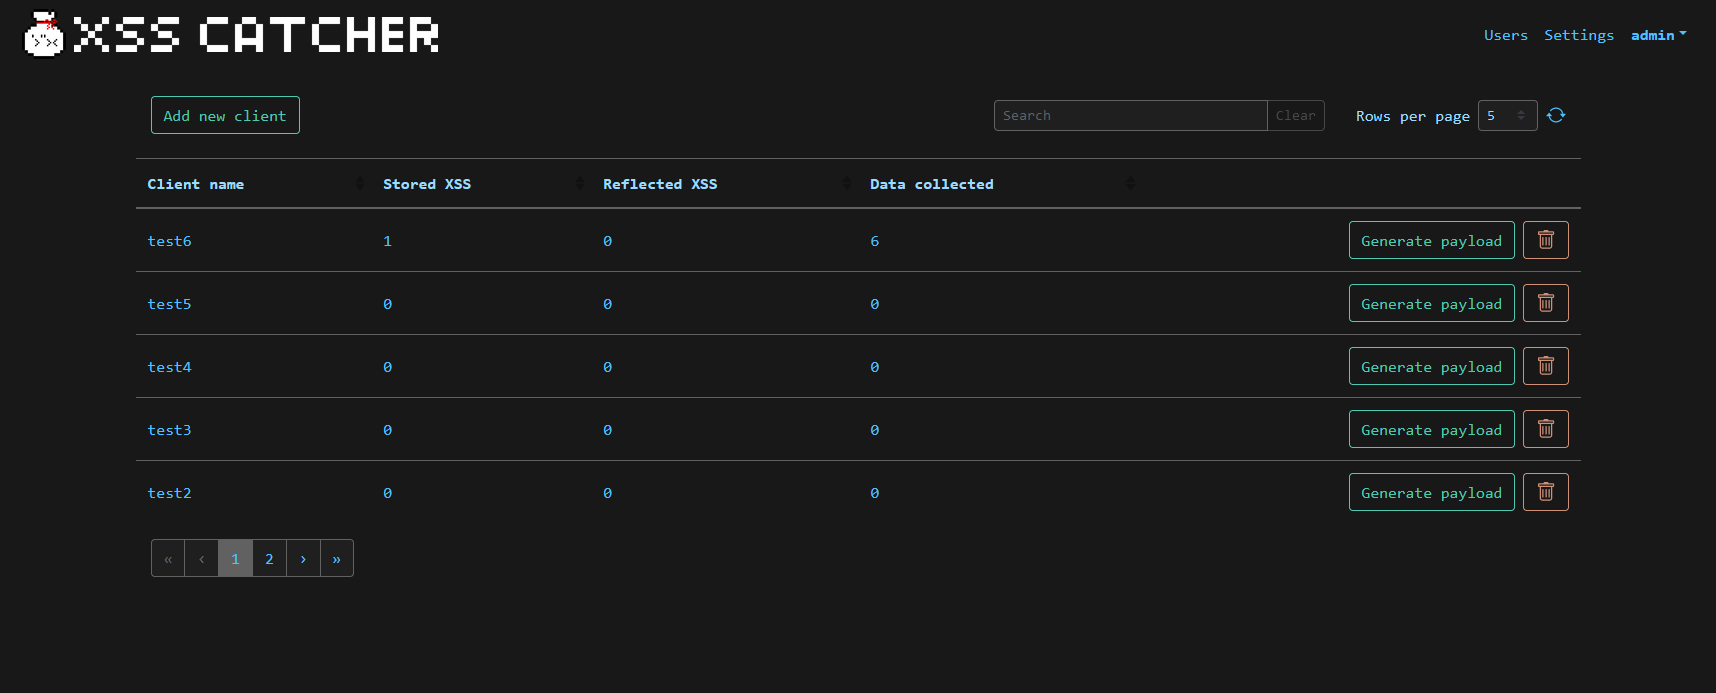 daxakahackerman/xss-catcher
A blind XSS detection and XSS data capture framework
 kljunowsky/cve-2022-42889-text4shell
Proof-of-concept exploit for CVE-2022-42889 (Text4Shell) in Apache Commons Text, with manual and mass exploitation scripts using script, URL, and DNS…
 ethicalhackingplayground/wordlistgen
Generates target specific word lists for Fuzzing with fuff
 malayke/cve-2023-33246_rocketmq_rce_exploit
CVE-2023-33246 RocketMQ RCE Detect By Version and Exploit
 shinthink/cve-2026-65883
Aimy Captcha-Less Form Guard Joomla Component PHP Object Injection RCE. clfgd XOR keystream recovery + unserialize(). CVSS 10.0 | CWE-502 |…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 malwaretech/log4jtools
Tools for investigating Log4j CVE-2021-44228
 wireghoul/htshells
Self contained htaccess shells and attacks
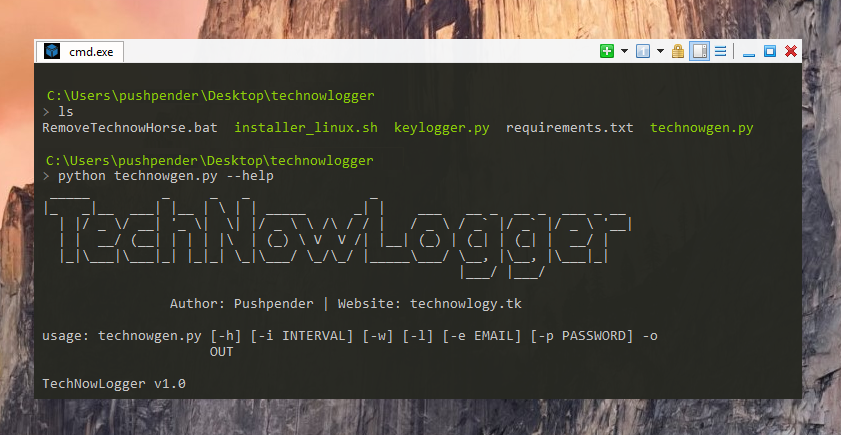 pushpenderindia/sinister
Sinister is Windows/Linux Keylogger Generator which sends key-logs via email with other juicy target info