
ezXSS
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
information-gatheringpayload-generationpenetration-testing+2
2.3k
ssl/ezxssBlind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 threat9/routersploit
Exploitation Framework for Embedded Devices
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
 mdsecactivebreach/sharpshooter
Payload Generation Framework
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
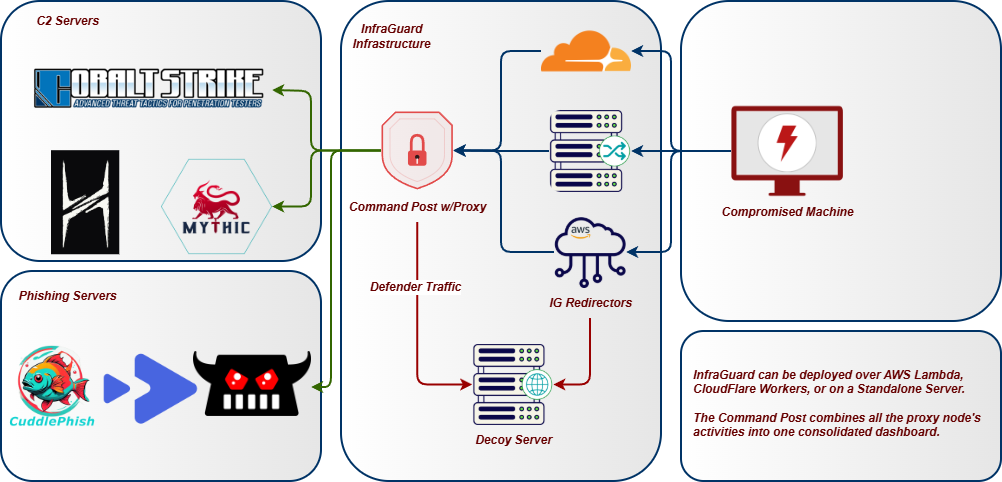 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution

 rek7/ddoor
DDoor - cross platform backdoor using dns txt records
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 funnywolf/pystinger
Bypass firewall for traffic forwarding using webshell

 f5-labs/parquet-canary-exploit-rce-poc-cve-2025-30065
Generates malicious Apache Parquet files to test for CVE-2025-30065 RCE vulnerability via SSRF callback. Designed for authorized security testing of…
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
 faisal-p27/wareed-dns-c2
DNS-only command-and-control framework with Windows agent, payload generation, remote shell execution, shellcode injection, and SOCKS5 proxy support…
 giterlizzi/nmap-log4shell
Nmap NSE script for detecting Apache Log4j RCE (CVE-2021-44228) by injecting JNDI exploit payloads via HTTP headers or TCP/UDP sockets across…