
CVE-2025-29824-Exploit
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
binary-exploitationexploitationmalware-analysis+6
20
afanpan/cve-2025-29824-exploitUse after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
 ajinabraham/xenotix-python-keylogger
Xenotix Python Keylogger for Windows.
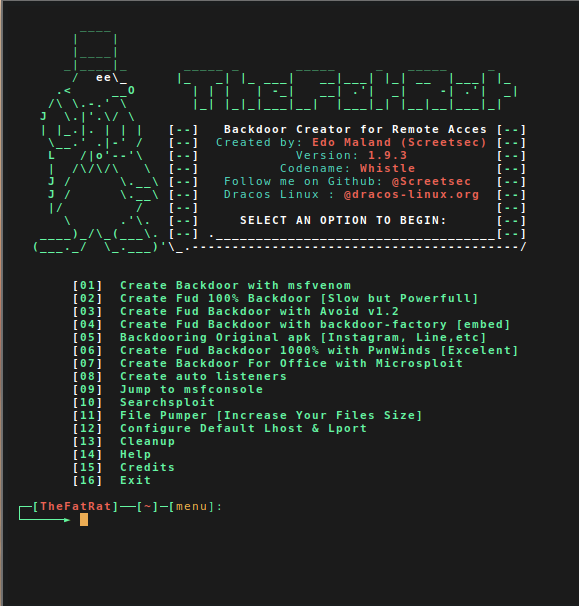 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 homjxi0e/cve-2017-8625_bypass_umci
Proof-of-concept exploit demonstrating UMCI bypass in Internet Explorer using JScript and ActiveX to execute arbitrary binaries, targeting Windows…
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 aaaddress1/pr0cess
some gadgets about windows process and ready to use :)
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
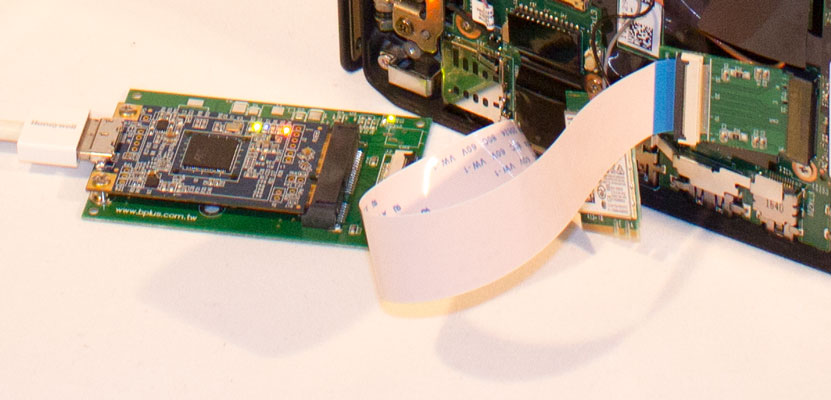 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
 u0pattern/cve-2018-1000117-exploit
Buffer Overflow Vulnerability that can result ACE
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 homjxi0e/cve-2017-9779
Automatic execution Payload From Windows By Path Users All Exploit Via File bashrc
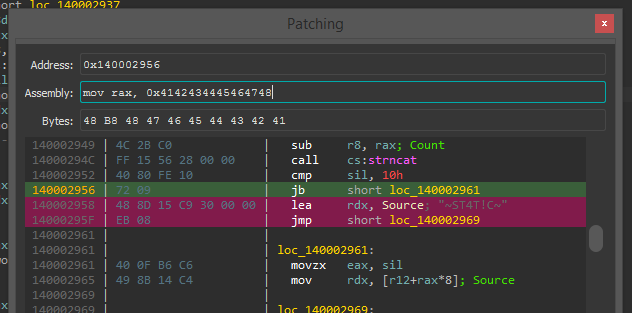 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
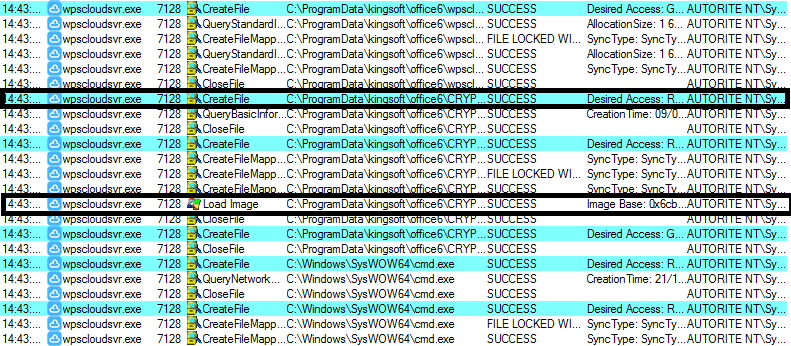 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
 zsecure/cve-2022-29359
CVE-2022-29359 - School Application System Stored Cross-Site Scripting
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
 malwaretech/tinyxpb
Windows XP 32-Bit Bootkit
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…