
custom-oscp-tooling
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
database-securitydns-analysishash-analysis+9
wattocyber/custom-oscp-toolingOSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
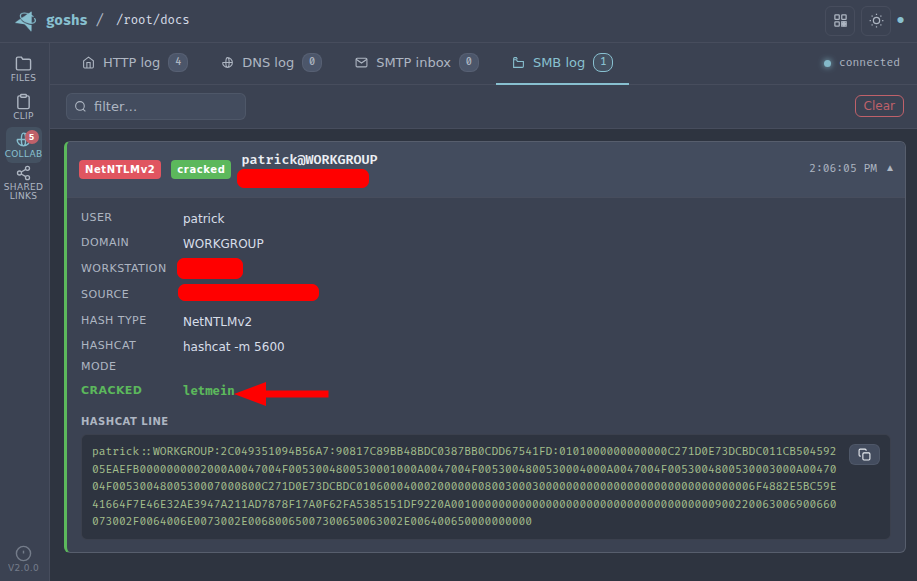
 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
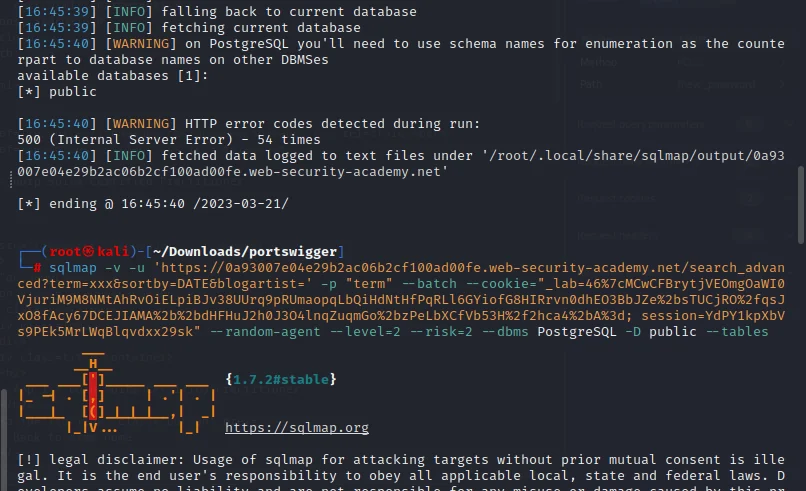 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
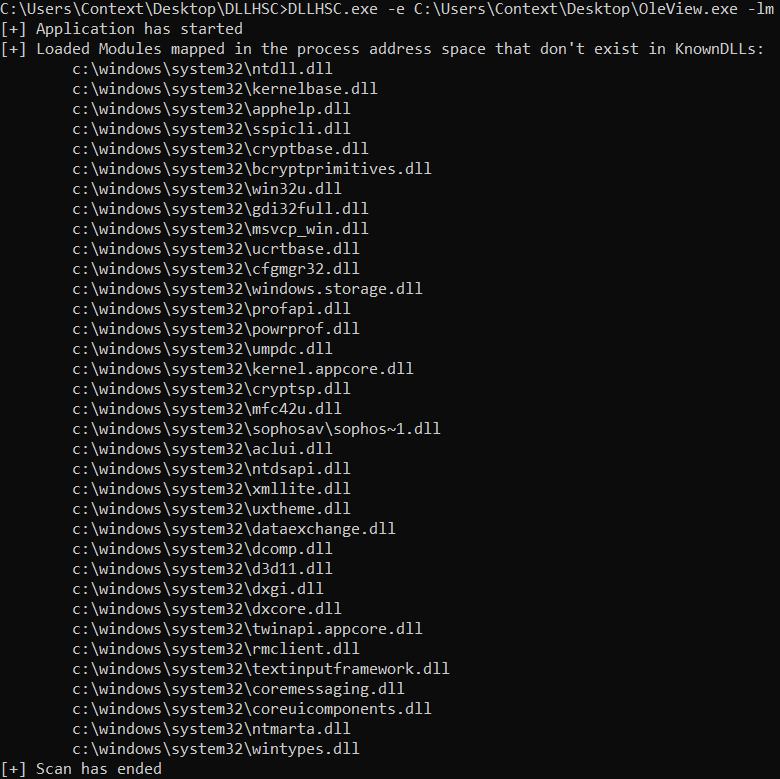 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 flyinbedxyz/cve-2021-1732
Local privilege escalation exploit for CVE-2021-1732 targeting Windows 10 and Server versions, with PoC code and affected system enumeration.
 philippedixon/cve-2018-15473
Python-based exploit for CVE-2018-15473, enabling SSH user enumeration via OpenSSH username validation timing attack. Updated from Python 2 to 3 for…
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
 al1ex/pentest-tools
Intranet penetration tools
 3gstudent/homework-of-python
Python codes of my blog.
 brmkit/toastnotify-bof
abusing windows toast notifications for fun and user manipulation