
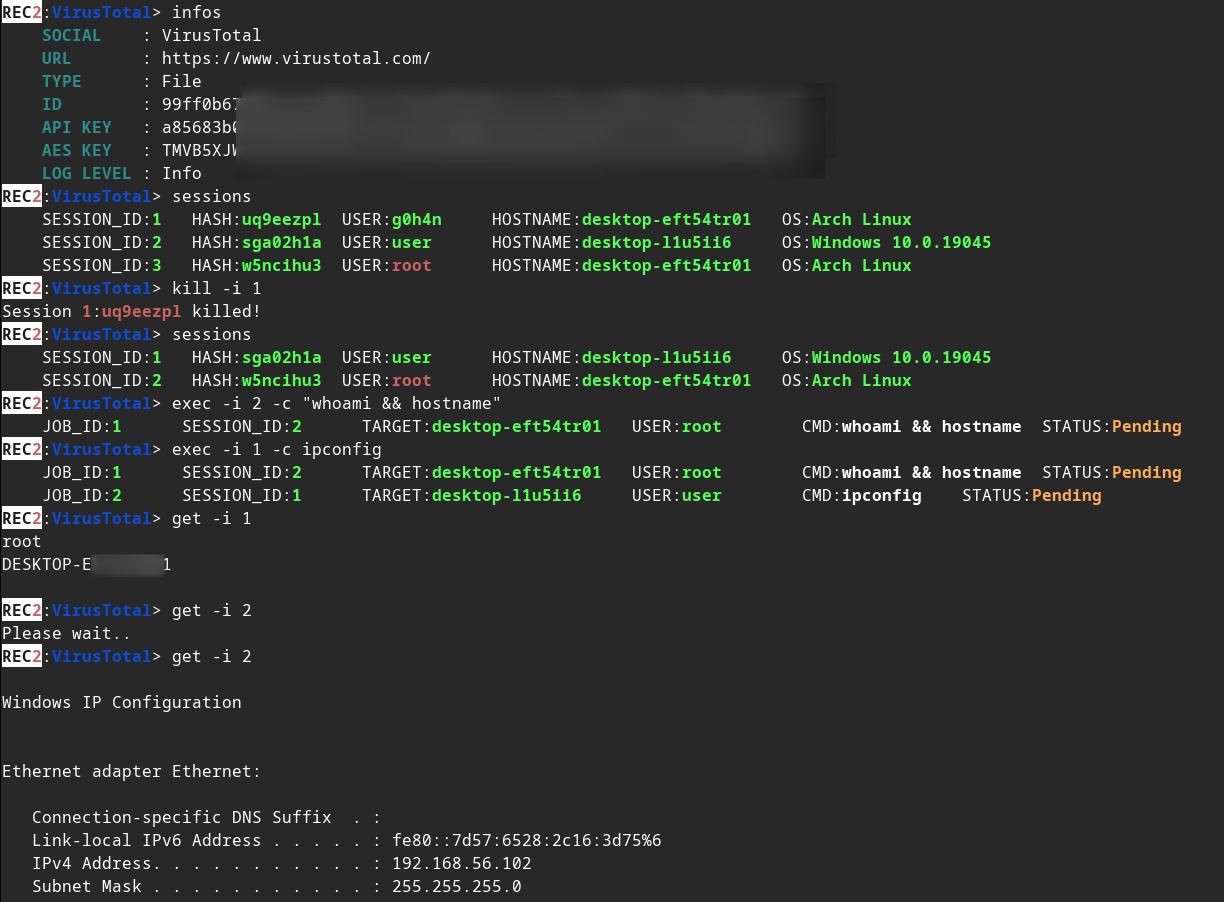
REC2
 g0h4n/rec2
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…
command-and-controlpayload-developmentpenetration-testing+3
162
g0h4n/rec2REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 edu0x01/hack-tools
Project that brings together several pentest tools
 m507/m-botnet
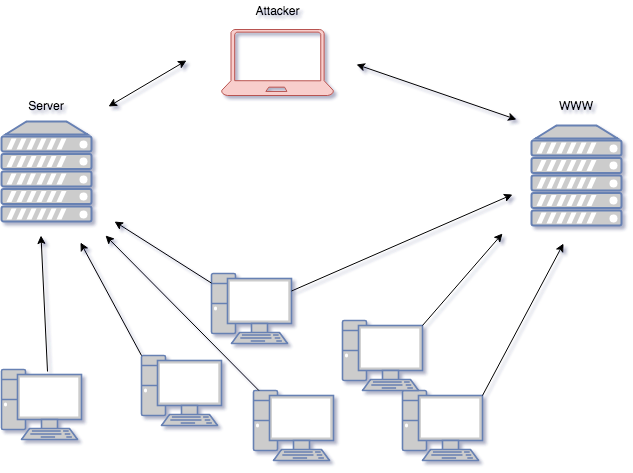
A C2 project that controls a self-propagating MS17-010 worm.
 erarnitox/malvexc2
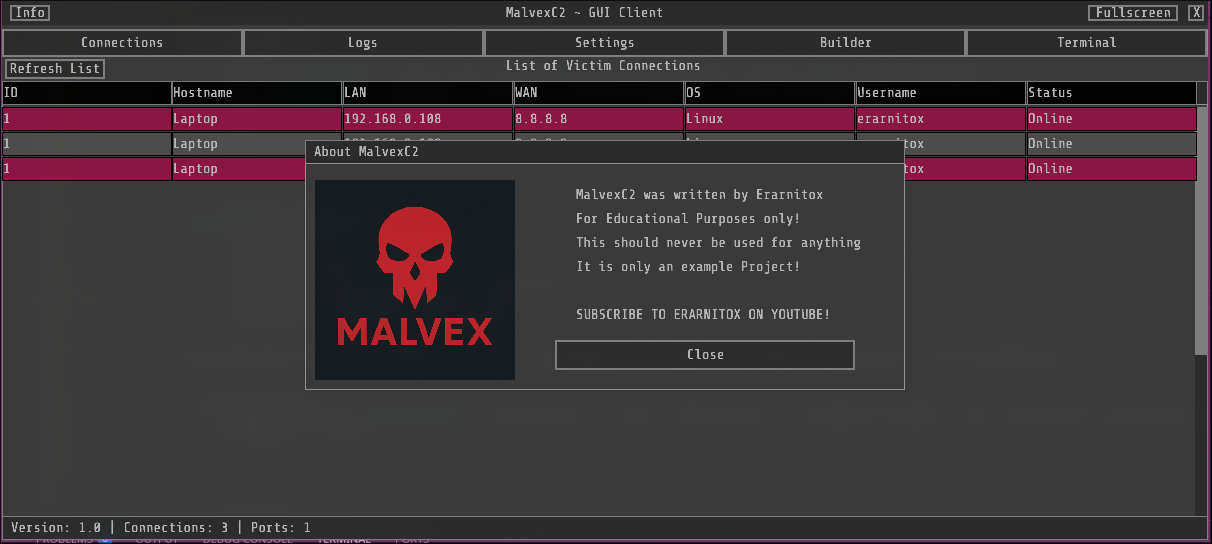
A simple C2 Framework written in modern C++
 s-retlaw/l4s_poc
Log4Shell (Cve-2021-44228) Proof Of Concept
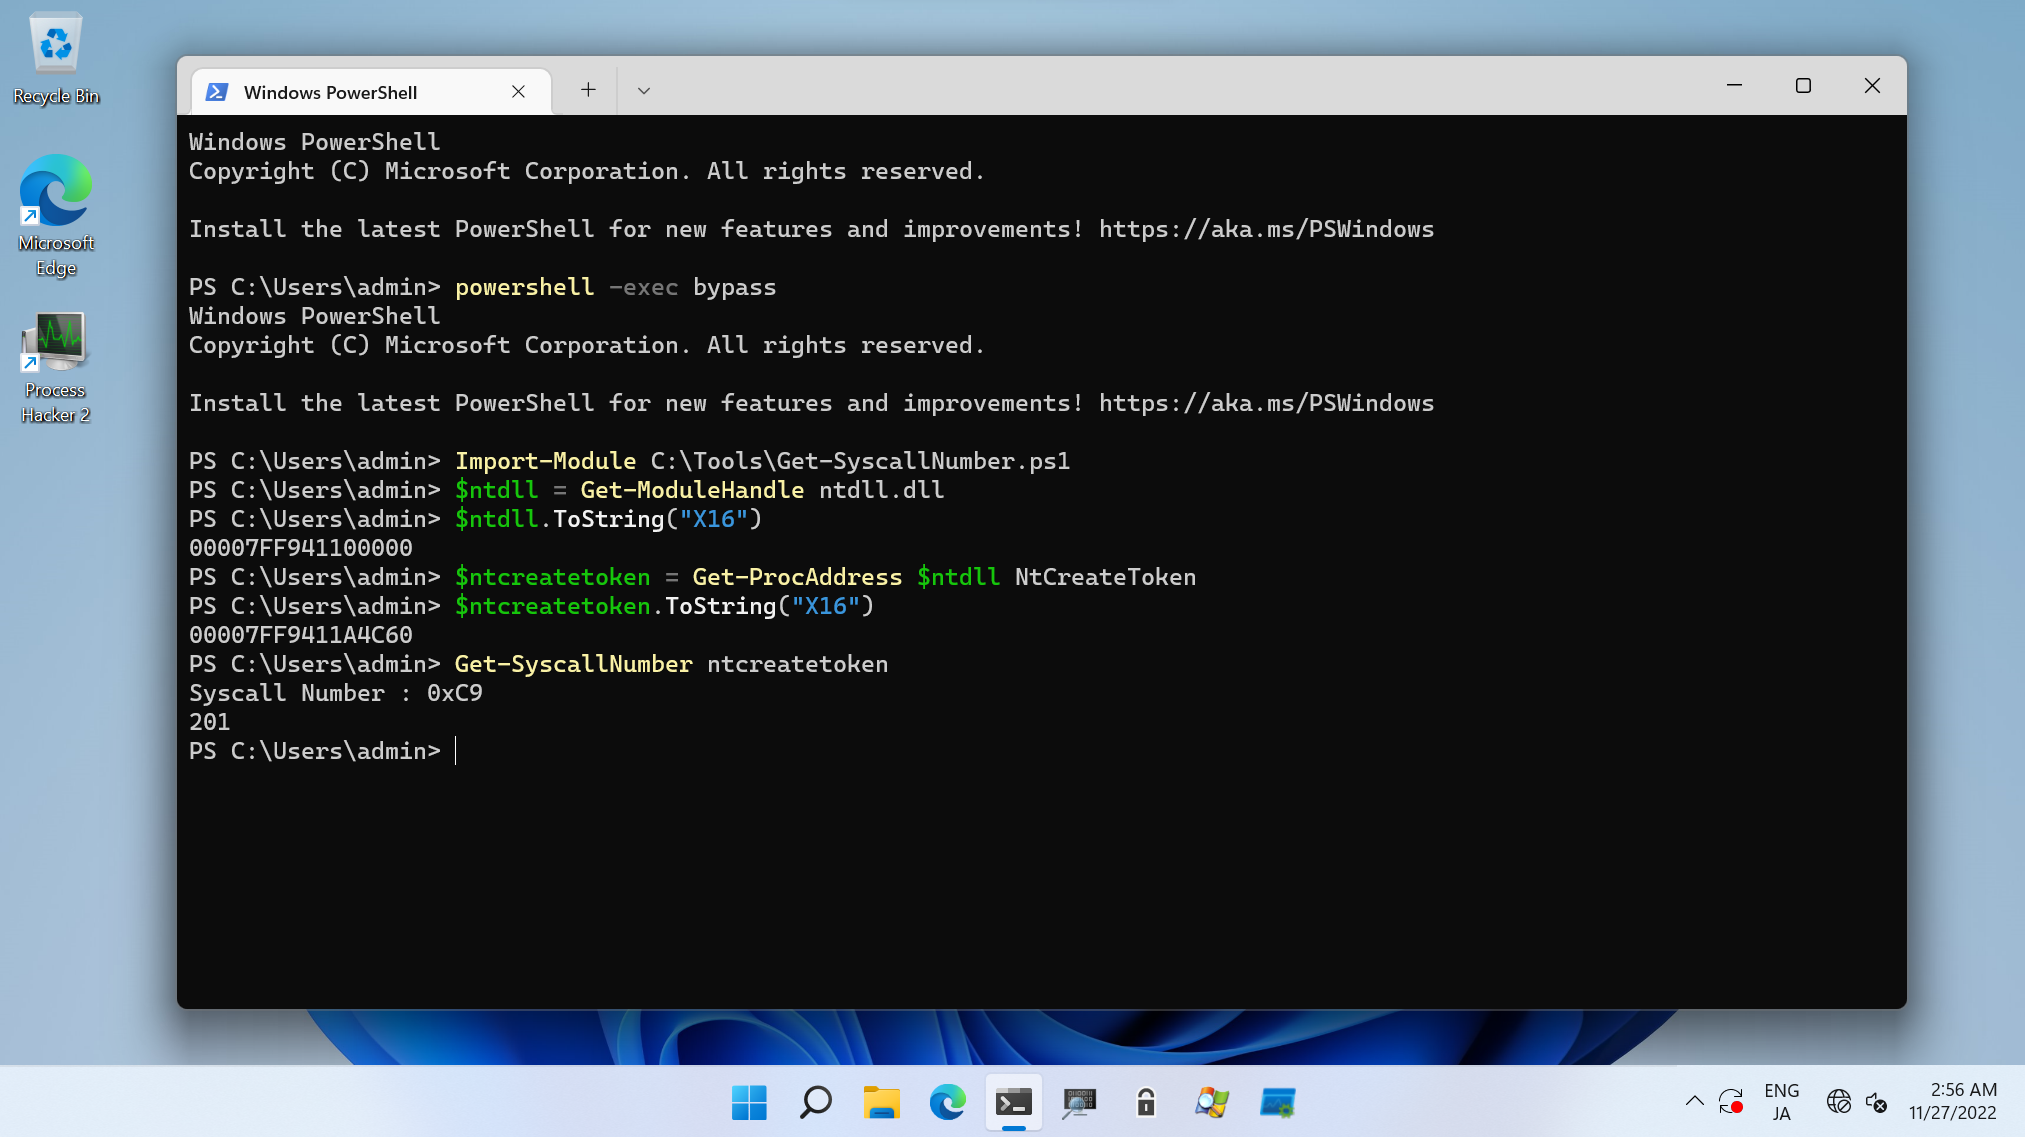 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 gmh5225/dropper
Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.
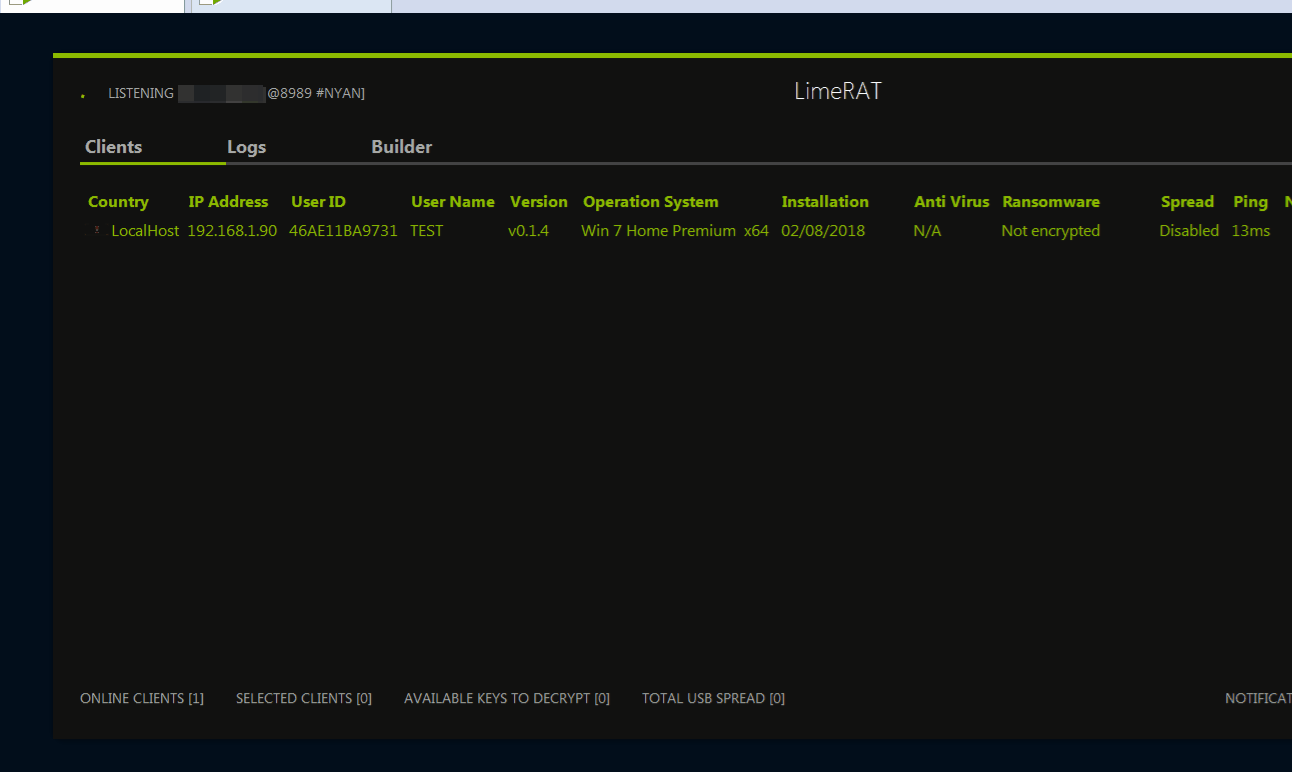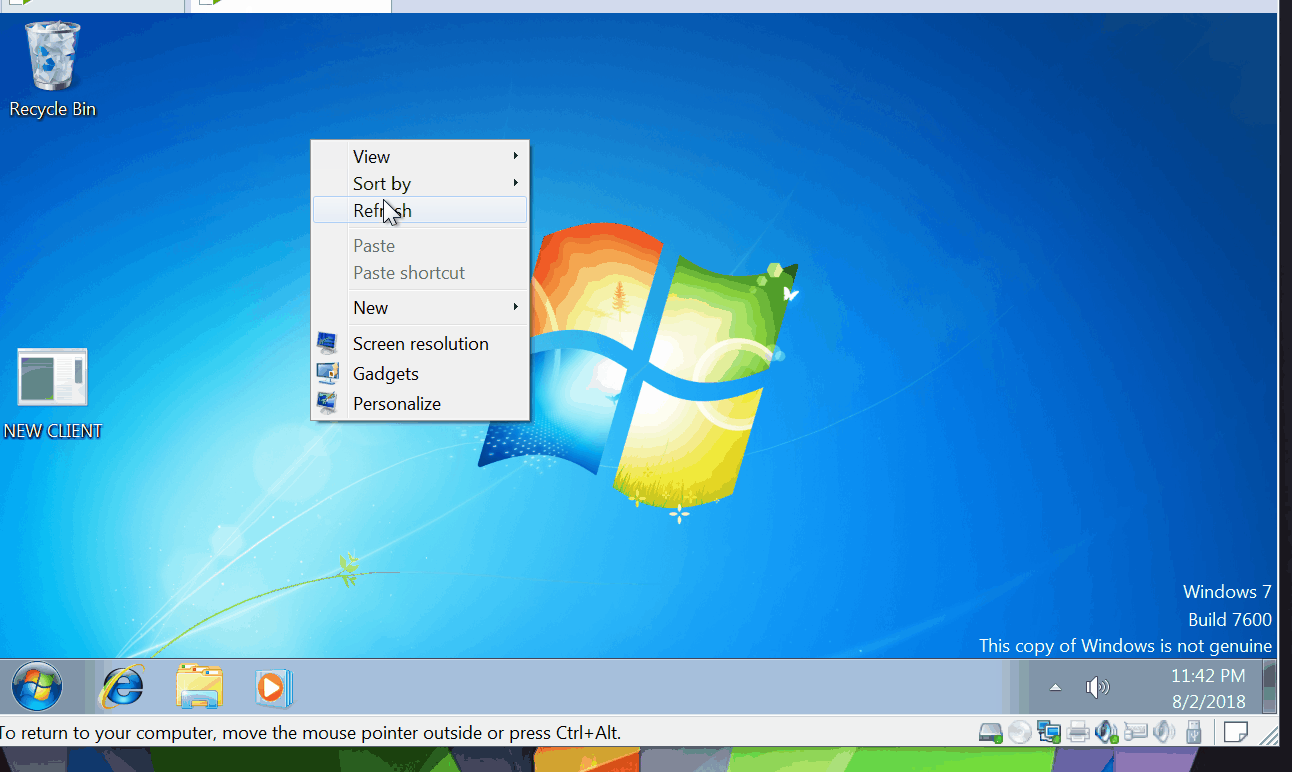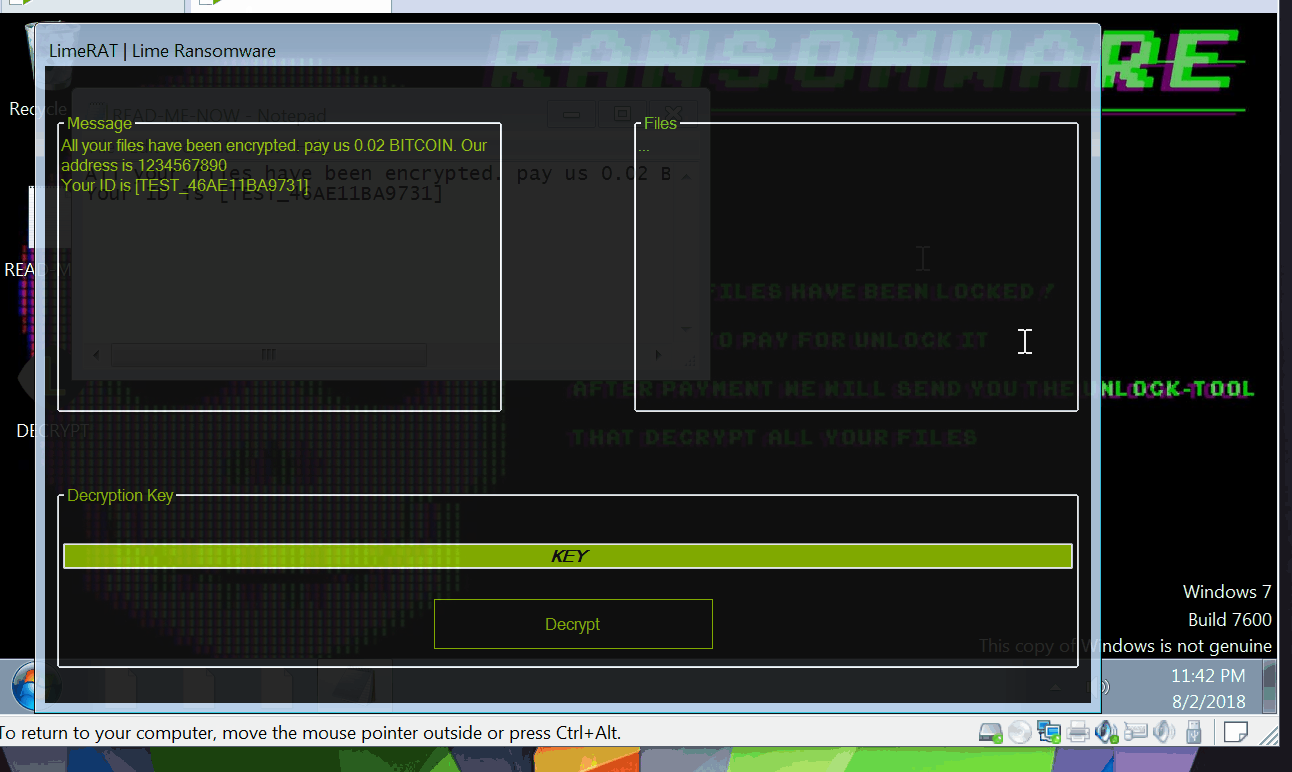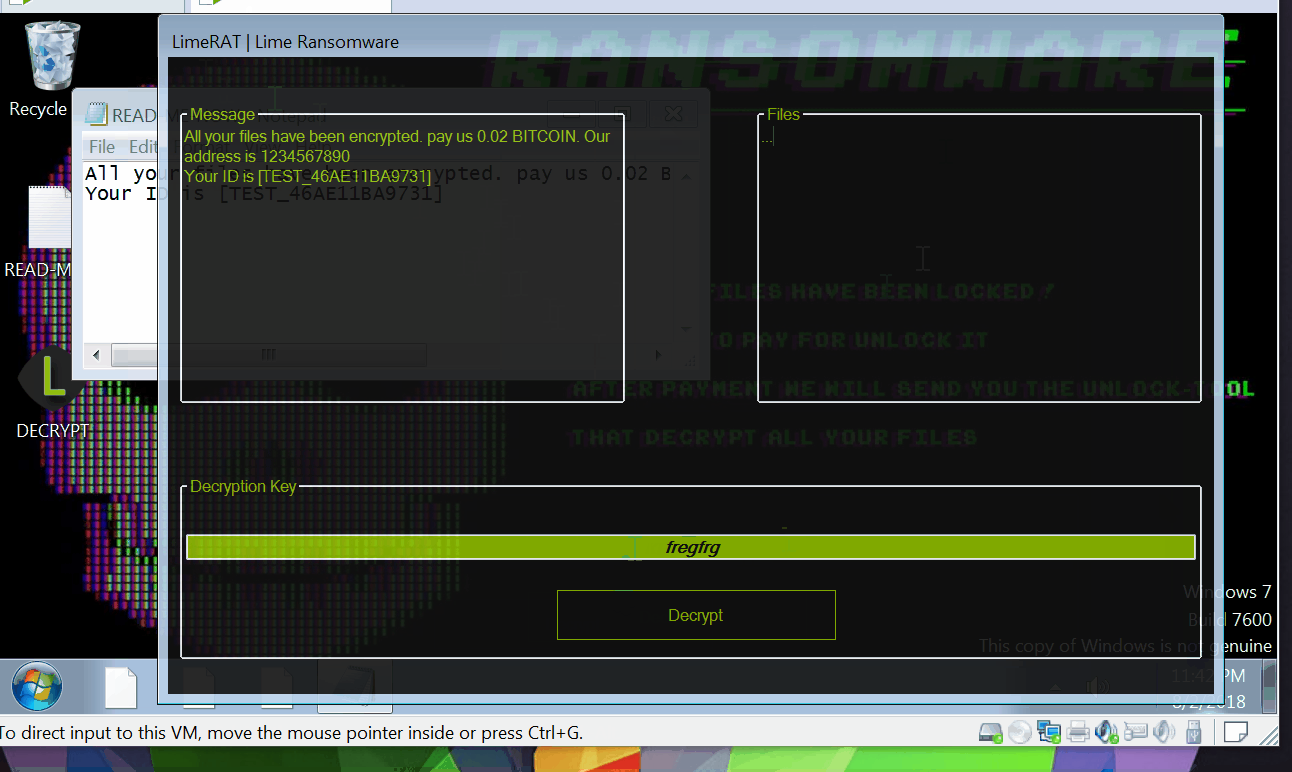 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 pulkin/esp8266-injection-example
Example project to demonstrate packet injection / sniffer capabilities of ESP8266 IC.
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
 bc-security/ironsharppack
IronSharpPack is a repo of popular C# projects that have been embedded into IronPython scripts that execute an AMSI bypass and then reflective load…
 i014n/pngloader
Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…