

CVE-2026-78006-POC
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
defensive-toolsexploitationpayload-development+7
4
deadexpl0it/cve-2026-78006-pocPOC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
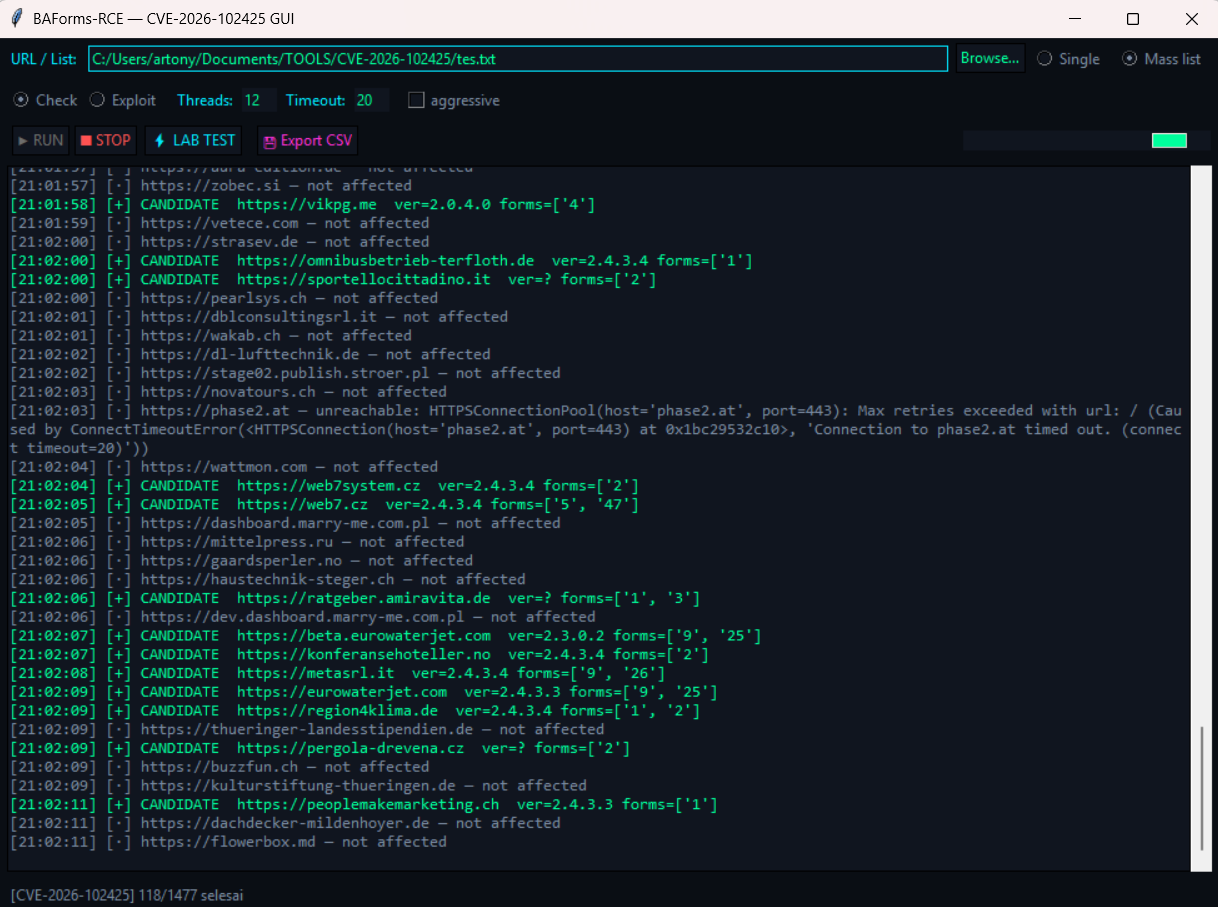 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
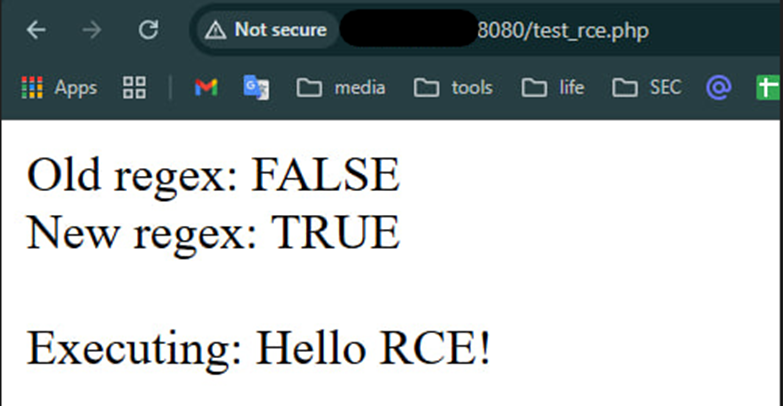 soltanali0/cve-2024-12877-exploit
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 ikow/php2shell-poc
CVE-2026-109618/109619 PHP session.upload_progress Exploit Research — POC & Analysis
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
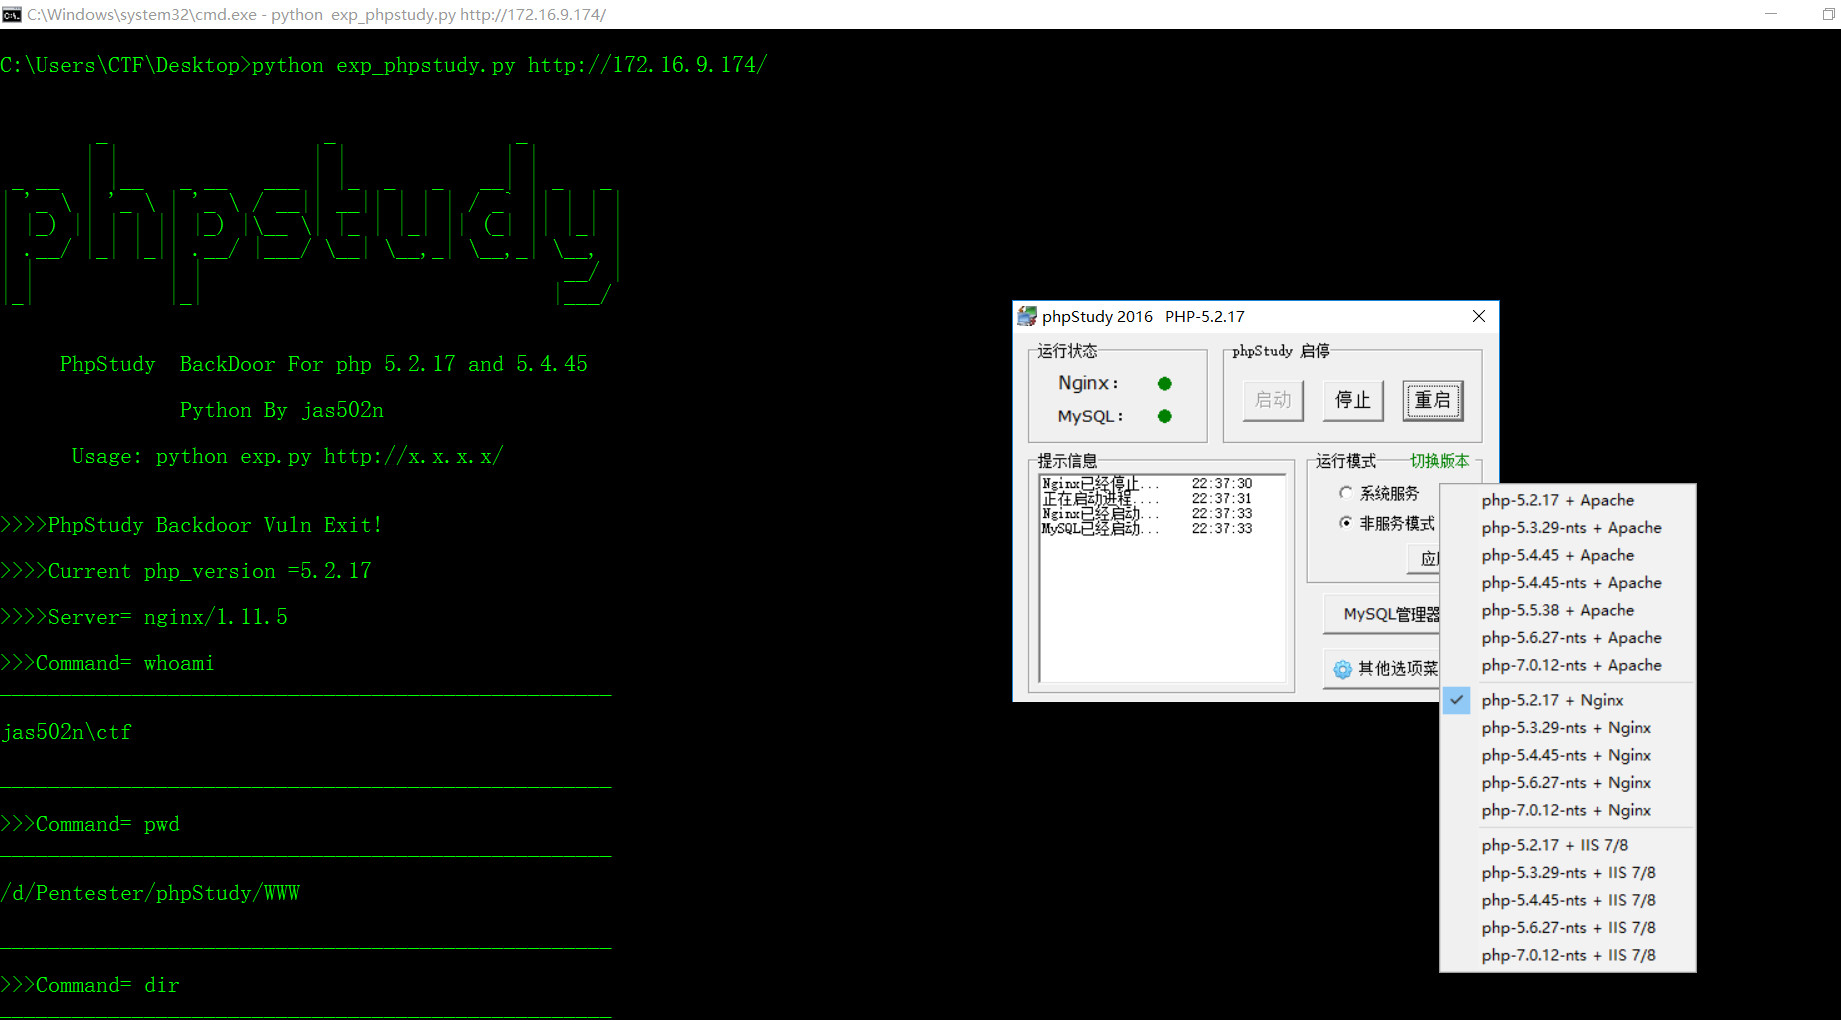 jas502n/phpstudy-backdoor
phpstudy dll backdoor for v2016 and v2018
 pwnvader/cve-2026-87902-poc-pwnvader
Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.
 sonerctnkya/cve-2022-30887
Proof-of-concept exploit for CVE-2022-30887, demonstrating remote code execution via file upload in Pharmacy Management System 1.0, with mitigation…
 tennc/webshell
This is a webshell open source project