
CVE-2021-3060
 anmolksachan/cve-2021-3060
CVE-2021-3060
command-and-controlexploitationpayload-development+3
anmolksachan/cve-2021-3060CVE-2021-3060
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
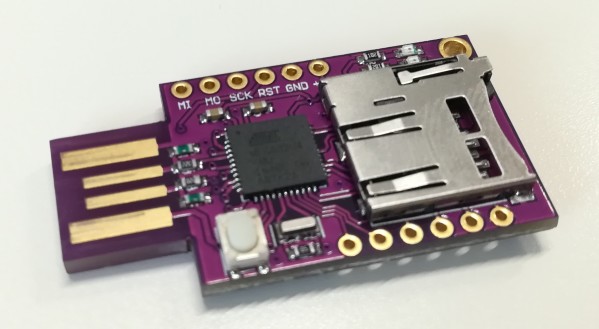 mharjac/bad_ducky
Rubber Ducky compatible clone based on CJMCU BadUSB HW.
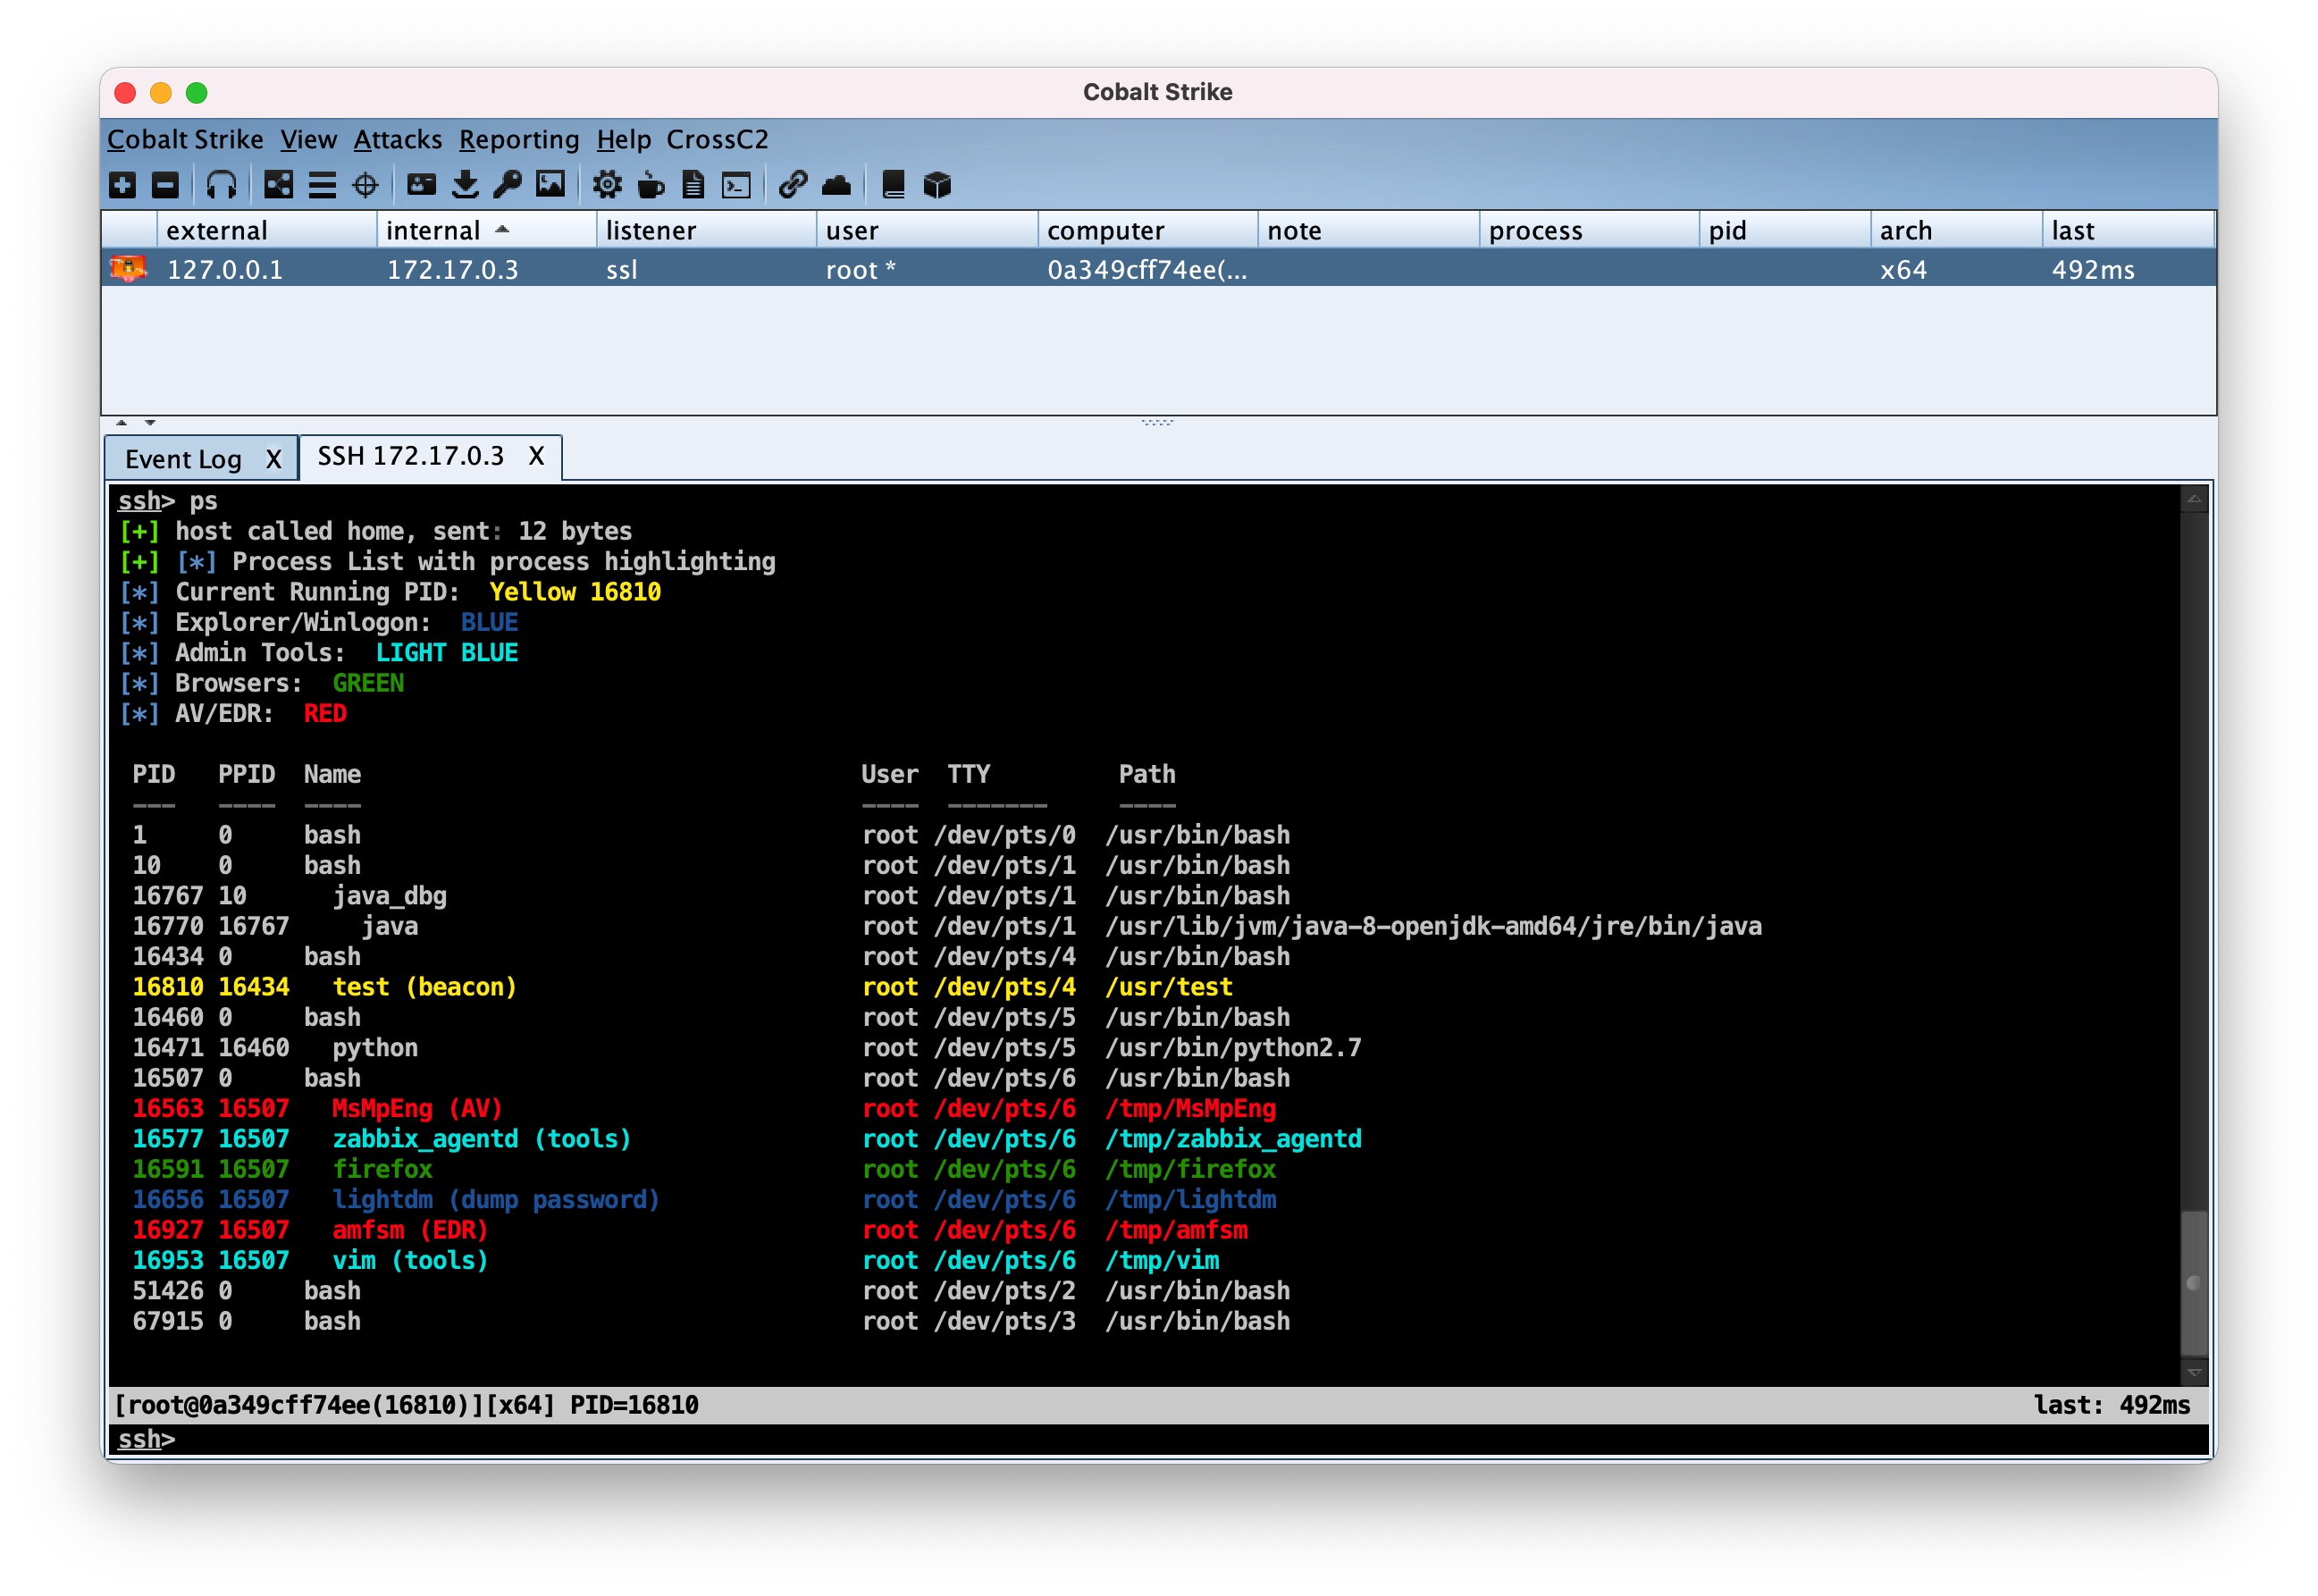 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 rkx1209/cve-2014-1303
CVE-2014-1303 (WebKit Heap based BOF) proof of concept for Linux
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 mr-un1k0d3r/thundershell
Python / C# Unmanaged PowerShell based RAT
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
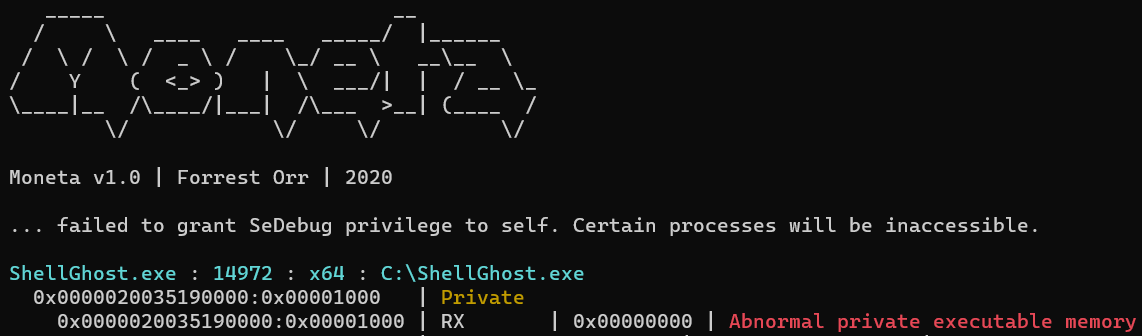 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 idov31/cronos
PoC for a sleep obfuscation technique leveraging waitable timers to evade memory scanners.
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 ionescu007/faxhell
A Bind Shell Using the Fax Service and a DLL Hijack
 lepotekil/msfmania
Python AV Evasion Tools
 gabemarshall/brosec
Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.