
Umbra
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
command-and-controleducationencryption-decryption-tools+6
135
h3xduck/umbraA LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 nabilboudra/cve-2017-5123
Educational demonstration of CVE-2017-5123 kernel exploit, ICMP-based rootkit command-and-control, and OS command injection vulnerable web…
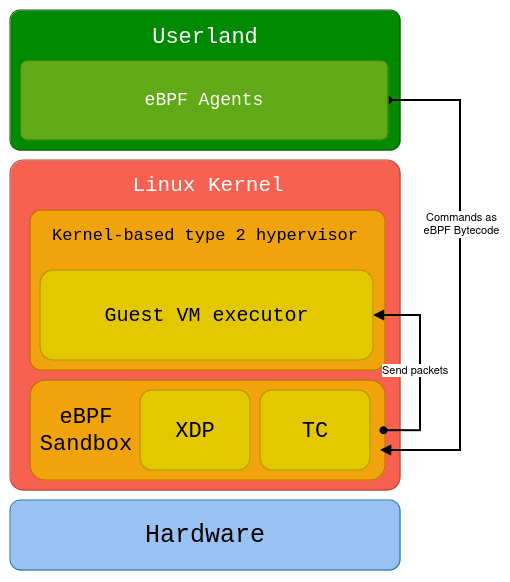 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 101010zyl/cve-2024-0582-dataonly
Data-only local privilege escalation exploit for Linux kernel io_uring CVE-2024-0582, using sprayed file structures and ext4_file_operations hooks to…
 0b0111100/2008
Linux kernel exploit implementations targeting CVE-2008-0600, CVE-2008-0900, and CVE-2008-4210, providing proof-of-concept code for privilege…
 panyu6325/cve-2015-1805
Proof-of-concept exploit for CVE-2015-1805, a Linux kernel vulnerability enabling local privilege escalation via a race condition in the pipe buffer…
 smarttfoxx/copyfail
CVE-2026-31431 (Copy Fail) PoC - Linux kernel page cache corruption via authencesn AF_ALG + splice()
 tc3650/cve-2026-43499-armv7
ARM32 Linux kernel privilege escalation exploit for CVE-2026-43499 (GhostLock futex UAF) targeting Huawei Watch 4 Pro with multiple exploitation…
 geniuszly/cve-2024-0582
Proof-of-concept exploit for CVE-2024-0582, a Linux kernel vulnerability. Leverages io_uring for buffer manipulation, KASLR leak, and privilege…
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 vulnquest58/dirtyclone-exploit
CVE-2026-46331 — Linux Kernel Local Privilege Escalation TC pedit + IPsec TEE Page Cache Corruption · Affected kernels: ≤ 6.12.9
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
 rvzsec/cve-2026-31431
PoC exploits for CVE-2026-31431, a Linux kernel LPE via authencesn page cache write, providing unprivileged user to root escalation on most distros…
 boos4721/copyfail-rs
Rust exploit for CVE-2026-31431, a Linux kernel page-cache write primitive via AF_ALG splice, enabling privilege escalation to root through…
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 morton-li/copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel privilege escalation, with x86_64, AArch64, and C payloads to obtain root on affected…