
godofwar
 kingsabri/godofwar
GodOfWar - Malicious Java WAR builder with built-in payloads
exploitationpayload-developmentpayload-generation+3
kingsabri/godofwarGodOfWar - Malicious Java WAR builder with built-in payloads
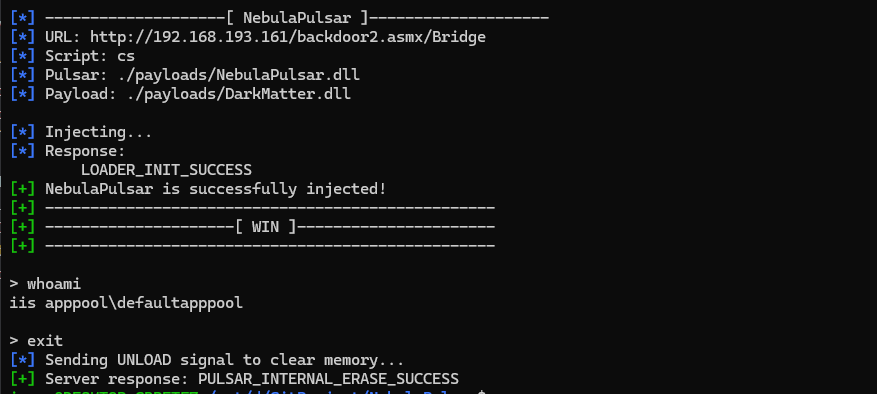 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 mbechler/marshalsec
Java deserialization vulnerability exploitation tool with payload generators for multiple marshallers (Jackson, XStream, SnakeYAML) and JNDI…
 breenmachine/javaunserializeexploits
Exploit Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS using Python PoC scripts and crafted HTTP requests.
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 pimps/ysoserial-modified
That repository contains my updates to the well know java deserialization exploitation tool ysoserial.
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 abdoghazy2015/ofbiz-cve-2023-49070-rce-poc
Pre-auth RCE proof-of-concept for Apache OFBiz CVE-2023-49070, exploiting XML-RPC Java deserialization to achieve remote code execution on vulnerable…
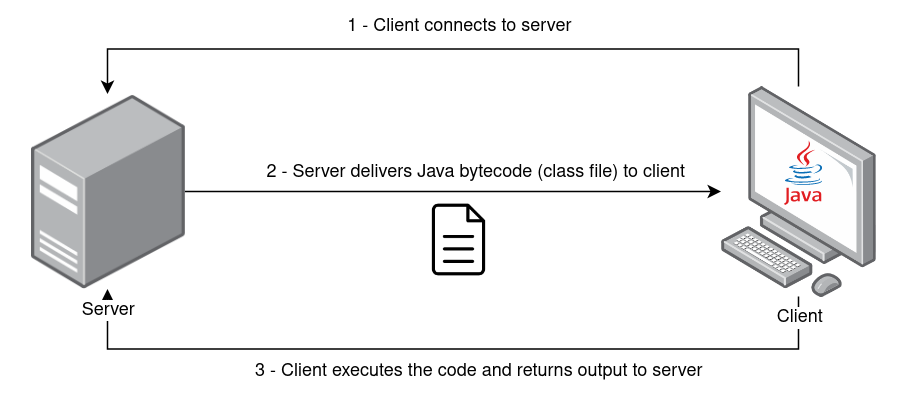 joaovarelas/java-remote-class-loader
Client-server tool for remotely loading and executing Java bytecode via ClassLoader and Reflect API, with ChaCha20 encryption and keepalive…
 ianxtianxt/cve-2015-7501
Educational lab for understanding Java deserialization vulnerabilities with PoC exploits for JBoss CVEs, gadget chain analysis, and a vulnerable HTTP…
 guhe120/cve20131491-jit
Proof-of-concept exploit for CVE-2013-1491 using Java JIT-Spray technique to demonstrate memory corruption in JRE 7u17 on Windows 7 32-bit.
 synacktiv/mojarragadget
Proof-of-concept exploit for a Java gadget chain in the Mojarra library, demonstrating deserialization vulnerability exploitation for versions 2.3…
 geneblue/cve-2014-7911-exp
exploit for cve-2014-7911; android; java deserialization ;system privilege;ace;
 gutierre0x80/cve-2026-59827
Technical analysis and proof of concept for CVE-2026-59827, a critical unsafe Java deserialization vulnerability in Metabase leading to remote code…
 mouadk/parquet-rce-poc-cve-2025-30065
Proof-of-concept exploit for CVE-2025-30065 demonstrating remote class instantiation and SSRF via malicious Parquet files in Java applications.
 mattb709/cve-2025-24813-poc-apache-tomcat-rce
A Python proof-of-concept exploit for CVE-2025-24813 - Unauthenticated RCE in Apache Tomcat (v9.0.0-9.0.98/10.1.0-10.1.34/11.0.0-11.0.2) via…
 ibonok/cve-2026-33439-poc
Exploit for OpenAM pre-auth RCE (CVE-2026-33439) using a Java deserialization gadget chain to execute commands and return output directly in the HTTP…
 velessecurity/cve-2020-14882-weblogic-analysis
Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.