

Invisi-Shell
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
defensive-toolsexploitationids-ips-evasion+9
1.3k
omerya/invisi-shellHide your Powershell script in plain sight. Bypass all Powershell security features
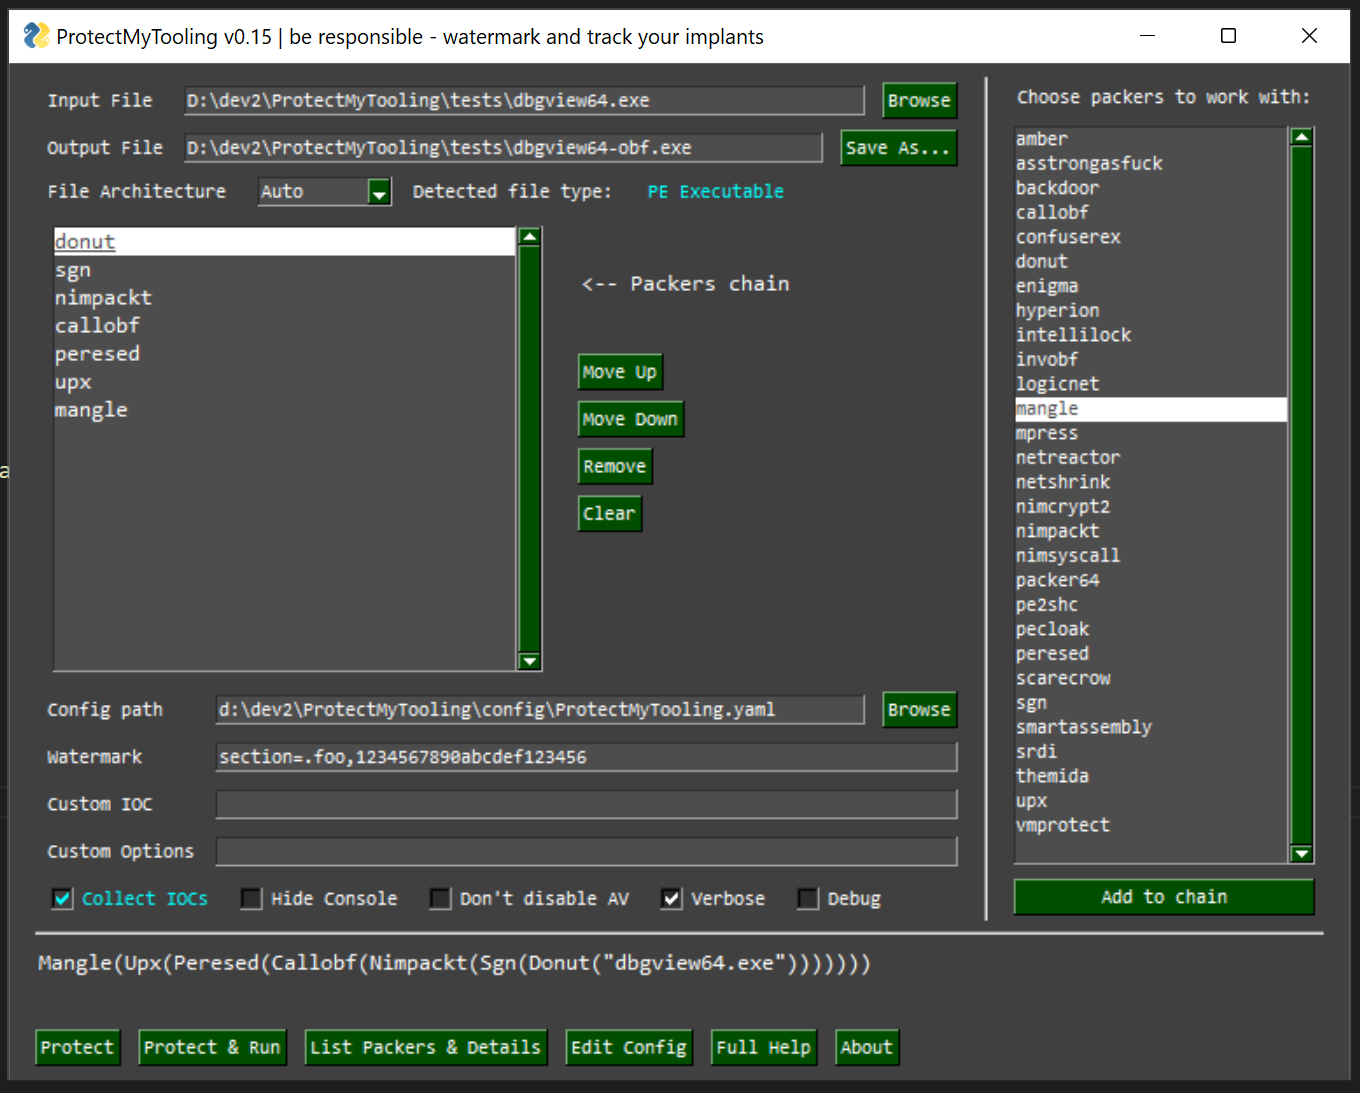 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
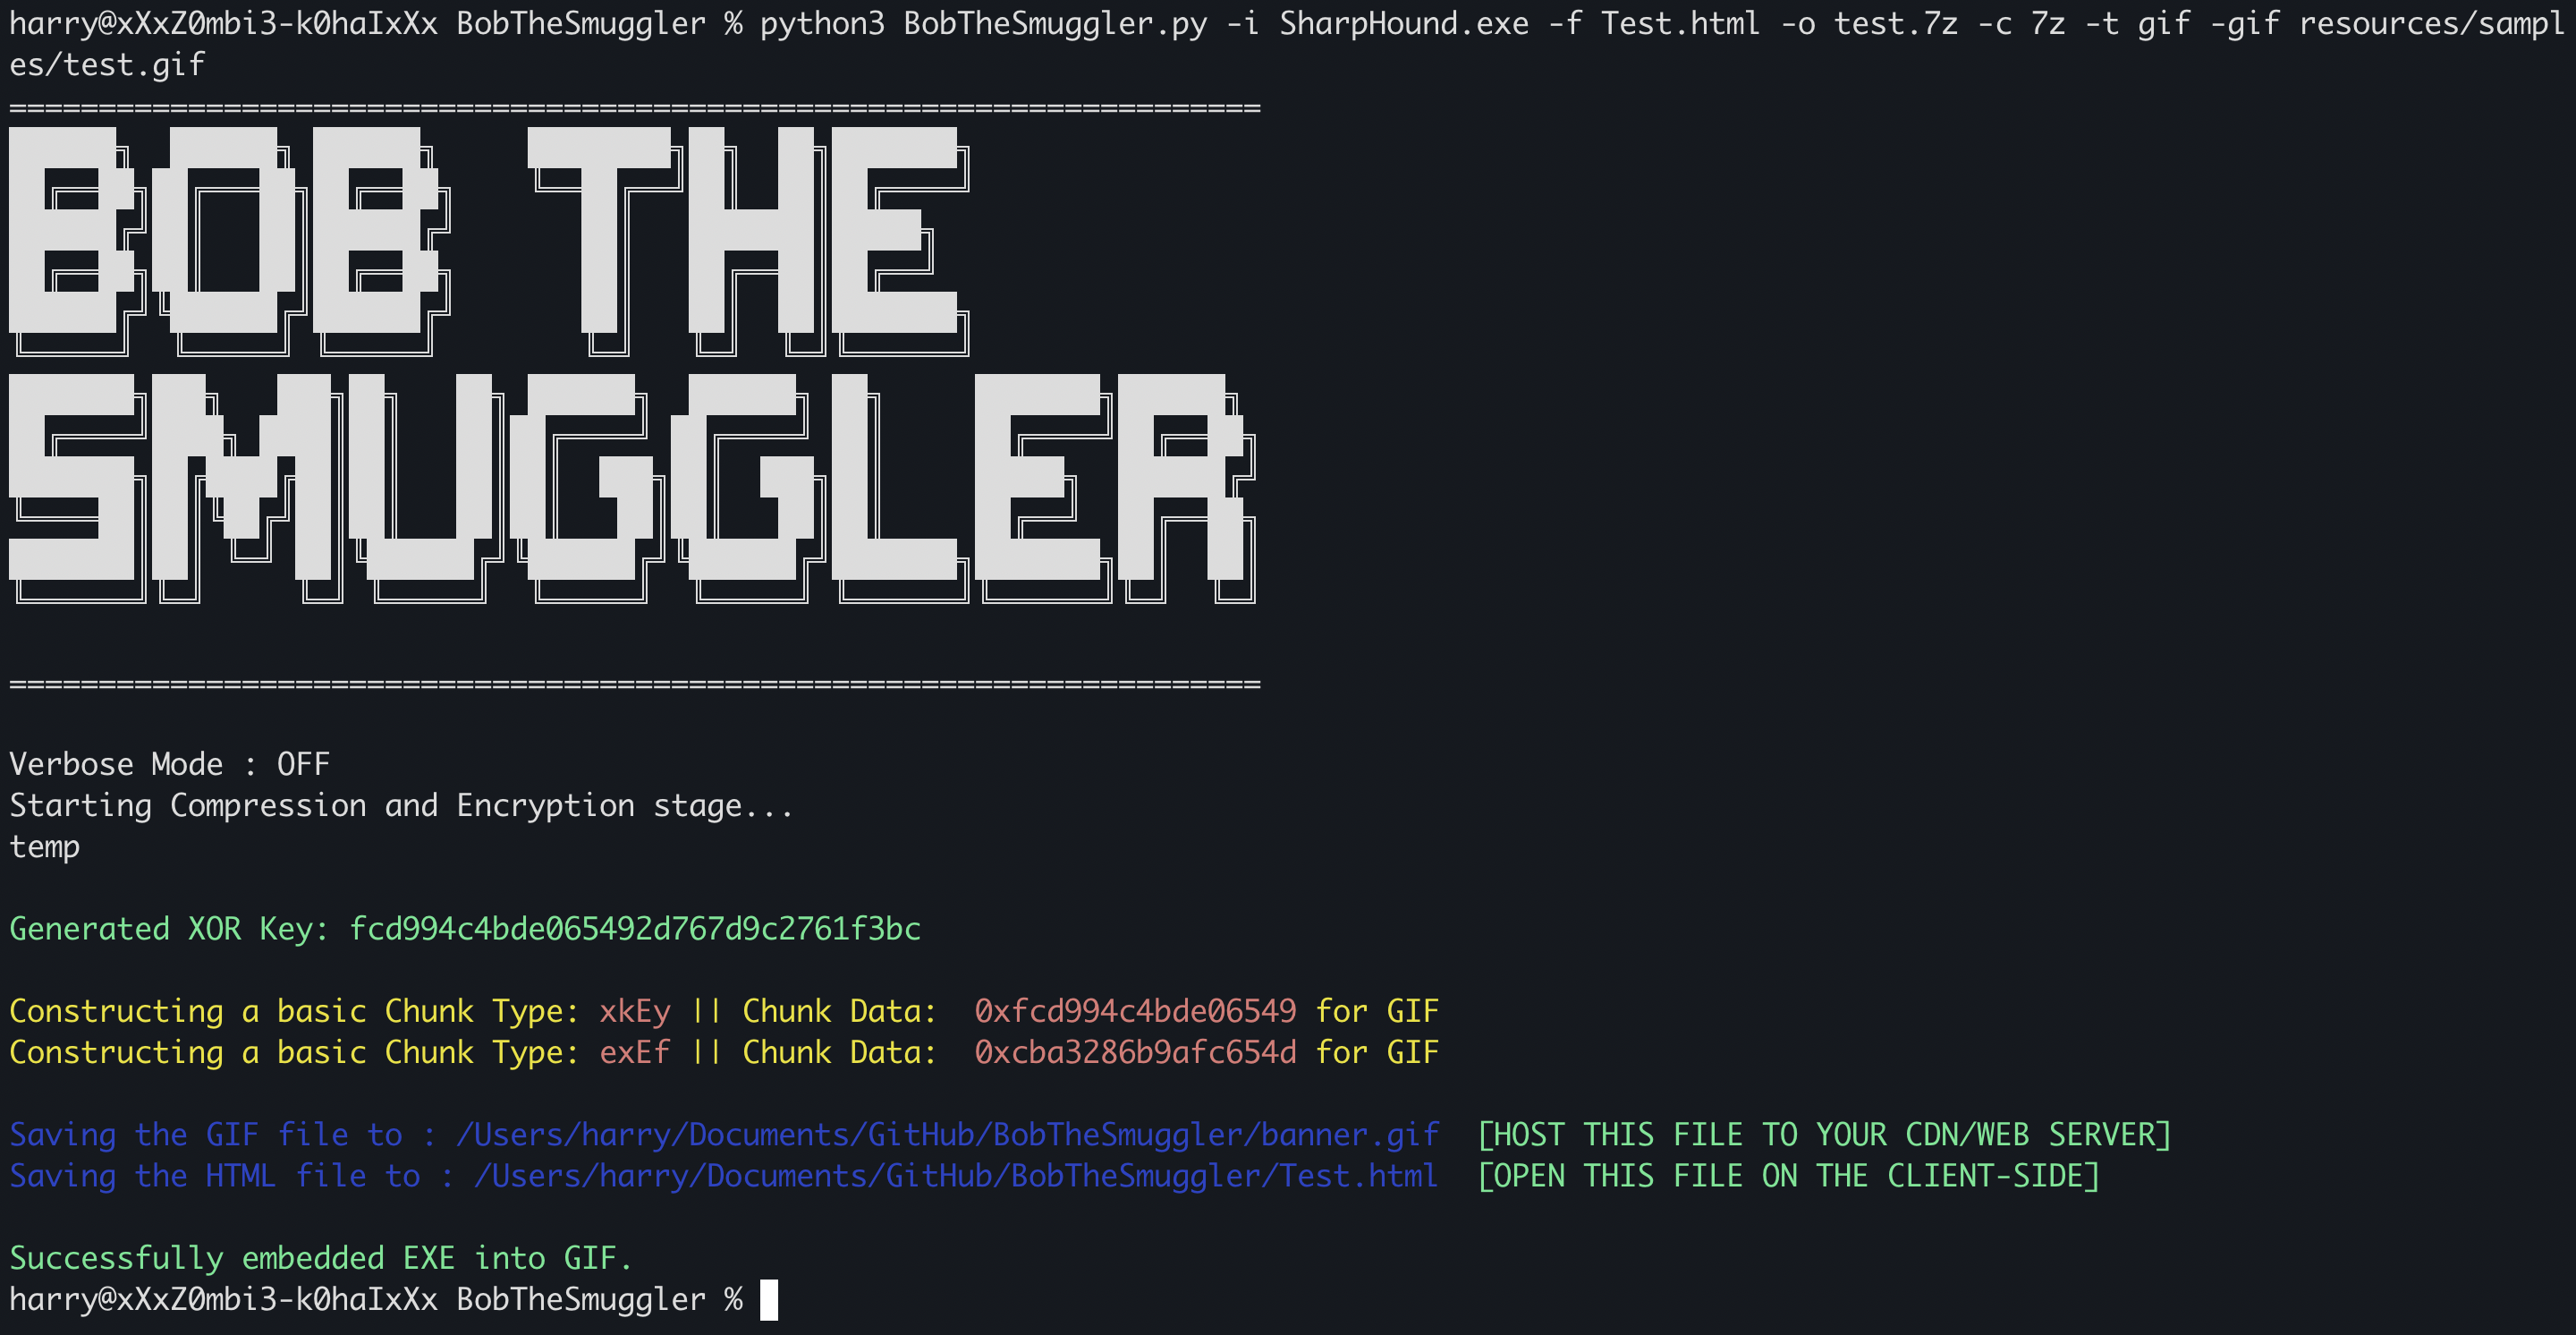 thecyb3ralpha/bobthesmuggler
"Bob the Smuggler": A tool that leverages HTML Smuggling Attack and allows you to create HTML files with embedded 7z/zip archives. The tool would…
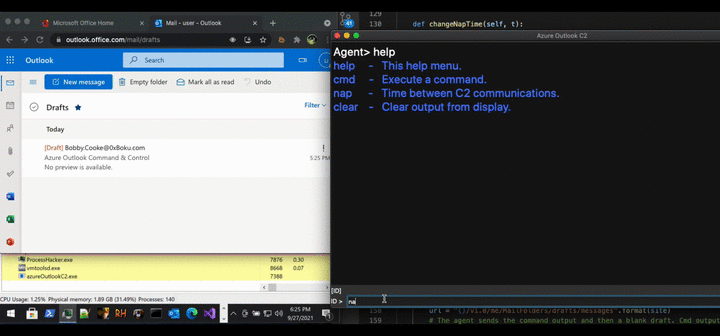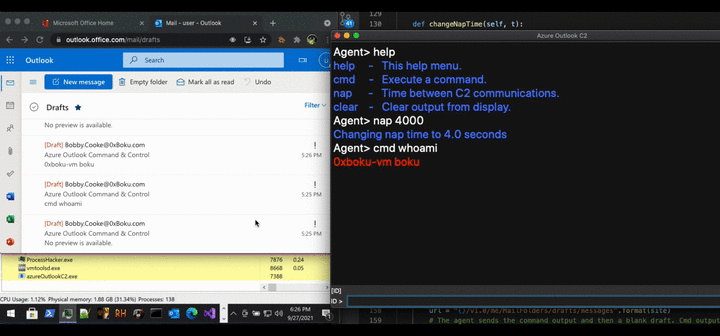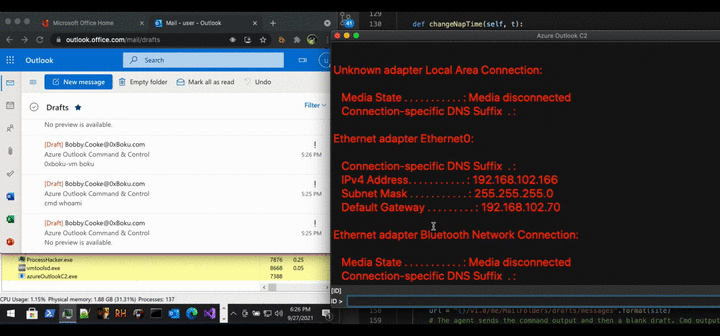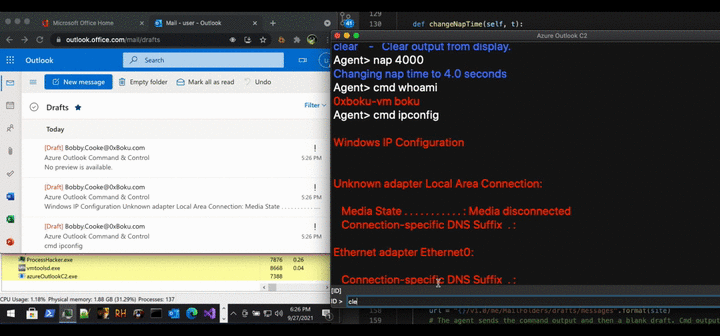 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…

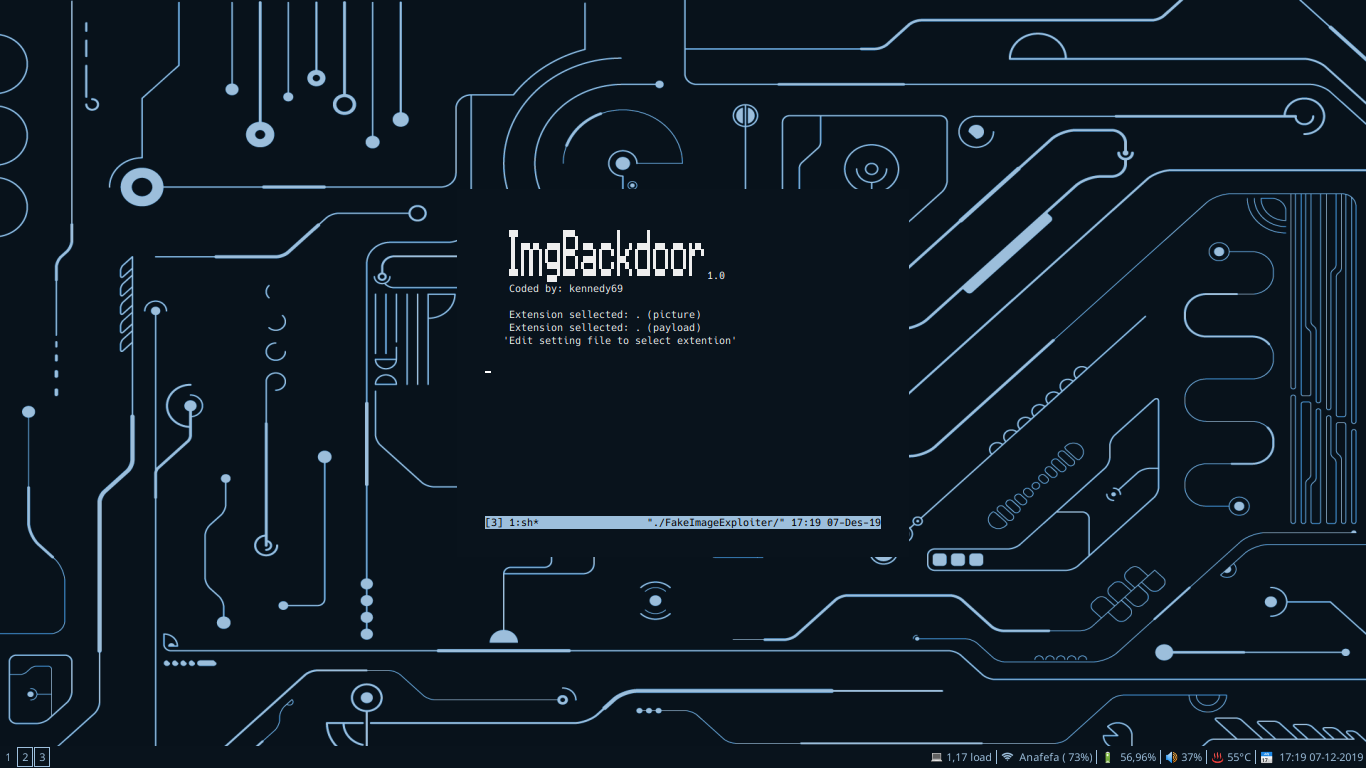 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 hazcod/ransomwhere
A PoC ransomware sample to test out your ransomware response strategy.
 smokeme/airstrike
Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
 portswigger/css-the-bomb-inside-your-inbox
All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
 d4vinci/palsy-virus
Python virus that will make your pc paralyzed once it opened :D
 fredbrave/cve-2022-46169-cacti-1.2.22
This is a exploit of CVE-2022-46169 to cacti 1.2.22. This exploit allows through an RCE to obtain a reverse shell on your computer.
 psycostea/pi-zero-2w-bad-usb
Configure your Pi Zero 2W to be a BadUSB
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
 pwnaccelerator/stagefright-cve-2015-3864
PoC - Binary patches for CVE-2015-3864 (NOT for production, use at your own risk)
 horkimhab/cve-2026-0001
CVE-2026-0001. Do with your own risk
 dedsec-47/metasploit-exploits-cve-2023-6710
Welcome to the Metasploit Exploits Repository, your go-to resource for a comprehensive collection of cutting-edge exploits designed for penetration…