

PiX-C2
 robertdavis1/pix-c2
Ping Exfiltration Command and Control (PiX-C2)
command-and-controlnetwork-securitypacket-sniffing-analysis+3
31
robertdavis1/pix-c2Ping Exfiltration Command and Control (PiX-C2)
 nabilboudra/cve-2017-5123
Educational demonstration of CVE-2017-5123 kernel exploit, ICMP-based rootkit command-and-control, and OS command injection vulnerable web…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 jimywork/cromos
Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.
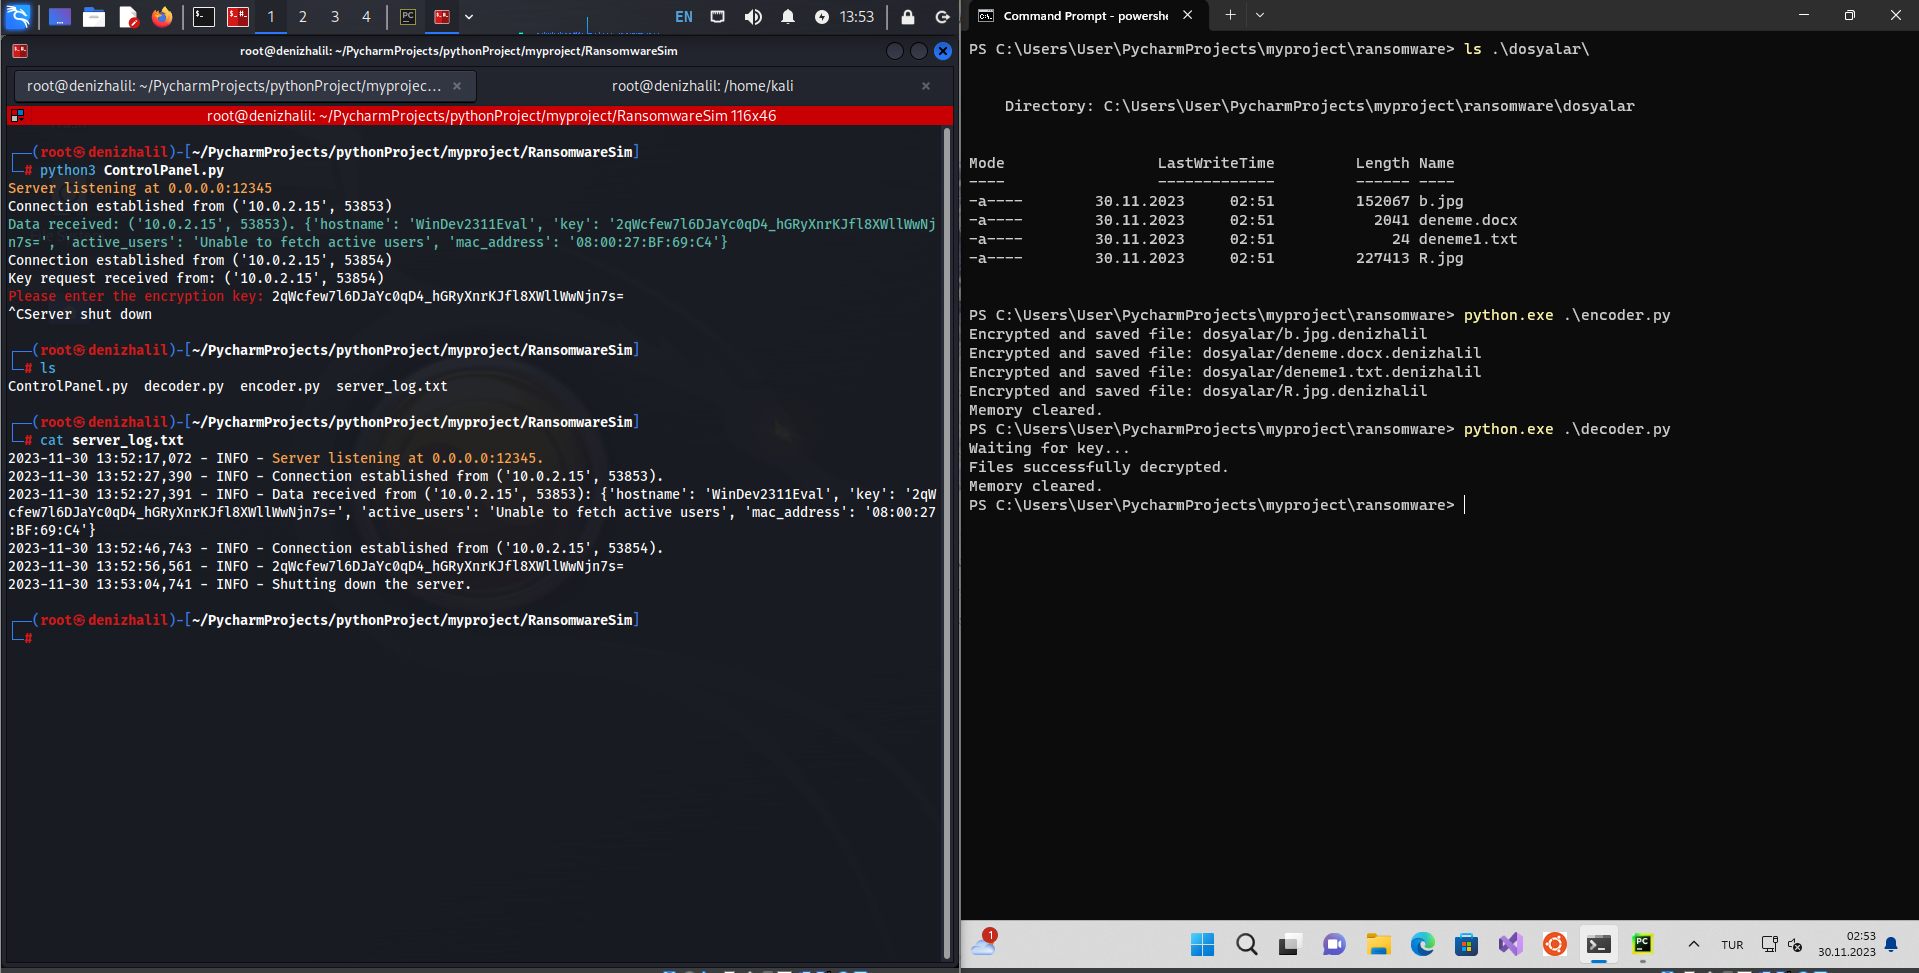 halildeniz/ransomwaresim
Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.
 tadash10/exploiting-cve-2021-44228-log4shell-in-a-banking-environment
Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.
 muhammad-ali007/follina_msdt_cve-2022-30190
Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…
 cotherm/cve-2025-25706
Detailed CVE-2025-25706 proof-of-concept demonstrating authenticated remote code execution via command injection in ProApps ping functionality,…
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…
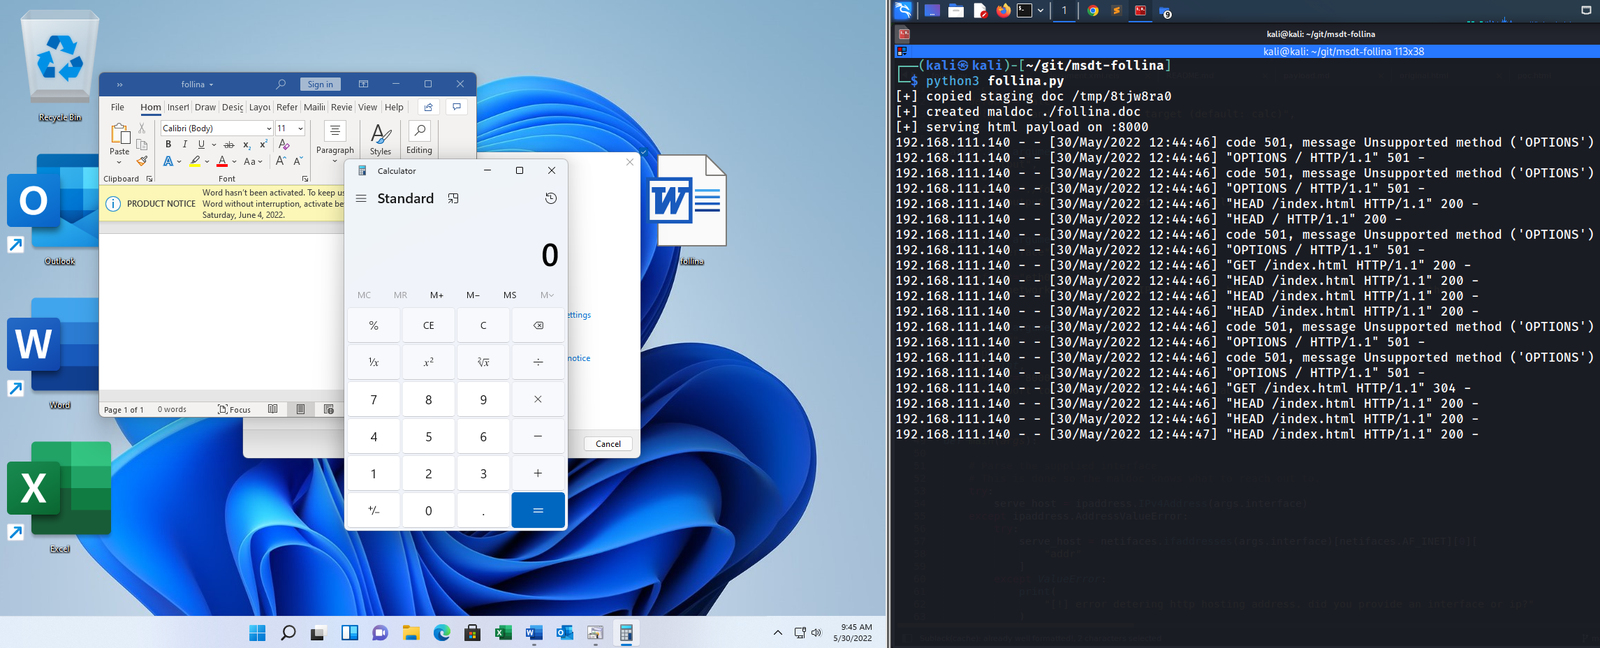 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
 accenture/codecepticon
.NET/PowerShell/VBA Offensive Security Obfuscator
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR