
frida-c2-mcp
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
android-securitycommand-and-controldynamic-analysis-sandboxing+8
65
s4dp4nd4/frida-c2-mcpAgentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 w0wbox/cve-2023-40448
poc for CVE-2023-40448 (under construction) ,This could probably be a piece for a jailbreak
 verygenericname/cve-2021-30955-poc-ipa
Proof-of-concept IPA for CVE-2021-30955, targeting iOS 15.0-15.2b1, demonstrating a local privilege escalation vulnerability.
 3h6-1/cve-2021-30862
Write-up and proof of concepts for CVE-2021-30862, 1-click RCE bug in iOS iTunes U
 theofficialflow/h-encore
Fully chained kernel exploit for the PS Vita on firmwares 3.65-3.68
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 alephsecurity/initroot
Motorola Untethered Jailbreak: Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 bmax121/apatch
The patching of Android kernel and Android system
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
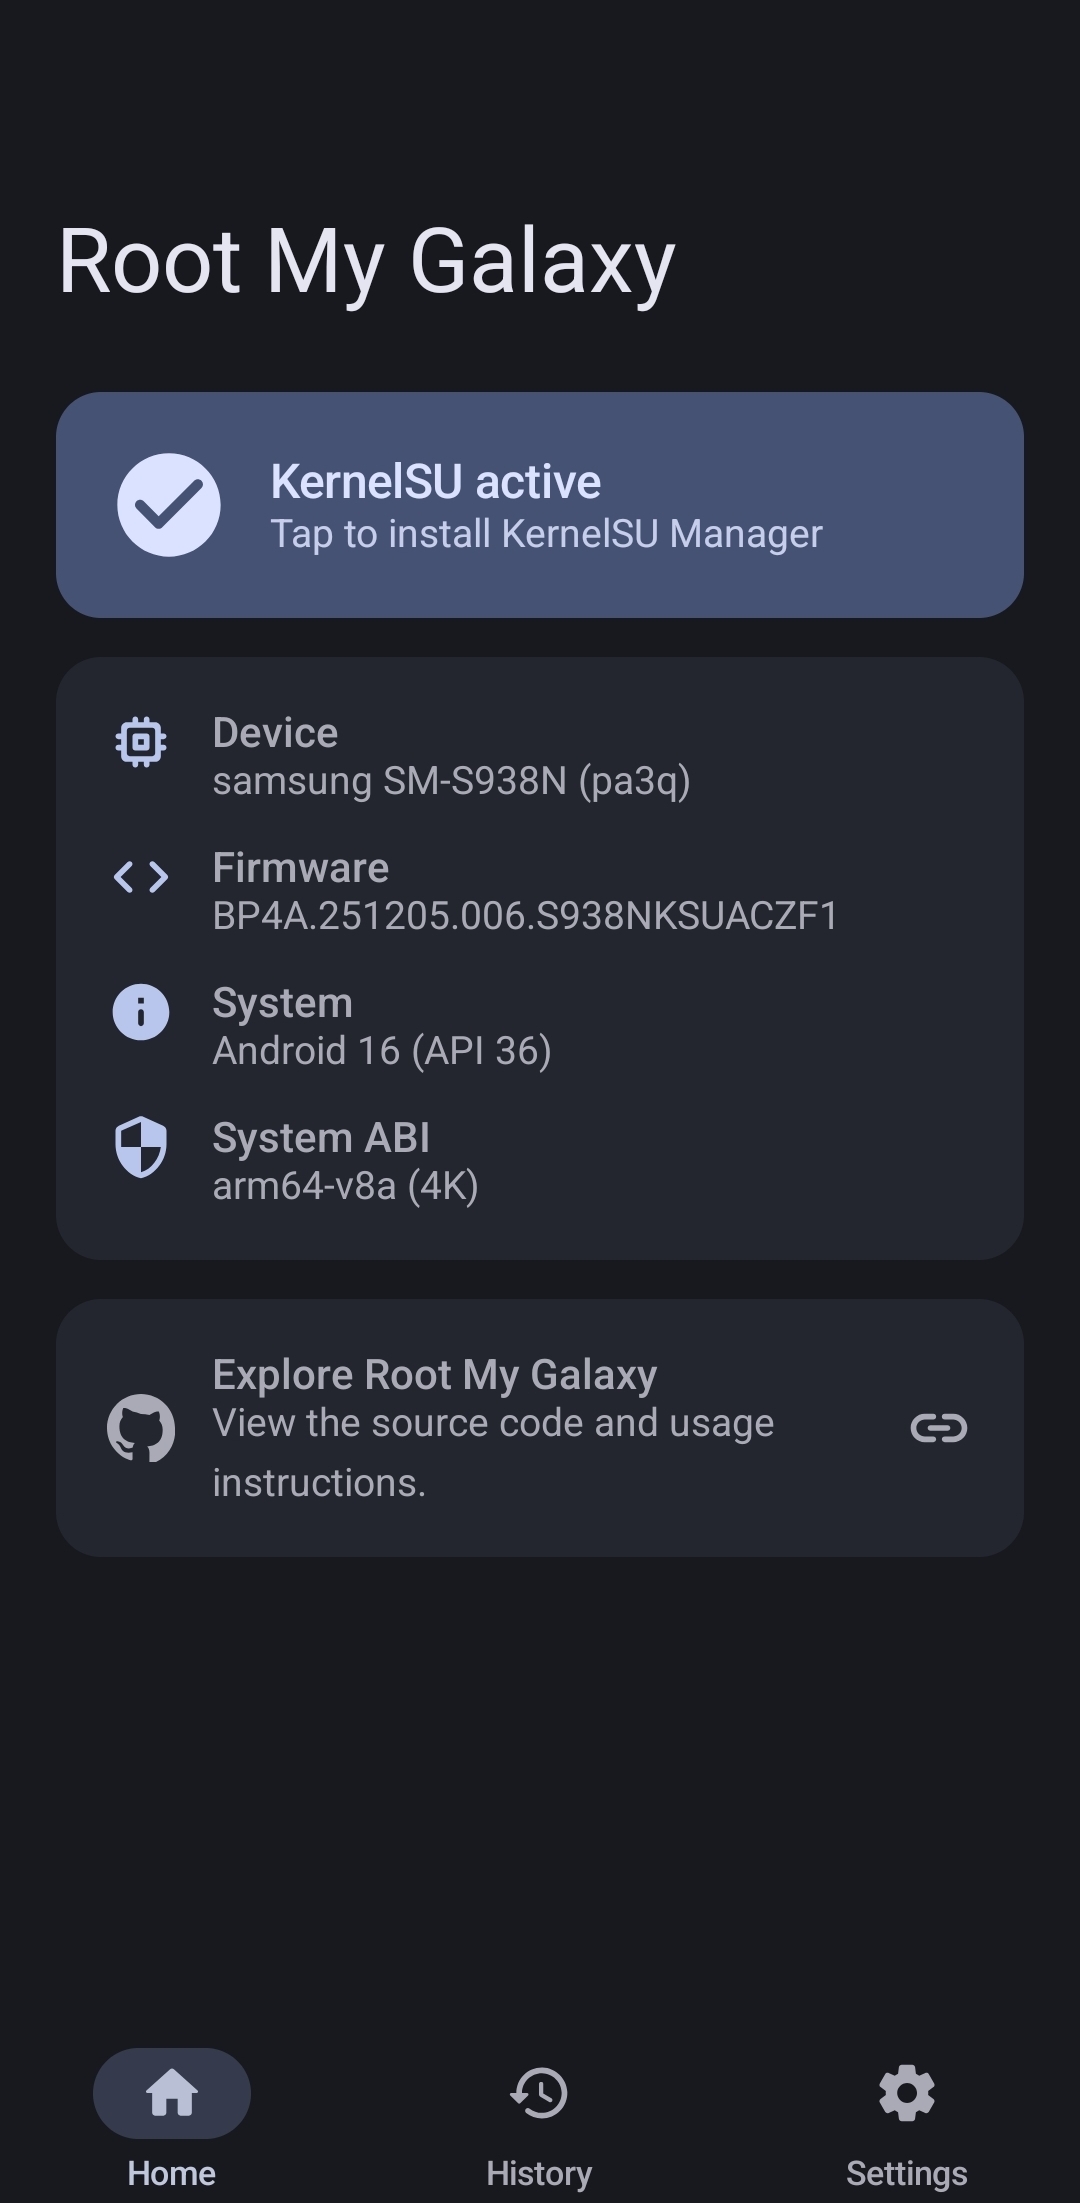 busung-dev/root-my-galaxy
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 m4sc3r4n0/evil-droid
Framework to create, generate, and embed APK payloads for Android penetration testing, leveraging Metasploit for exploitation and Apktool for…
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 sensepost/kwetza
Python script to inject existing Android applications with a Meterpreter payload.
 mwsrc/betterandrorat
Android Remote Access Trojan
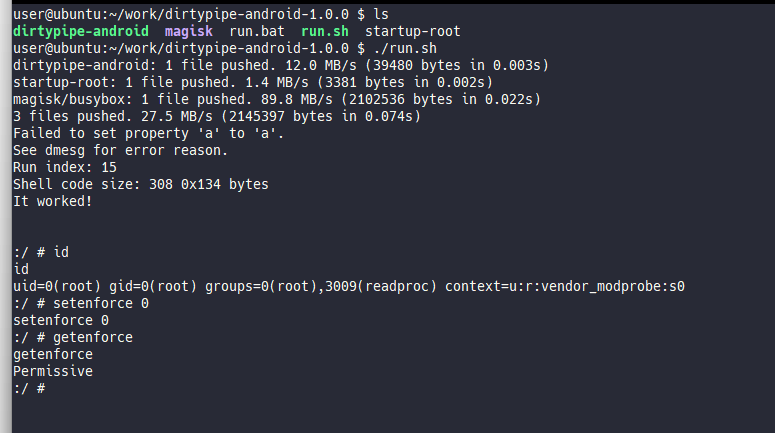 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 davidbuchanan314/nxloader
My first Android app: Launch Fusée Gelée payloads from stock Android (CVE-2018-6242)