
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
99 results
DLLHSC preview

DLLHSC

GitHubctxis/dllhsc

Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
binary-analysisexploitationpayload-development+1
158
6 years ago
DllShimmer preview

DllShimmer

GitHubprint3m/dllshimmer

Weaponize DLL hijacking easily. Backdoor any function in any DLL.
adversarial-attackpayload-developmentpenetration-testing+2
7631 year ago
PrintSpoofer-ReflectiveDLL preview

PrintSpoofer-ReflectiveDLL

GitHubjonyfilc/printspoofer-reflectivedll

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
exploitationlateral-movementpayload-development+4
22 months ago
DLLirant preview

DLLirant

GitHubredteamsocietegenerale/dllirant

DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.

binary-analysisdynamic-code-analysisexploitation+3
5033 years ago
RemoteDLLInjector preview

RemoteDLLInjector

GitHubal1ex/remotedllinjector

RemoteDLLInjector
exploitationpayload-developmentpenetration-testing+3
96 years ago
ExportHider preview

ExportHider

GitHubfrkngksl/exporthider

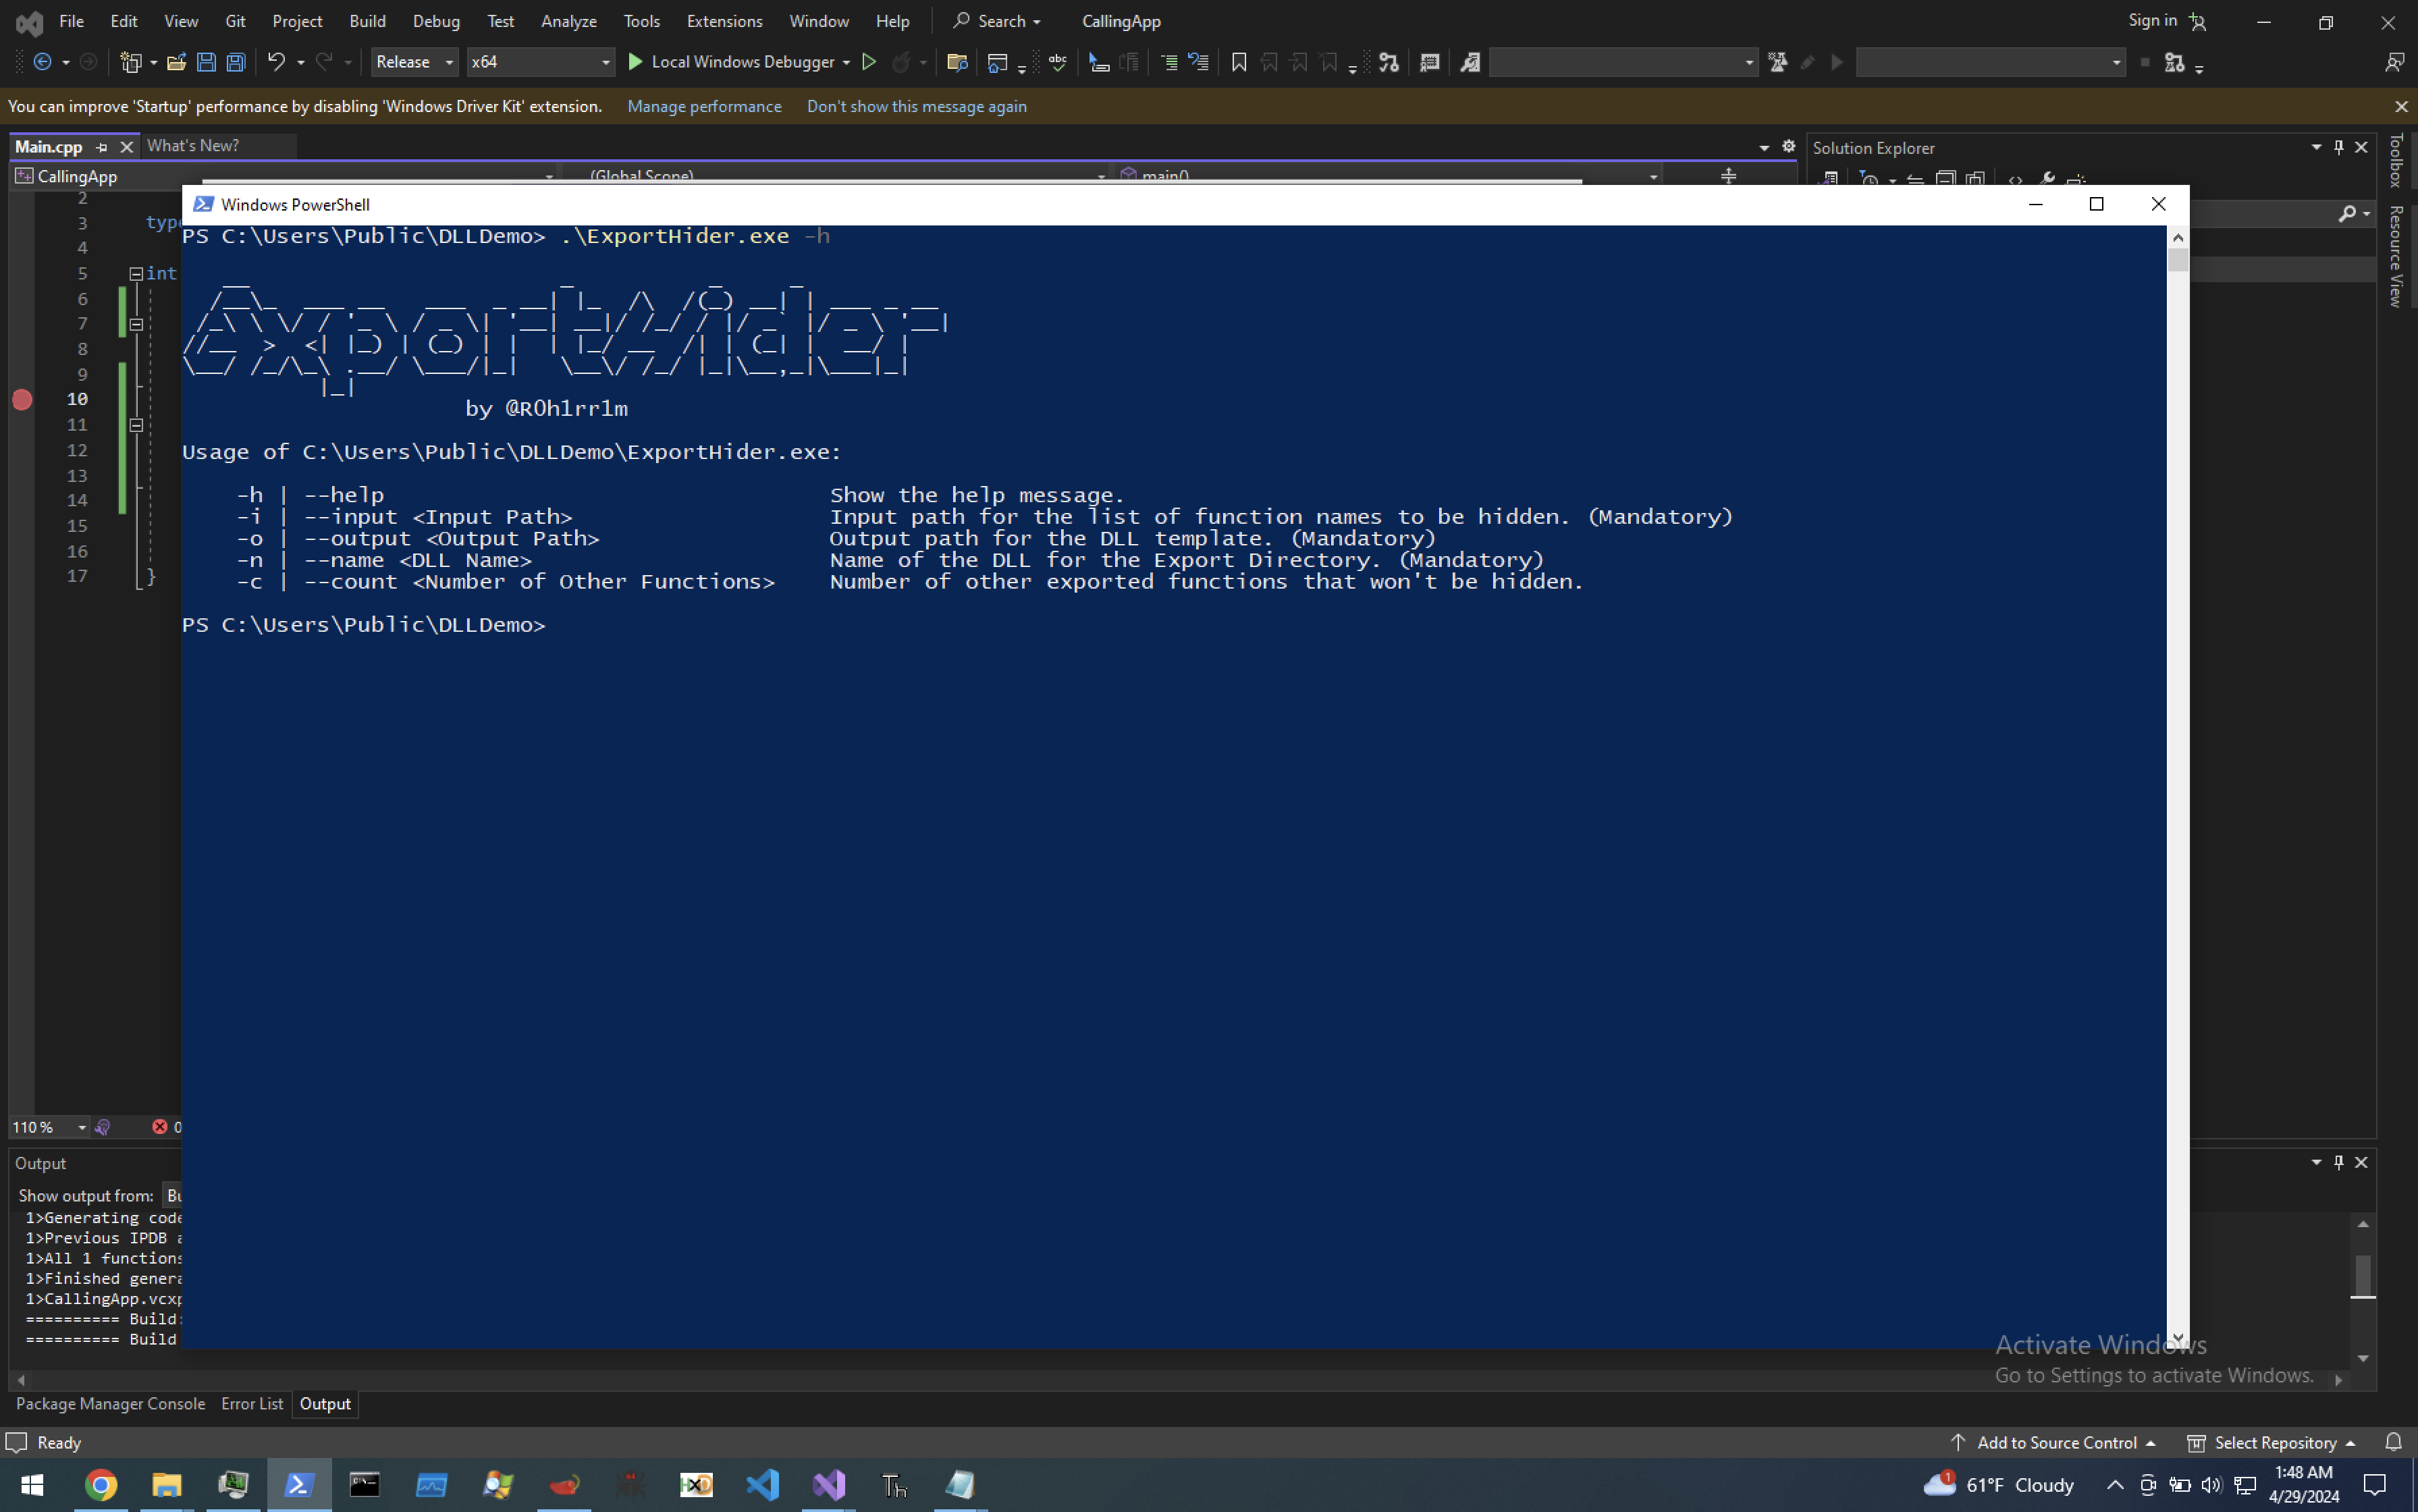
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
binary-analysisdynamic-code-analysisexploitation+4
366 months ago
ExportDumper preview

ExportDumper

GitHubiilegacyyii/exportdumper

A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
binary-analysispayload-developmentred-teaming+1
724 years ago
CVE-2025-21420-PoC preview

CVE-2025-21420-PoC

GitHubdmitri131313/cve-2025-21420-poc

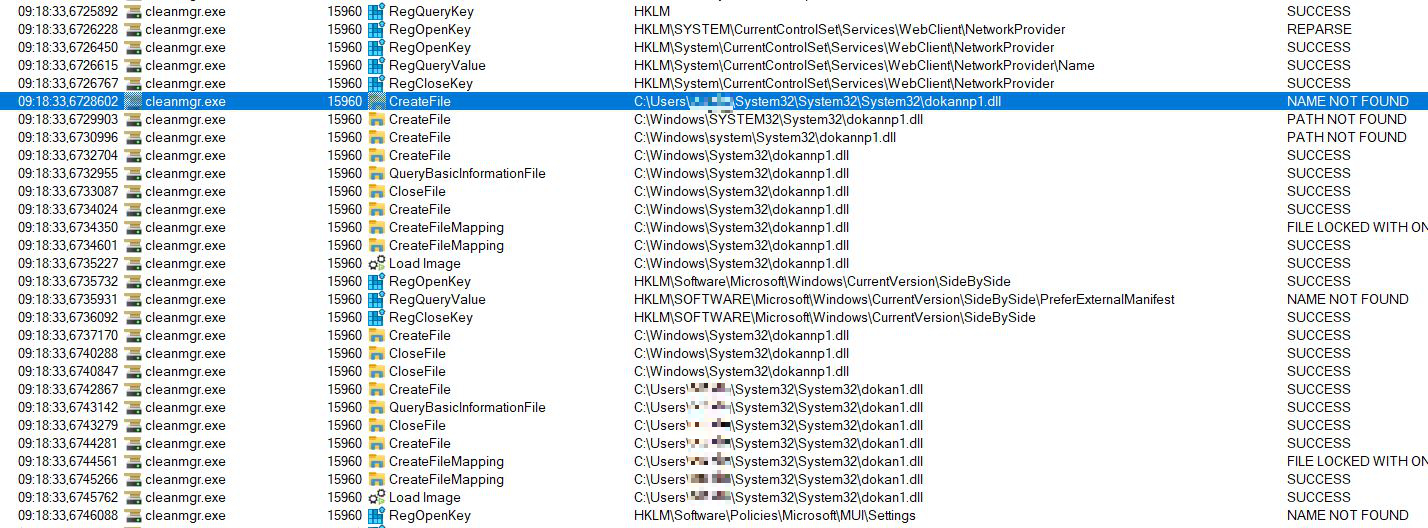
We found a way to DLL sideload with cleanmgr.exe
binary-exploitationexploitationpayload-development+2
11 year ago
Kernel_VADInjector preview

Kernel_VADInjector

GitHublleon1435/kernel_vadinjector

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
adversarial-attackids-ips-evasionpayload-development+3
543 years ago
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
binary-exploitationexploitationmalware-analysis+6
12510 months ago
Mangle preview
Archived

Mangle

GitHuboptiv/mangle

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
binary-analysisdefensive-toolsexploitation+6
1.2k3 years ago
CVE-2015-6132 preview

CVE-2015-6132

GitHubhexx0r/cve-2015-6132

Microsoft Office / COM Object DLL Planting
binary-exploitationexploitationpayload-development+2
1510 years ago
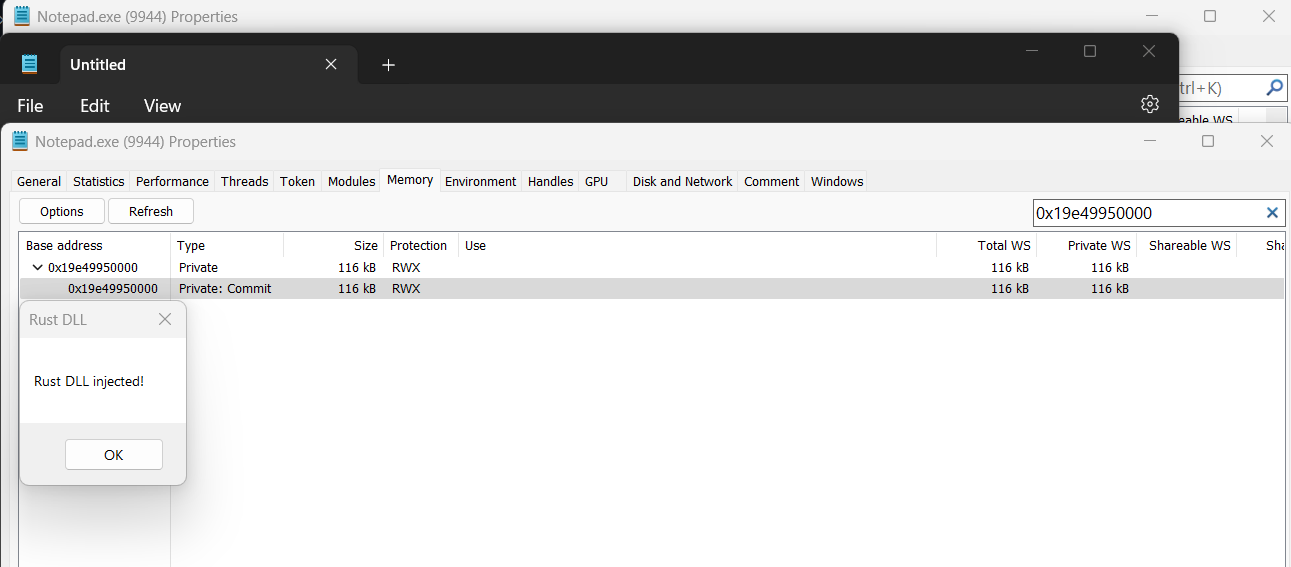
CVE-2025-24076 preview

CVE-2025-24076

GitHubmbanyamer/cve-2025-24076

Python exploit for CVE-2025-24076, a Windows Cross Device Service privilege escalation vulnerability. Replaces a DLL to achieve SYSTEM privileges via…
binary-exploitationeducationexploitation+3
211 year ago
winsos-poc preview

winsos-poc

GitHubthiagopeixoto/winsos-poc

A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
adversarial-attackexploitationpayload-development+2
1122 years ago
cve-2022-32223 preview

cve-2022-32223

GitHubianyong/cve-2022-32223

Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
binary-exploitationexploitationpayload-development+2
34 years ago
CVE-2021-1366 preview

CVE-2021-1366

GitHubkoztkozt/cve-2021-1366

Proof-of-concept for Cisco AnyConnect HostScan local privilege escalation via DLL hijacking and IPC command injection, demonstrating DLL proxying to…
binary-exploitationexploitationpayload-development+2
3 years ago
venom-rs preview
Archived

venom-rs

GitHubmemn0ps/venom-rs

Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
payload-developmentpost-exploitationred-teaming+2
3682 years ago
CVE-2026-21508_POC preview

CVE-2026-21508_POC

GitHub0xc4r/cve-2026-21508_poc

Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…

binary-exploitationexploitationpayload-development+2
298 months ago
Previous123456Next