
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
31 results
chyrp-lite-rce-poc preview

chyrp-lite-rce-poc

GitHubiltosec/chyrp-lite-rce-poc

CVE-2026-53767 + CVE-2026-53768 - Authenticated RCE in Chyrp Lite ≤ 2026.01 via uploads_path blocklist bypass and missing extension validation
educationexploitationpayload-development+4
3 months ago
CVE-2022-29072 preview

CVE-2022-29072

GitHubkagancapar/cve-2022-29072

7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the Help>Contents…
binary-exploitationcommand-and-controlexploitation+5
6714 years ago
WP-Contest-Gallery-28.1.4-Exploit preview

WP-Contest-Gallery-28.1.4-Exploit

GitHubcerberusmrxi/wp-contest-gallery-28.1.4-exploit

Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
exploitationpassword-crackingpayload-development+4
12 months ago
JS-Tap preview

JS-Tap

GitHubhoodoer/js-tap

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…
command-and-controldata-exfiltrationinformation-gathering+8
4772 months ago
aggrokatz preview

aggrokatz

GitHubsec-consult/aggrokatz

Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
exploit-frameworkspayload-developmentpenetration-testing+2
1545 years ago
crauEmu preview

crauEmu

GitHubdsecurity/crauemu

crauEmu is an uEmu extension for developing and analyzing payloads for code-reuse attacks
binary-exploitationexploit-frameworkspayload-development+1
1106 years ago
Remote-BOF-Runner preview

Remote-BOF-Runner

GitHubpard0p/remote-bof-runner

Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
binary-exploitationcommand-and-controleducation+8
1018 months ago
processhacker-mcp preview

processhacker-mcp

GitHubillegal-instruction-co/processhacker-mcp

Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…

debuggersdynamic-analysis-sandboxingexploitation+7
517 months ago
apfell-chrome-extension-c2server preview

apfell-chrome-extension-c2server

GitHubxorrior/apfell-chrome-extension-c2server

Apfell C2 Server for the Google Chrome Extension Payload
command-and-controlexploit-frameworkspayload-development+3
126 years ago
React2Shell preview

React2Shell

GitHubsho-luv/react2shell

CVE-2025-55182 security test kit: CLI scanner + Chrome extension + Nuclei templates + Docker lab.
ctfeducationexploit-frameworks+7
109 months ago
CVE-2024-44902 preview

CVE-2024-44902

GitHubfru1ts/cve-2024-44902

Proof-of-concept exploit for CVE-2024-44902, a deserialization vulnerability in ThinkPHP v6.1.3–v8.0.4 enabling remote code execution via crafted…

code-analysisexploitationpayload-development+3
62 years ago
CVE-2026-48909-Joomla-SP-Exploit preview

CVE-2026-48909-Joomla-SP-Exploit

GitHubcerberusmrxi/cve-2026-48909-joomla-sp-exploit

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
code-analysiscommand-and-controleducation+8
22 months ago
CVE-2026-13001 preview

CVE-2026-13001

GitHubghostpels/cve-2026-13001

Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…

educationexploitationpayload-development+3
2 months ago
CVE-2026-46275 preview

CVE-2026-46275

GitHubxxconi/cve-2026-46275

Python exploit for CVE-2026-46725, achieving unauthenticated remote code execution in TYPO3 ceselector extension via PHP object injection and Monolog…
code-analysiseducationexploitation+4
4 months ago
CVE-2024-9264-Fixed preview

CVE-2024-9264-Fixed

GitHubexerrdev/cve-2024-9264-fixed

Fixed proof-of-concept exploit for CVE-2024-9264, a critical Grafana RCE via DuckDB SQL expressions. Executes reverse shell using corrected shellfs…
educationexploitationpayload-development+3
1 year ago
CVE-2021-26700 preview

CVE-2021-26700

GitHubjune-in-exile/cve-2021-26700

Educational RCE exploit for CVE-2021-26700 in VS Code npm extension, demonstrating DNS tunneling to a Caldera C2 server via malicious package.json…

command-and-controldns-analysiseducation+4
3 years ago
external_c2_framework preview

external_c2_framework

GitHubund3rf10w/external_c2_framework

Python api for usage with cobalt strike's External C2 specification
command-and-controlexploit-frameworkspayload-development+3
2384 years ago
SliverKeylogger preview

SliverKeylogger

GitHubtrustedsec/sliverkeylogger

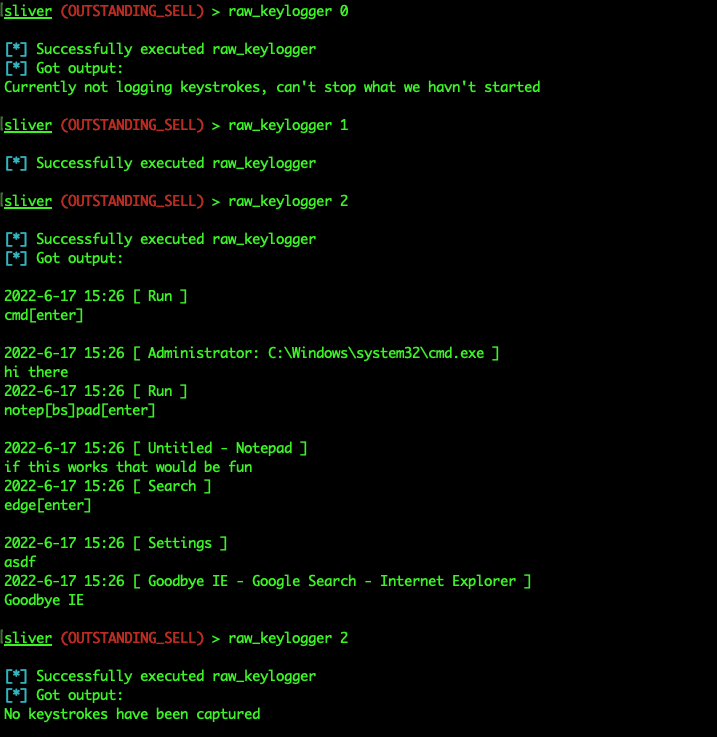
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…

command-and-controldata-exfiltrationpayload-development+2
1713 years ago
Previous12Next