

byvalver
 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
binary-analysisexploitationmachine-learning+6
63
umpolungfish/byvalvertakes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…
 cyhe50/cve-2025-32434-poc
Proof-of-concept exploit for CVE-2025-32434, a pickle deserialization vulnerability in PyTorch's weights_only mode, demonstrating malicious tar file…
 bardlaudian/cve-2024-37054
Proof-of-concept that poisons MLflow registered models via the REST API, embedding a malicious pickle to trigger RCE when the model is loaded.
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 ocfagb/hacktivity-vulns-exploits-lab
Writeup + CVE analysis + countermeasures for the Hacktivity 'Vulnerabilities, Exploits, and Remote Access Payloads' lab (netcat shells, Metasploit,…
 0xtensho/cve-2025-49132-poc
Proof-of-concept exploit for CVE-2025-49132, abusing a file inclusion vulnerability in Pterodactyl to achieve remote code execution via pearcmd.php.
 apache/caldera
Automated Adversary Emulation Platform
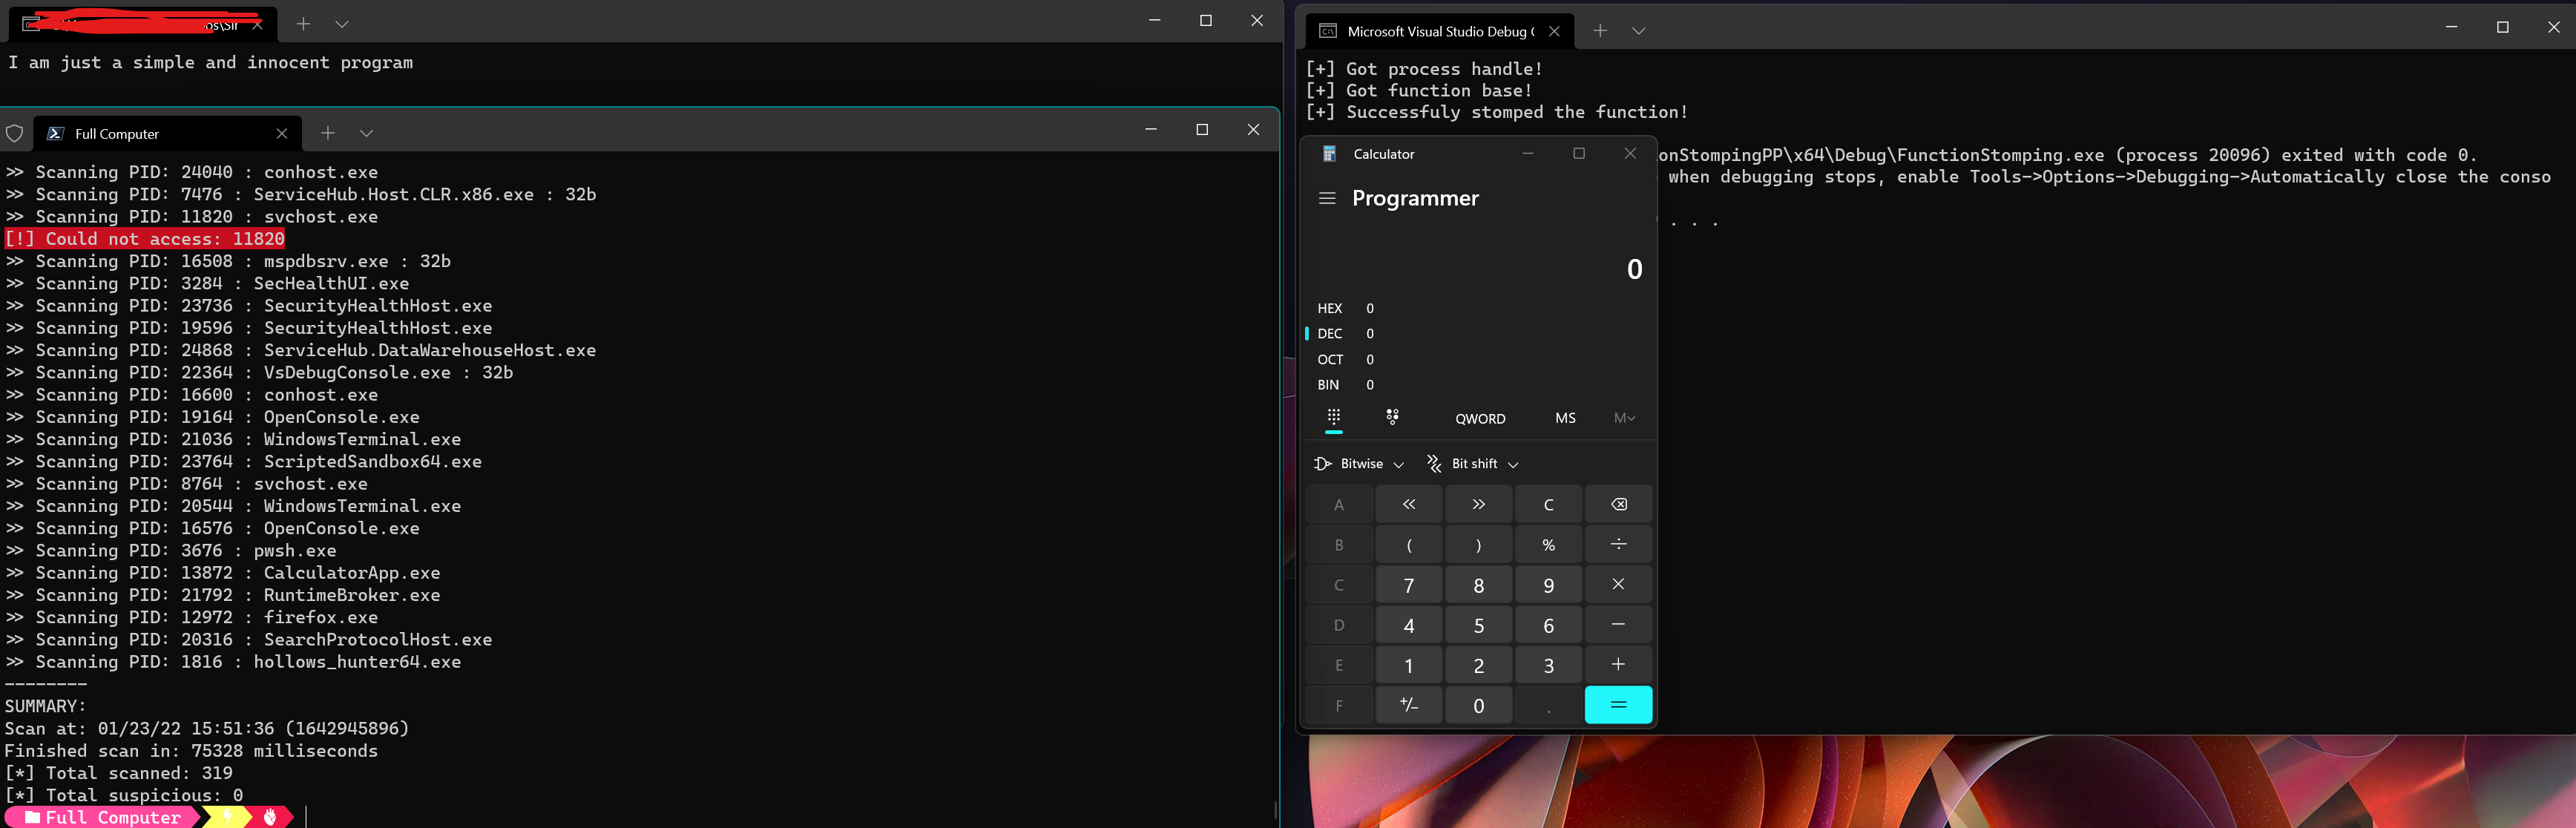 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
 wysiiwyg/poc-cve-2022-30190
Proof-of-concept exploit for CVE-2022-30190 (Follina), demonstrating remote code execution via crafted Microsoft Office documents using the ms-msdt…
 razureink/cve-2026-63030_60137-wordpress_rce_reproduction
CVE Reproduction: cve-2026-63030_60137-wordpress_rce_reproduction
 seahcy/cve-2025-24813
Instructions for rapid deployment of Tomcat v9.0.90 with java 25.0.1 2025-10-21 LTS on Windows Server 2019 Standard for lazy researchers.