
CVE-2024-38472
 abdurahmon3236/cve-2024-38472
Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
command-and-controlexploit-frameworkslateral-movement+6
4
abdurahmon3236/cve-2024-38472Metasploit module that exploits Apache HTTP Server SSRF (CVE-2024-38472) on Windows to reach internal services and achieve remote code execution.
 binracer/ms08-067
This repository contains a Metasploit module implementation for the MS08-067 Windows Server Service vulnerability (CVE-2008-4250). This is a classic…
 vulncheck-oss/external-c2-experiments
Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…
 tiagob0b/cve-2021-22005
Metasploit module for CVE-2021-22005 VMware vCenter arbitrary file upload vulnerability with proof-of-concept and remote code execution exploit.
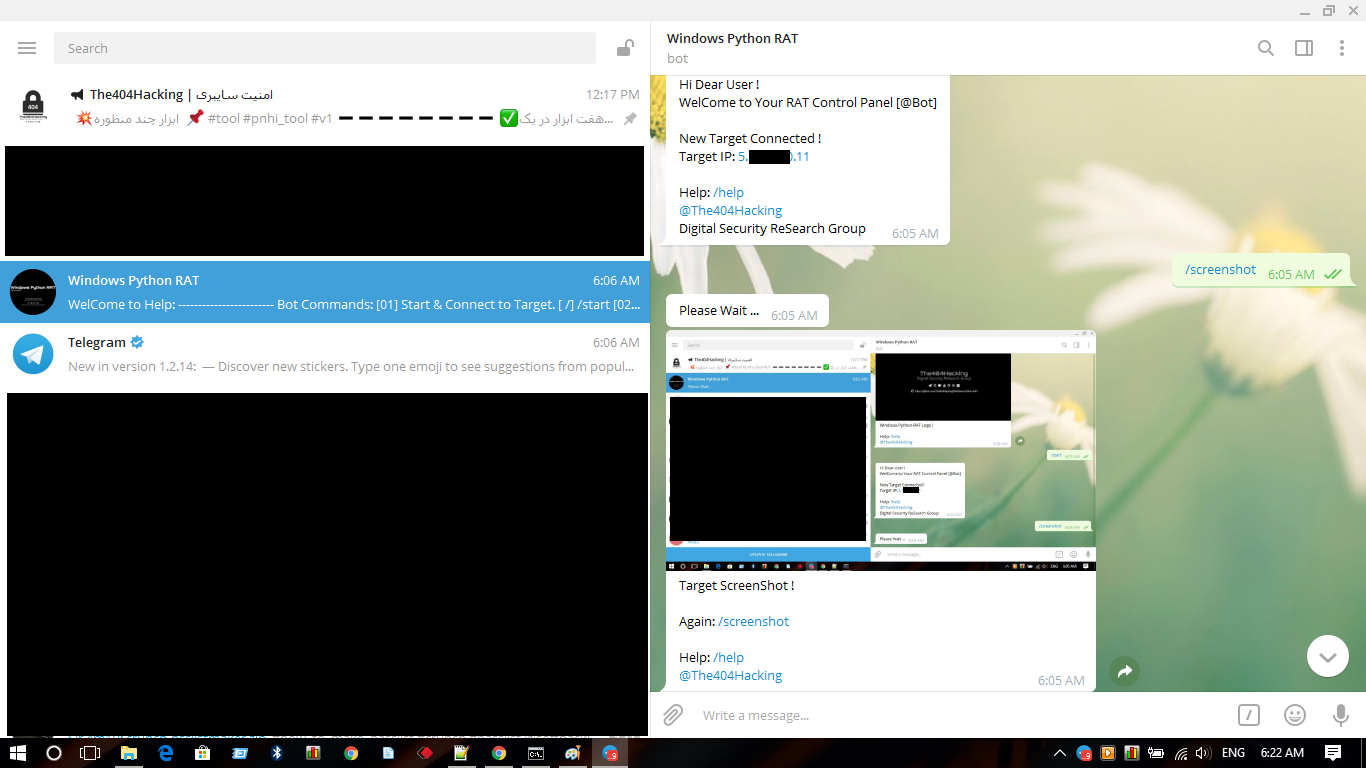 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
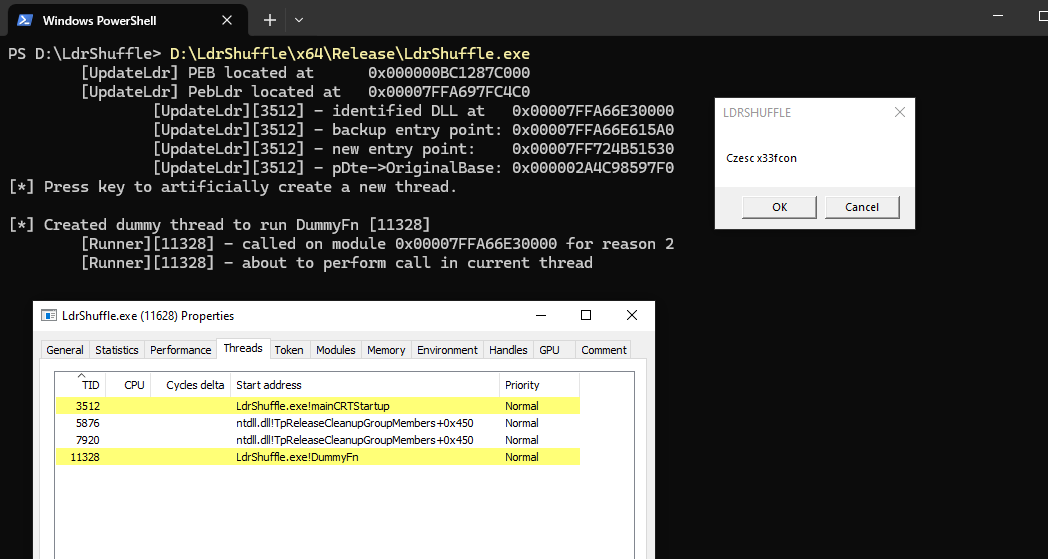 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 zcgonvh/cve-2017-7269
fixed msf module for cve-2017-7269
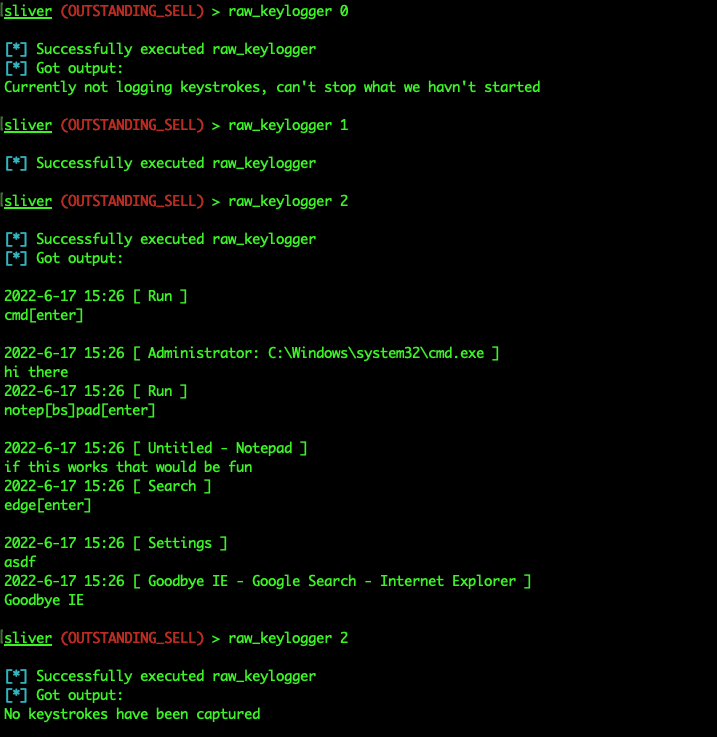 trustedsec/sliverkeylogger
Windows keylogging module for the Sliver C2 implant framework, using Raw Input to capture keystrokes and expose start, stop, and retrieval commands…
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
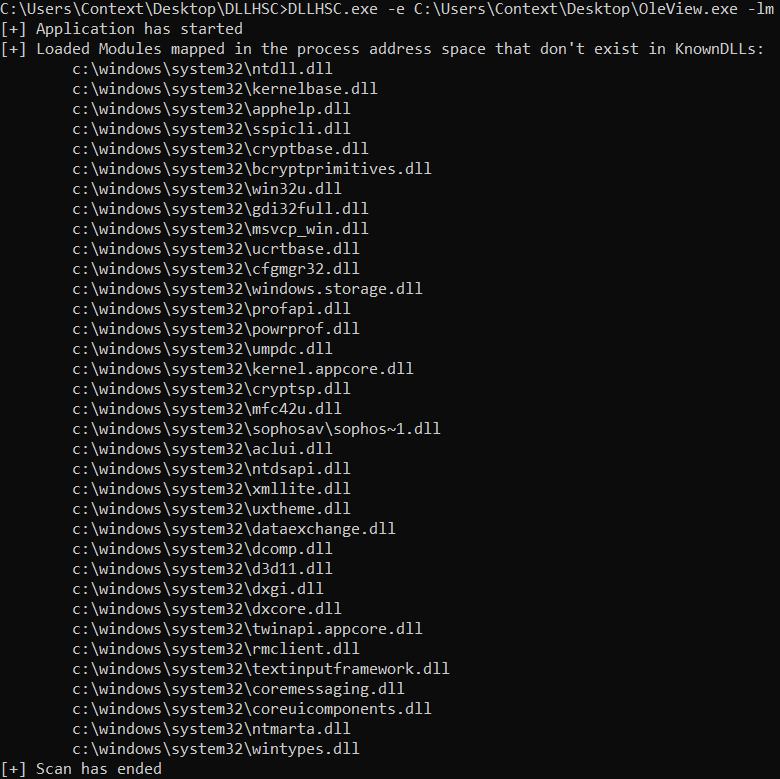 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
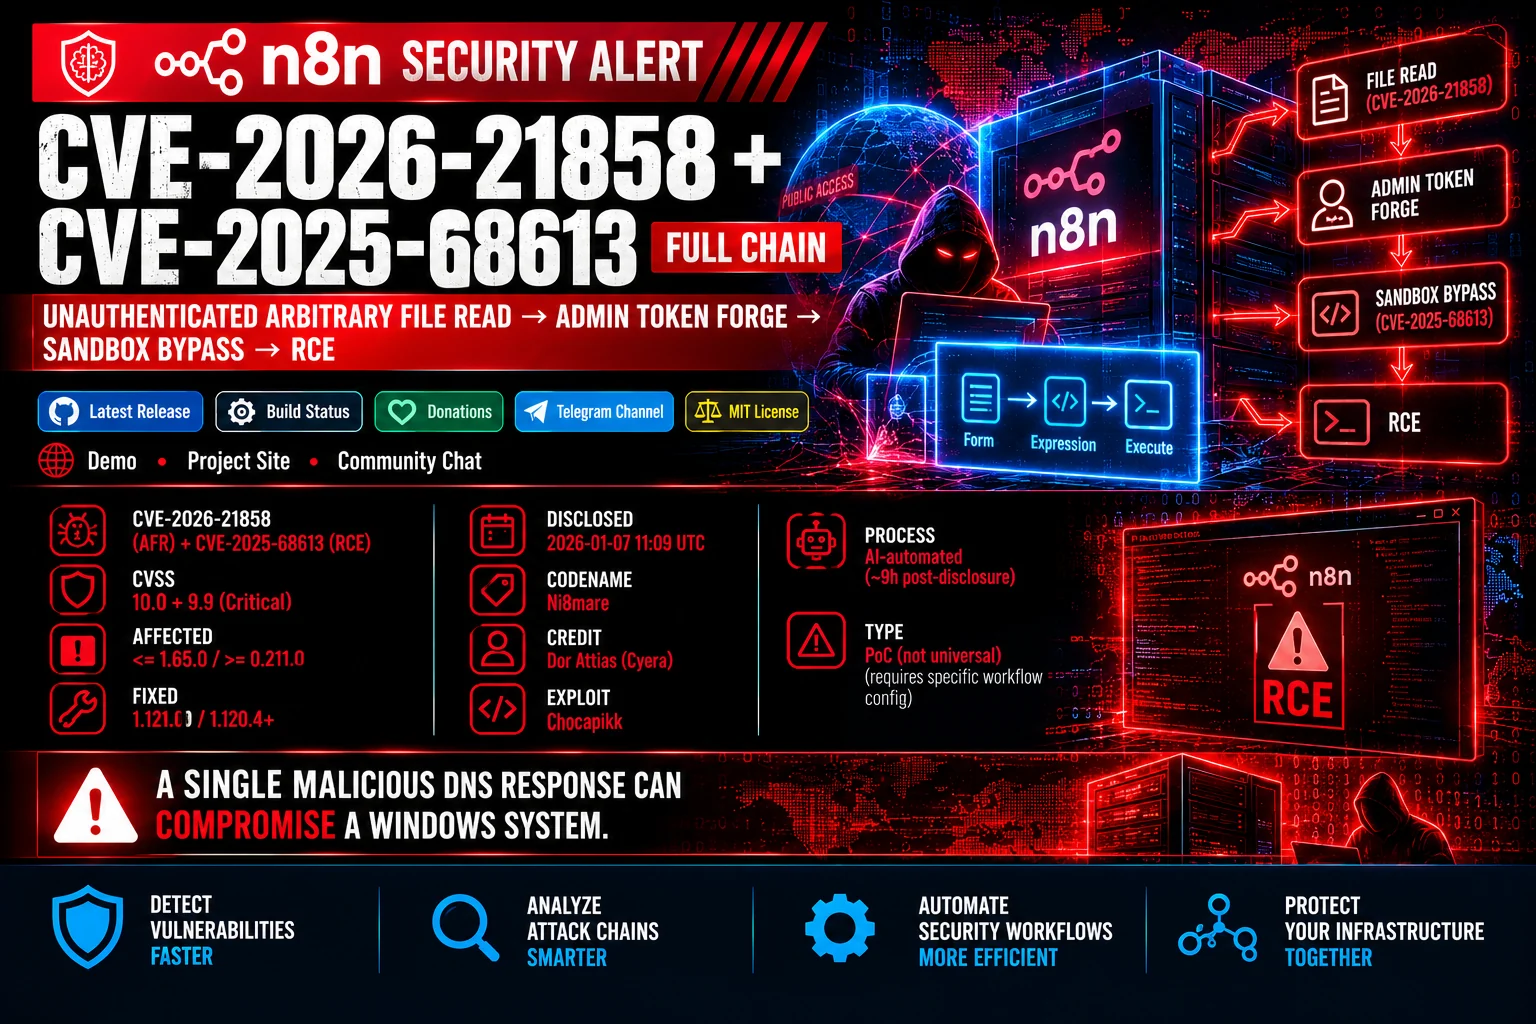 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 huynambka/cve-2026-26114-poc
Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
 p3nt3st3r-star/cve-2026-42945-poc
Proof-of-concept exploit for CVE-2026-42945, a critical heap buffer overflow in NGINX's rewrite module enabling unauthenticated remote code…
 rickgeex/msf-module-cve-2019-0708
Metasploit module for CVE-2019-0708 (BlueKeep) - https://github.com/rapid7/metasploit-framework/tree/5a0119b04309c8e61b44763ac08811cd3ecbbf8d/modules/…