
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
42 results
Hwacha preview

Hwacha

GitHubn00py/hwacha

Deploy payloads to *Nix systems en masse
command-and-controlexploitationlateral-movement+7
1086 years ago
CVE-2024-57394 preview

CVE-2024-57394

GitHubcwjchoi01/cve-2024-57394

Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…

binary-exploitationexploitationlateral-movement+4
1 year ago
GadgetToJScript preview

GadgetToJScript

GitHubmed0x2e/gadgettojscript

A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…

adversarial-attackexploitationlateral-movement+5
1.1k5 years ago
tgt-monitor-bof preview

tgt-monitor-bof

GitHubjakobfriedl/tgt-monitor-bof

Async BOF to automatically extract or renew Kerberos TGTs on a target system.
authenticationlateral-movementpayload-development+3
1351 month ago
ColdWer preview

ColdWer

GitHub0xsh3llf1r3/coldwer

Cobalt Strike BOF to freeze EDR/AV processes and dump LSASS using WerFaultSecure.exe PPL bypass

exploitationlateral-movementpayload-development+3
1467 months ago
RunPE preview

RunPE

GitHubnettitude/runpe

C# Reflective loader for unmanaged binaries.
adversarial-attackimpersonation-toolspayload-development+6
4473 years ago
PrintSpoofer-ReflectiveDLL preview

PrintSpoofer-ReflectiveDLL

GitHubjonyfilc/printspoofer-reflectivedll

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
exploitationlateral-movementpayload-development+4
21 month ago
RedTeam-Tools preview

RedTeam-Tools

GitHuba-poc/redteam-tools

Tools and Techniques for Red Team / Penetration Testing
exploitationlateral-movementosint+7
9.7k5 months ago
DCOMUploadExec preview

DCOMUploadExec

GitHubdeepinstinct/dcomuploadexec

DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
exploitationlateral-movementpayload-development+3
3961 year ago
dcomhijack preview

dcomhijack

GitHubwkl-sec/dcomhijack

Lateral Movement Using DCOM and DLL Hijacking
exploitationlateral-movementpayload-development+3
3263 years ago
DLHell preview

DLHell

GitHubsynacktiv/dlhell

Local & remote Windows DLL Proxying
exploitationlateral-movementpayload-development+3
1712 years ago
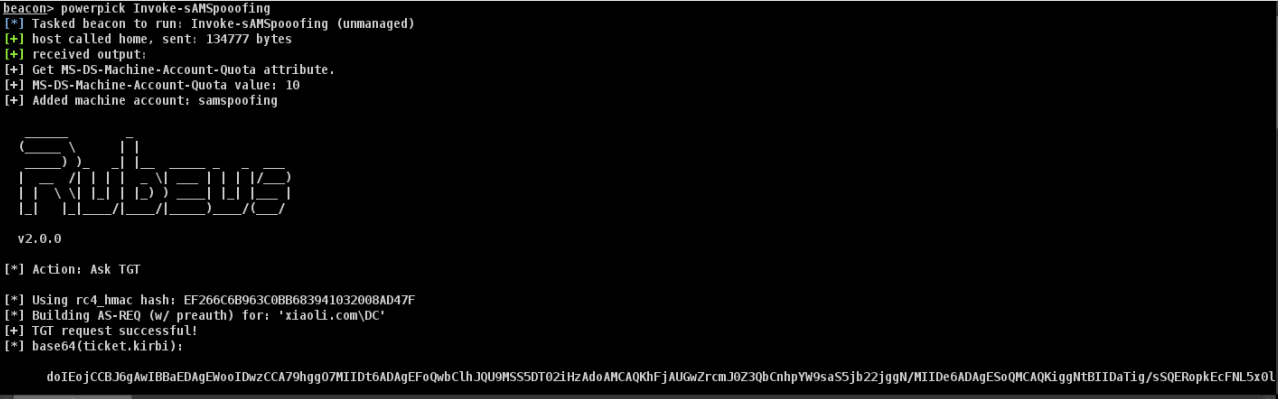
Invoke-sAMSpoofing preview

Invoke-sAMSpoofing

GitHubxiaolichan/invoke-samspoofing

CVE-2021-42287/CVE-2021-42278 exploits in powershell
exploitationlateral-movementpayload-development+3
394 years ago
CVE-2025-50505 preview

CVE-2025-50505

GitHuba0yami/cve-2025-50505

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
command-and-controldns-analysisexploitation+8
2011 months ago
ad-autopwn preview

ad-autopwn

GitHubjonaslejon/ad-autopwn

Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
command-and-controlexploitationlateral-movement+7
1945 days ago
RpcProxyInvoke preview

RpcProxyInvoke

GitHubklezvirus/rpcproxyinvoke

Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
binary-exploitationcommand-and-controlexploitation+8
1382 years ago
LocalPotato_CVE-2023-21746 preview

LocalPotato_CVE-2023-21746

GitHubmuhammad-ali007/localpotato_cve-2023-21746

Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
binary-exploitationexploitationlateral-movement+5
33 years ago
CVE-2020-25265-25266 preview

CVE-2020-25265-25266

GitHubrefi64/cve-2020-25265-25266

Proof-of-concept exploit demonstrating CVE-2020-25265 and CVE-2020-25266, using a crafted MP3 file to achieve arbitrary code execution via…
binary-exploitationexploitationlateral-movement+3
25 years ago
CVE-2024-32002 preview

CVE-2024-32002

GitHubcharlesgargasson/cve-2024-32002

Exploit for CVE-2024-32002, a Git RCE vulnerability that uses recursive submodule cloning and symlinks to execute arbitrary commands on Windows and…

command-and-controlexploitationlateral-movement+6
2 years ago
Previous123Next