
ad-autopwn
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
command-and-controlexploitationlateral-movement+7
37
jonaslejon/ad-autopwnAutomated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 kleiton0x00/redditc2
Abusing Reddit API to host the C2 traffic.
 hackerhouse-opensource/offensivelua
Offensive Lua.
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
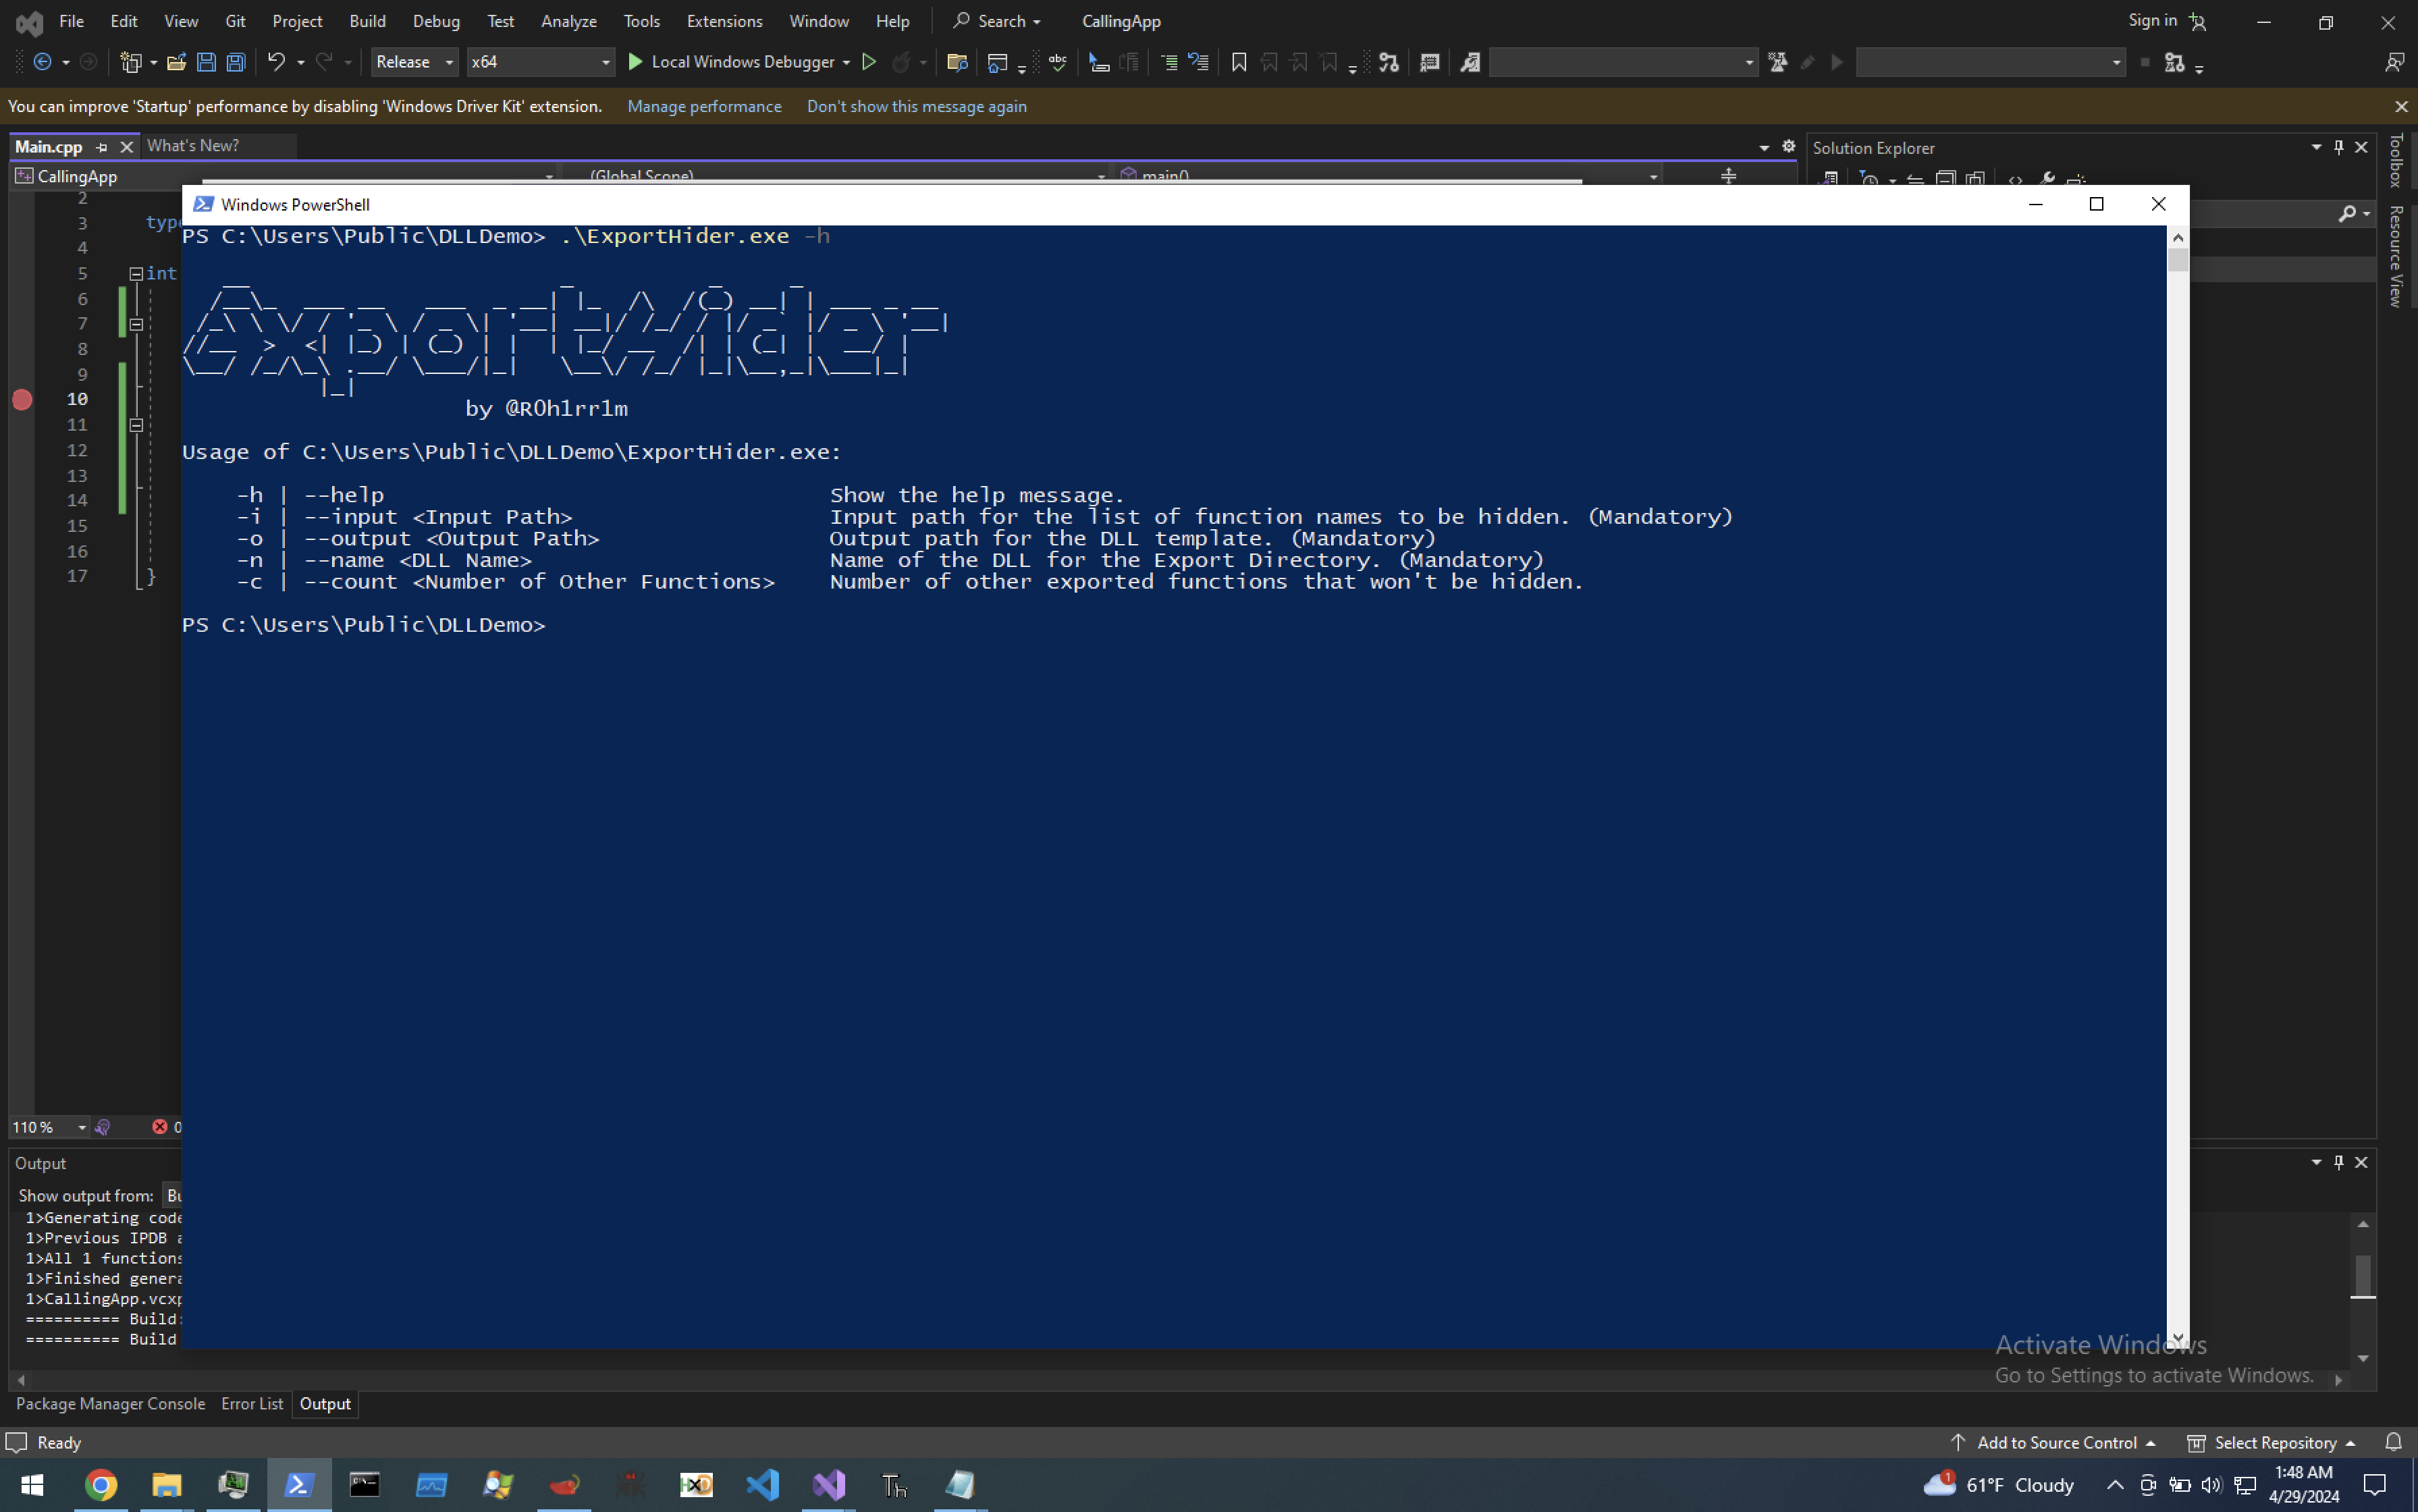 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 abraxas/veneficus-implant-public
Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 faithtiannn/cve-2025-55182
CVE-2025-55182漏洞检测工具
 i3r1h0n/ingressnightterror
My view on IngressNightmare vulnerability (CVE-2025-1974)
 vmc8ll/poc-cve-2024-23897
CVE-2024-23897: Jenkins Arbitrary File Read Lead to RCE
 galoget/printnightmare-cve-2021-1675-cve-2021-34527
CVE-2021-1675 / CVE-2021-34527 - PrintNightmare Python, C# and PowerShell Exploits Implementations (LPE & RCE)
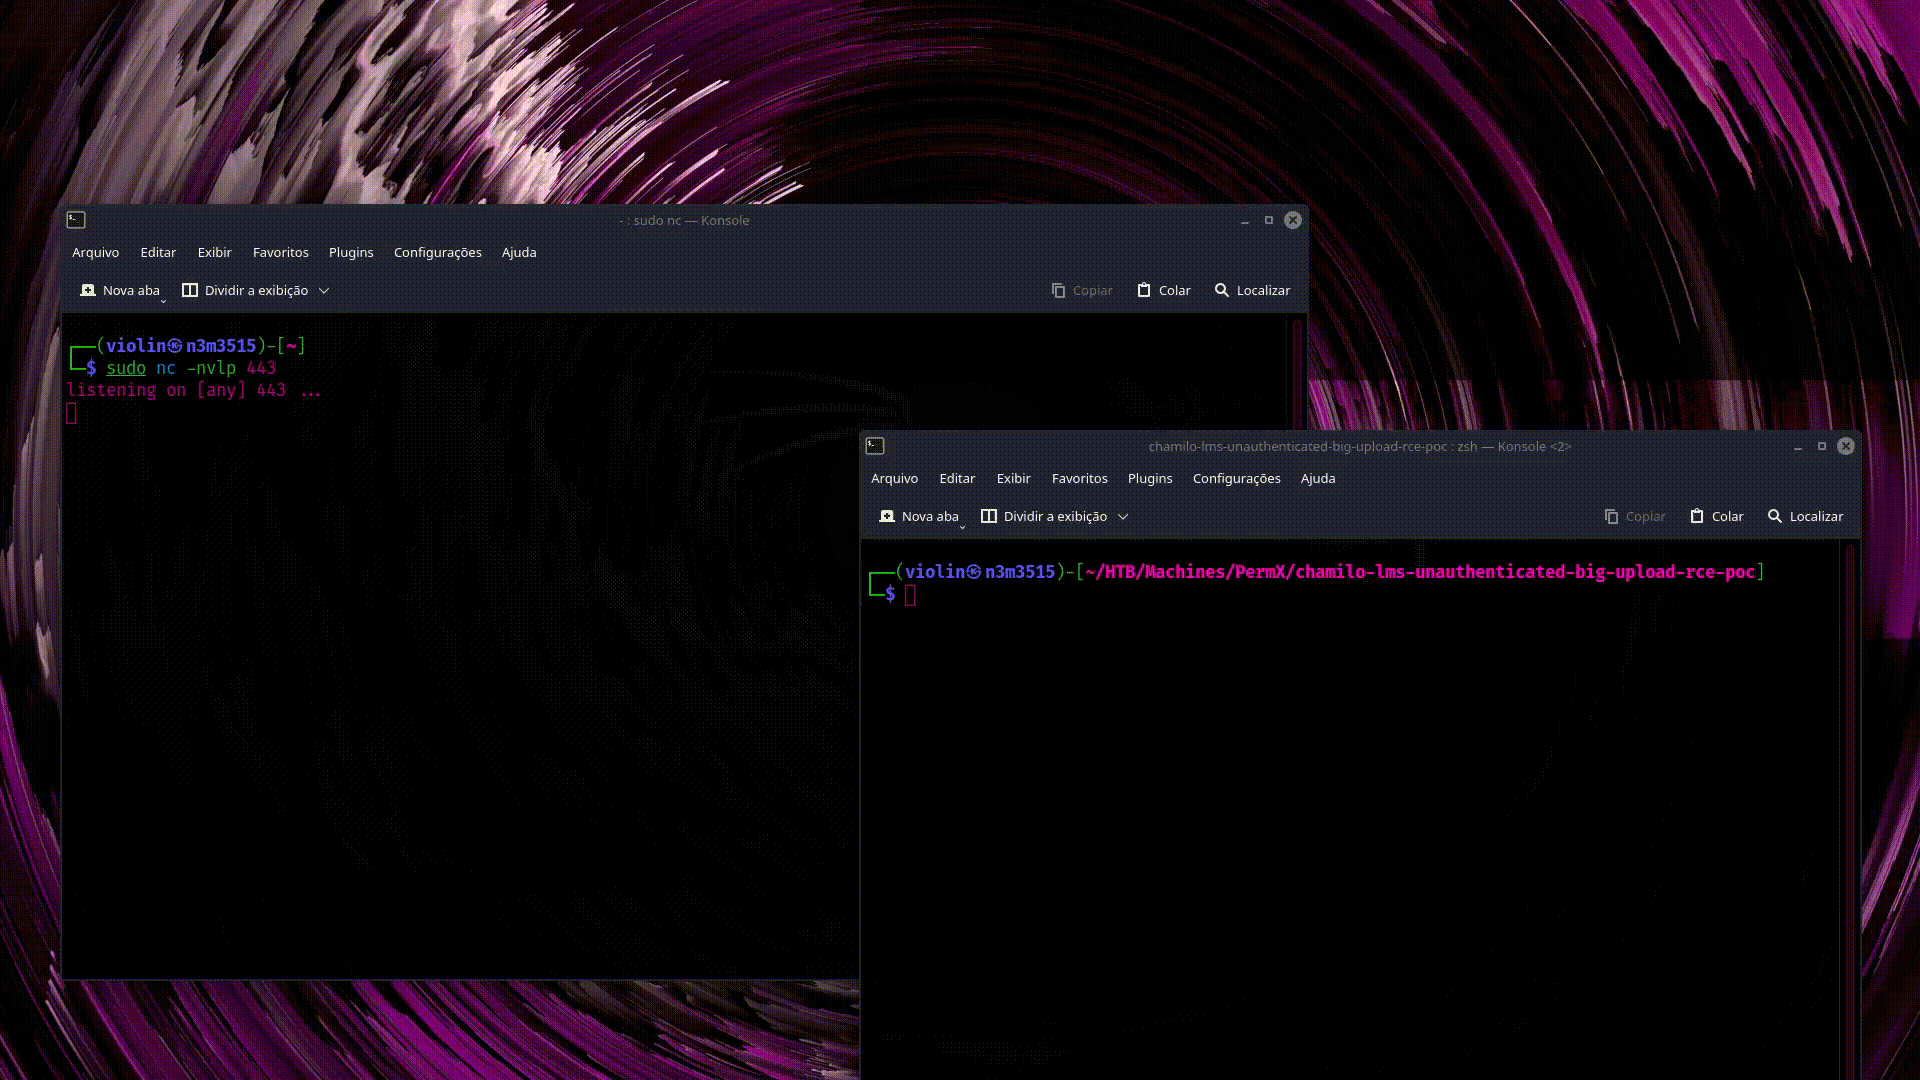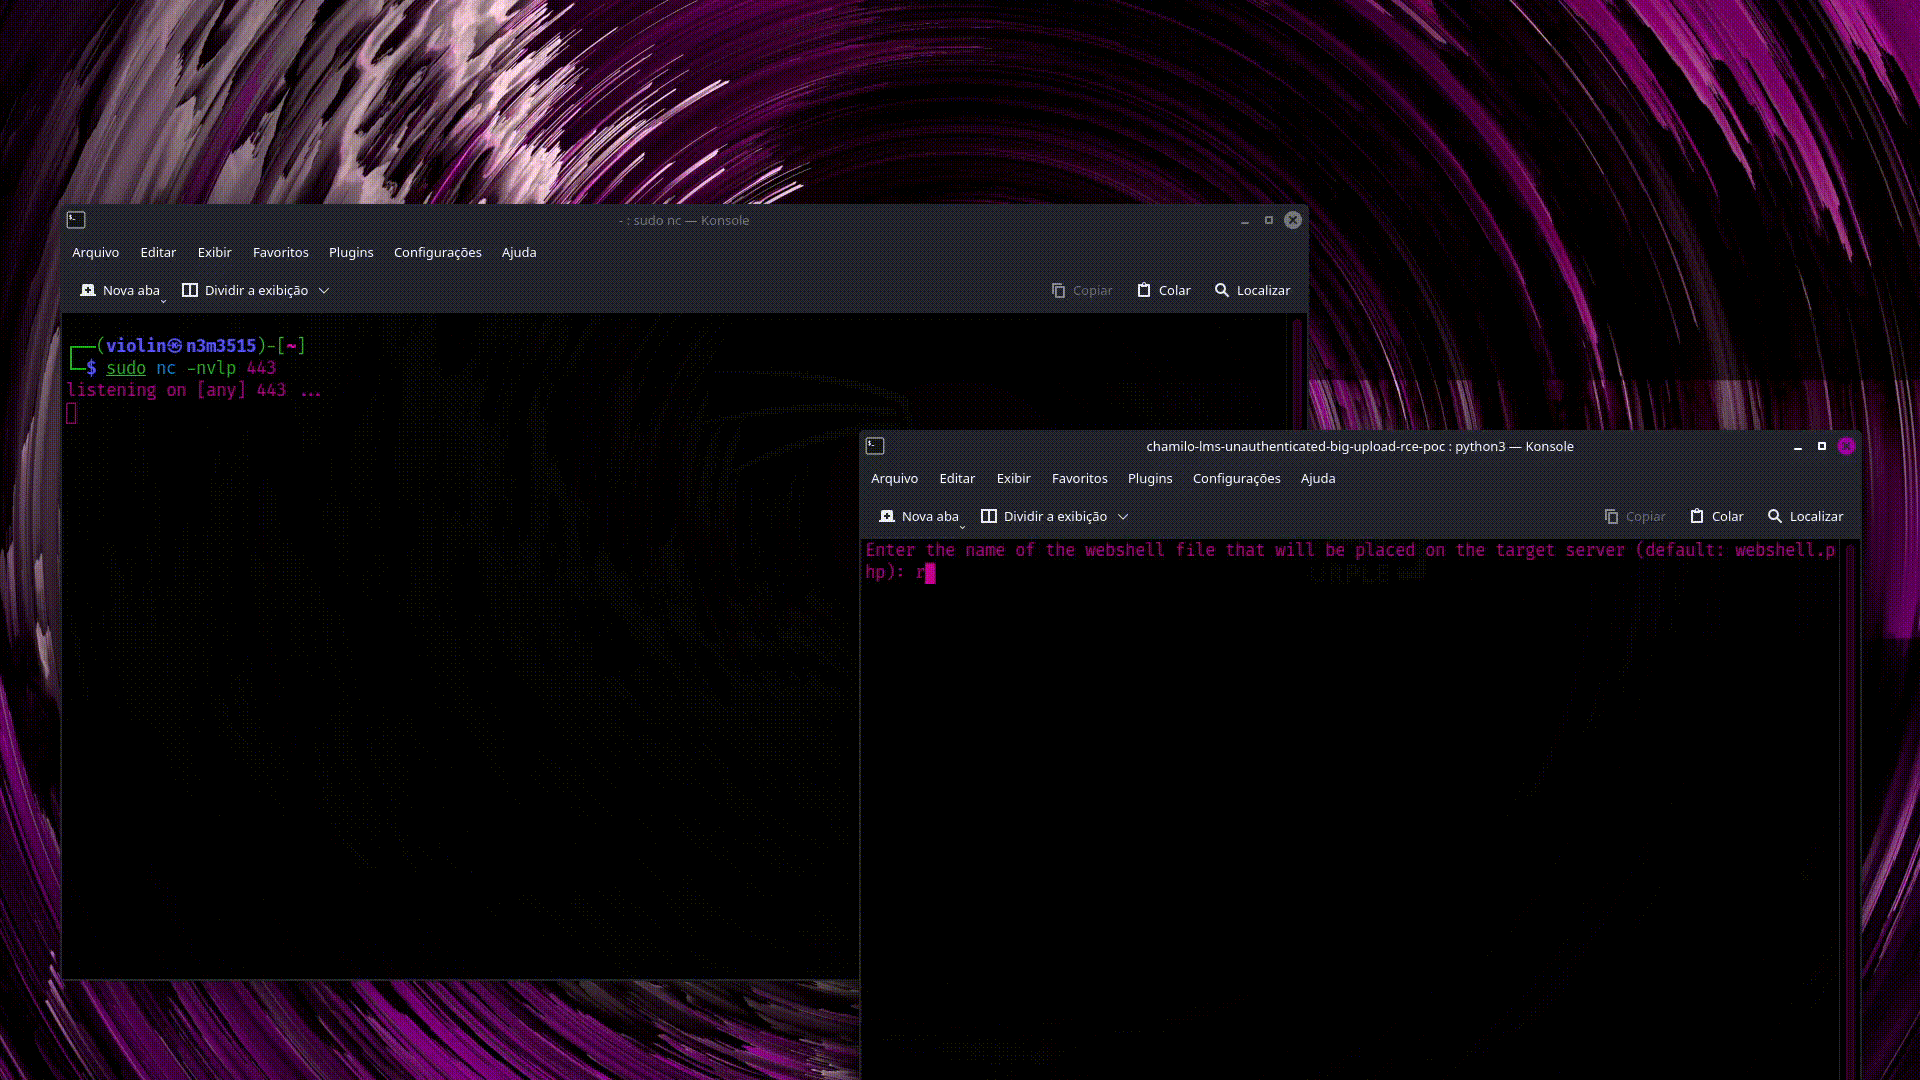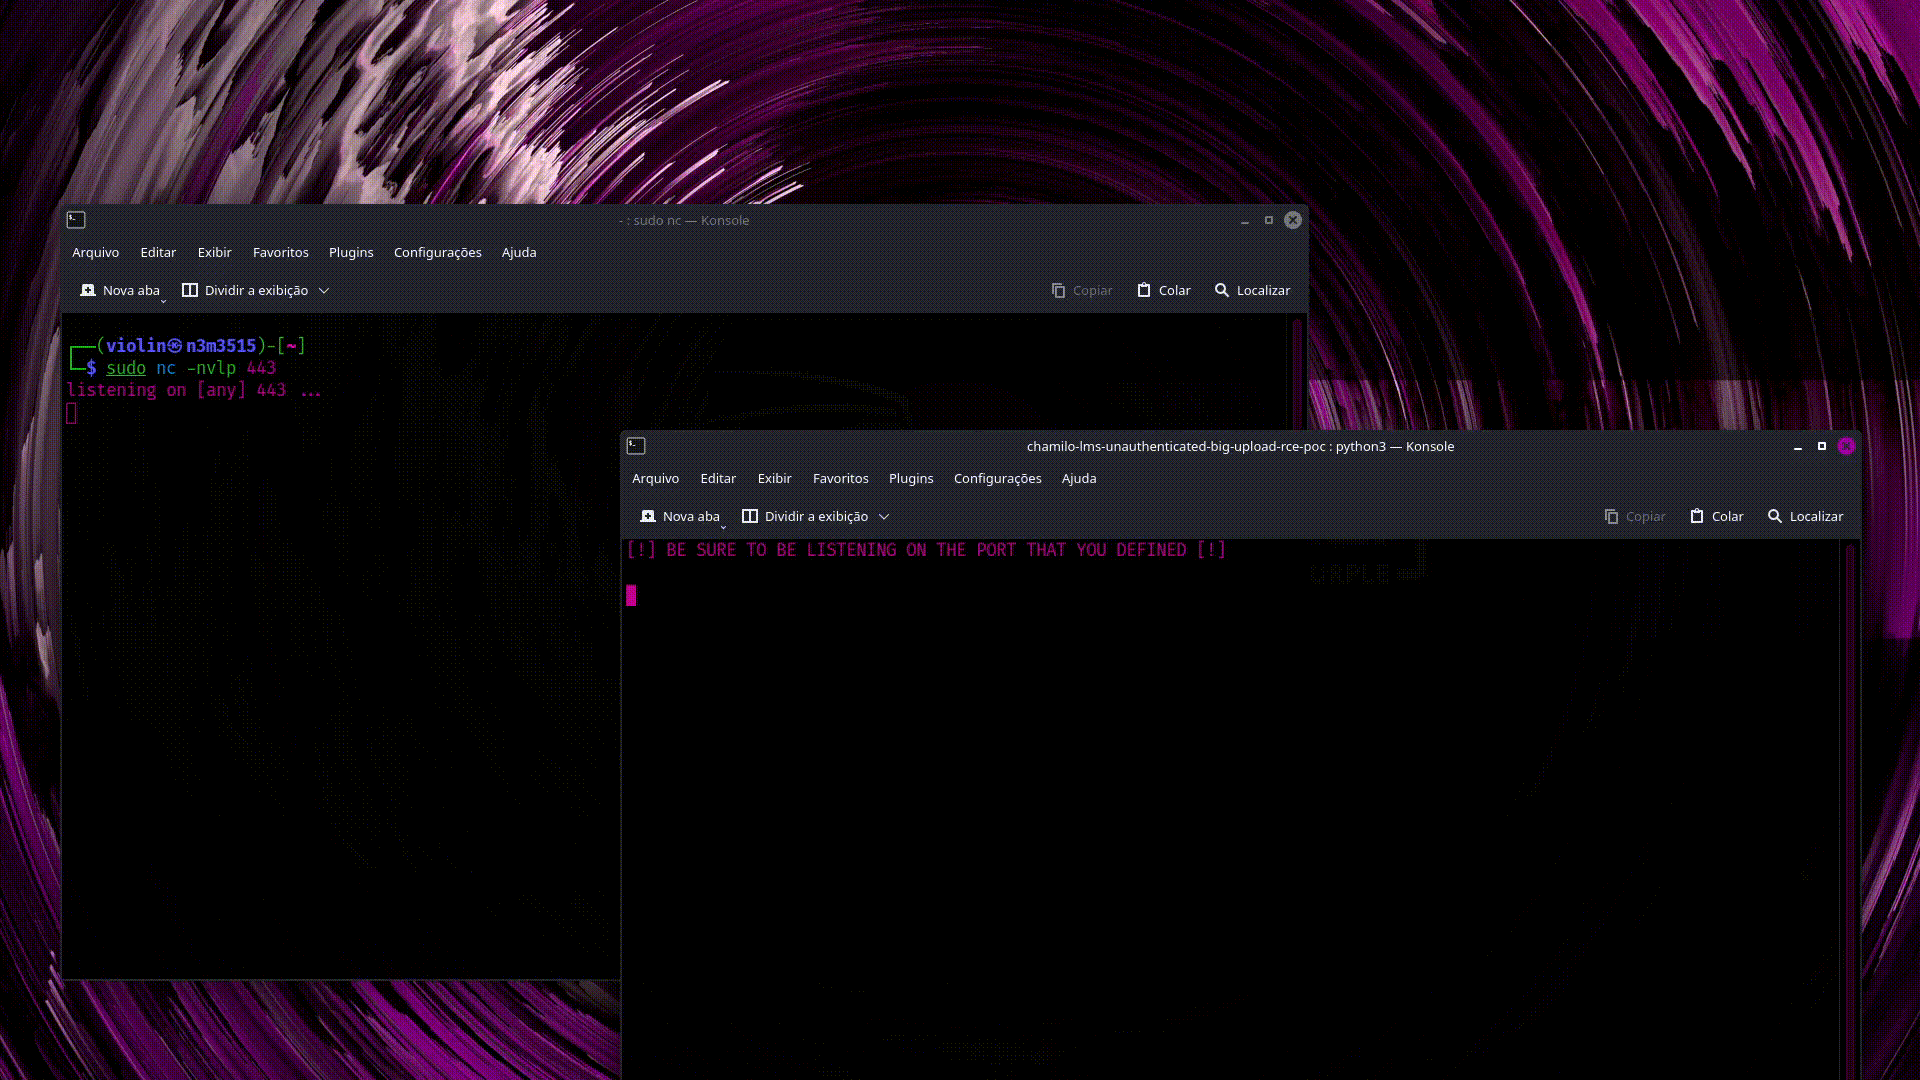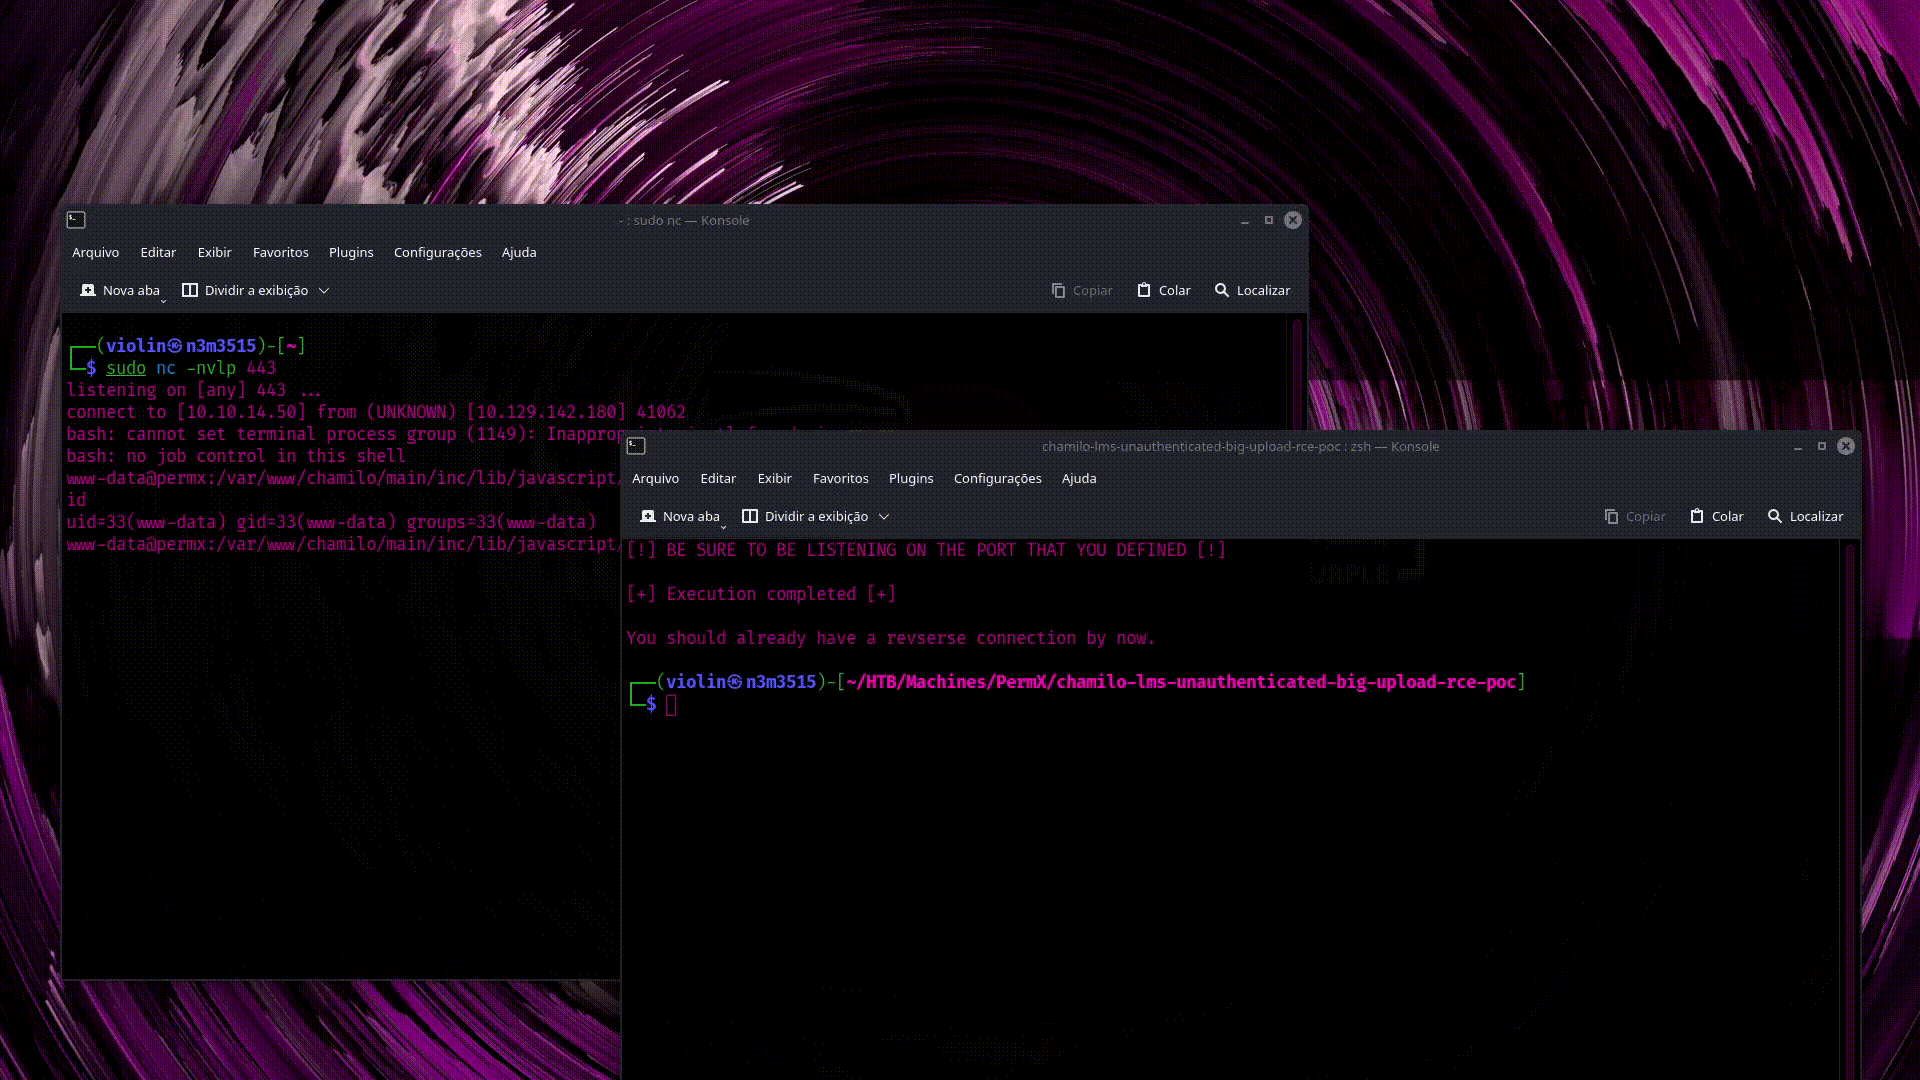 m3m0o/chamilo-lms-unauthenticated-big-upload-rce-poc
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220