
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
3650 results
0x00sec_code preview

0x00sec_code

GitHub0x00pf/0x00sec_code

Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…

binary-exploitationeducationexploitation+5
332
2 months ago
waf-community-bypasses preview

waf-community-bypasses

GitHubwaf-bypass-maker/waf-community-bypasses

Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
curated-resourcespayload-developmentpenetration-testing+3
5512 years ago
AtomicSyscall preview

AtomicSyscall

GitHubdaem0nc0re/atomicsyscall

Tools and PoCs for Windows syscall investigation.
adversarial-attackbinary-analysiseducation+3
3649 months ago
acCOMplice preview

acCOMplice

GitHubnccgroup/accomplice

Tools for discovery and abuse of COM hijacks

payload-developmentpersistence-mechanismspost-exploitation+1
3396 years ago
defcon33_silence_kill_edr preview

defcon33_silence_kill_edr

GitHubarosenmund/defcon33_silence_kill_edr

Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
adversarial-attackeducationlabs-practice+6
3481 year ago
Fritter preview

Fritter

GitHub0xrootpls/fritter

Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
binary-exploitationexploitationpayload-development+5
2531 month ago
CVE-2018-11776-Python-PoC preview

CVE-2018-11776-Python-PoC

GitHubhook-s3c/cve-2018-11776-python-poc

Working Python test and PoC for CVE-2018-11776, includes Docker lab
exploitationlabs-practicepayload-development+3
1238 years ago
winspy preview

winspy

GitHubcyb0r9/winspy

Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…

exploit-frameworkspayload-developmentpayload-generation+2
2137 years ago
CVE-2023-34362 preview

CVE-2023-34362

GitHubhorizon3ai/cve-2023-34362

Proof-of-concept exploit for CVE-2023-34362, abusing SQL injection to obtain a sysadmin API token and deserialization for remote code execution on…
exploitationpayload-developmentpenetration-testing+2
1403 years ago
CVE-2022-44666 preview

CVE-2022-44666

GitHubj00sean/cve-2022-44666

Technical write-up and proof-of-concept for CVE-2022-44666, a Windows Contacts syslink control href attribute escape vulnerability enabling remote…
exploitationpayload-developmentphishing-tools+2
1543 years ago
unisoc-su preview

unisoc-su

GitHubskorpion96/unisoc-su

A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models
android-securitybinary-exploitationcommand-and-control+7
1354 days ago
sleep_python_bridge preview

sleep_python_bridge

GitHubcobalt-strike/sleep_python_bridge

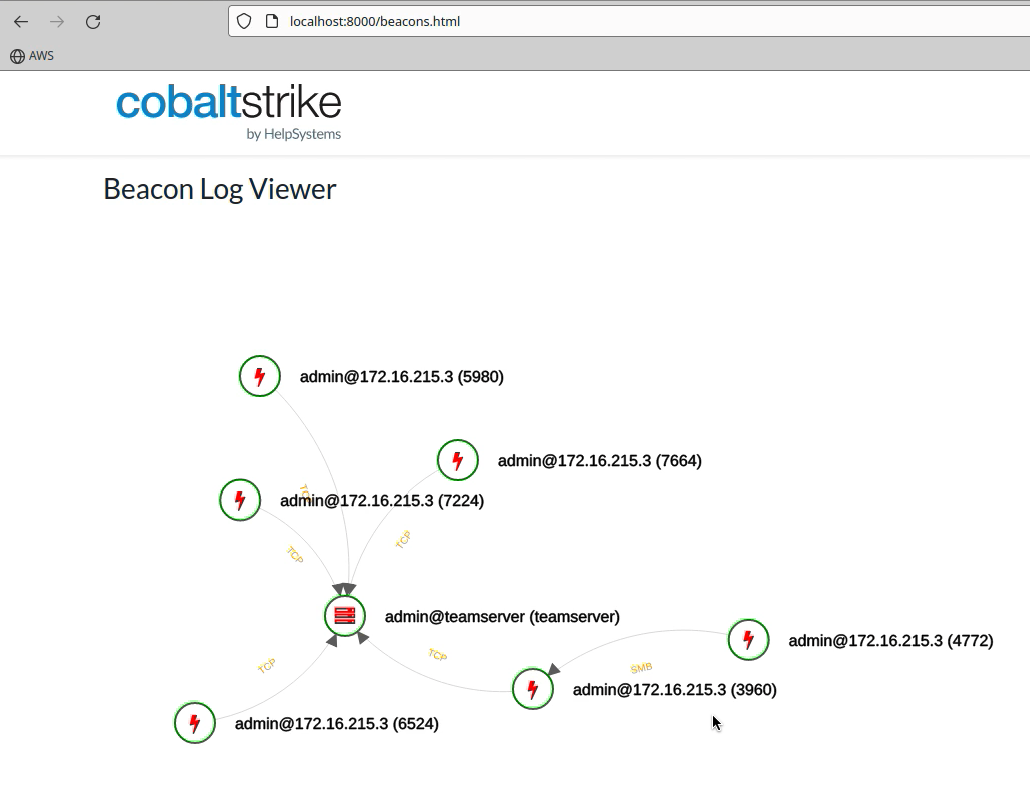
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
command-and-controlioc-managementlog-analysis+3
1881 year ago
MagiskEoP preview

MagiskEoP

GitHubcanyie/magiskeop

Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…
android-securitybinary-exploitationcode-analysis+5
1981 year ago
RansomwareSim preview

RansomwareSim

GitHubhalildeniz/ransomwaresim

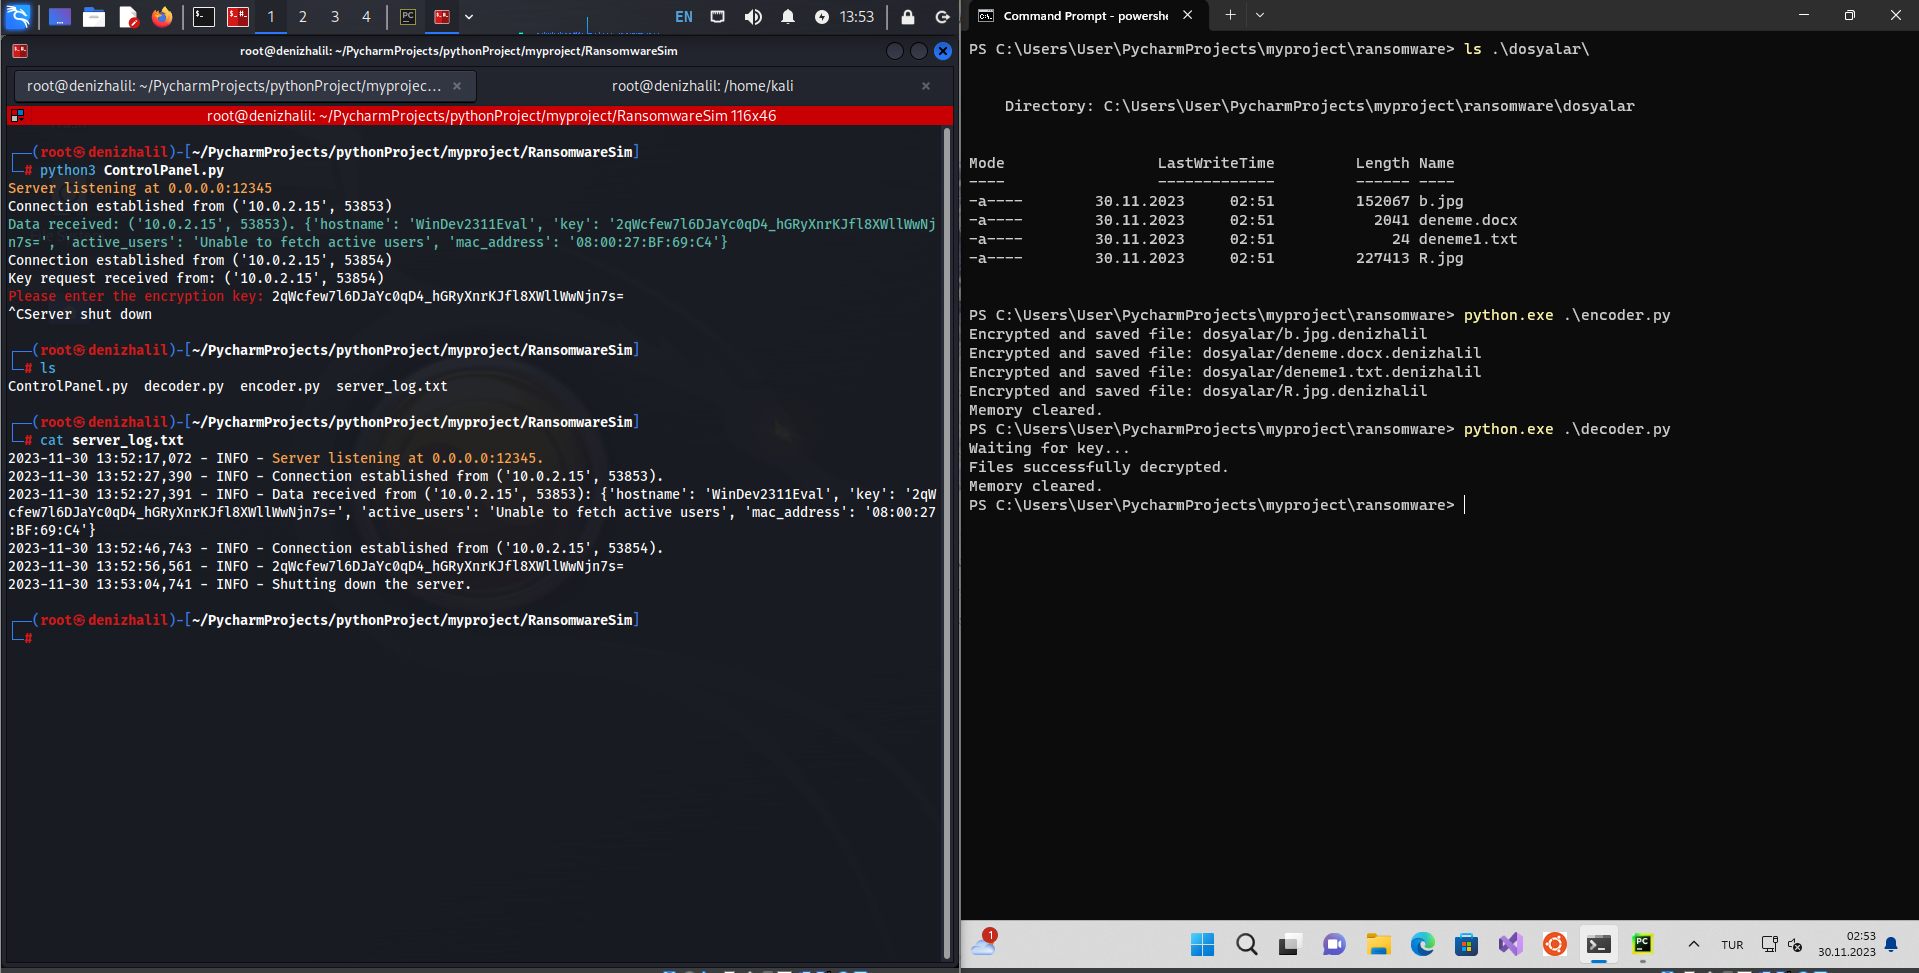
Educational ransomware simulator demonstrating file encryption, C2 communication, and decryption for cybersecurity training and malware analysis.

command-and-controleducationencryption-decryption-tools+3
1762 years ago
whatsapp-mitd-mitm preview

whatsapp-mitd-mitm

GitHubcensus/whatsapp-mitd-mitm

PoC and tools for exploiting CVE-2020-6516 (Chrome) and CVE-2021-24027 (WhatsApp)
android-securityexploitationmobile-security+3
1495 years ago
airstrike preview

airstrike

GitHubsmokeme/airstrike

Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…
command-and-controleducationpayload-development+2
1742 years ago
crauEmu preview

crauEmu

GitHubdsecurity/crauemu

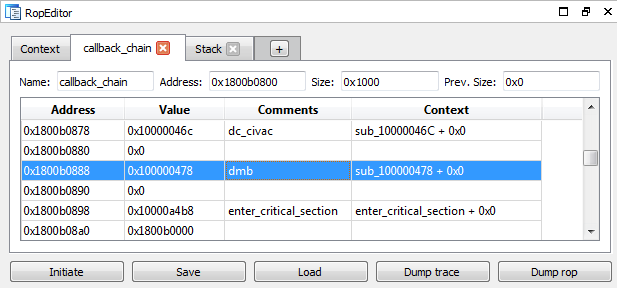
crauEmu is an uEmu extension for developing and analyzing payloads for code-reuse attacks

binary-exploitationexploit-frameworkspayload-development+1
1106 years ago
CVE-2020-15778 preview

CVE-2020-15778

GitHubcpandya2909/cve-2020-15778

Technical write-up and proof-of-concept for CVE-2020-15778, an authenticated command injection vulnerability in OpenSSH scp (<=8.3p1) allowing remote…

command-and-controlexploitationpayload-development+3
1423 years ago
Previous1…456…100Next