
meizu21-ghostlock-root
 ymh001/meizu21-ghostlock-root
MEIZU 21 locked-bootloader runtime root via CVE-2026-43499 and KernelSU late-load
android-securityexploitationmobile-app-pentesting+4
2
ymh001/meizu21-ghostlock-rootMEIZU 21 locked-bootloader runtime root via CVE-2026-43499 and KernelSU late-load
 michaelroland/omapi-cve-2015-6606-exploit
Simple Exploit for Verification of CVE-2015-6606
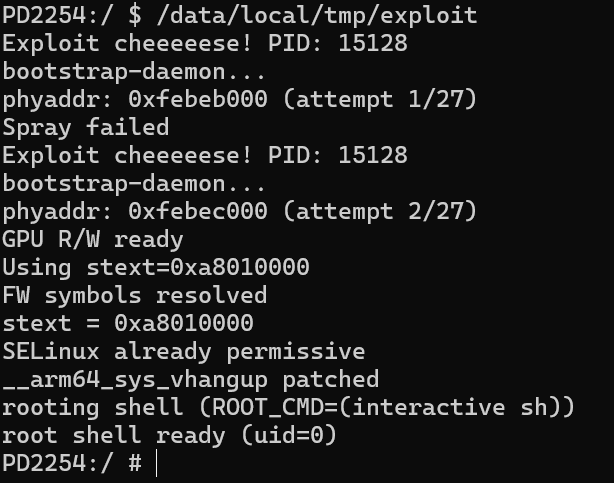 xianwan1314/cve-2025-21479-iqoo11pro
CVE-2025-21479 (Qualcomm Adreno GPU) reproduction notes for vivo iQOO 11 Pro (PD2254) - authorized research
 ruik-tech/ghostlock-s25fe
GhostLock (CVE-2026-43499) for the Galaxy S25 FE (W.I.P)
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 k0mraid3/k0mraid3s-system-shell-prebuilt
Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
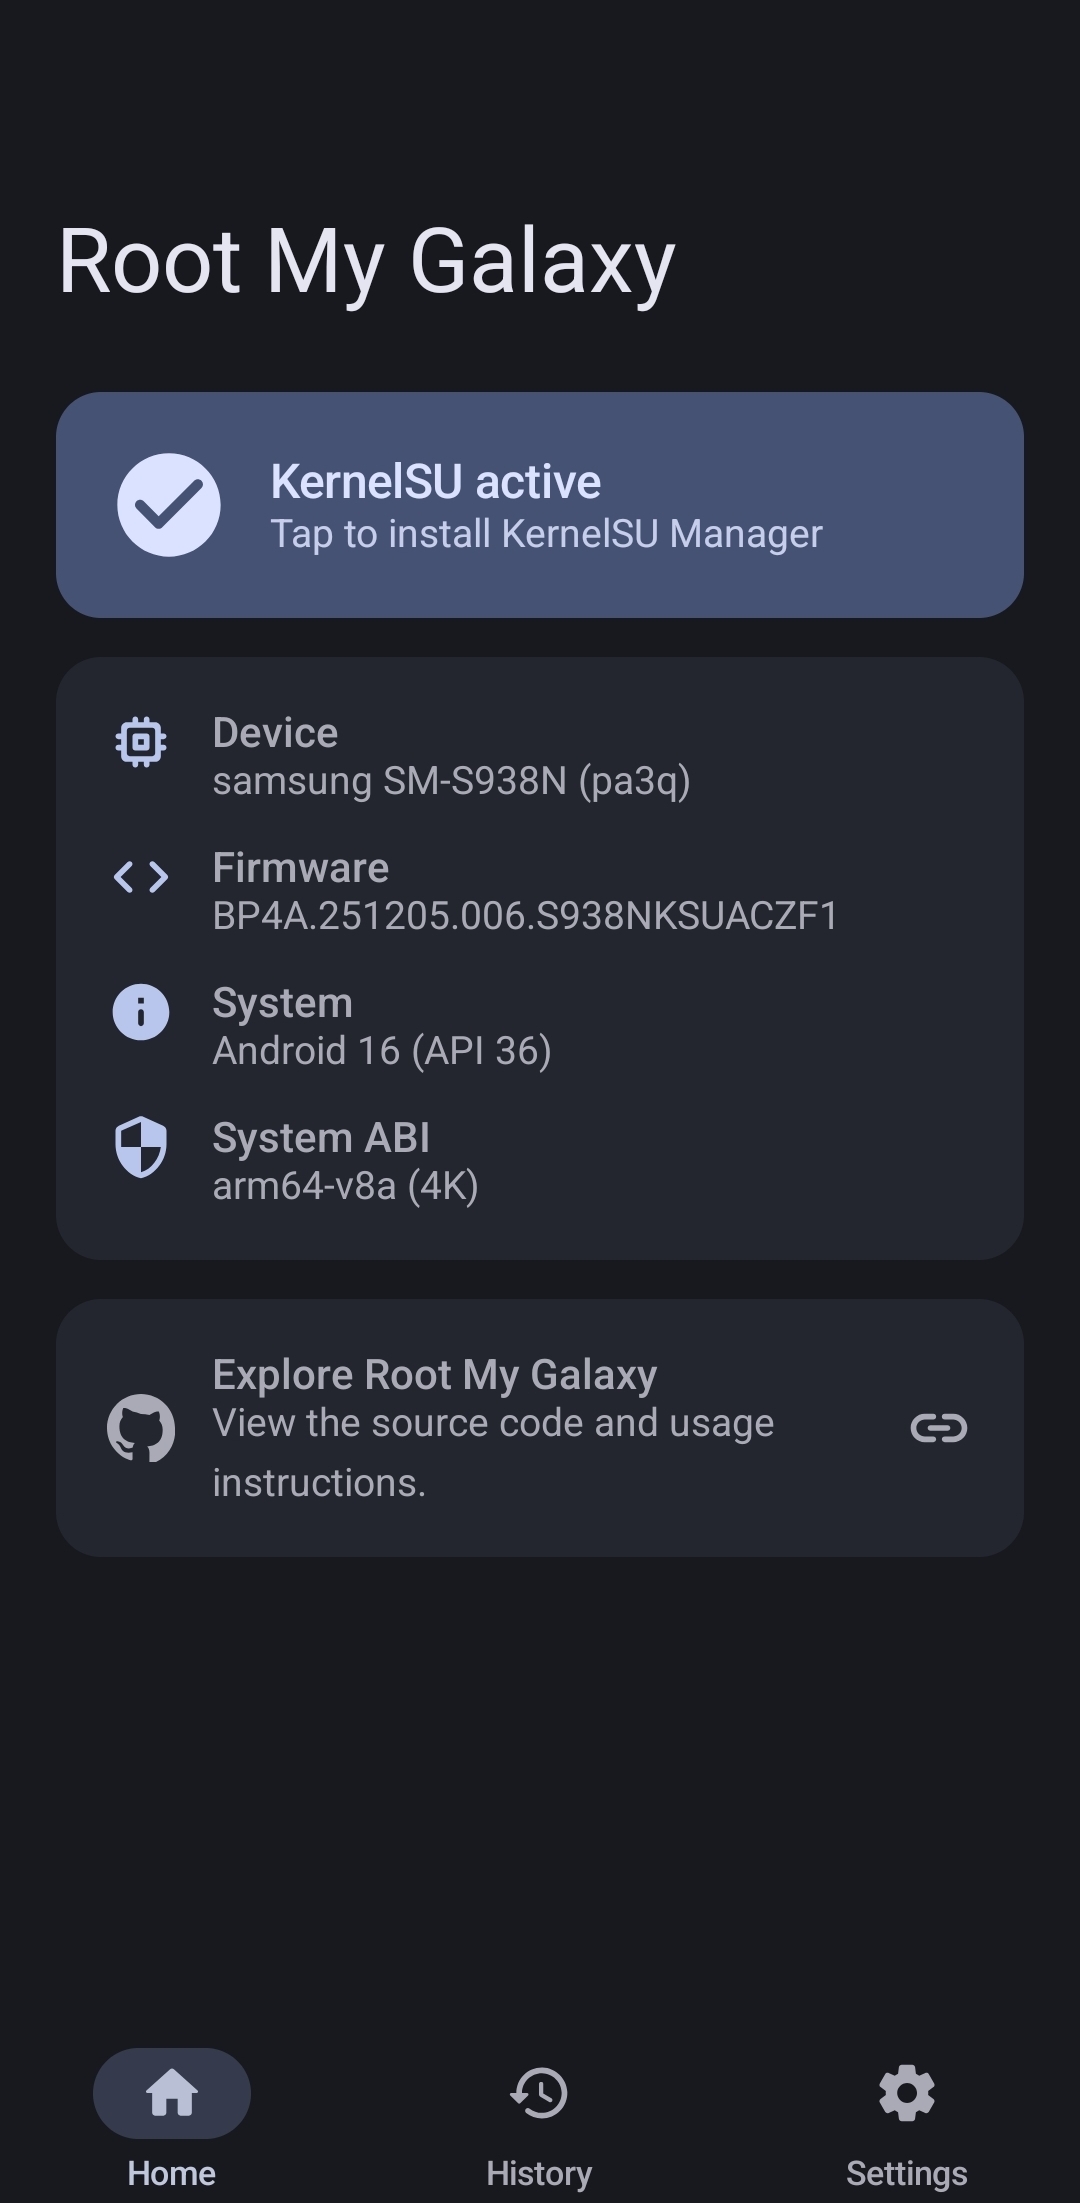 busung-dev/root-my-galaxy
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 skorpion96/unisoc-su
A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models
 canyie/magiskeop
Exploit and writeup for installed app to root privilege escalation through CVE-2024-48336 (Magisk Bug #8279), Privileges Escalation / Arbitrary Code…
 secmob/pocforcve-2015-1528
I'll submit the poc after blackhat
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 zenyxx-xd/rootmyvivo
One-click root for vivo/iQOO devices on locked bootloader | CVE-2026-43499 + KernelSU
 alephsecurity/initroot
Motorola Untethered Jailbreak: Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
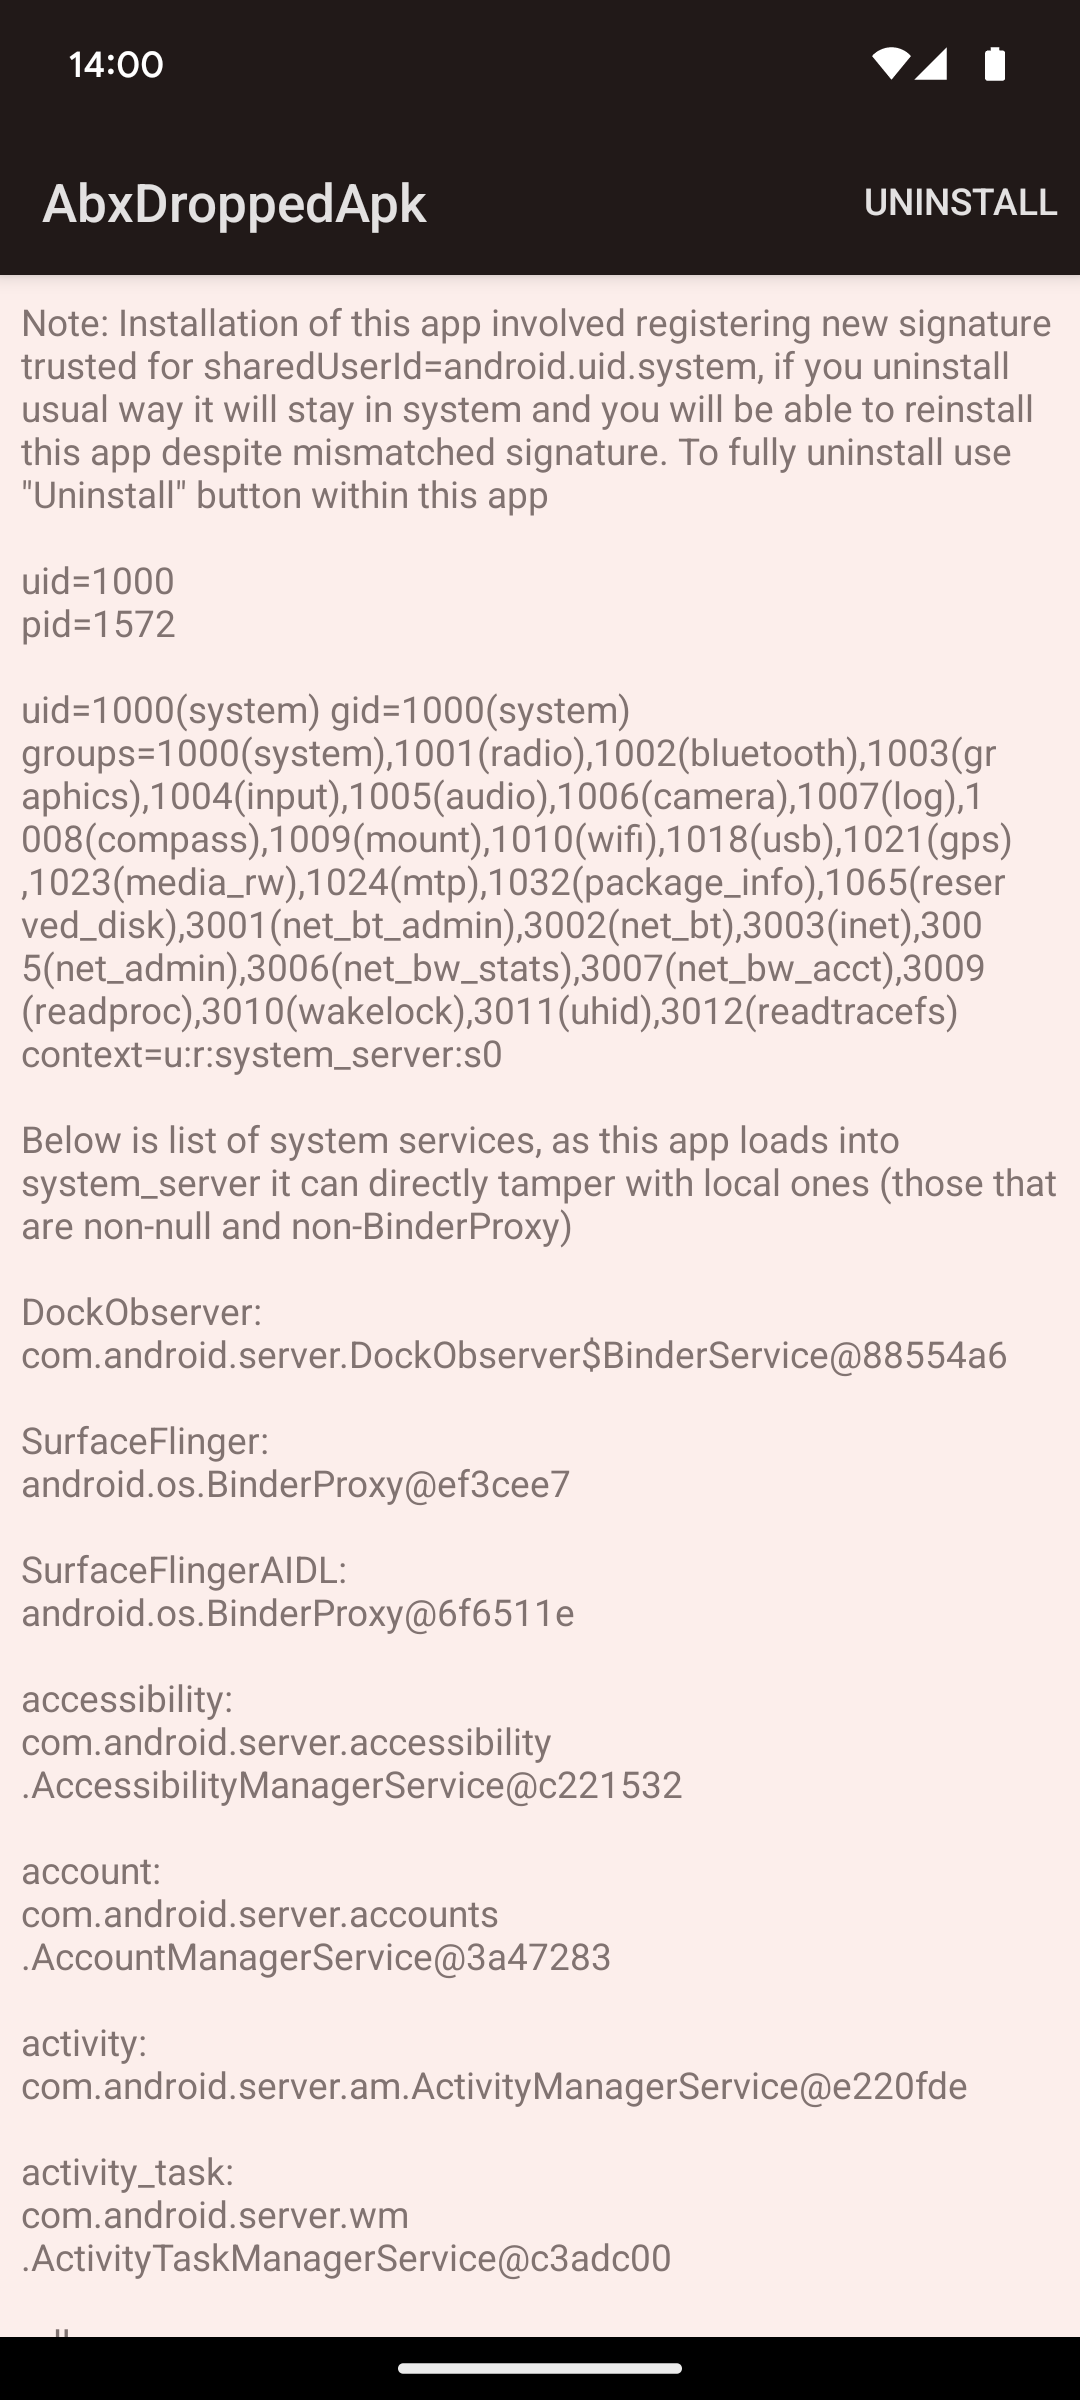 michalbednarski/abxoverflow
Writeup and exploit for CVE-2024-34740, integer overflow in Android's BinaryXmlSerializer to system_server file write and then to system_server code…
 busung-dev/cve-2026-43499-s25u
Standalone CVE-2026-43499 PoC for Galaxy S25 Ultra SM-S938N S938NKSUACZF1
 michalbednarski/thisseemswrong
Writeup and exploit for CVE-2024-49746: Android's Parcel::continueWrite closing File Descriptors that are later used