

CVE-2019-0752
 edxsh/cve-2019-0752
Proof-of-concept exploit for CVE-2019-0752 targeting Internet Explorer 11 on Windows 10 x64. Uses JavaScript DOM manipulation and special address…
exploitationpayload-developmentpenetration-testing+2
2
edxsh/cve-2019-0752Proof-of-concept exploit for CVE-2019-0752 targeting Internet Explorer 11 on Windows 10 x64. Uses JavaScript DOM manipulation and special address…
 ludovicpatho/cve-2022-22965_spring4shell
A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…
 simoesctt/ctt-enhanced-cve-2026-46339-exploit-engine
Python framework exploiting CVE-2026-46339 for unauthenticated RCE on 9Router via MCP bridge, using temporal sharding and dispersion to evade…
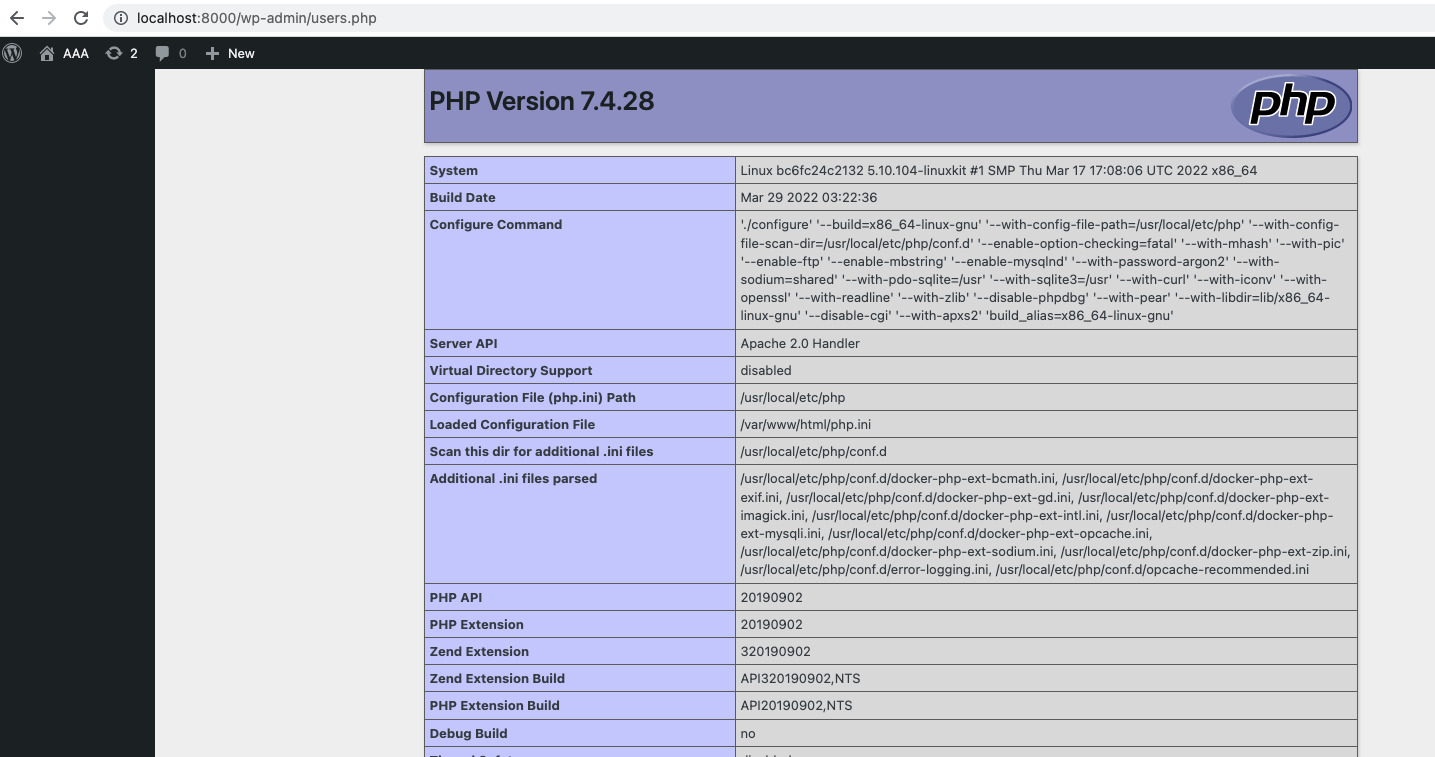 grazee/cve-2022-1329-wordpress-elementor-rce
Proof-of-concept exploit for CVE-2022-1329, a remote code execution vulnerability in WordPress Elementor 3.6.0-3.6.2. Includes Docker-based…
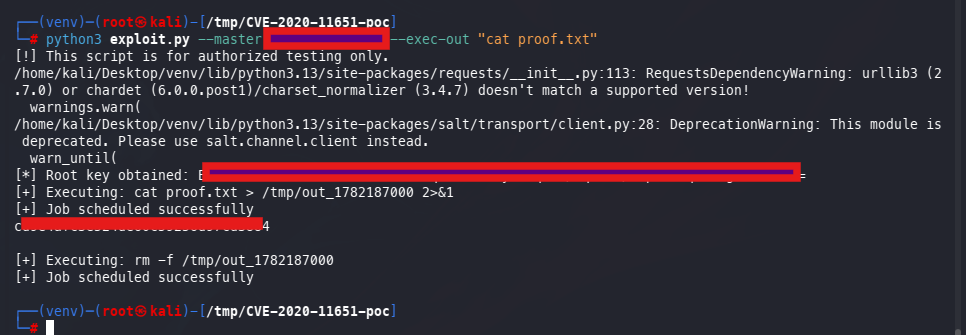 s1lentf00thold/cve-2020-11651-poc
Proof-of-concept exploit for CVE-2020-11651, a critical remote code execution vulnerability in SaltStack, enabling unauthenticated command execution…
 fatkz/cve-2022-24112
Proof-of-Concept exploit for Apache APISIX 2.12.x RCE (CVE-2022-24112) via Lua filter_func injection. Executes arbitrary system commands on…
 synacktiv/laravel_cookie_killer
Decrypt and re-encrypt Laravel session cookies to exploit insecure PHP deserialization for remote code execution.
 itsmehacker/ducky-exploit
Arduino Rubber Ducky Framework
 p0dalirius/cve-2022-45771-pwndoc-lfi-to-rce
Pwndoc local file inclusion to remote code execution of Node.js code on the server
 flyinbedxyz/cve-2021-1732
Local privilege escalation exploit for CVE-2021-1732 targeting Windows 10 and Server versions, with PoC code and affected system enumeration.
 rajchowdhury240/cve-2025-67435
A critical Remote Code Execution (RCE) vulnerability has been identified in PluXML CMS version 5.8.22. This vulnerability allows authenticated…
 0z09e/cve-2022-22909
Hotel Druid 3.0.3 Code Injection to Remote Code Execution
 nemo-wq/printnightmare-cve-2021-34527
PrintNightmare - Windows Print Spooler RCE/LPE Vulnerability (CVE-2021-34527, CVE-2021-1675) proof of concept exploits
 warxim/cve-2022-41852
CVE-2022-41852 Proof of Concept (unofficial)
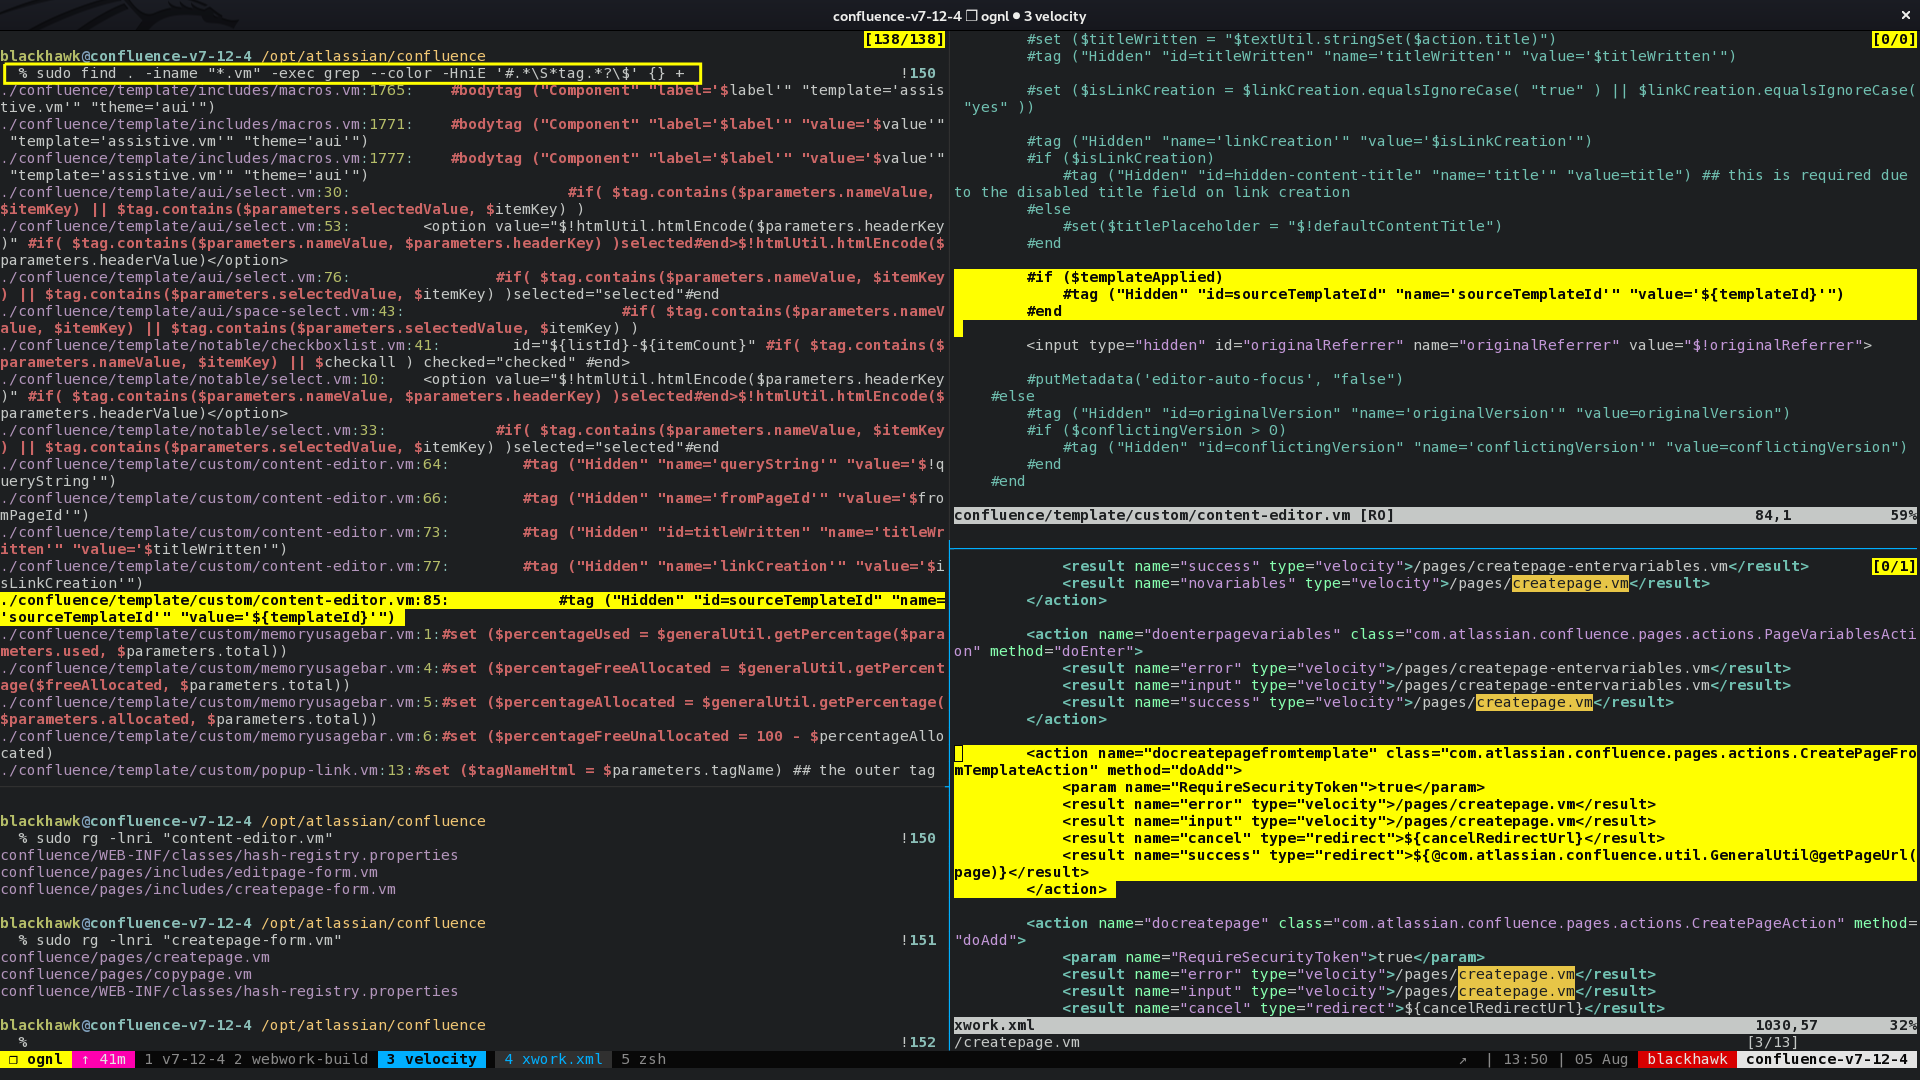 orangmuda/cve-2021-26084
CVE-2021-26084 - Confluence Server Webwork OGNL injection
 joshterrill/cve-2025-55182-realistic-poc
a realistic POC demonstrating the missing `hasOwnProperty` check in [email protected]
 drkim-dev/cve-2026-25924
Proof-of-concept exploit for CVE-2026-25924, demonstrating administrative remote code execution in Kanboard through a missing access control check on…
 barroqueiro/cve-2023-37941
Exploit on the default cache of superset by using pickle