
Koppeling
 monoxgas/koppeling
Adaptive DLL hijacking / dynamic export forwarding
binary-exploitationexploitationpayload-development+1
monoxgas/koppelingAdaptive DLL hijacking / dynamic export forwarding
 ionescu007/faxhell
A Bind Shell Using the Fax Service and a DLL Hijack
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 dazzyddos/clickonceblobber
Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…
 klezvirus/koppeling-p
Adaptive DLL hijacking / dynamic export forwarding - EAT preserve
 phackt/wptsextensions.dll
WptsExtensions.dll for exploiting DLL hijacking of the task scheduler.
 jas502n/phpstudy-backdoor
phpstudy dll backdoor for v2016 and v2018
 dust-life/cve-2019-18935-memshell
C++ memshell DLL generator for CVE-2019-18935, enabling in-memory web shell deployment via Telerik UI deserialization with Assembly.Load and IJW…
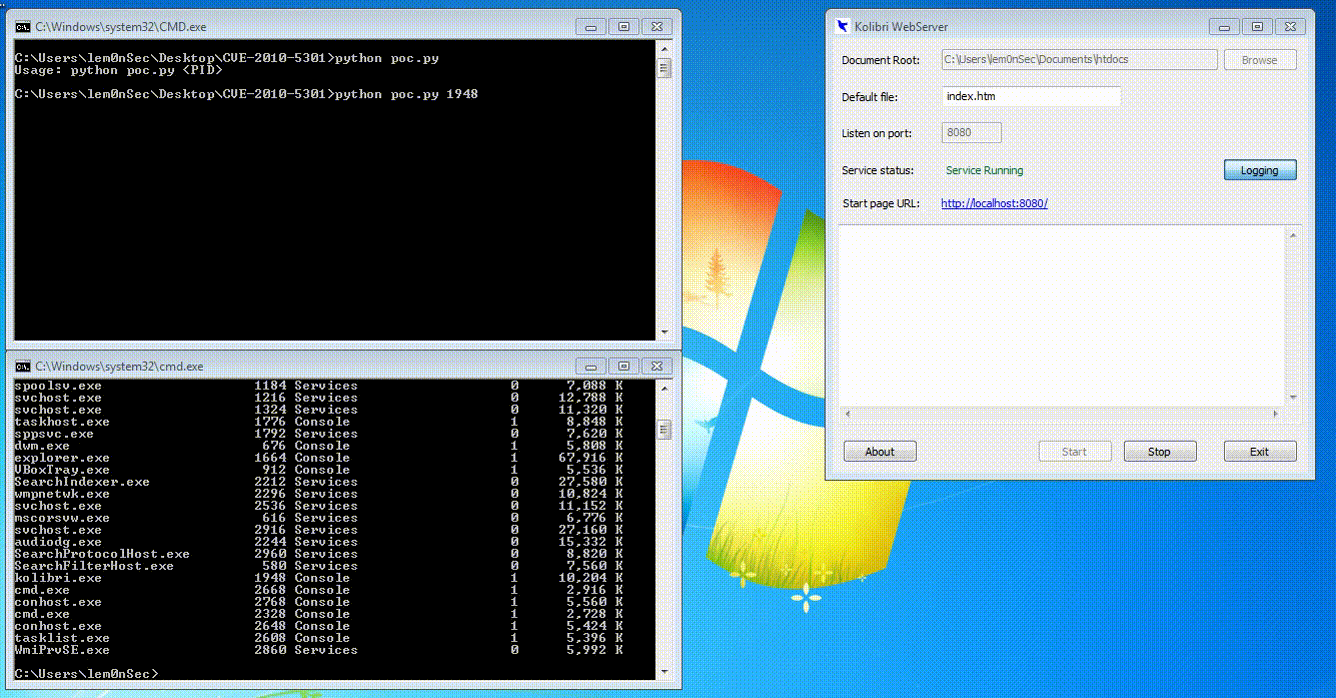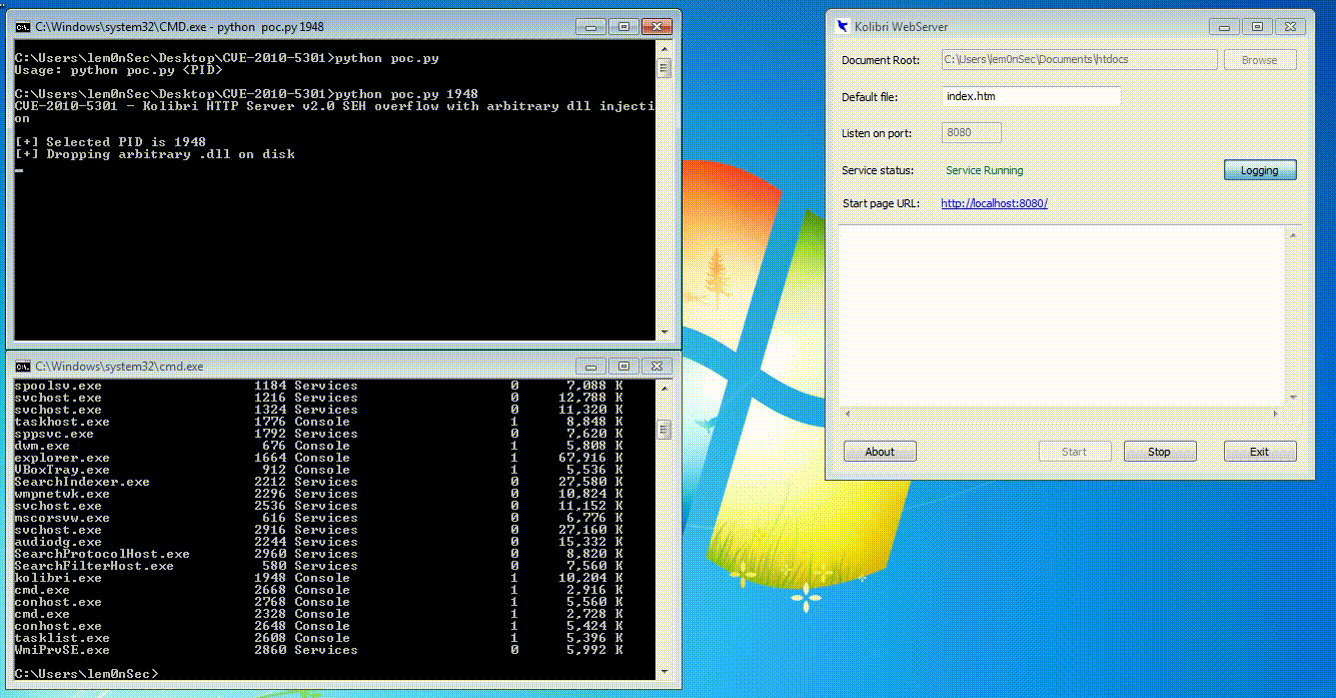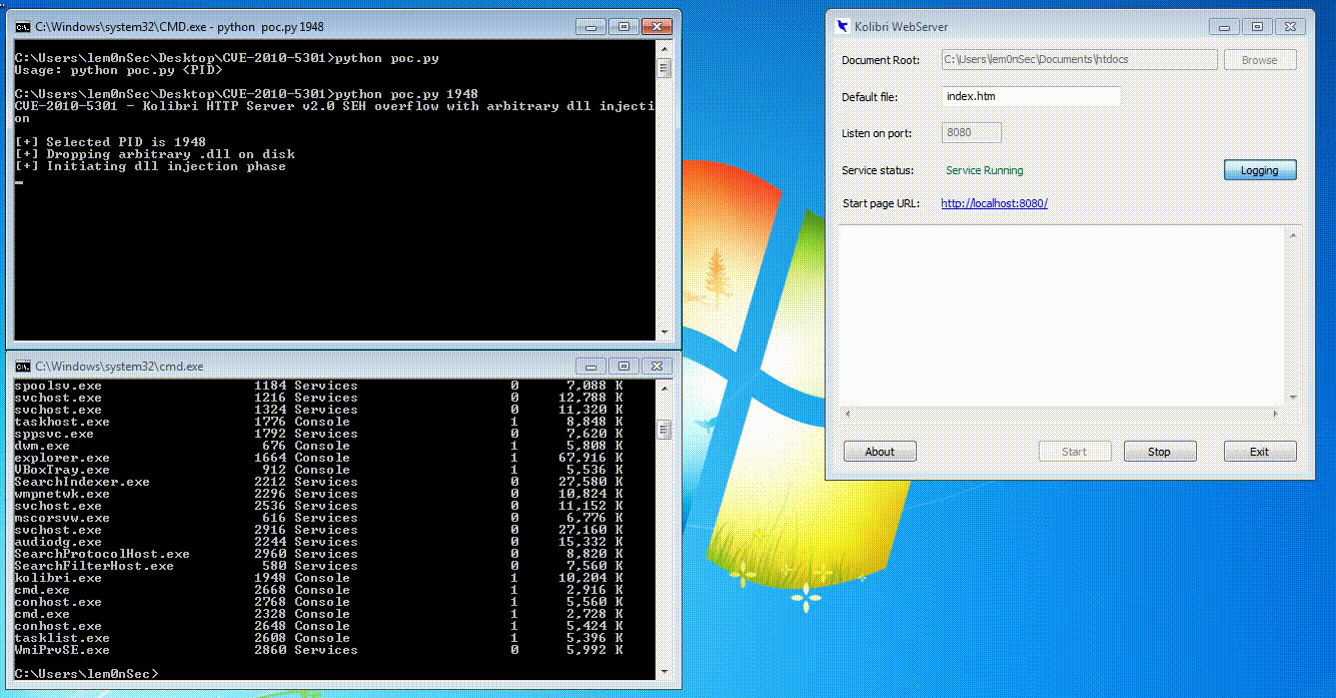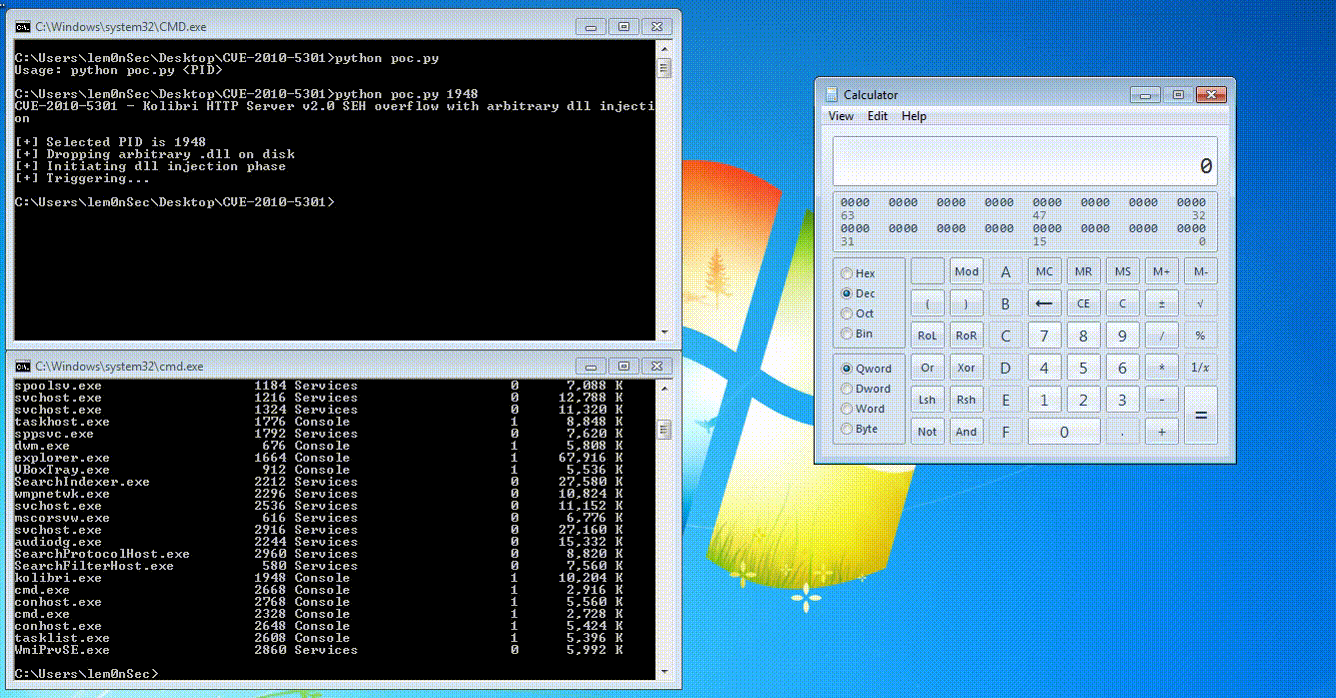 lem0nsec/cve-2010-5301
A proof of concept of an SEH overflow with arbitrary dll injection
 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
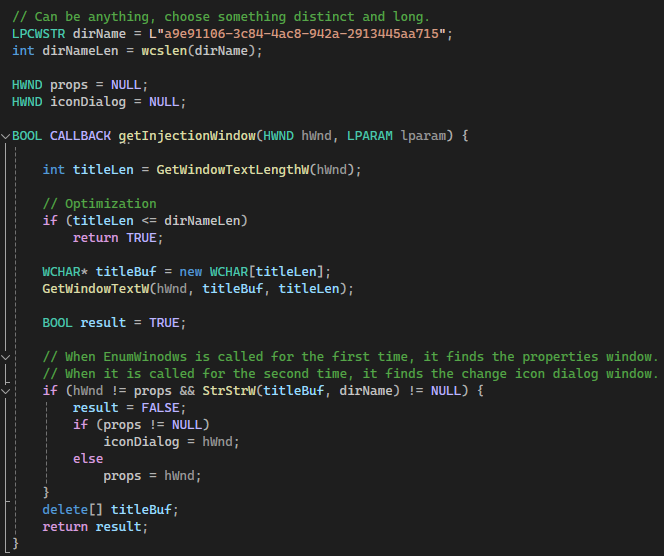 d419h/iconjector
Inject DLLs into the explorer process using icons
 bats3c/darkloadlibrary
LoadLibrary for offensive operations
 ashr/cve-2017-8759-exploits
Two versions of CVE-2017-8759 exploits
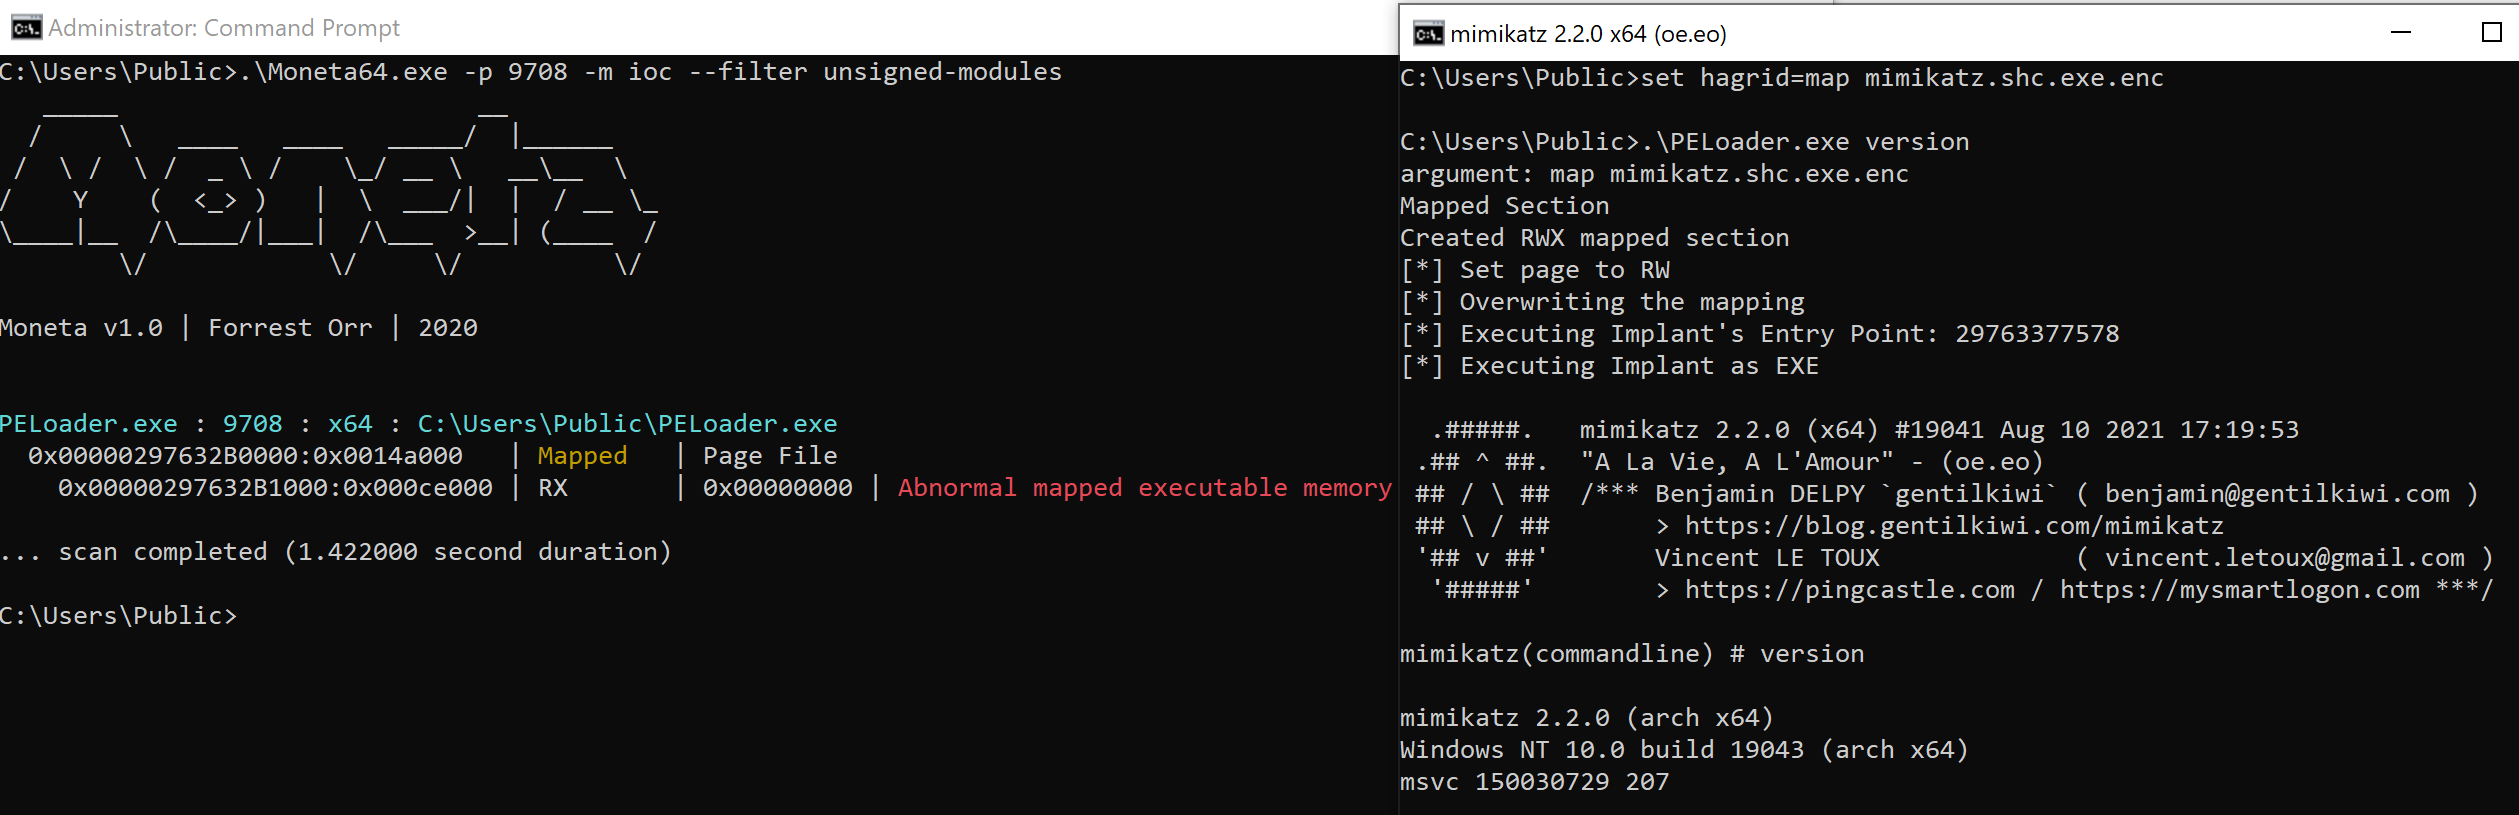 hagrid29/peloader
PE loader with various shellcode injection techniques
 elliotkillick/ldrlockliberator
For when DLLMain is the only way
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.