
liffy
 mzfr/liffy
Local file inclusion exploitation tool
payload-developmentpenetration-testingvulnerability-analysis+2
mzfr/liffyLocal file inclusion exploitation tool
 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 redcode-labs/coldfire
Golang malware development library
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 bibo318/cve-2024-4577-rce-attack
ATTACK PoC - PHP CVE-2024-4577
 showy-headteacher114/cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.
 joshuavanderpoll/cve-2026-44262
Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.
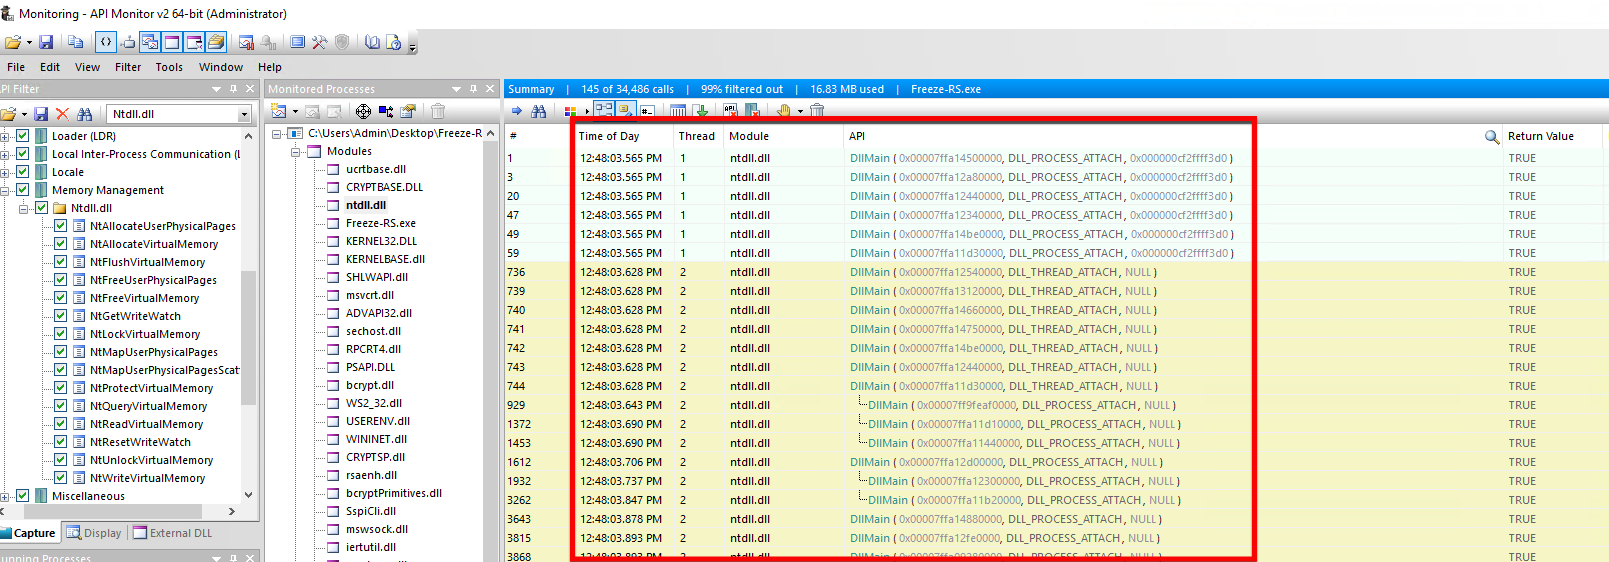
 edu0x01/hack-tools
Project that brings together several pentest tools
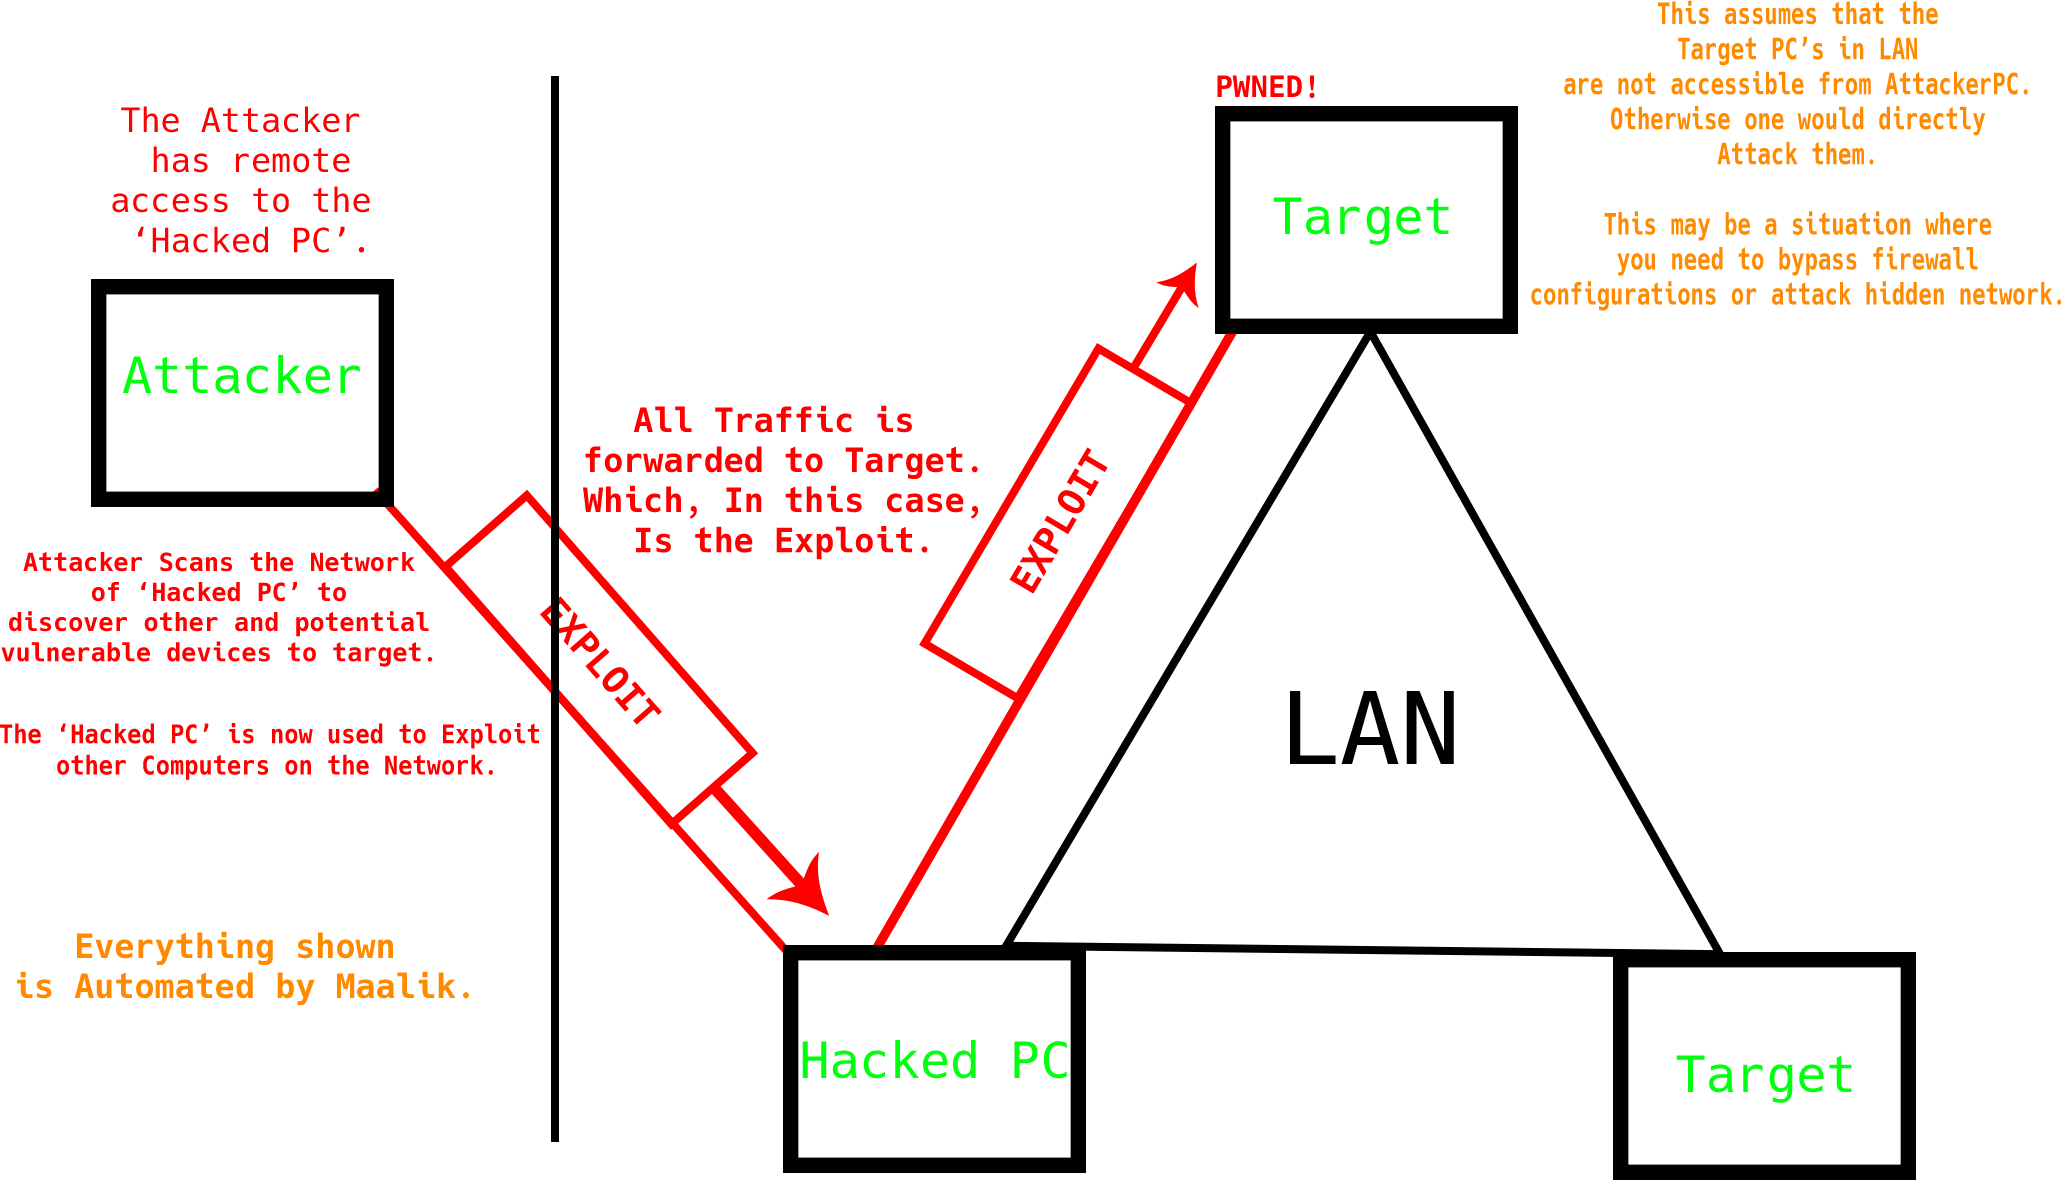 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
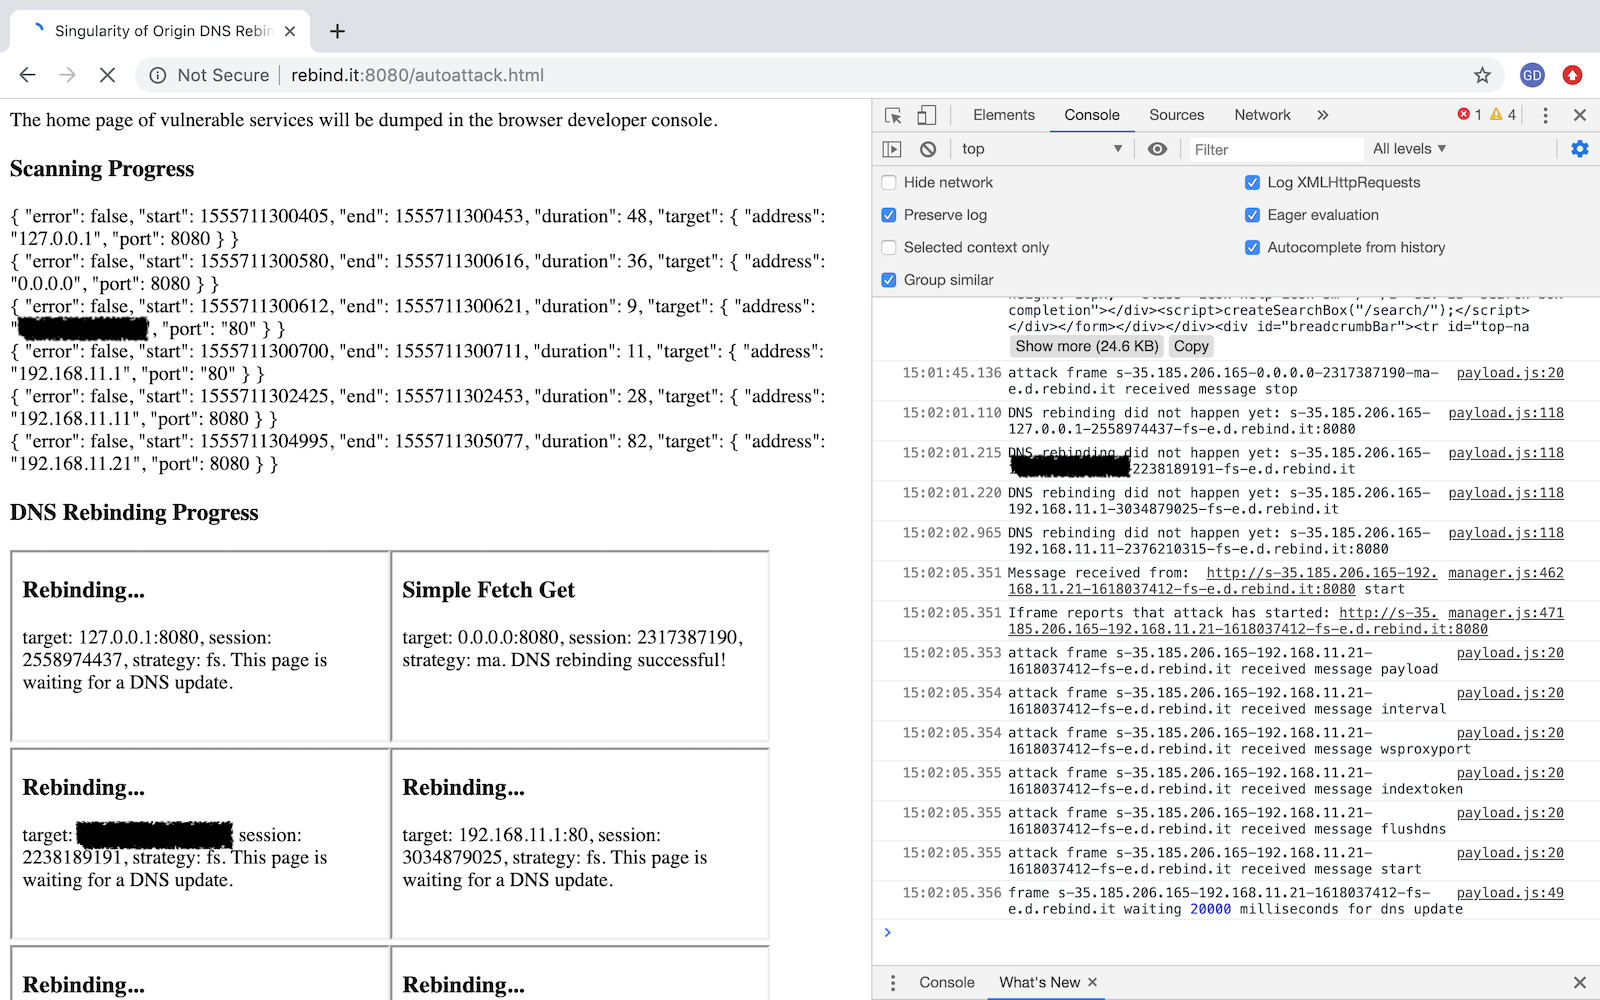 nccgroup/singularity
A DNS rebinding attack framework.
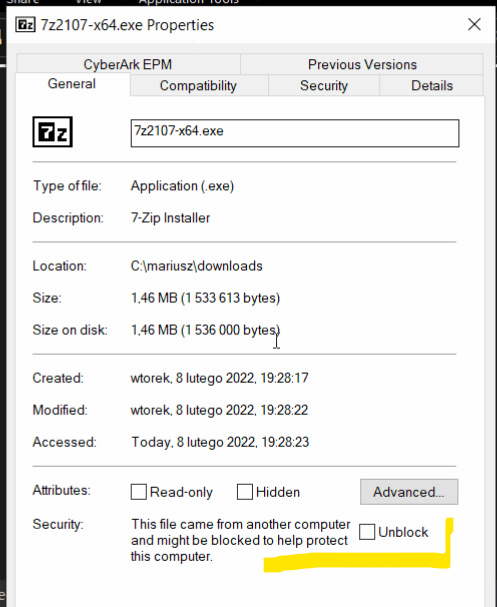 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
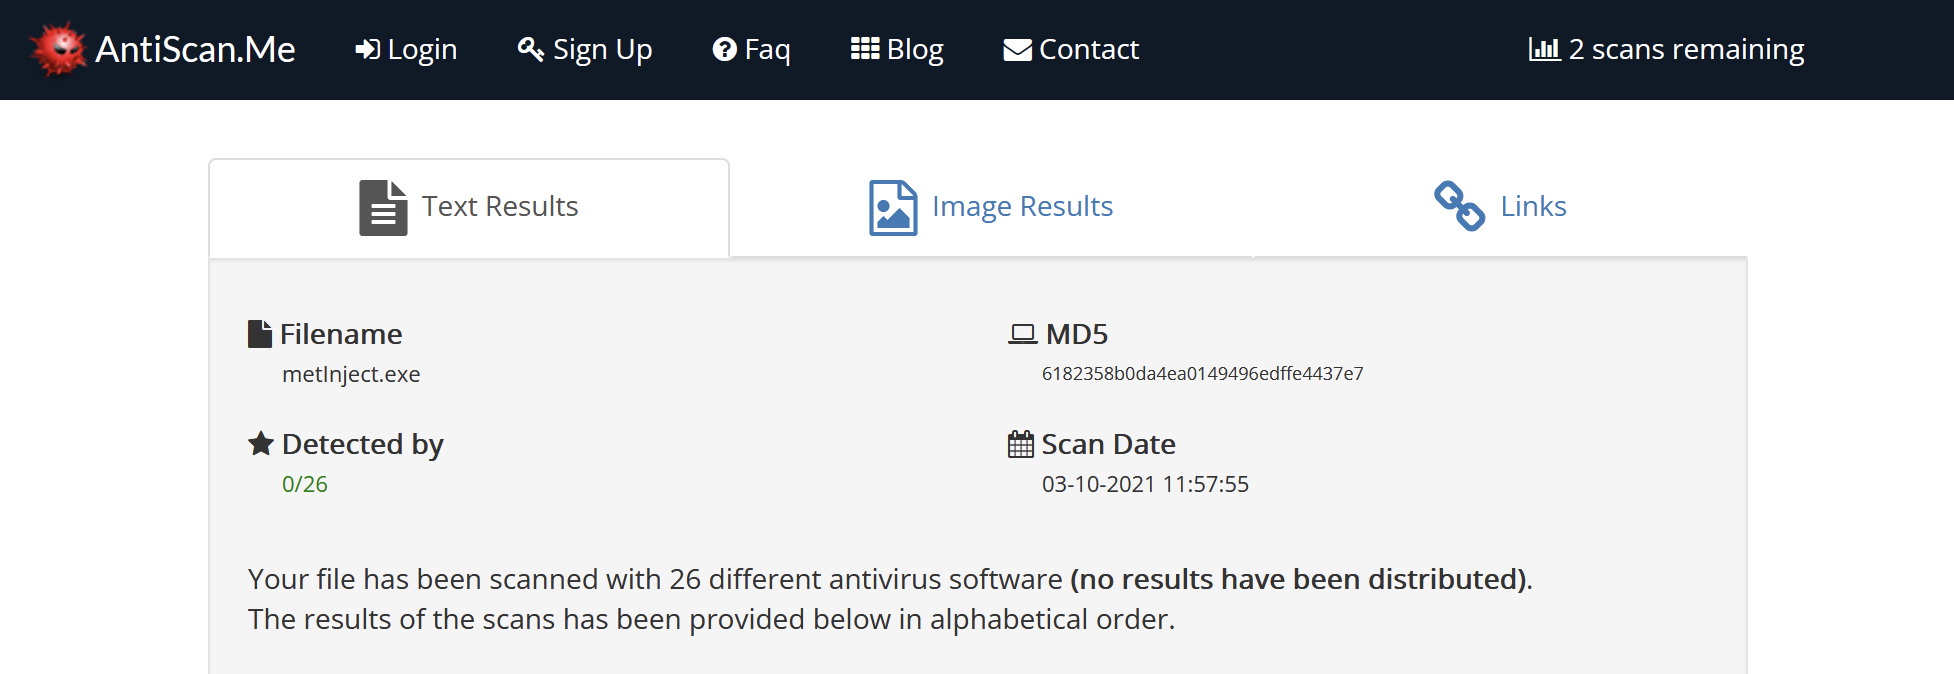 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
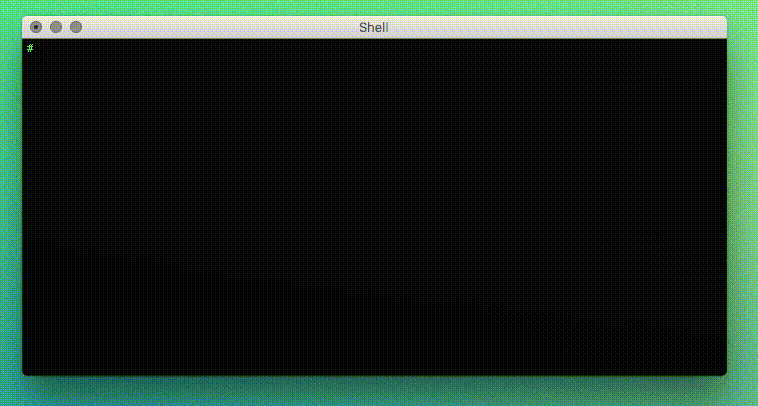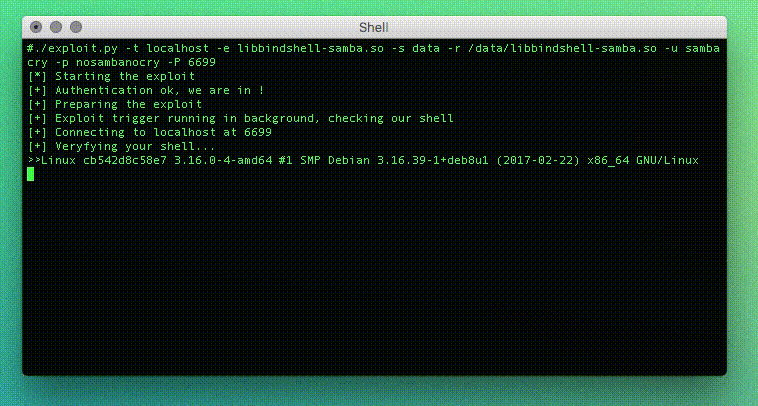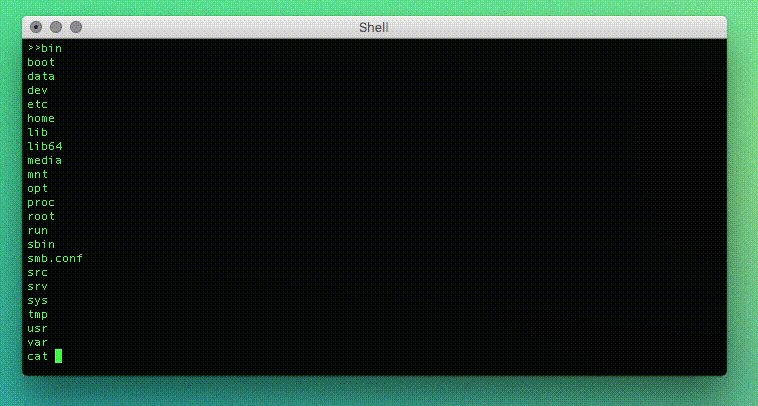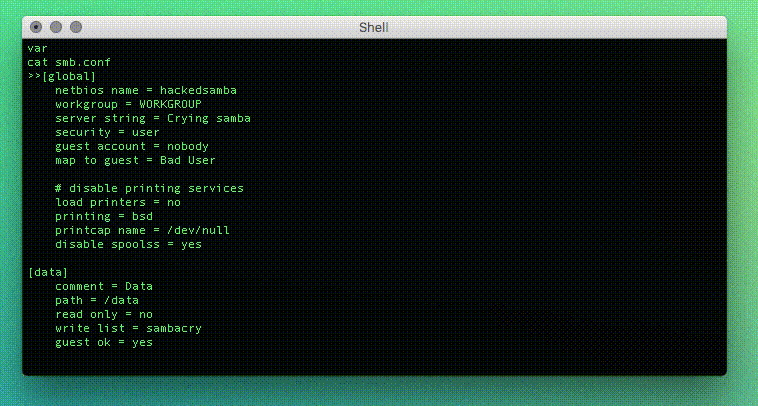 opsxcq/exploit-cve-2017-7494
SambaCry exploit and vulnerable container (CVE-2017-7494)
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…